

TATS
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
authenticationidentity-access-managementlog-analysis+2
39
icemoonhsv/tatsAnalyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
 squeeze440/tugtainer-poc
PoC — OIDC id_token accepted without signature/audience/expiry check in Tugtainer (GHSA-crjc-6vc7-xrfh, CVE-2026-87004, CVSS 8.1).
 ccob/pivert
Emulates NIST SP 800-73 PIV smart cards on Windows using a PFX certificate and private key, enabling smart-card authentication for RDP, Citrix, and…
 logangoins/sharpsuccessor
SharpSuccessor is a .NET Proof of Concept (POC) for fully weaponizing Yuval Gordon’s (@YuG0rd) BadSuccessor attack from Akamai.
 synacktiv/captaincredz
CaptainCredz is a modular and discreet password-spraying tool.
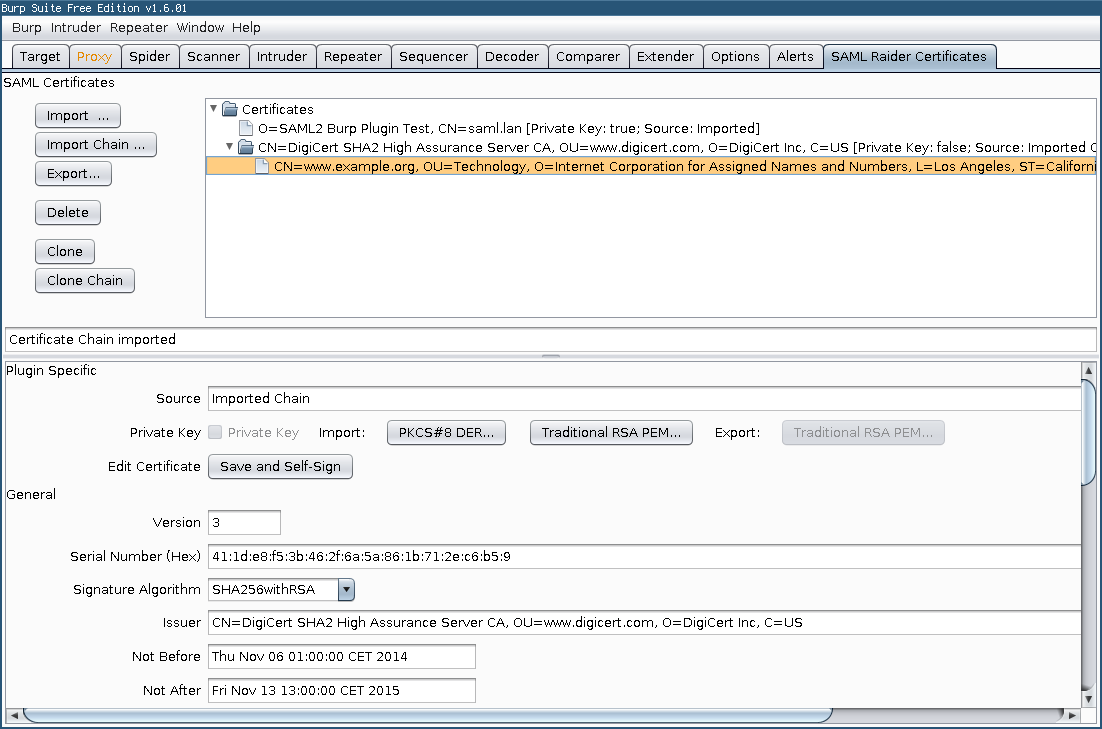 lindi2/samlraider
SAML2 Burp Extension
 notitssixtyn3in/cve-2025-4172025
Security advisory for CVE-2025-4172025: an authentication bypass vulnerability in Copilot enabling unauthorized account access, session hijacking,…
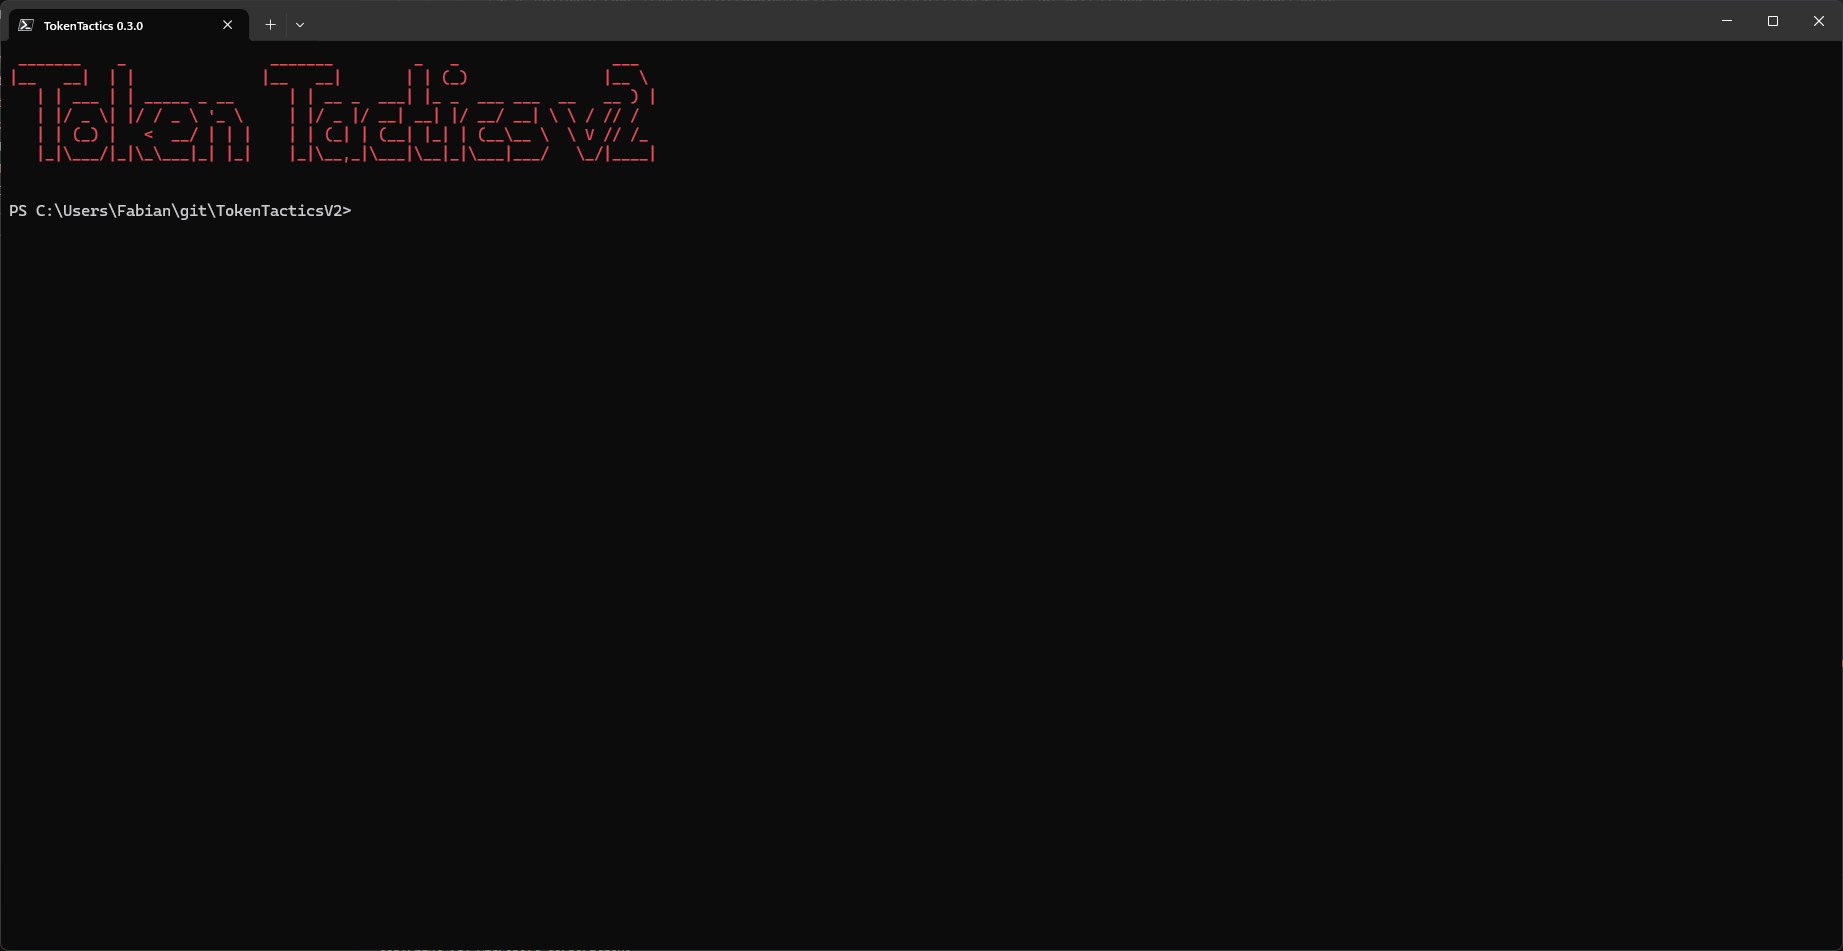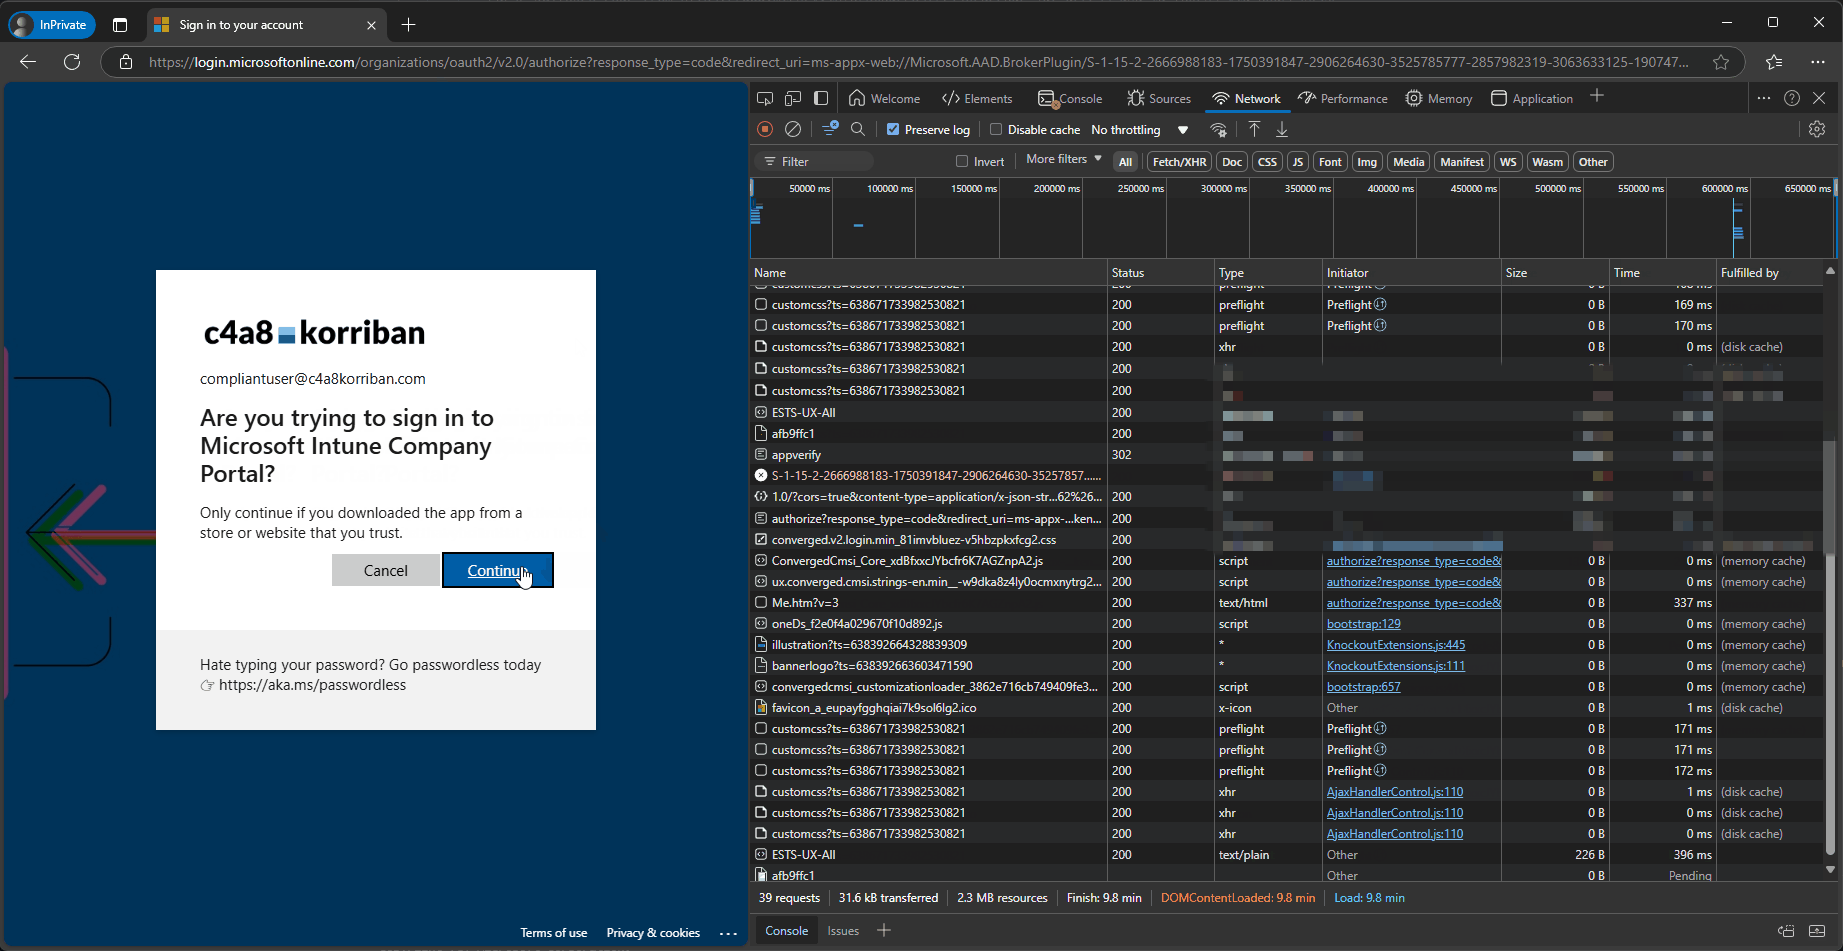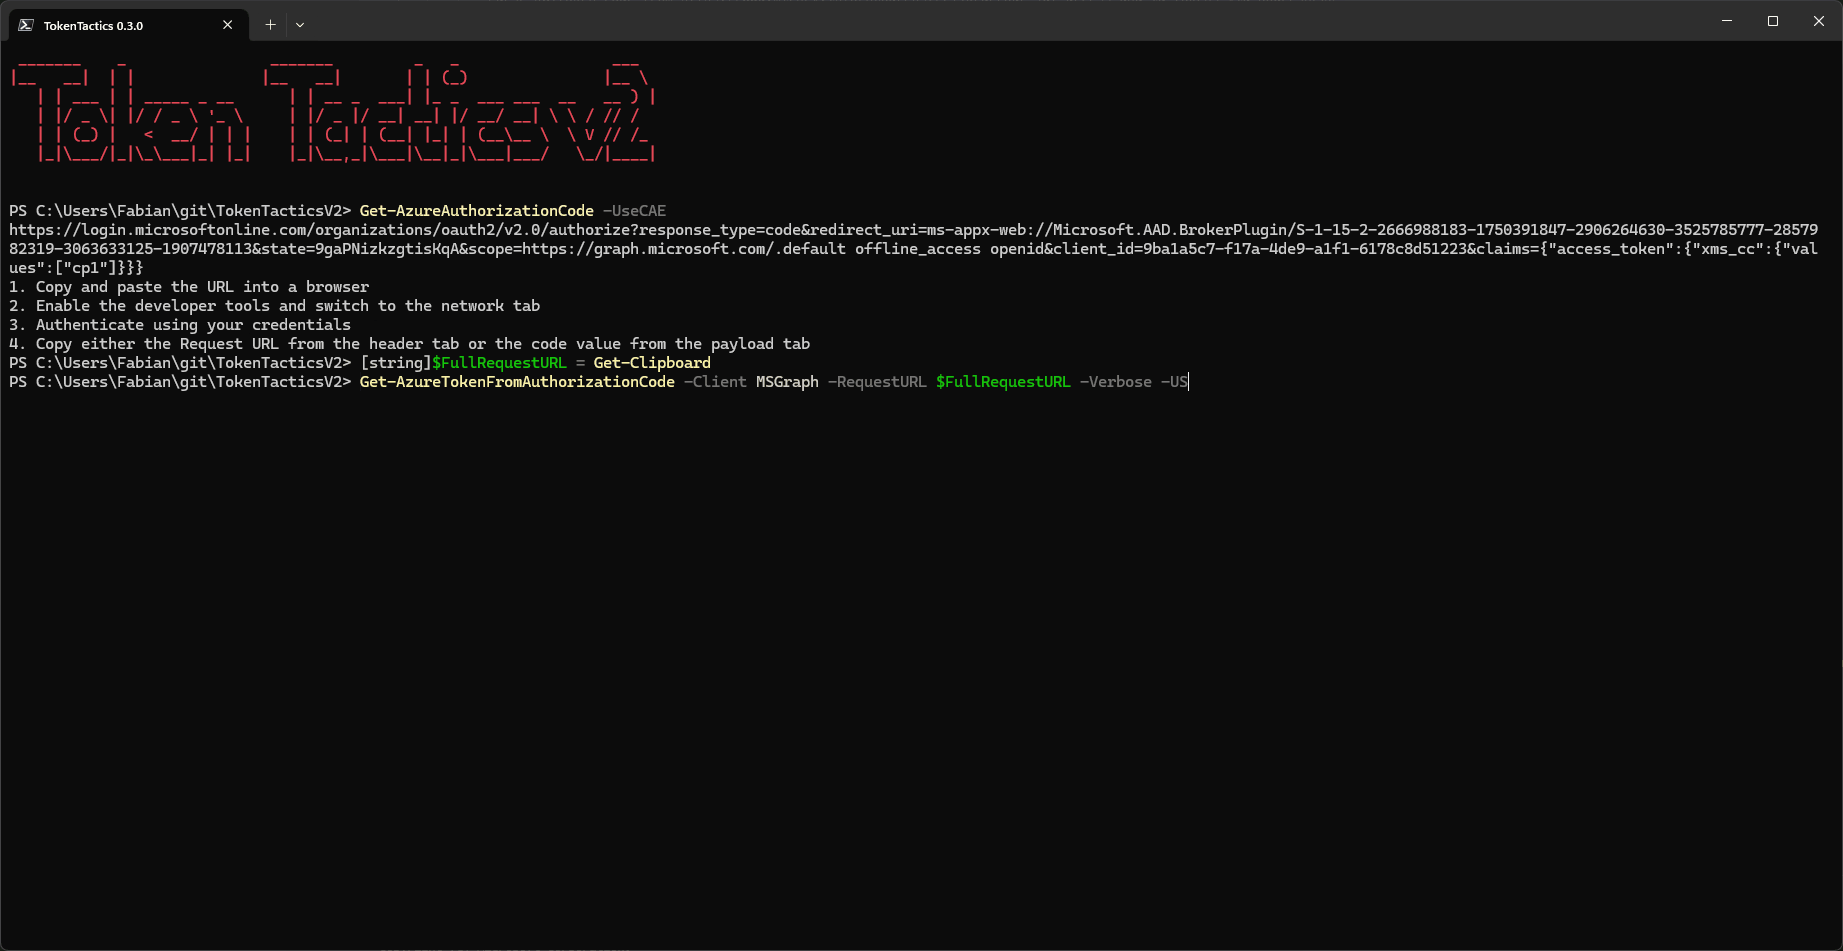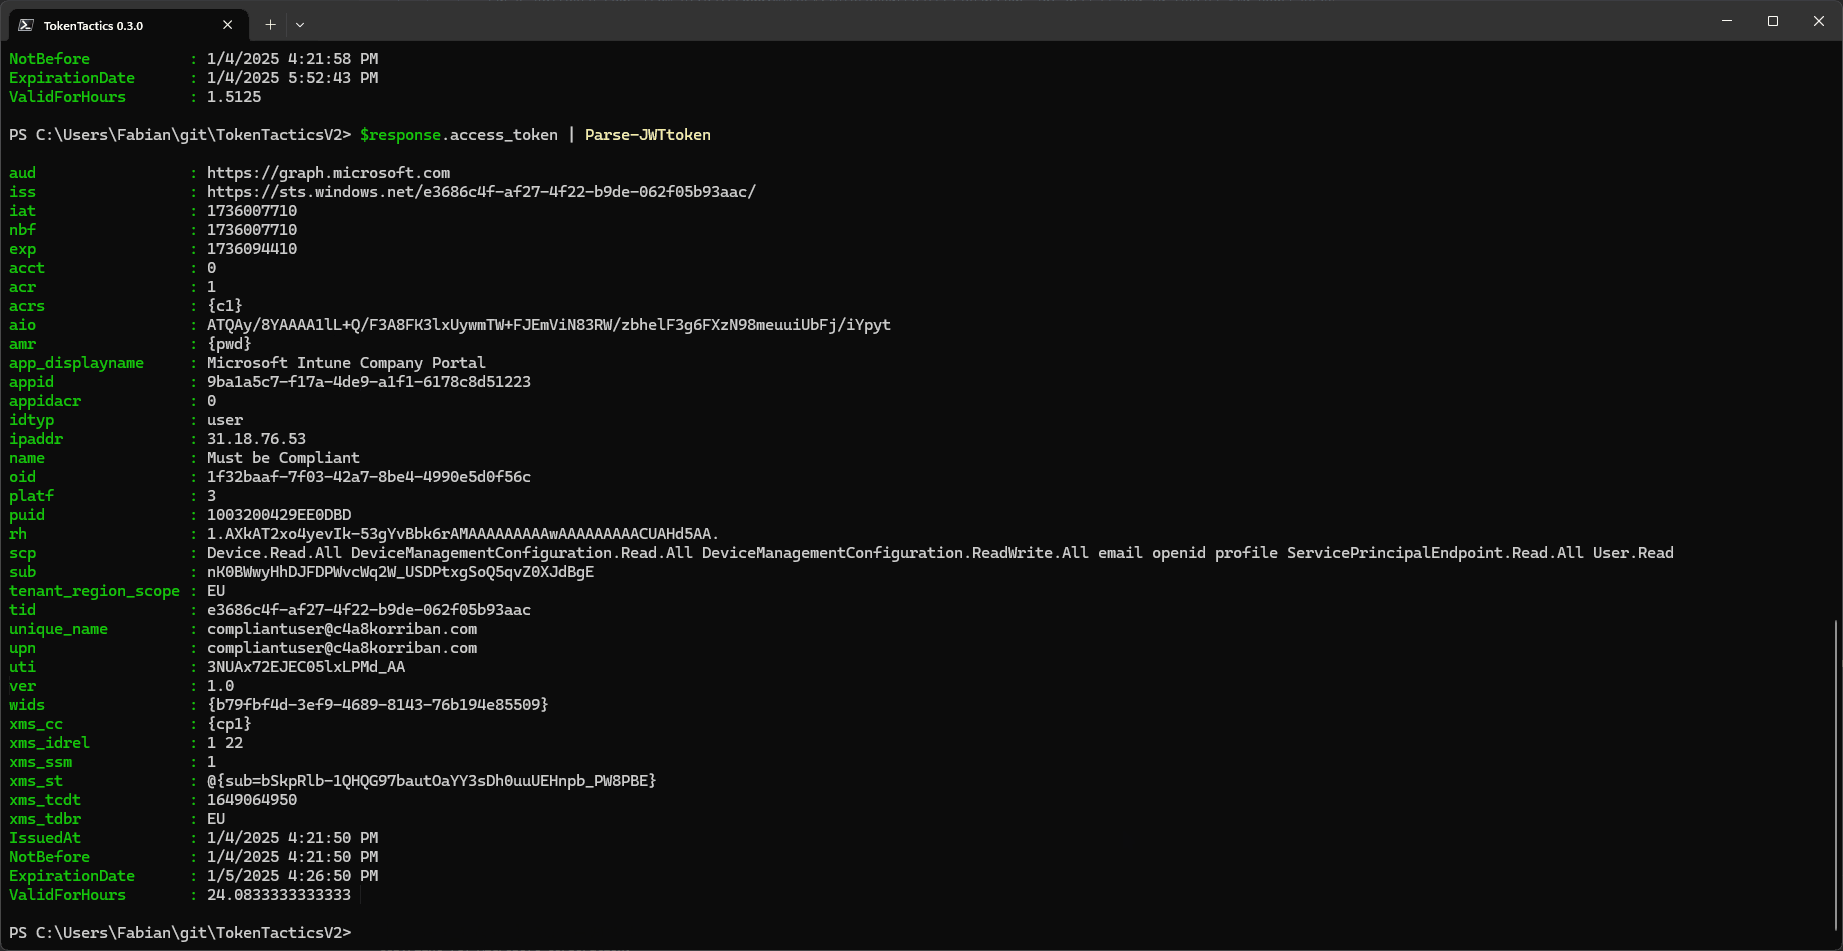 f-bader/tokentacticsv2
A fork of the great TokenTactics with support for CAE and token endpoint v2