


 jedisct1/libsodium
A modern, portable, easy to use crypto library.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 gentilkiwi/mimikatz
A little tool to play with Windows security
 frizb/hashcat-cheatsheet
Hashcat reference for OSCP/penetration testing: hash identification, cracking syntax for Linux, Windows, archives, databases, Kerberos tickets, and…
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 keithjjones/fileintel
A modular Python application to pull intelligence about malicious files
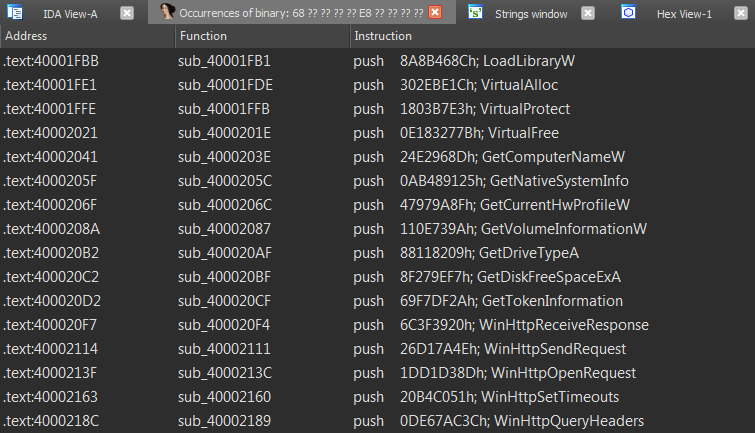 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 neorai/vt-py-scanner
Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
 jtesta/rainbowcrackalack
Rainbow table generation & lookup tools. Make Rainbow Tables Great Again!
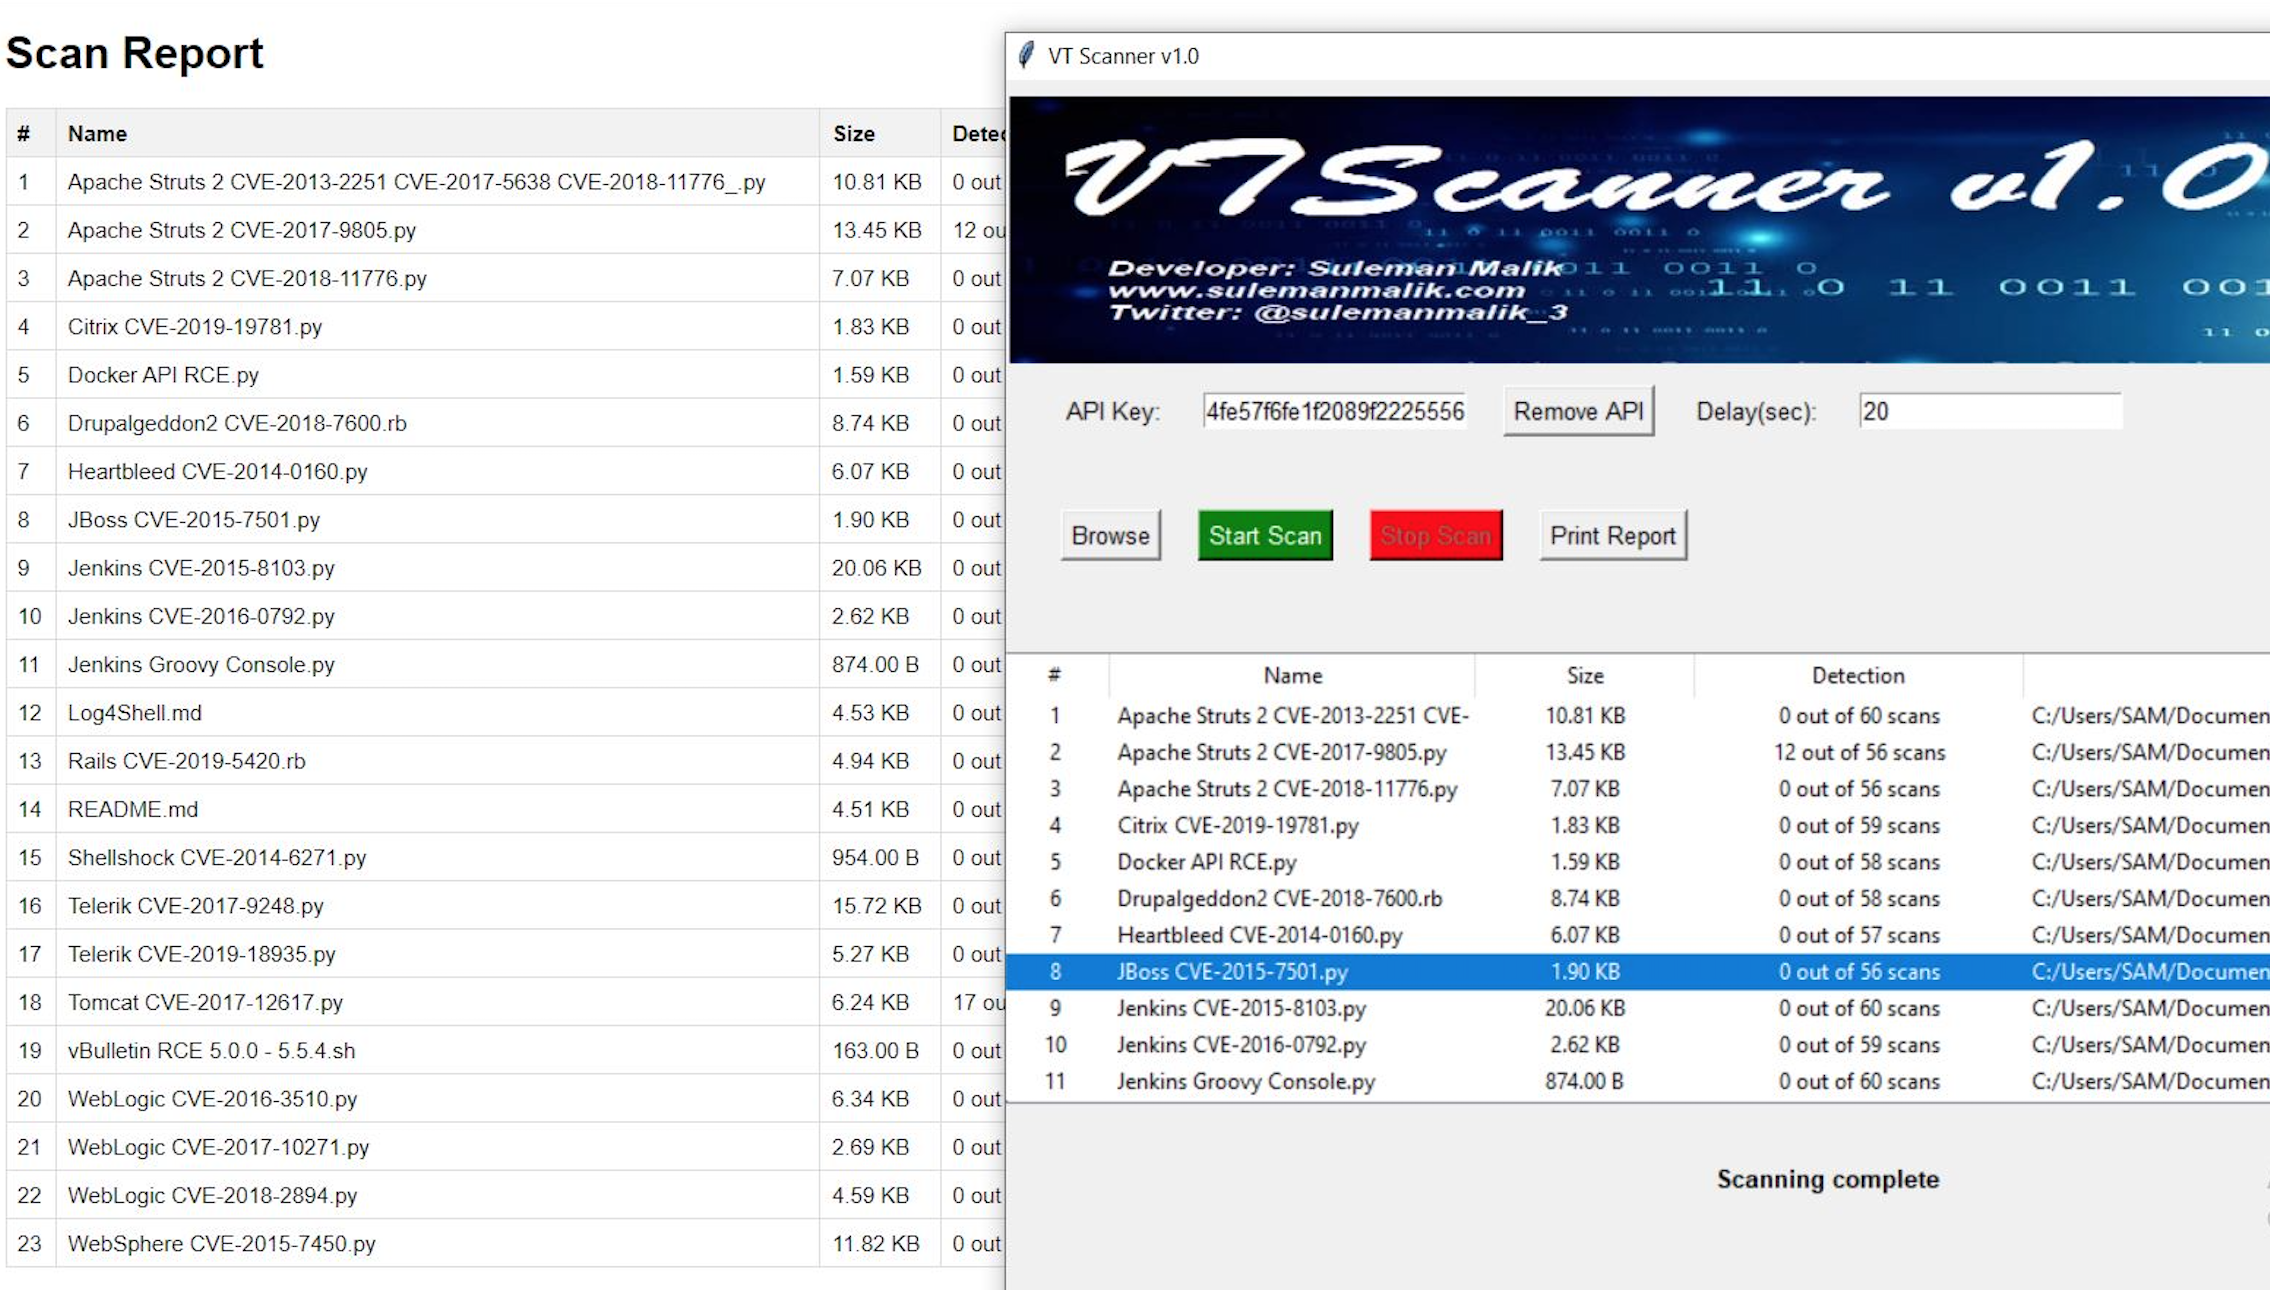 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
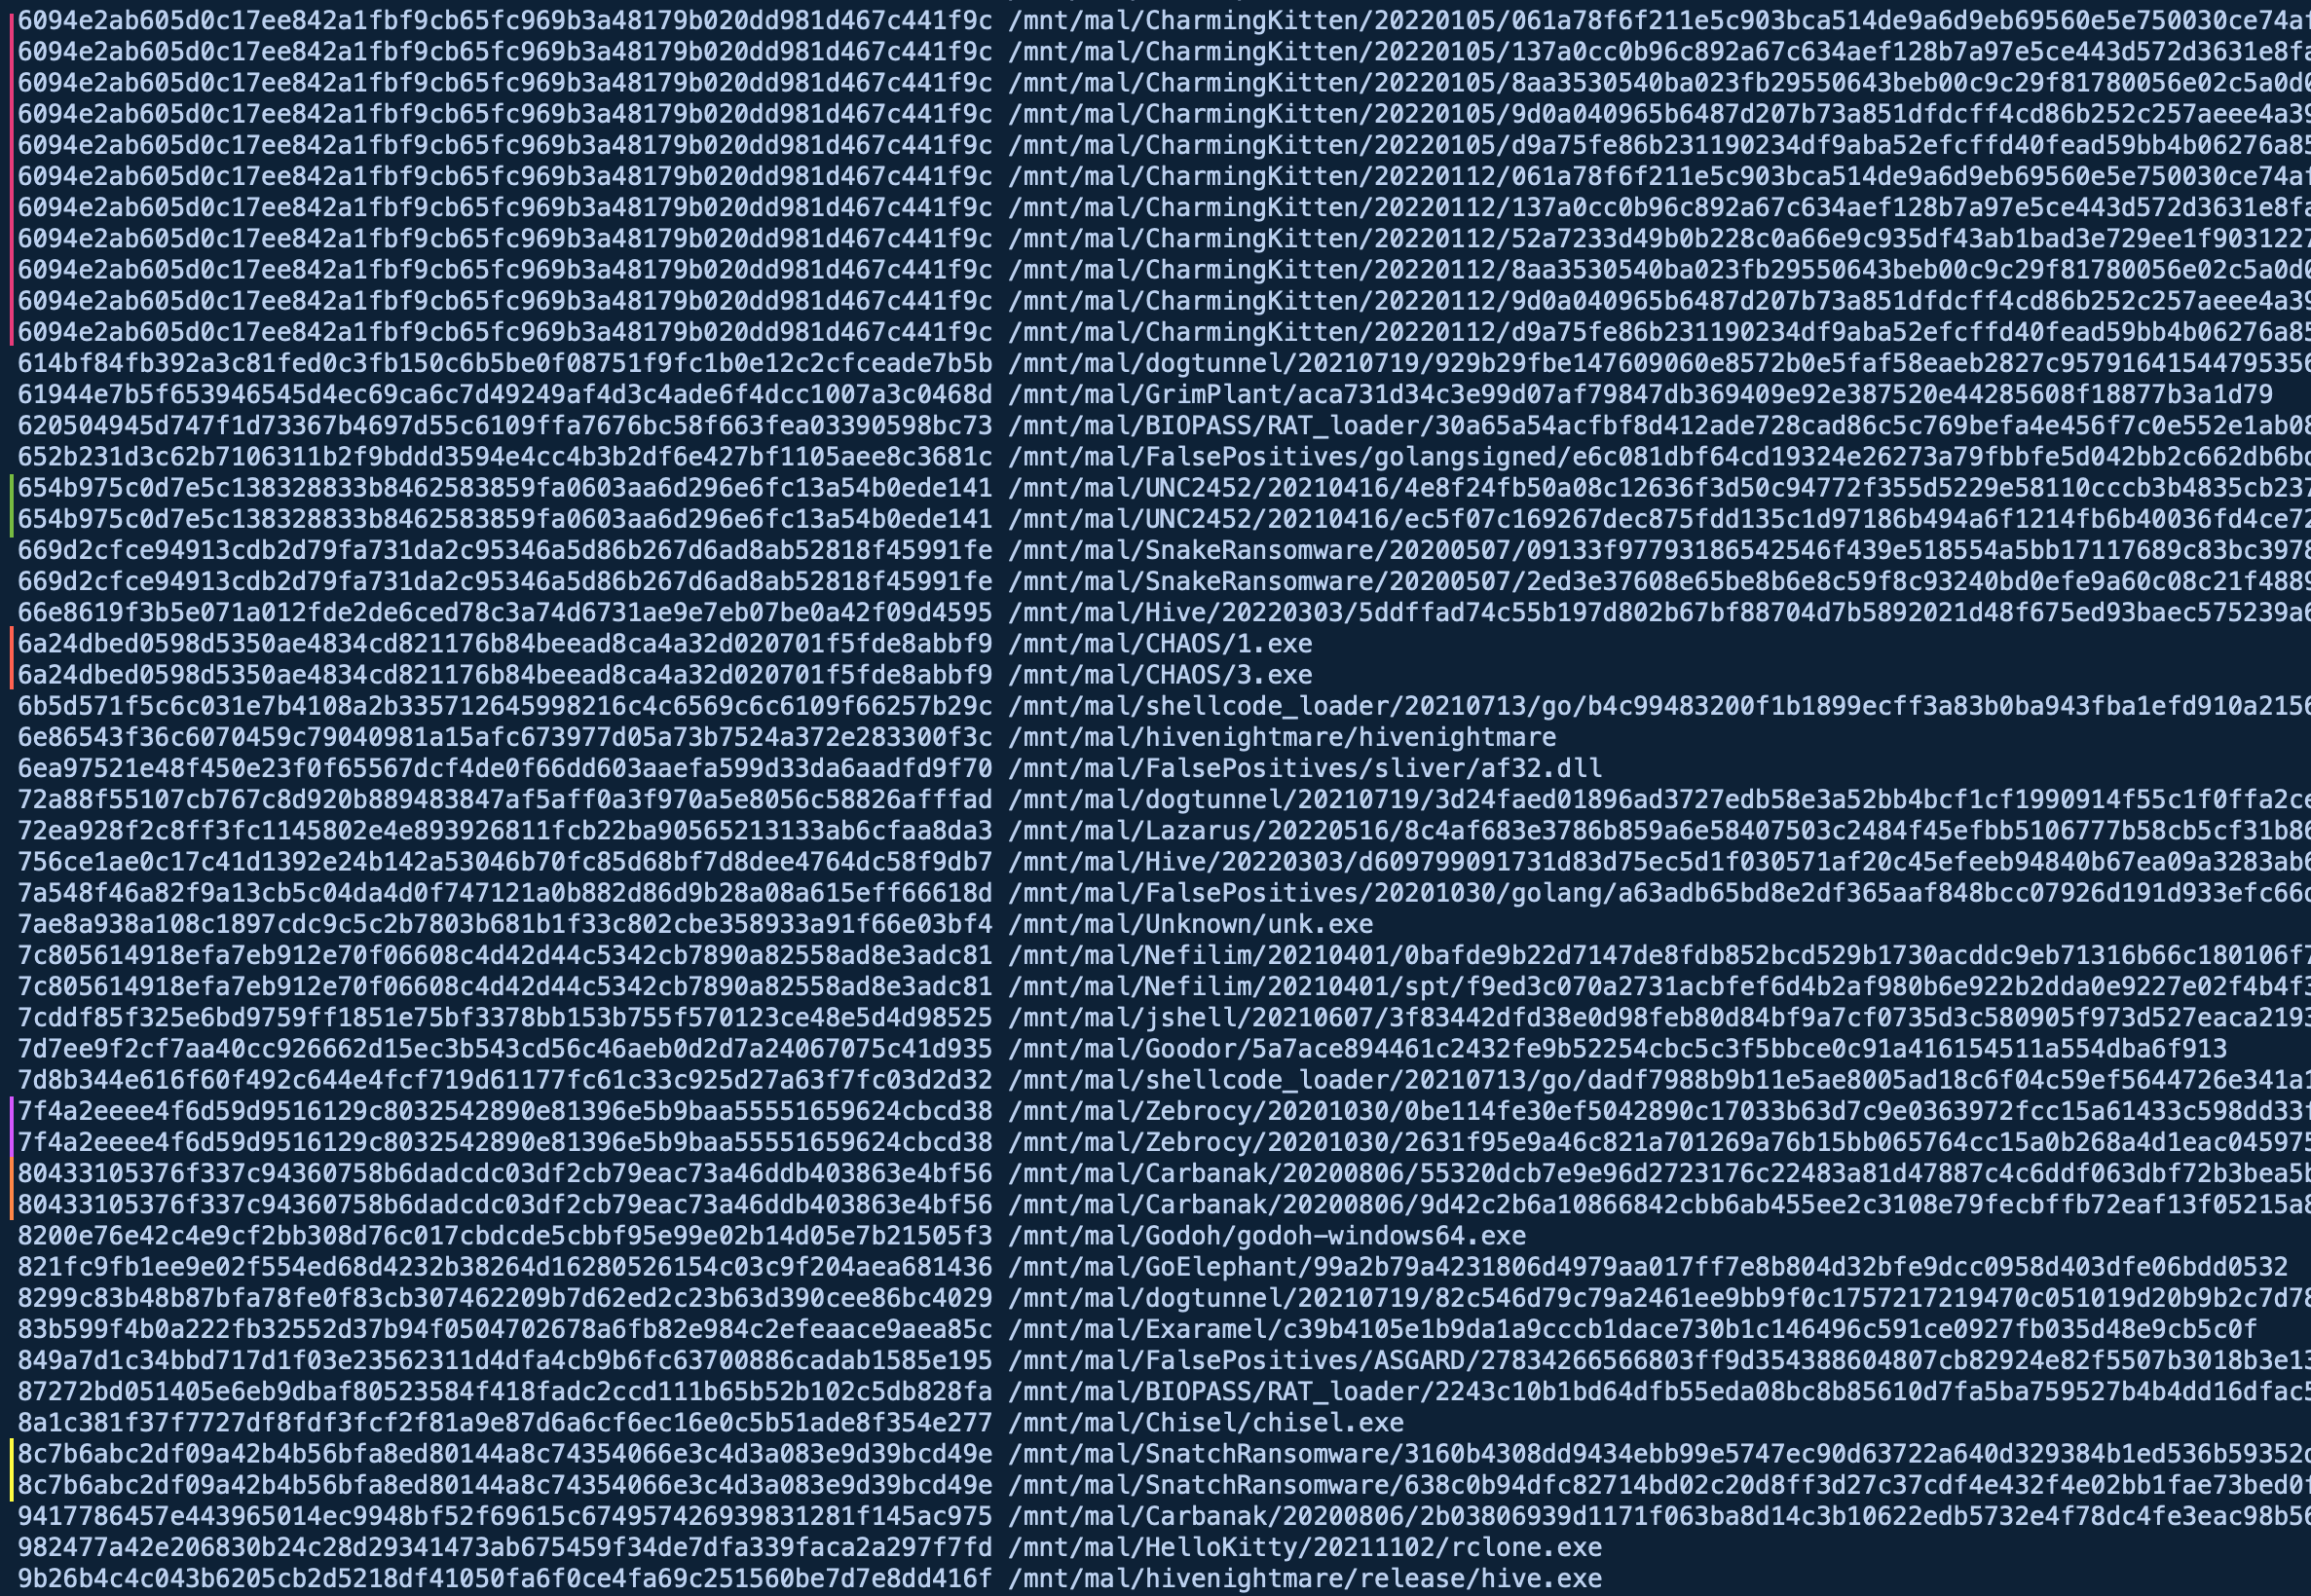 nextronsystems/gimphash
Imphash-like calculation on Golang binaries