Windows-SignedBinary

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…

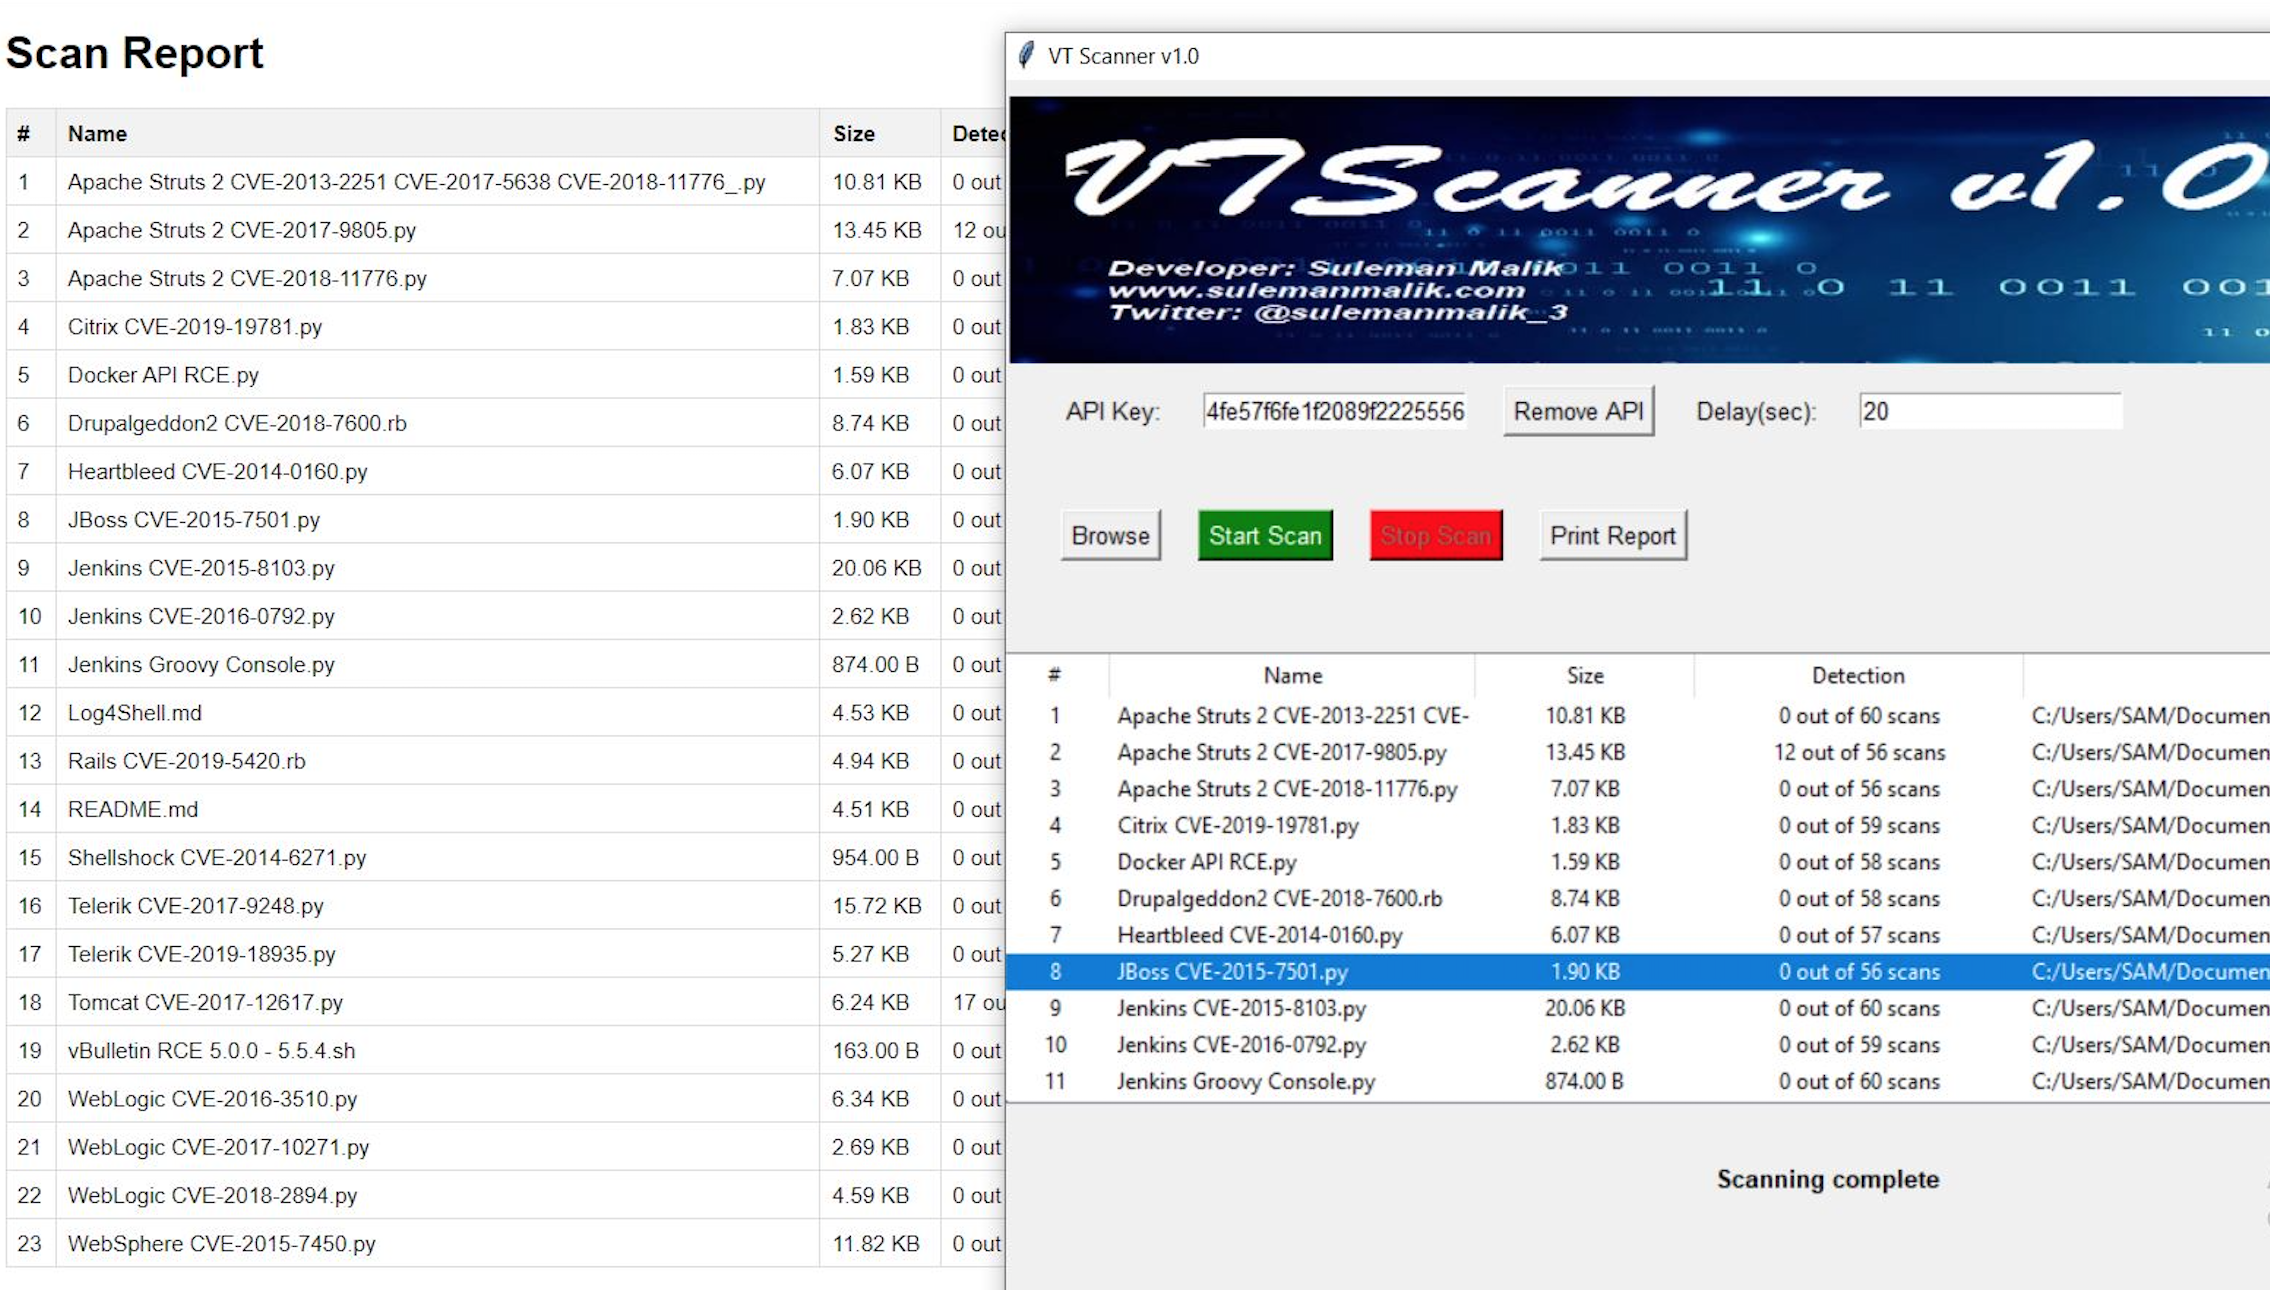
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.

Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.

The SOC Analysts all-in-one CLI tool to automate and speed up workflow.

A Pythonic interface and command line tool for interacting with the InQuest Labs API.

OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…


OSINT tool - gets data from services like shodan, censys etc. in one app

**HashEye** is a powerful Python CLI tool for instantly detecting and analyzing hash types. It provides detailed information about hash formats,…

Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness

PACK (Password Analysis and Cracking Kit)

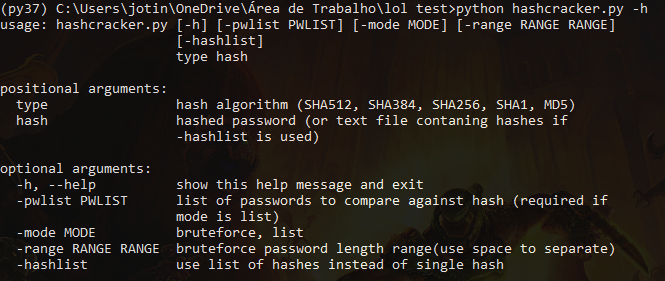
Python-based hash cracker supporting SHA512, SHA256, SHA1, MD5, and more. Features auto-detection of hash type, bruteforce, and password list modes…

All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.

Automater - IP URL and MD5 OSINT Analysis

A malware analysis and classification tool.

Hash-based malware scanner for incident response. Scans files recursively using known malware hashes, supports multithreading, extension filtering,…

Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.

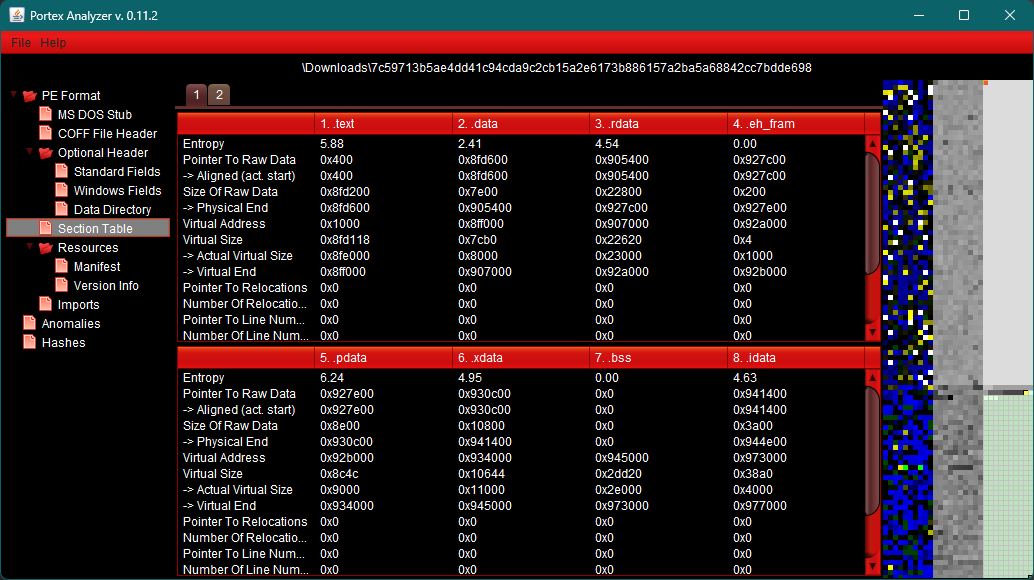
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library