
 aabysszg/hashdump-bypassedr
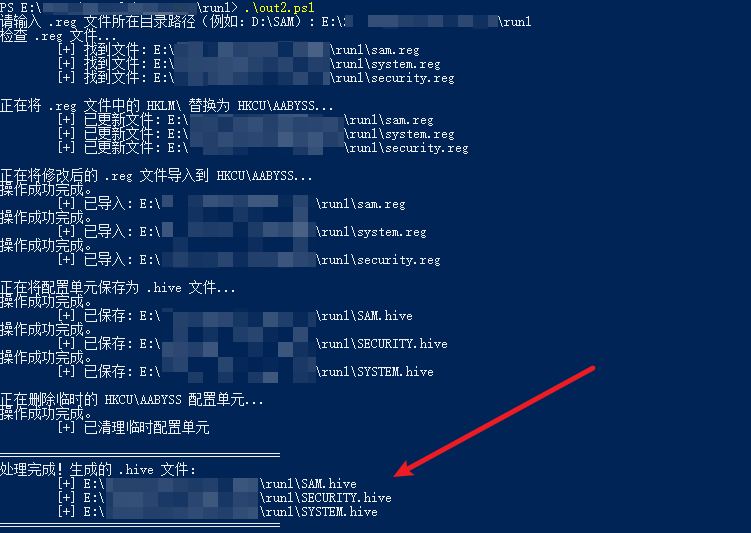
Windows绕过EDR实现DumpHash
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 keithjjones/fileintel
A modular Python application to pull intelligence about malicious files
 netspooky/inhale
A malware analysis and classification tool.
 jehadalqurashi/blackdir-framework
Web Application Vulnerability Scanner
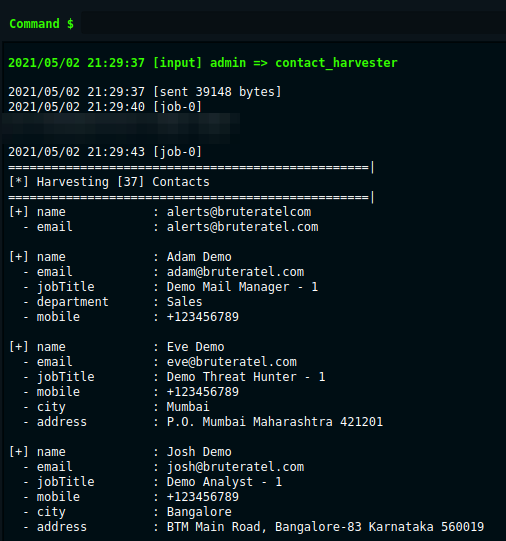 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
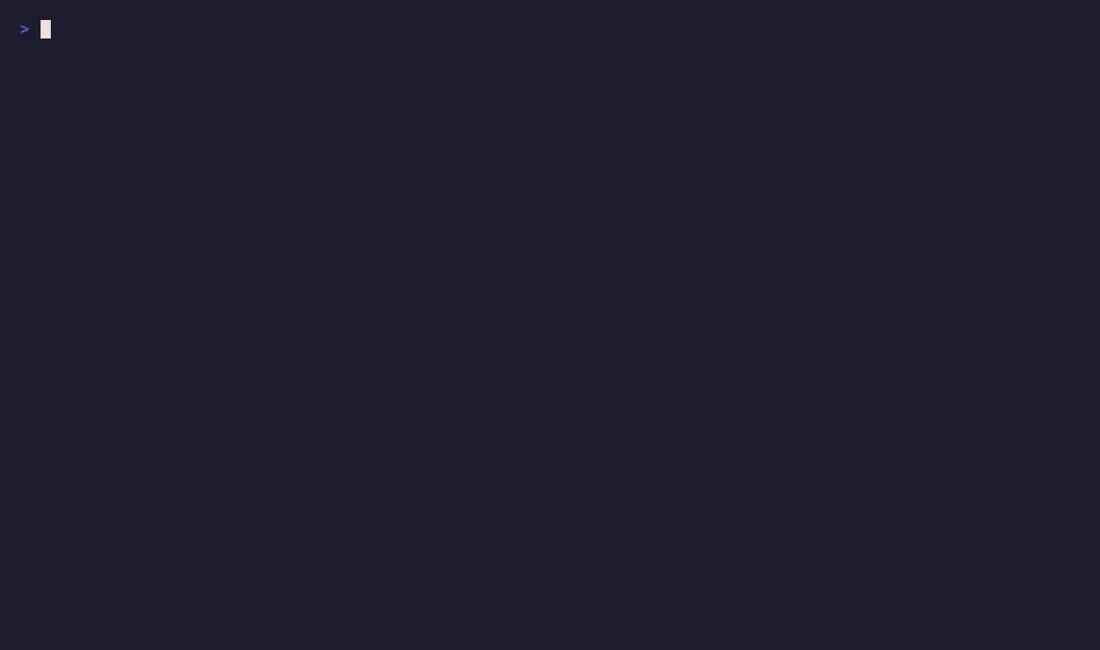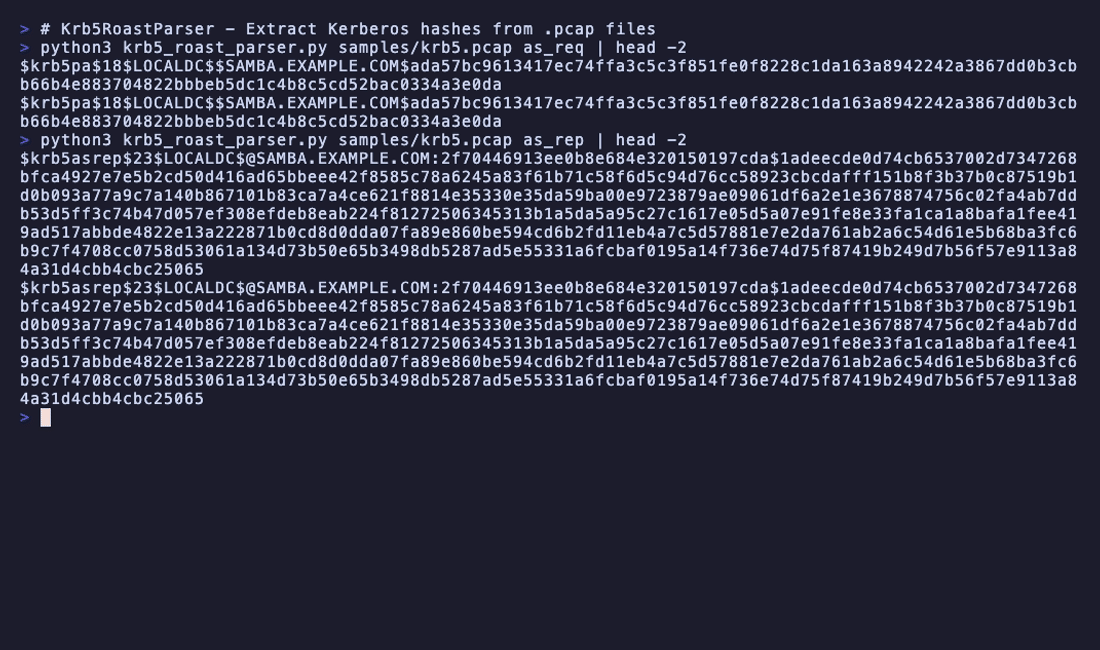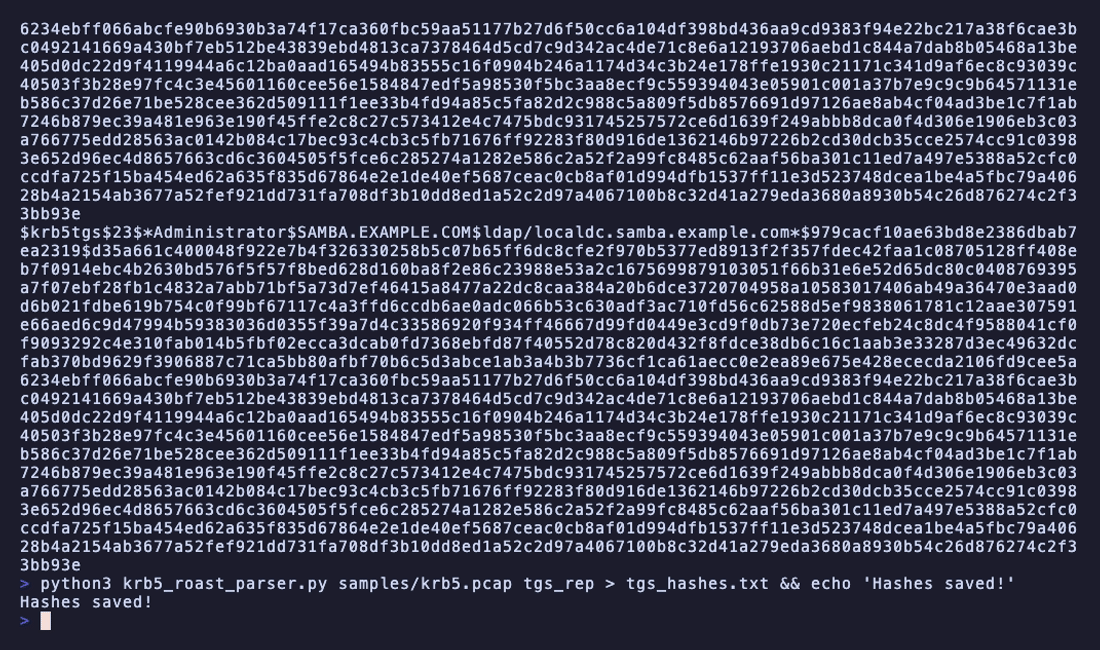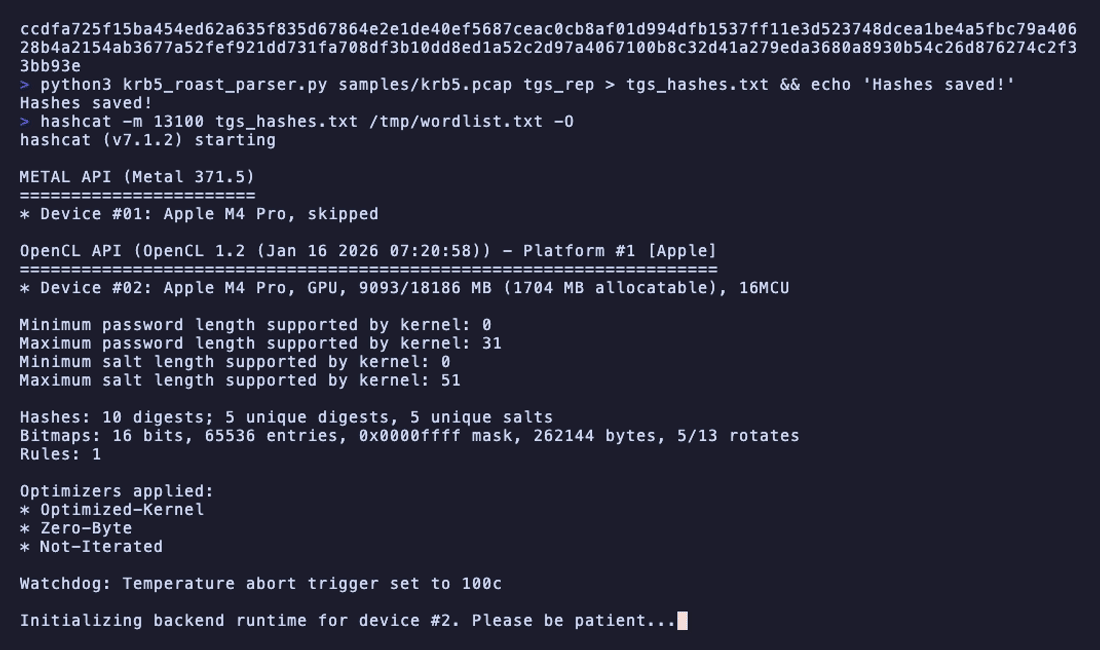 jalvarezz13/krb5roastparser
KrbRoastParser is a tool for parsing Kerberos packets from pcap files to extract AS-REQ, AS-REP and TGS-REP hashes
 sensepost/assless-chaps
Crack MSCHAPv2 challenge/responses quickly using a database of NT hashes
 buybitart/cyclepatrol
Bash tool for on-foot Wi-Fi security checks in a loop, with evidence reports. (re-invented wifi WarDriving)
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
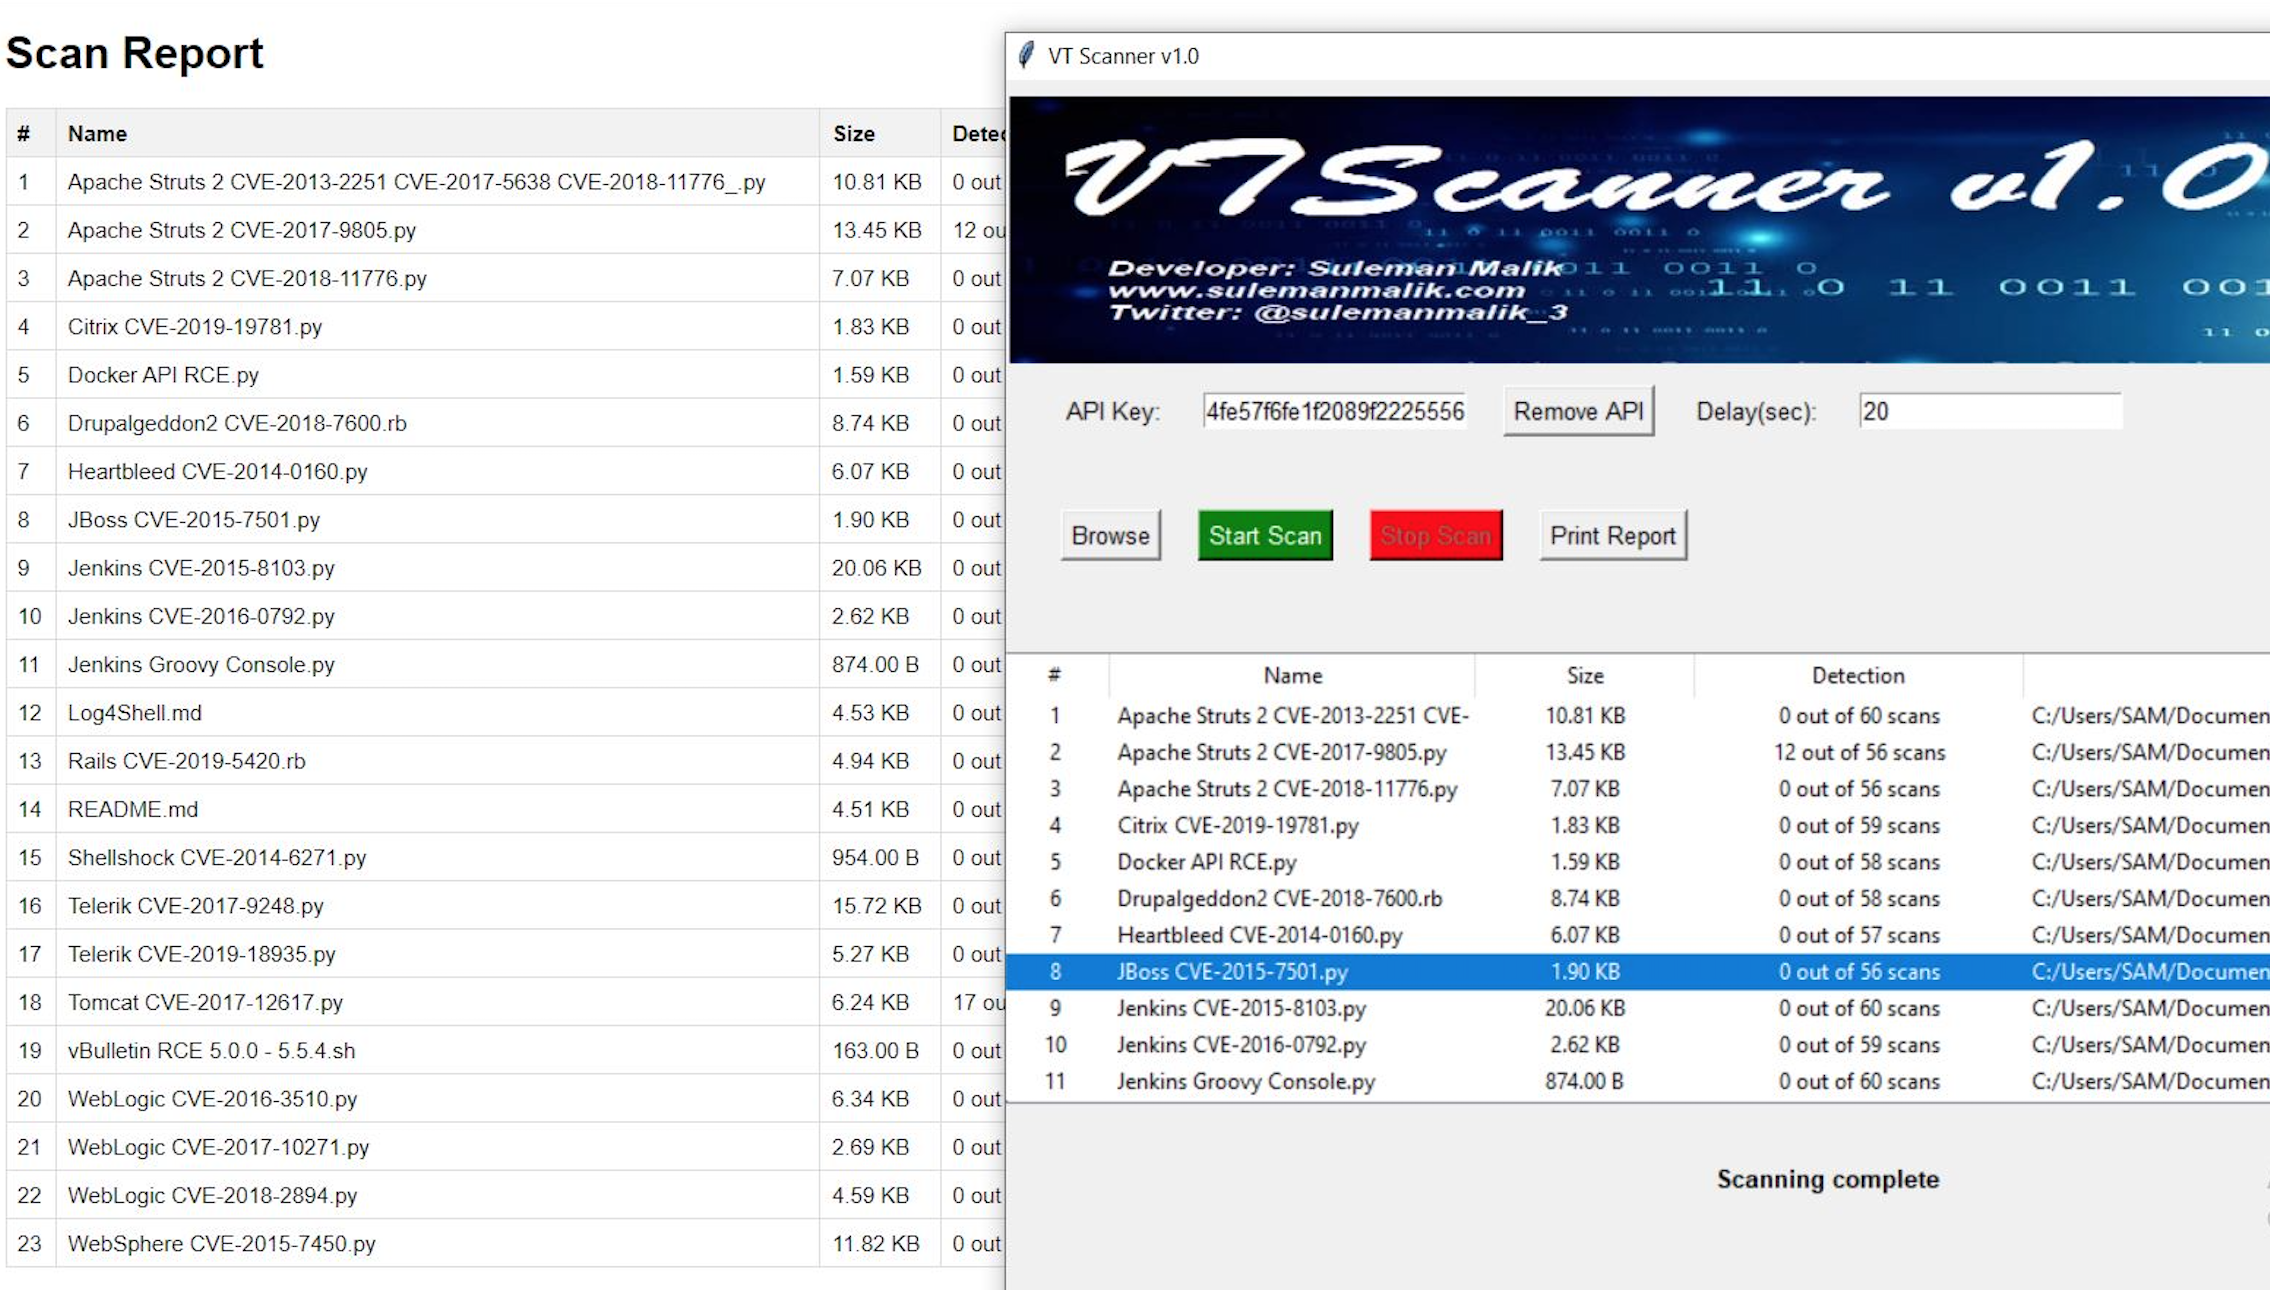 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
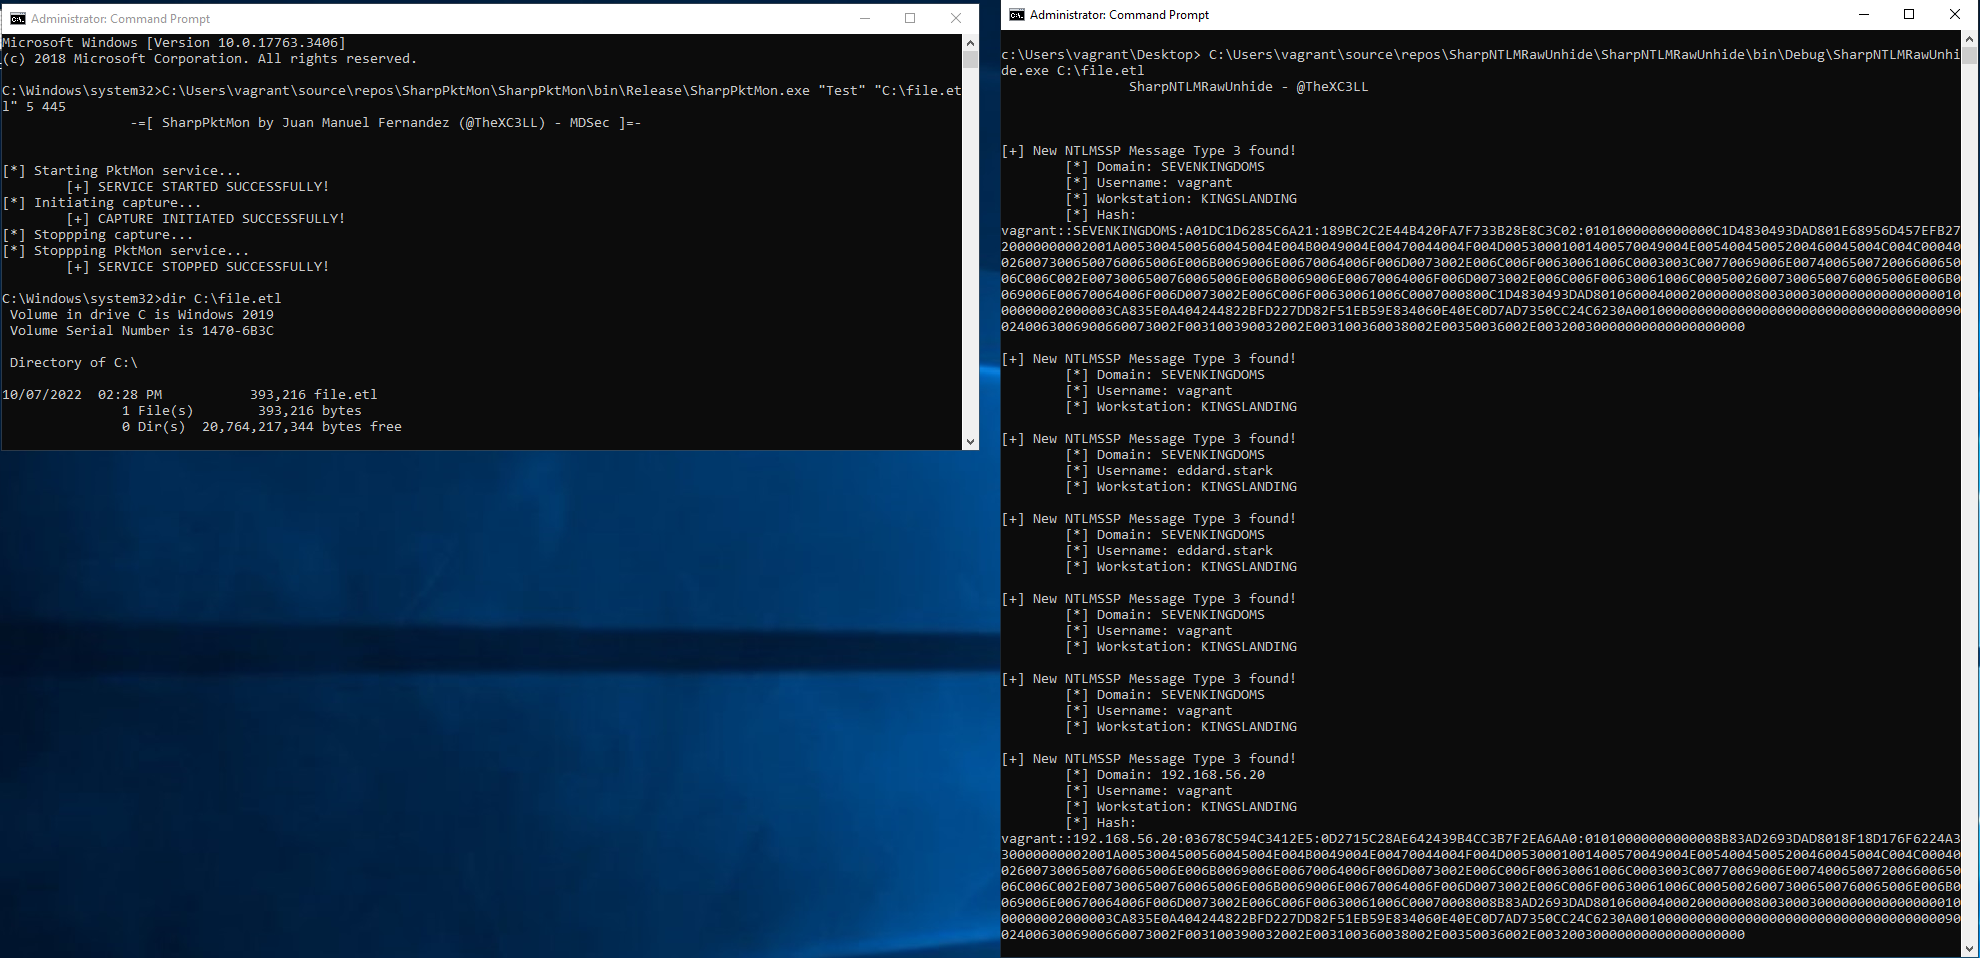 x-c3ll/sharpntlmrawunhide
C# version of NTLMRawUnHide
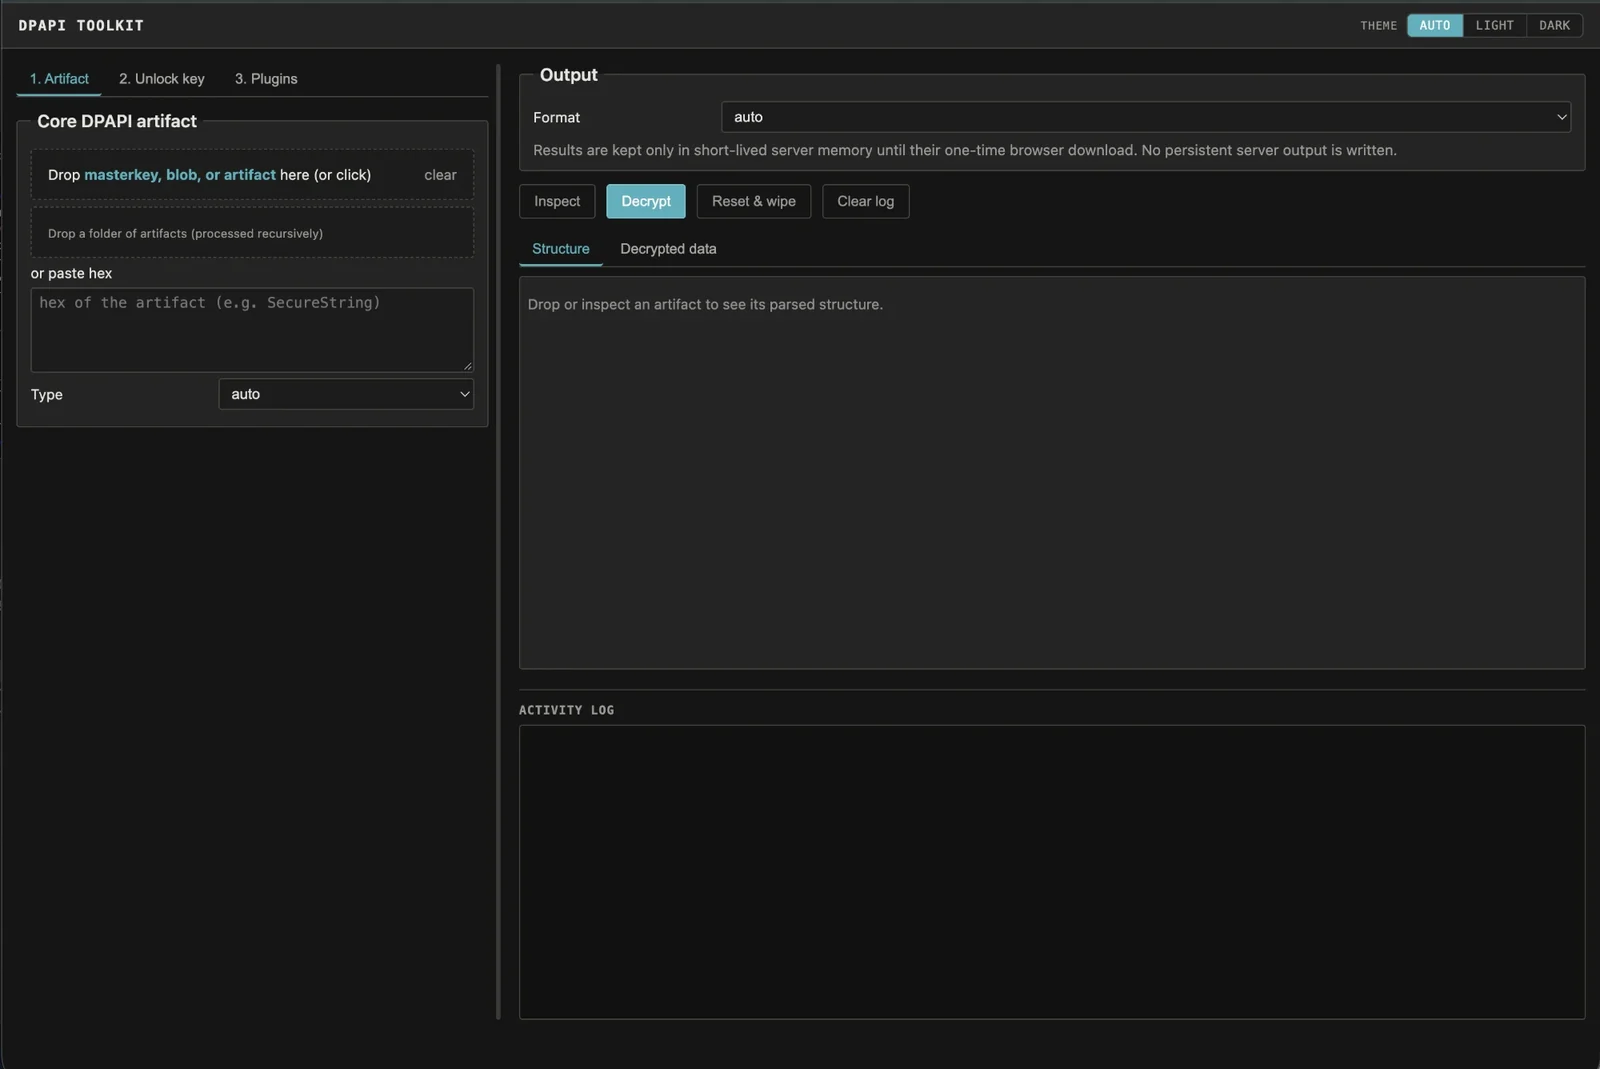 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.