

IPED
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
3.1k
sepinf-inc/ipedIPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
 hashcat/hashcat
World's fastest and most advanced password recovery utility
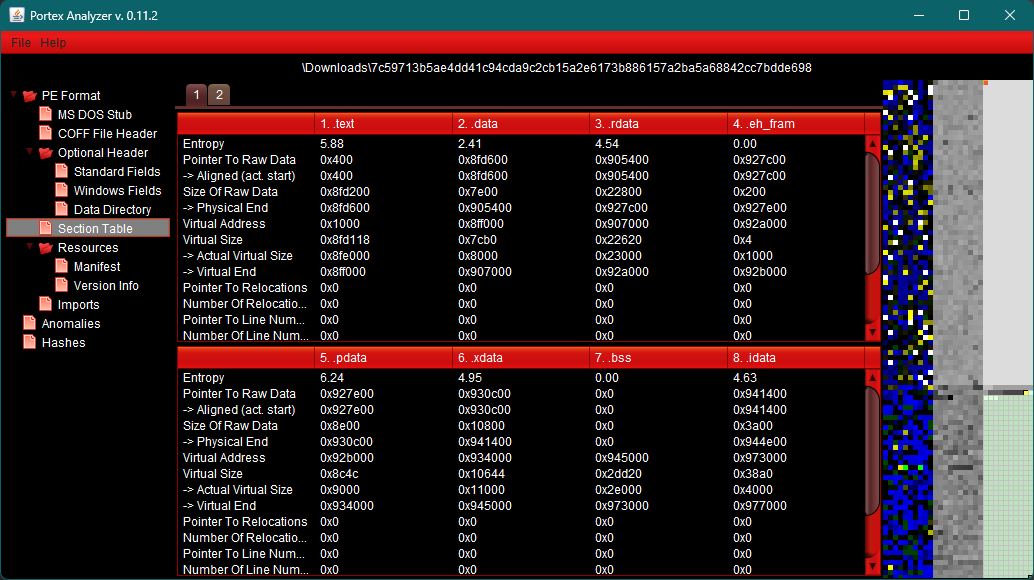 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
 badkeys/badkeys
Tool to find common vulnerabilities in cryptographic public keys
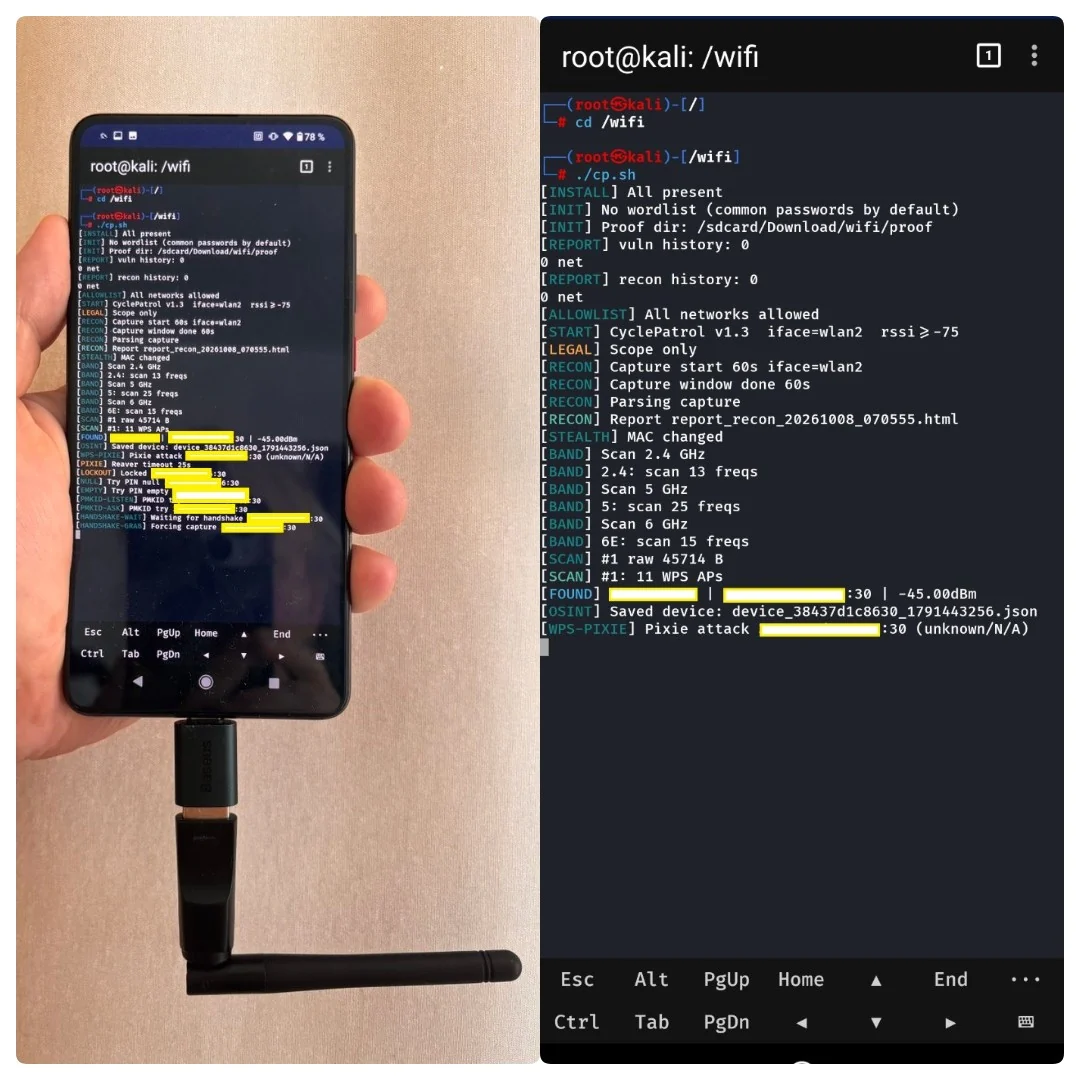 buybitart/cyclepatrol
Bash tool for on-foot Wi-Fi security checks in a loop, with evidence reports. (re-invented wifi WarDriving)
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 blake3-team/blake3
Fast cryptographic hash function with PRF, MAC, KDF, and XOF modes. Supports verified streaming, incremental updates, and parallelized hashing via…
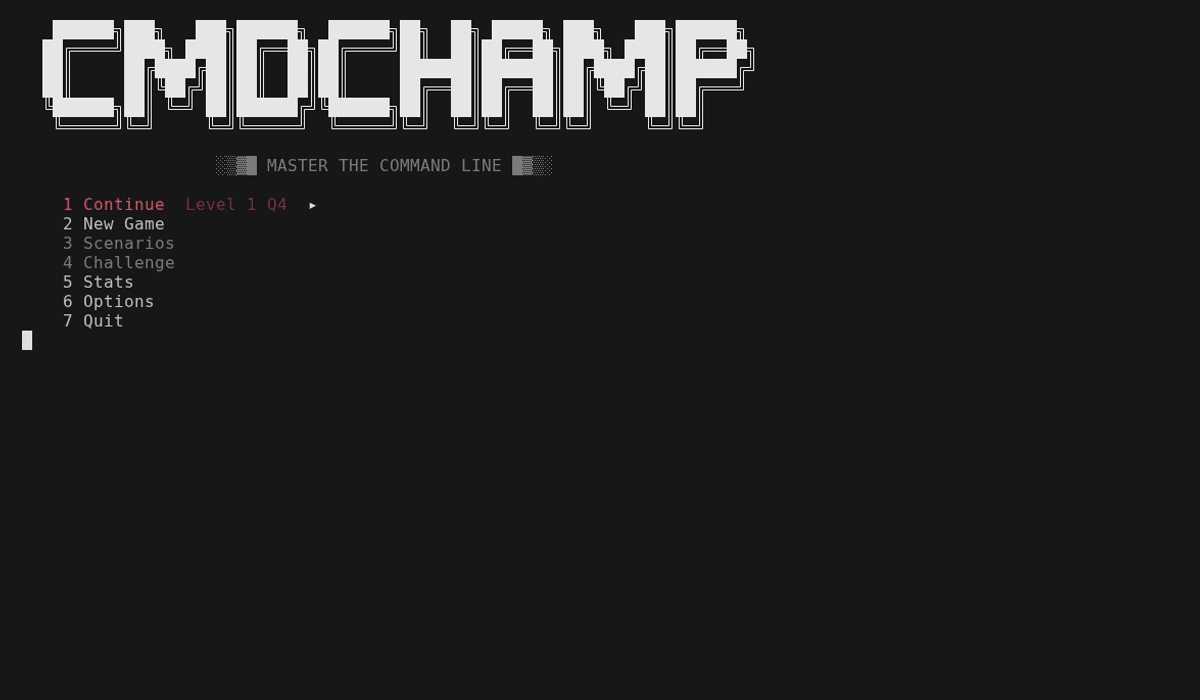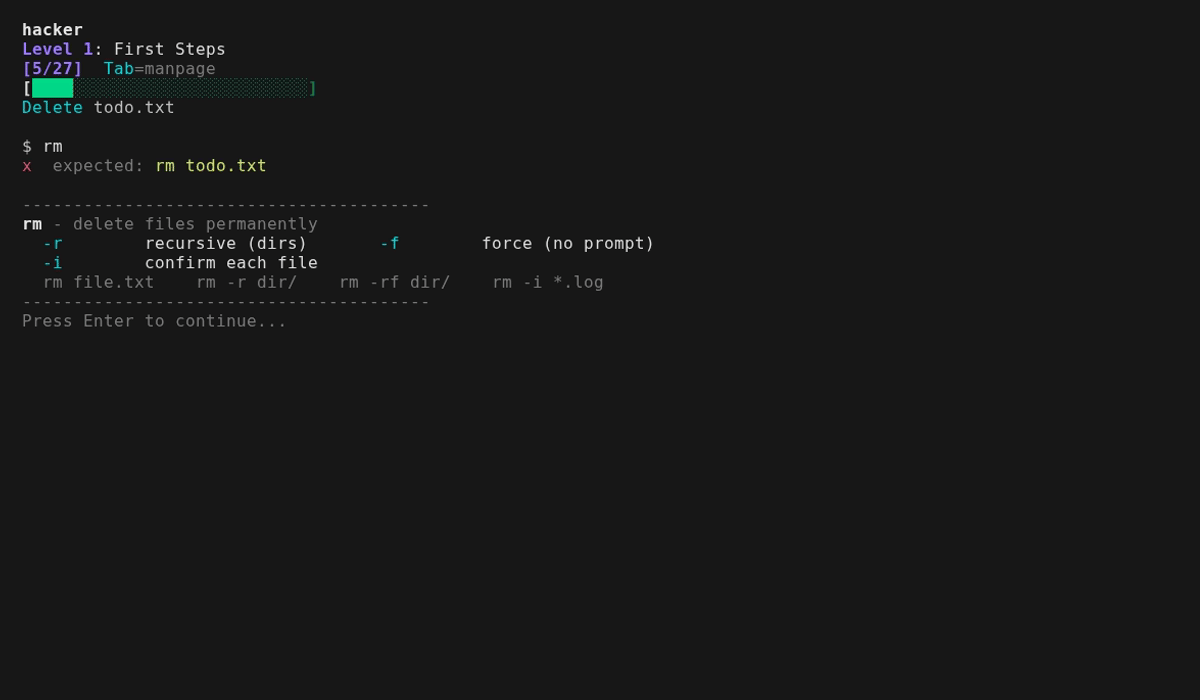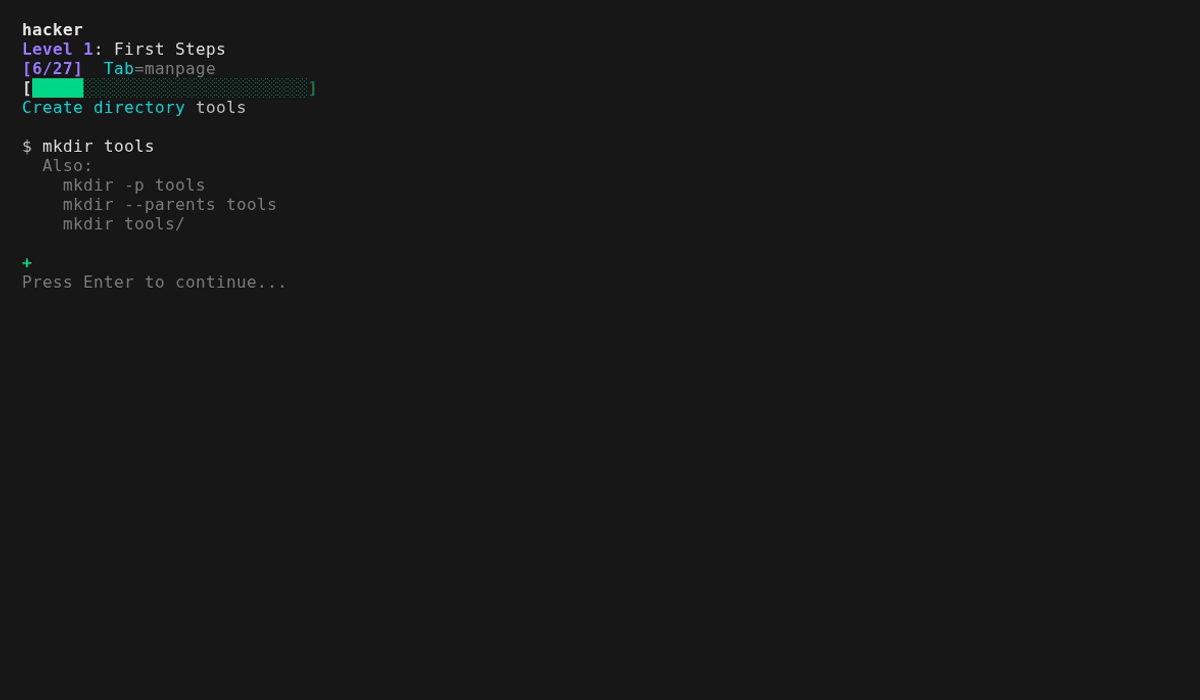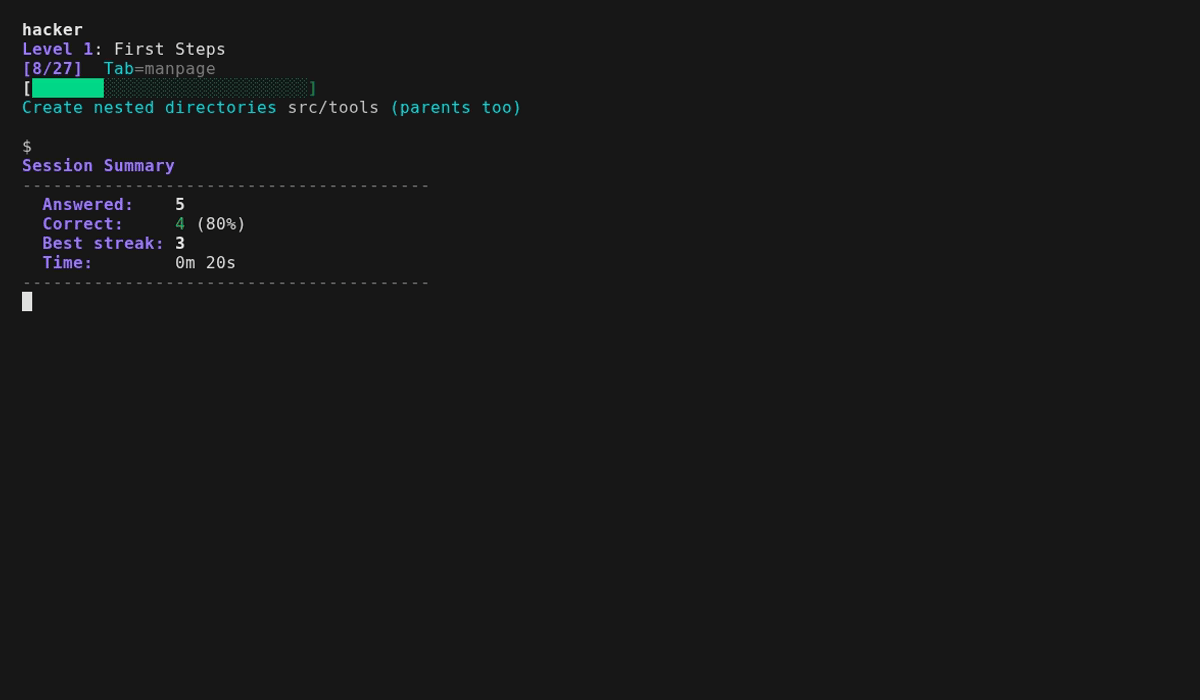 mellen9999/cmdchamp
bash CLI trainer — 30 levels from ls to privilege escalation
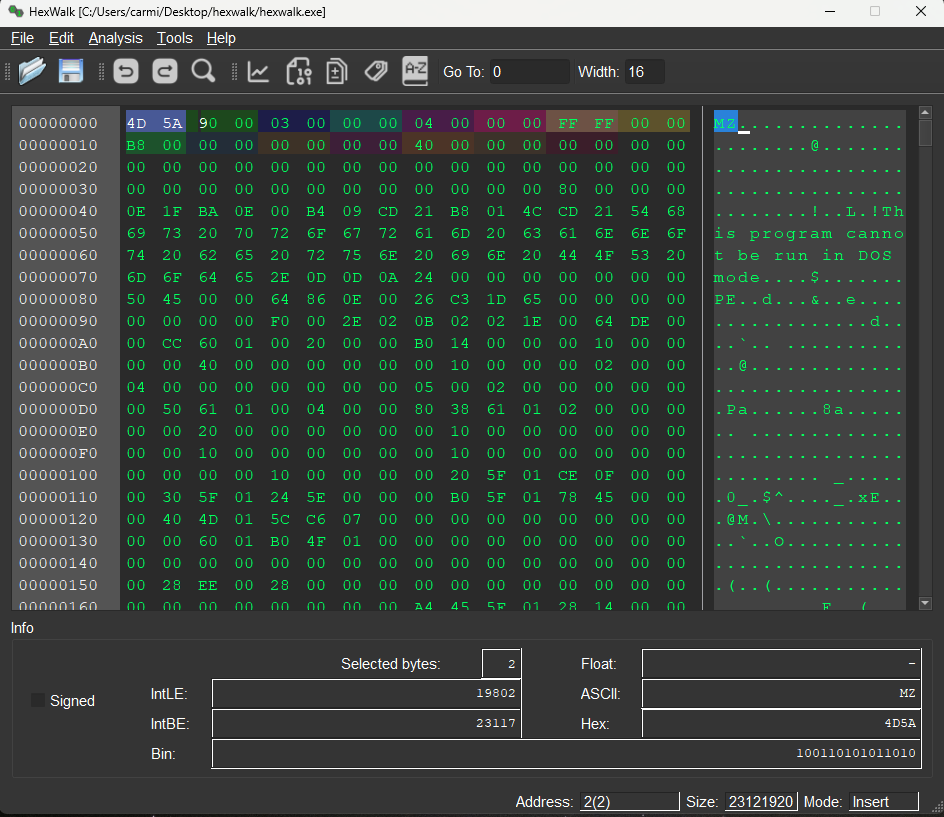 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 0xbekoo/cve-2026-8863
Hashes and shim versions for the UEFI Secure Boot shims affected by CVE-2026-8863
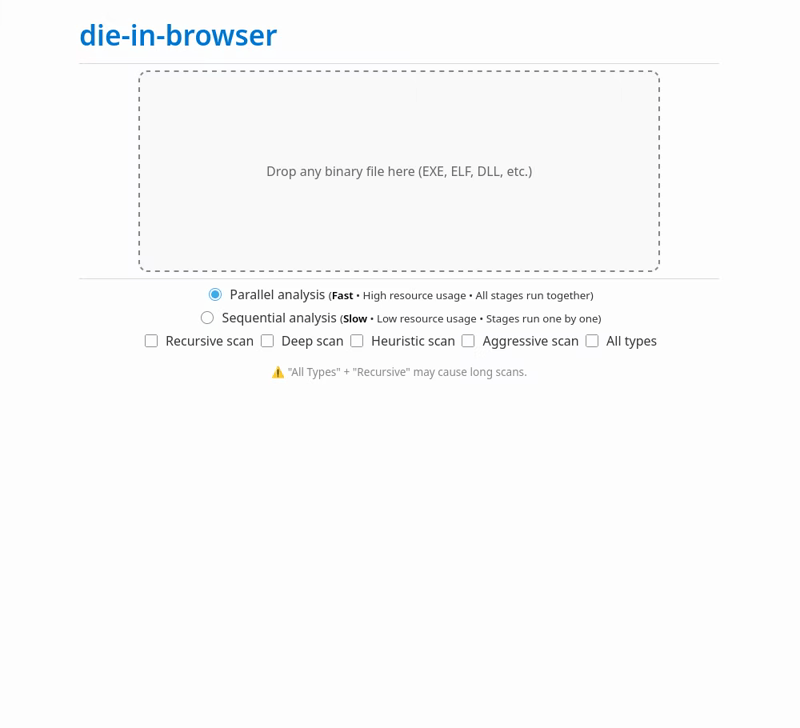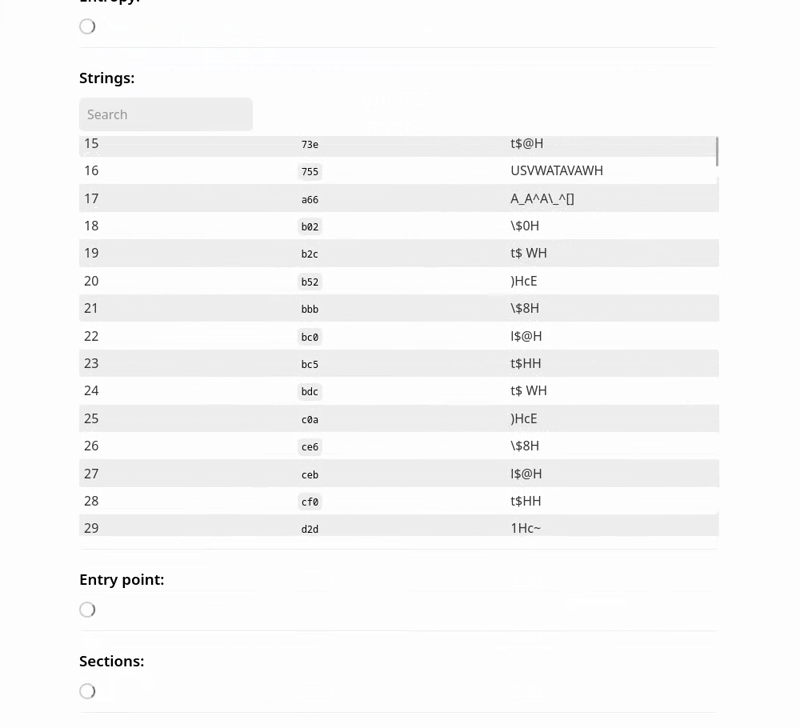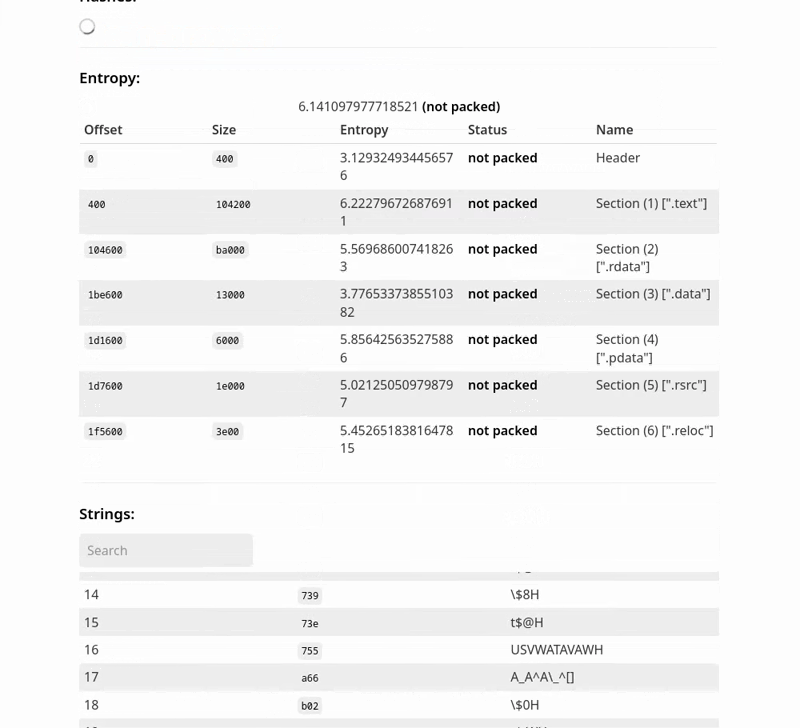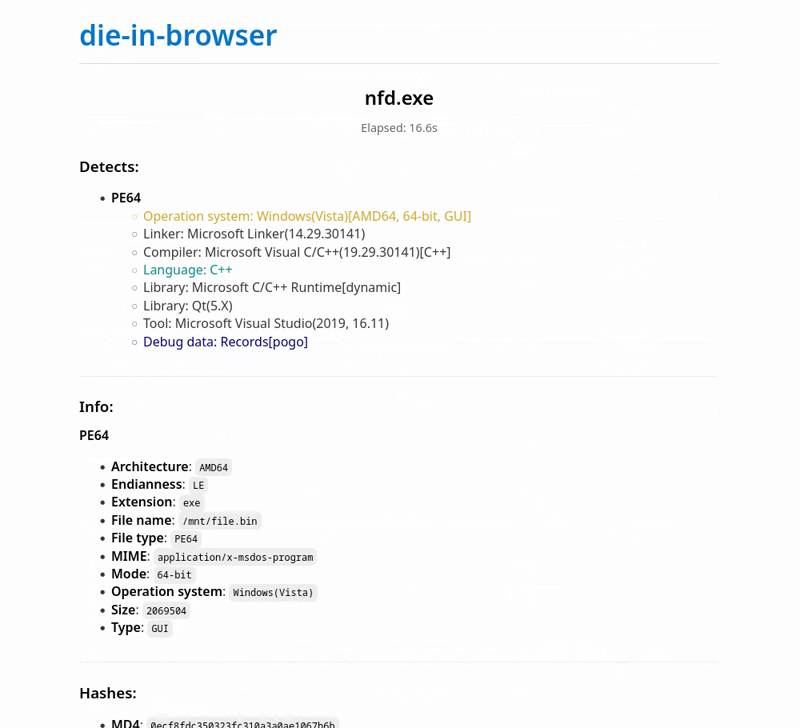 xoreaxlmbdx/die-in-browser
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
 microsoft/symcrypt-openssl
OpenSSL engine for use with SymCrypt cryptographic library
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
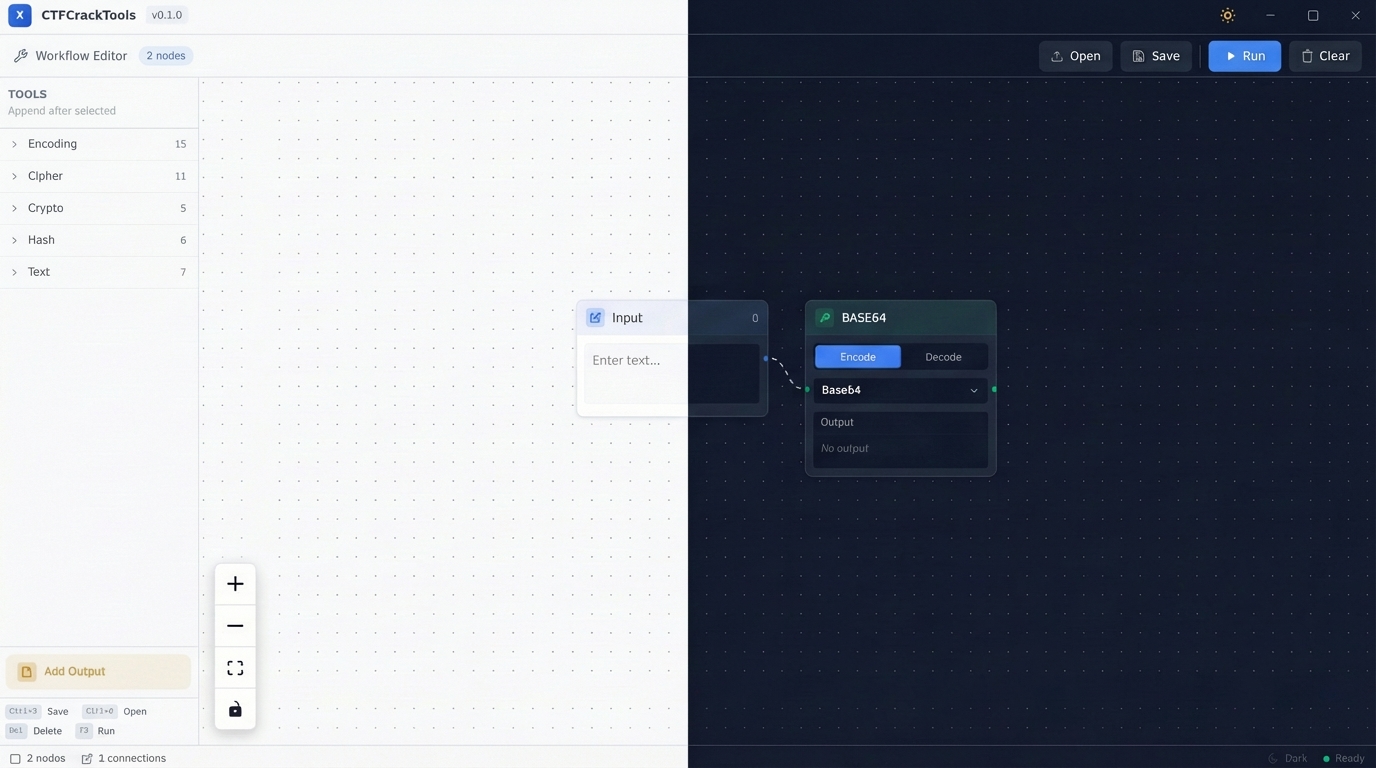 0chencc/ctfcracktools
The next-generation CTF Swiss Army Knife powered by Rust & Tauri. Features a visual node-based workflow and local AI intelligence for extreme…
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…