
IDAChef
 exporx/idachef
CyberChef-style recipe toolkit for IDA Pro: chain 289 encoding, cipher, compression, and hashing operations on database bytes, then patch results…
binary-analysiscode-analysiscryptography+6
exporx/idachefCyberChef-style recipe toolkit for IDA Pro: chain 289 encoding, cipher, compression, and hashing operations on database bytes, then patch results…
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 aide/aide
File integrity monitoring tool that detects unauthorized changes to monitored files and directories using attribute checks, multiple hash algorithms,…
 didierstevens/didierstevenssuite
Collection of Python scripts for malware analysis, file format parsing, hashing, and forensic triage, including PDF, OLE, and XOR analysis utilities.
 buybitart/cyclepatrol
Bash tool for on-foot Wi-Fi security checks in a loop, with evidence reports. (re-invented wifi WarDriving)
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 bandrel/hashcatrosetta
Hashcat rule analyzer and interpreter - A Rosetta Stone for decoding hashcat rule syntax
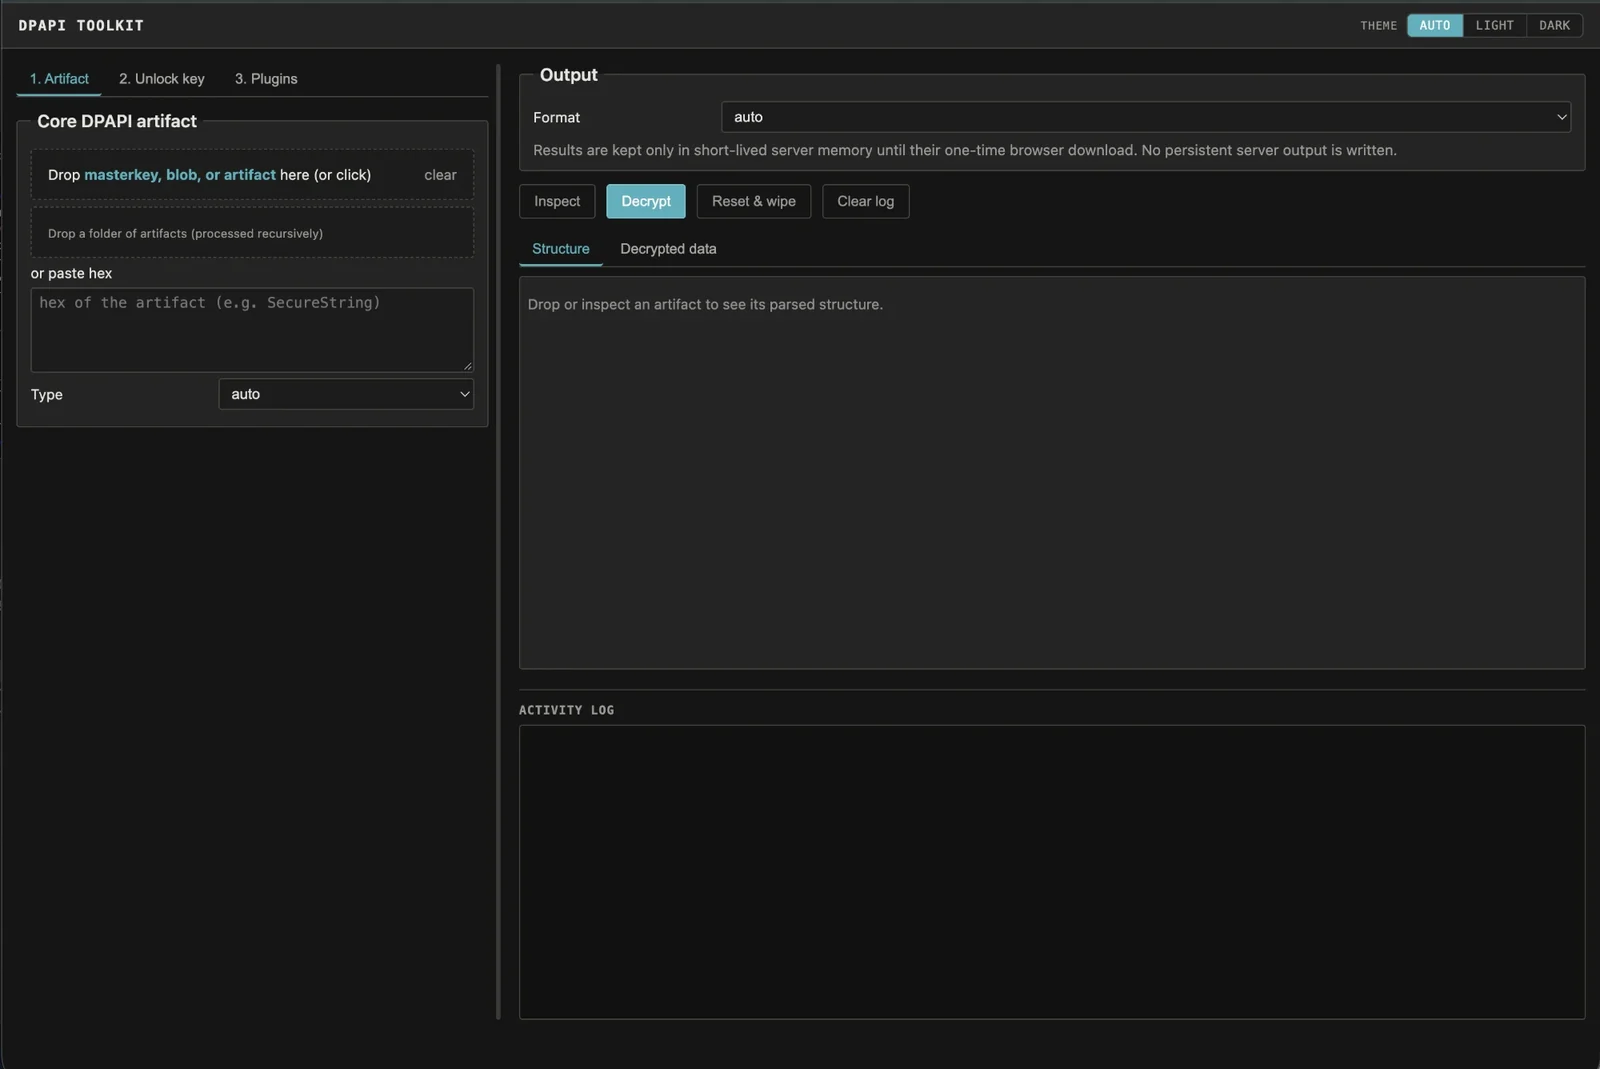 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
 paulmillr/noble-curves
Audited & minimal JS implementation of elliptic curve cryptography.
 t-beckett/h-osint
Local-first, keyboard-driven OSINT workbench for the terminal with 28 modules covering username, domain, IP, email, breach, and geolocation lookups…
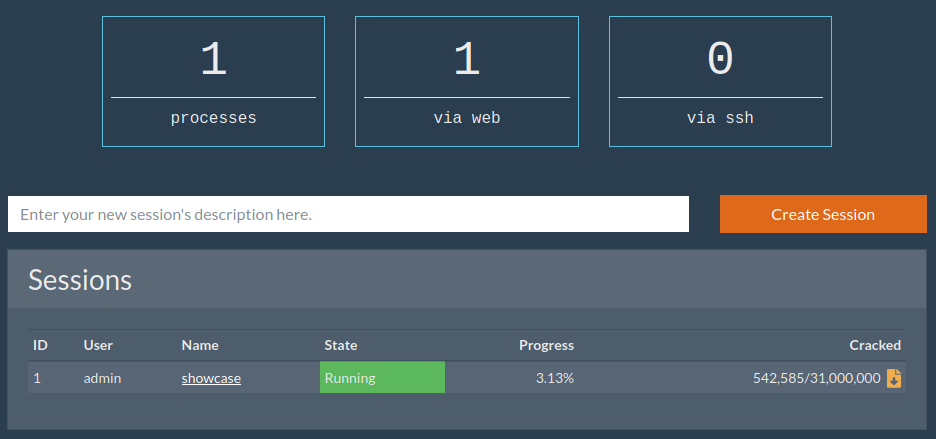 sadreck/crackerjack
Web-based GUI for Hashcat that simplifies password cracking with session management, mask generation, wordlist support, and multi-user access.
 brannondorsey/naive-hashcat
Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…
 frizb/hashcat-cheatsheet
Hashcat reference for OSCP/penetration testing: hash identification, cracking syntax for Linux, Windows, archives, databases, Kerberos tickets, and…
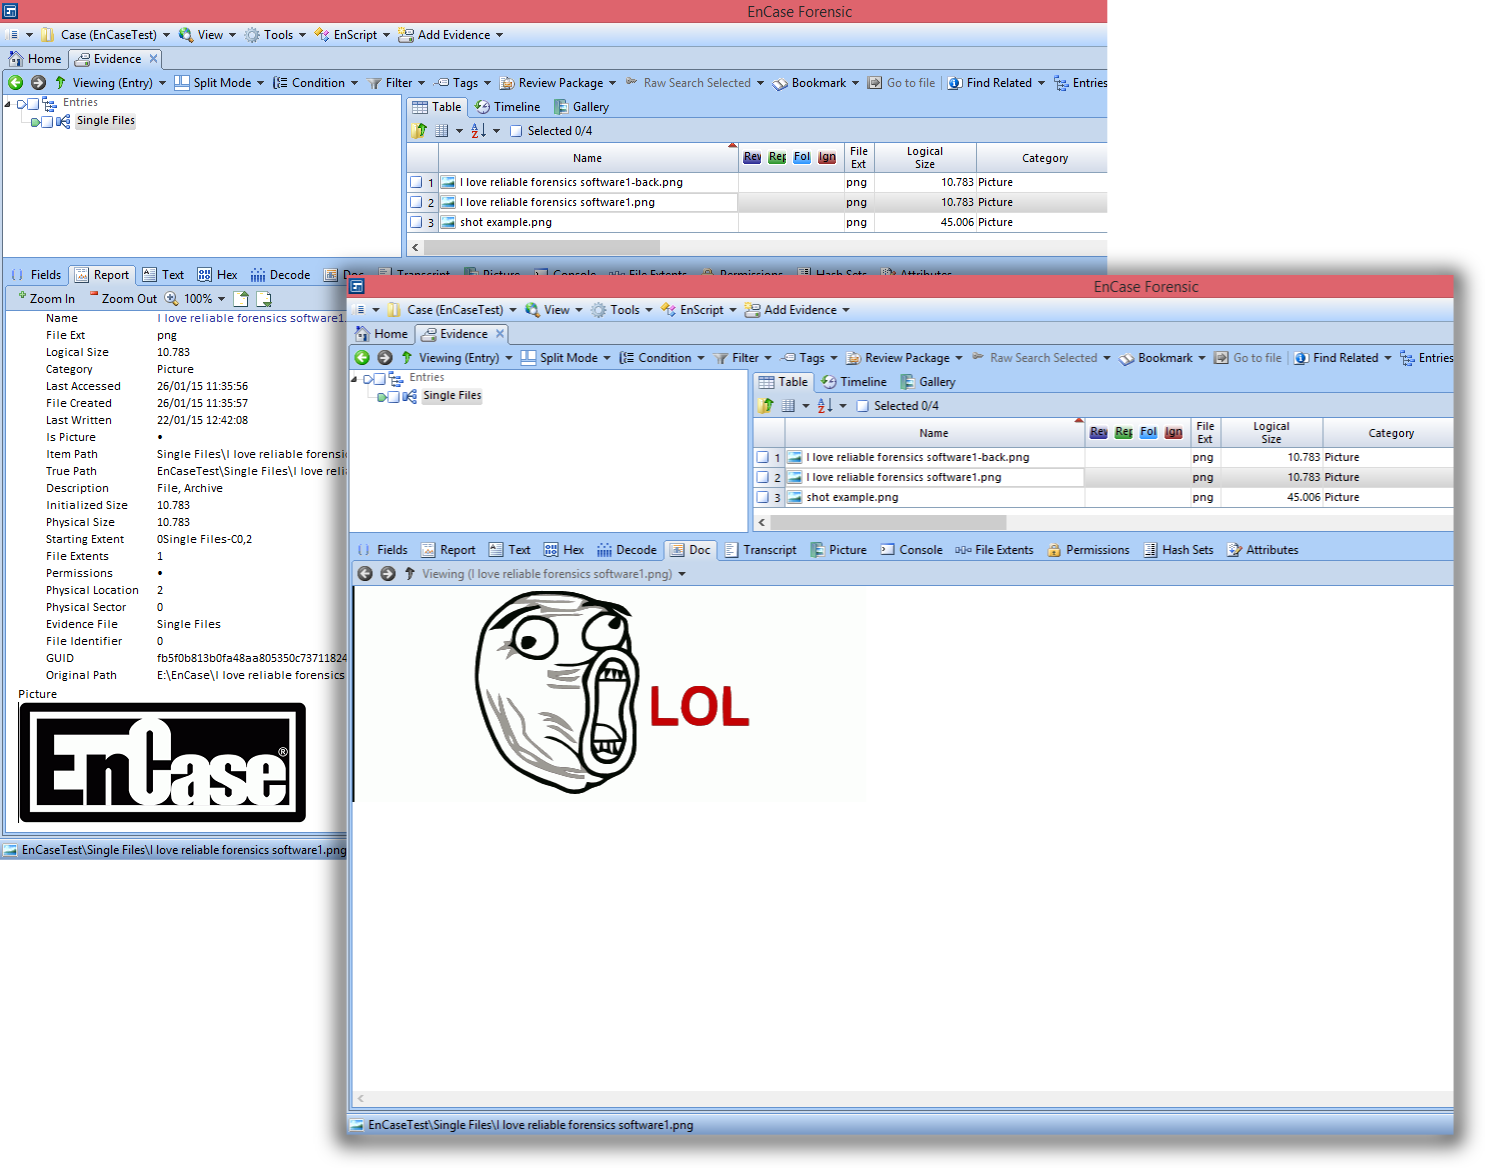
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 abusech/yaraify
Open YARA scan- and search engine