
lab
 chakshugupta13/lab
Code artifacts from research paper implementations
cryptographycurated-resourceseducation+2
chakshugupta13/labCode artifacts from research paper implementations
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…
 fin3ss3g0d/cve-2024-4956
Python utility for automating CVE-2024-4956 path traversal exploitation with mass file extraction, plus custom Hashcat module for cracking Apache…
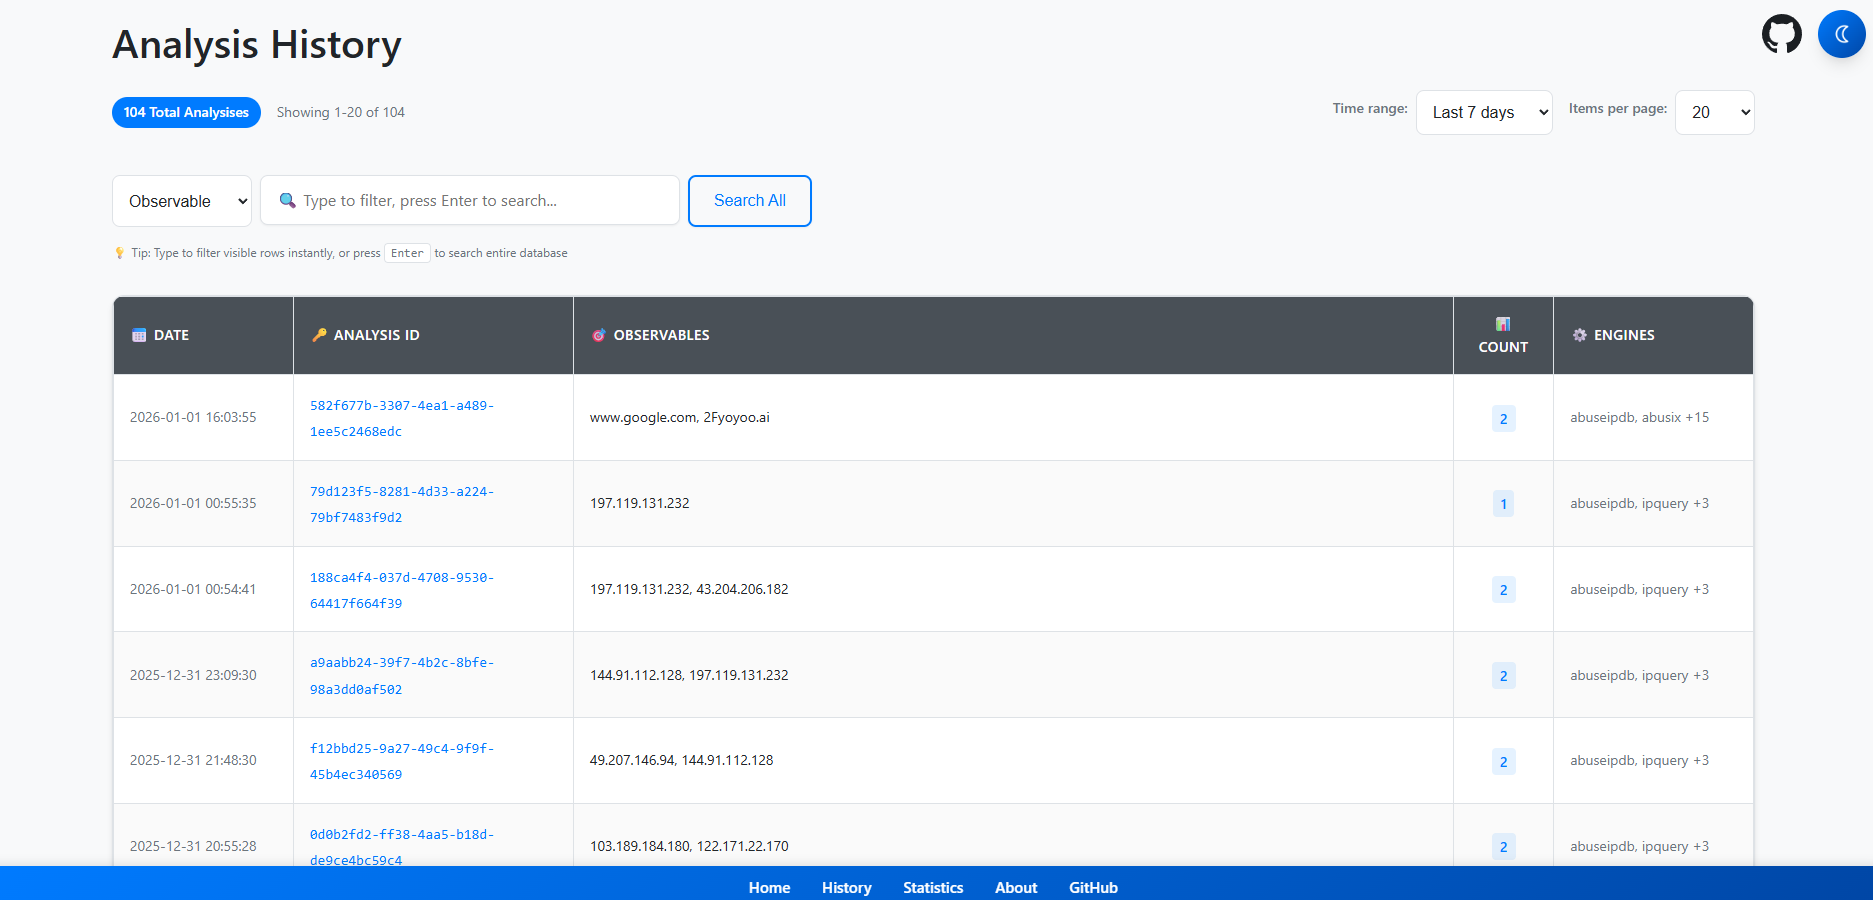 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
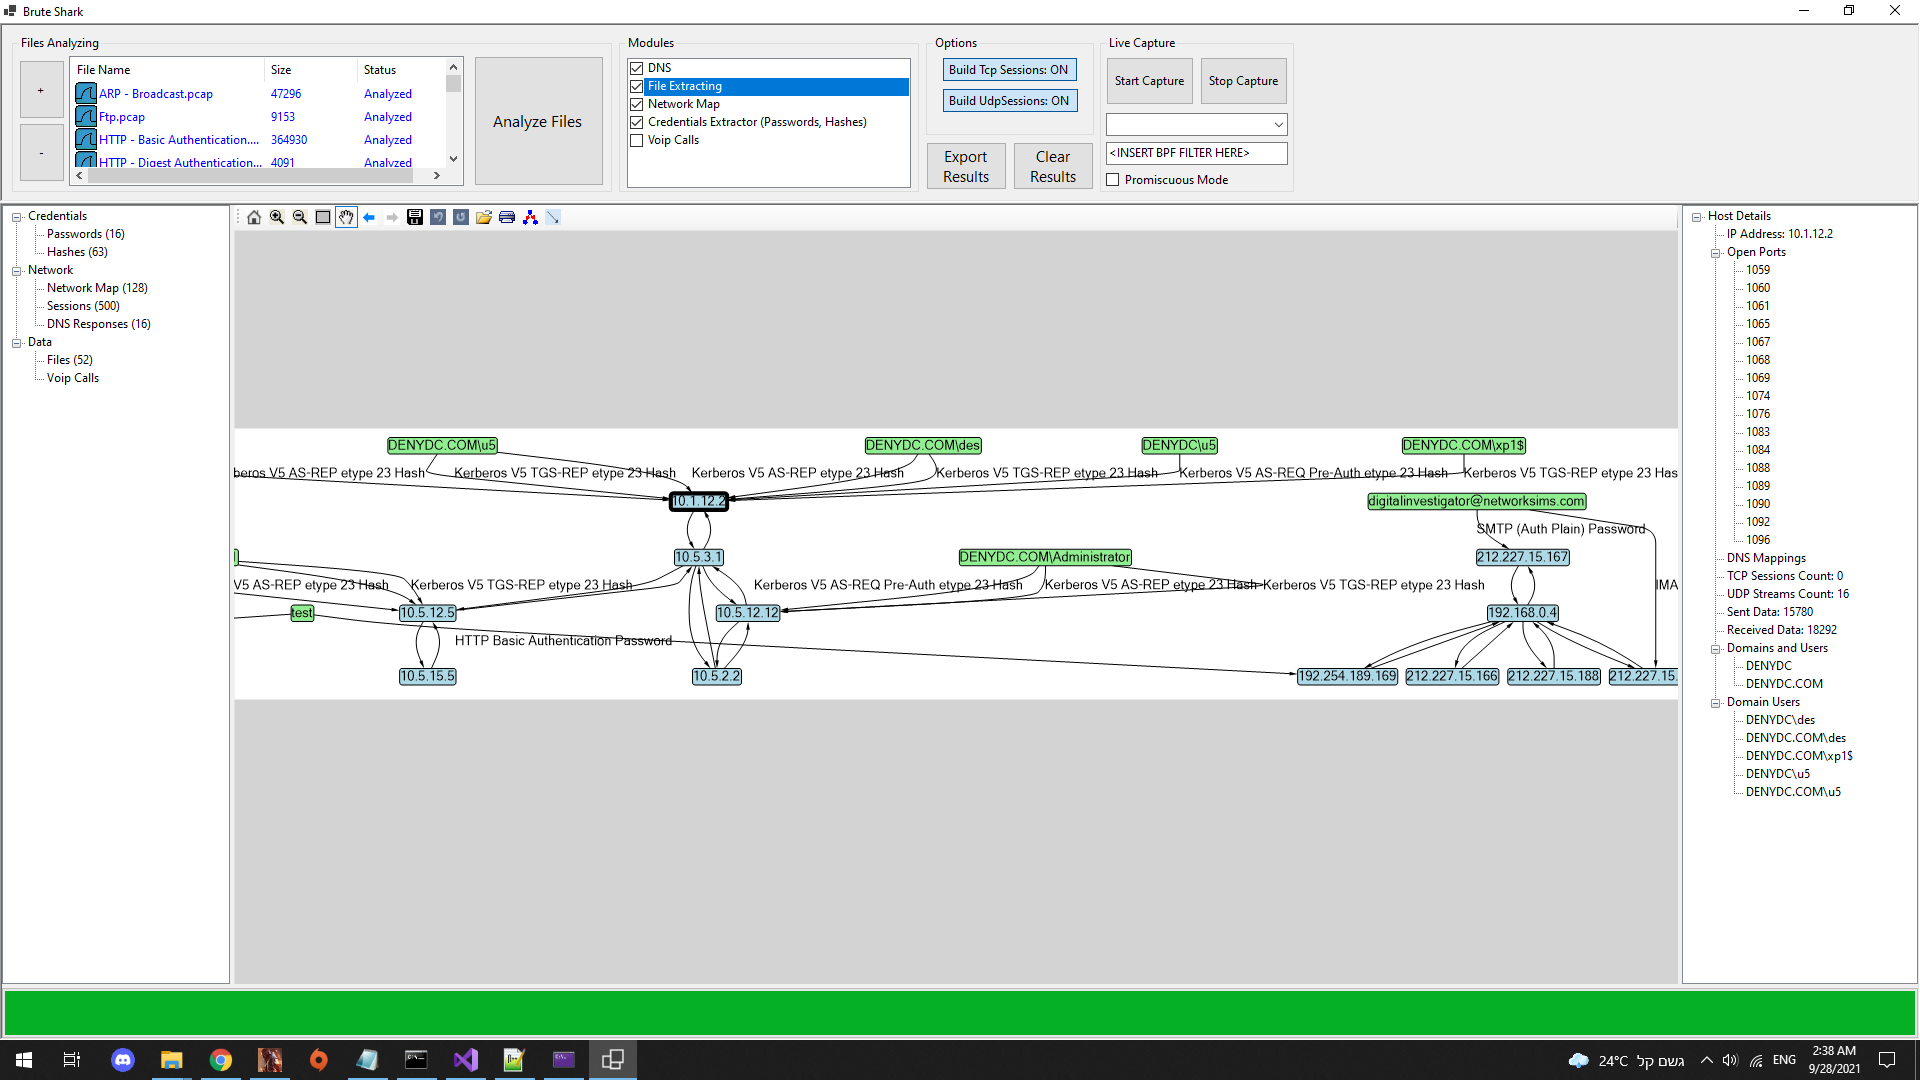
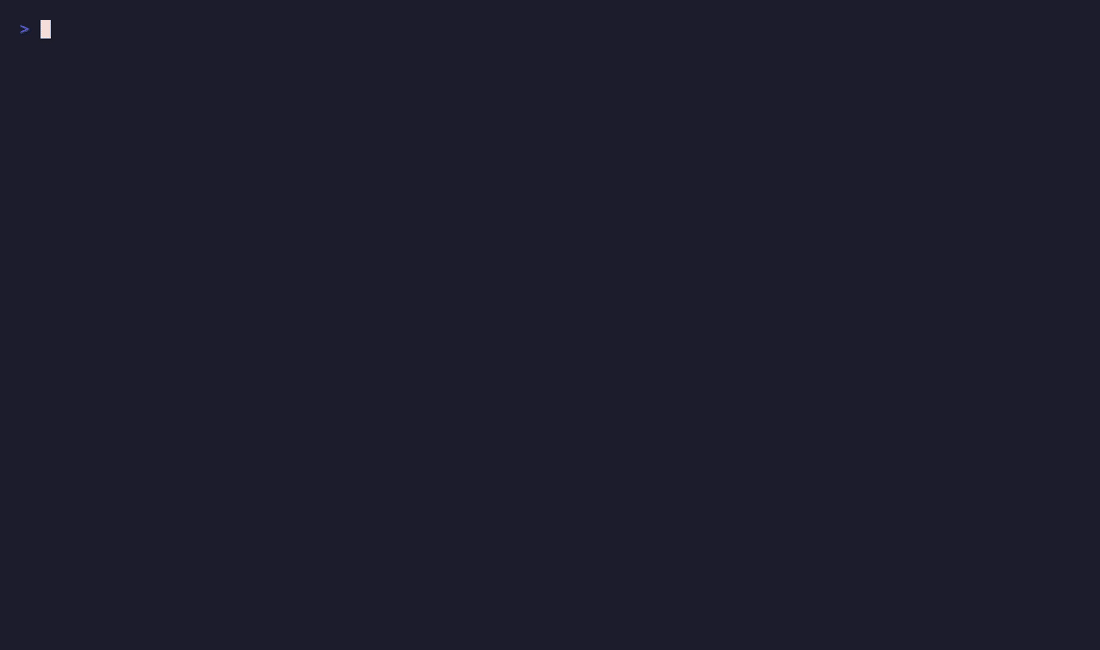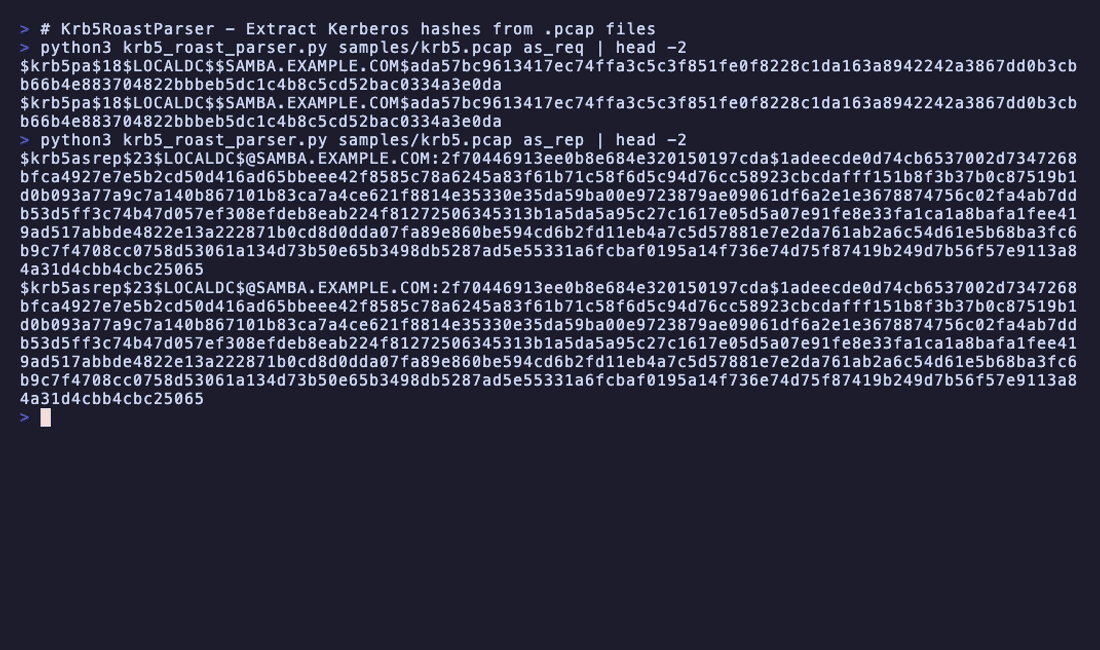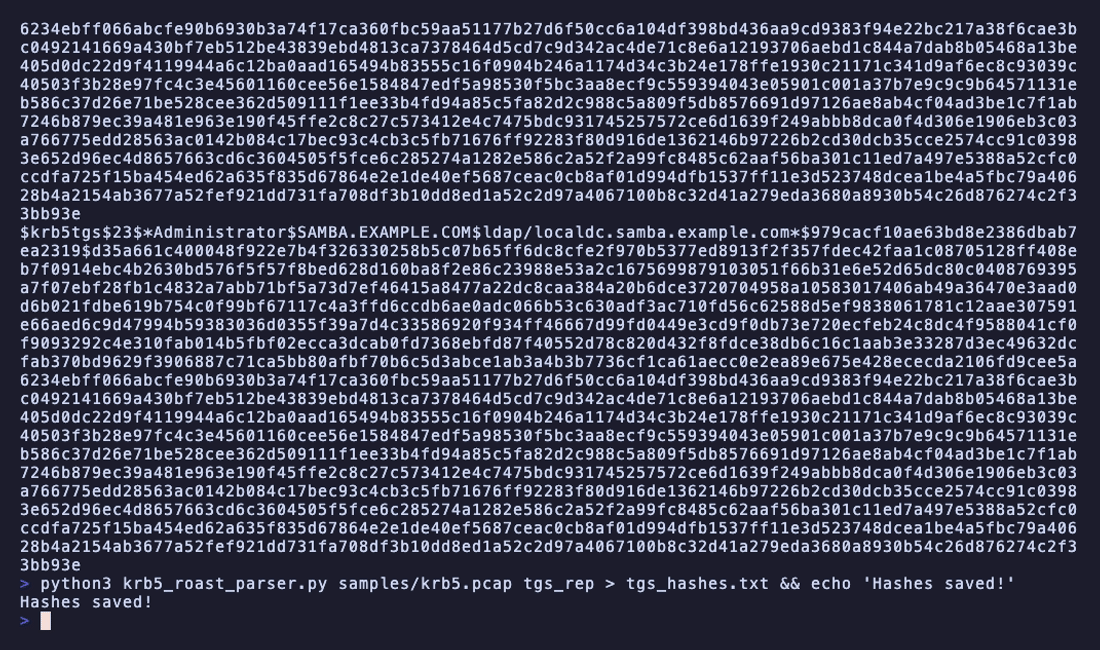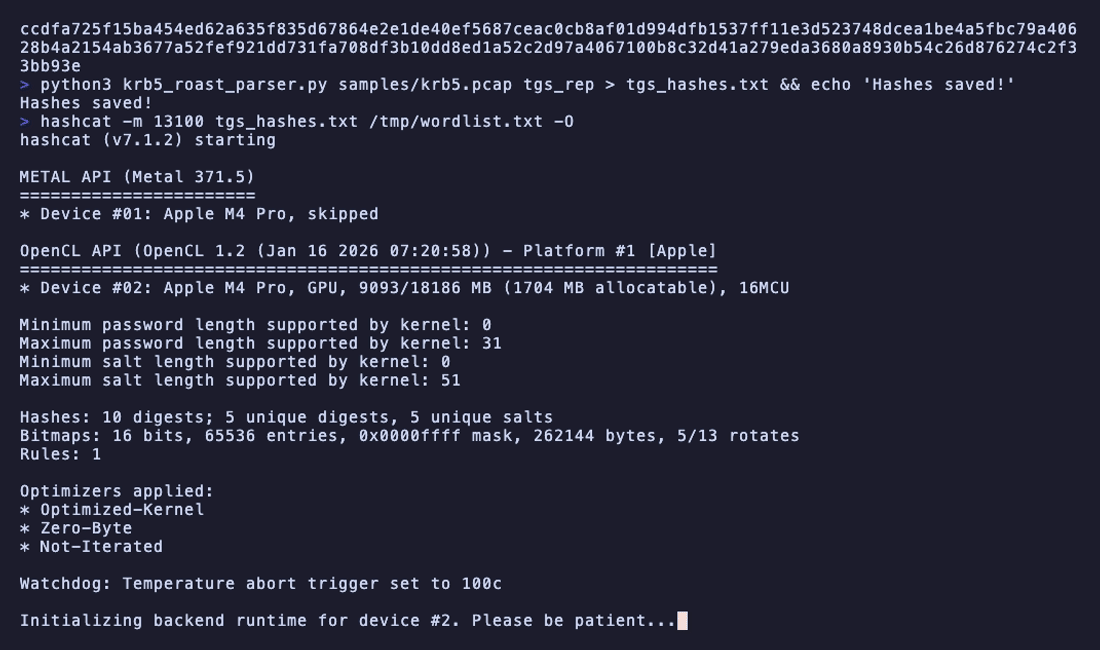 jalvarezz13/krb5roastparser
KrbRoastParser is a tool for parsing Kerberos packets from pcap files to extract AS-REQ, AS-REP and TGS-REP hashes
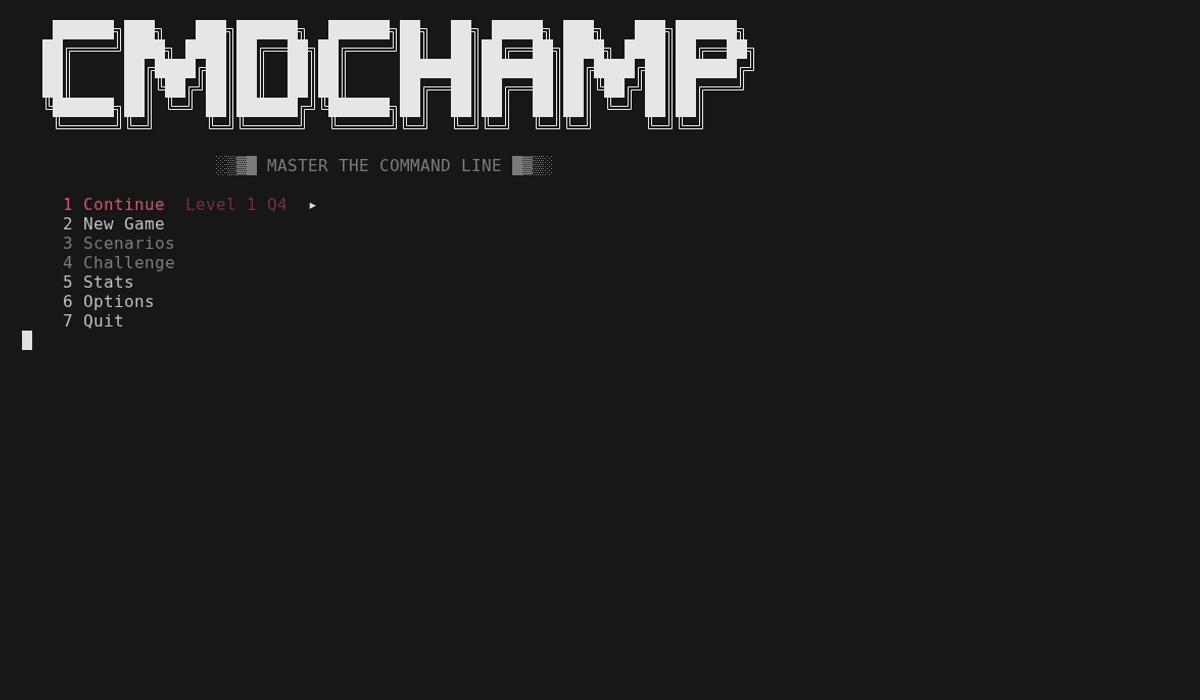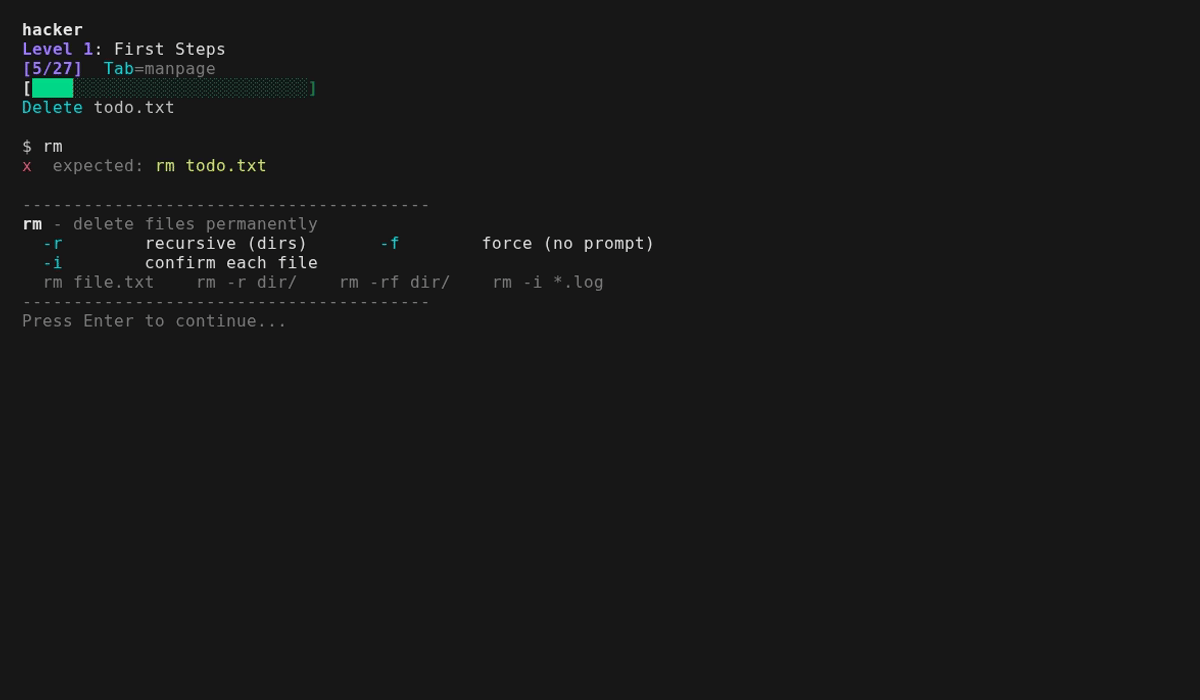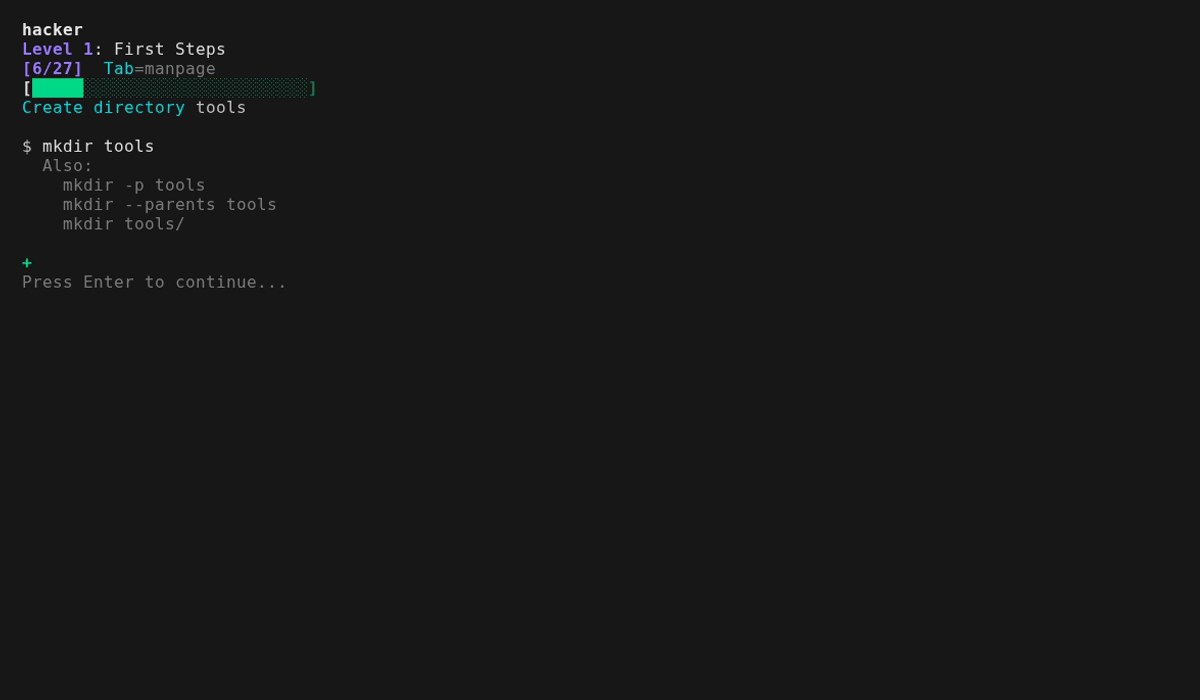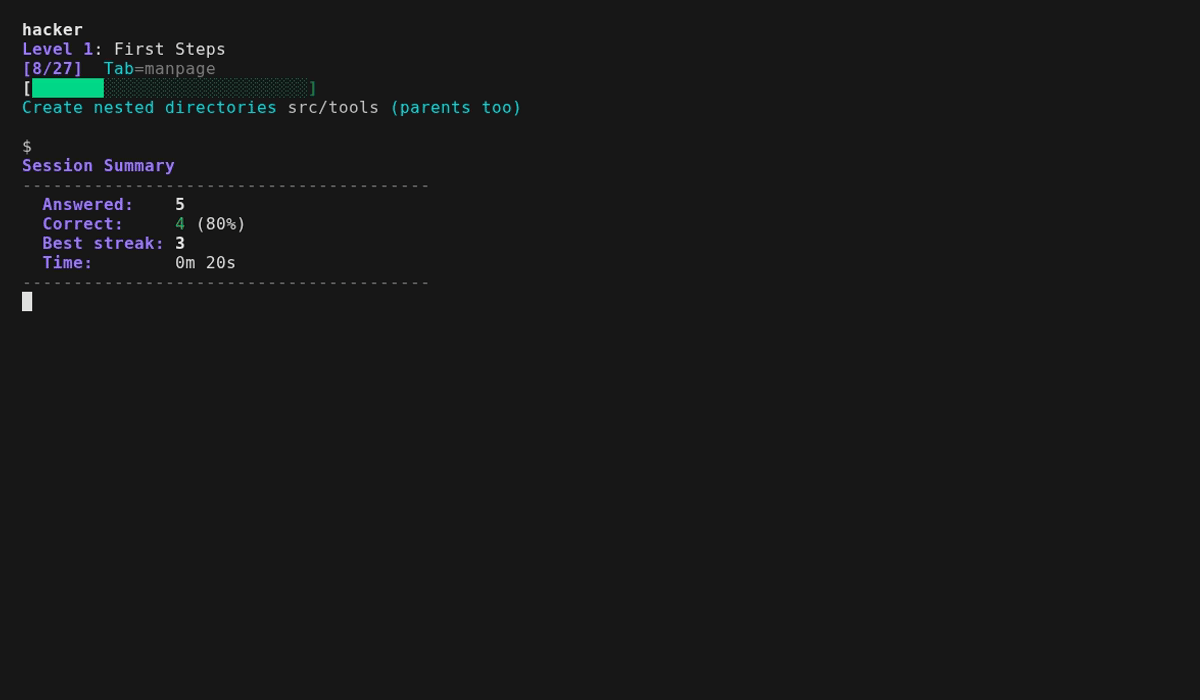 mellen9999/cmdchamp
bash CLI trainer — 30 levels from ls to privilege escalation
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
 hashcat/hashcat
World's fastest and most advanced password recovery utility
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 trustedsec/hate_crack
A tool for automating cracking methodologies through Hashcat from the TrustedSec team.