
IDAChef
 exporx/idachef
CyberChef-style recipe toolkit for IDA Pro: chain 289 encoding, cipher, compression, and hashing operations on database bytes, then patch results…
binary-analysiscode-analysiscryptography+6
18
exporx/idachefCyberChef-style recipe toolkit for IDA Pro: chain 289 encoding, cipher, compression, and hashing operations on database bytes, then patch results…
 hashcat/hashcat-utils
Small utilities that are useful in advanced password cracking
 chakshugupta13/lab
Code artifacts from research paper implementations
 jawadasghar471600-dot/wi-fi-fortress-auditor
Wi-Fi Security Audit & WPA2 Password Testing Guide 2026: Master Monitor Mode
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 aide/aide
File integrity monitoring tool that detects unauthorized changes to monitored files and directories using attribute checks, multiple hash algorithms,…
 didierstevens/didierstevenssuite
Collection of Python scripts for malware analysis, file format parsing, hashing, and forensic triage, including PDF, OLE, and XOR analysis utilities.
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 buybitart/cyclepatrol
Bash tool for on-foot Wi-Fi security checks in a loop, with evidence reports. (re-invented wifi WarDriving)
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
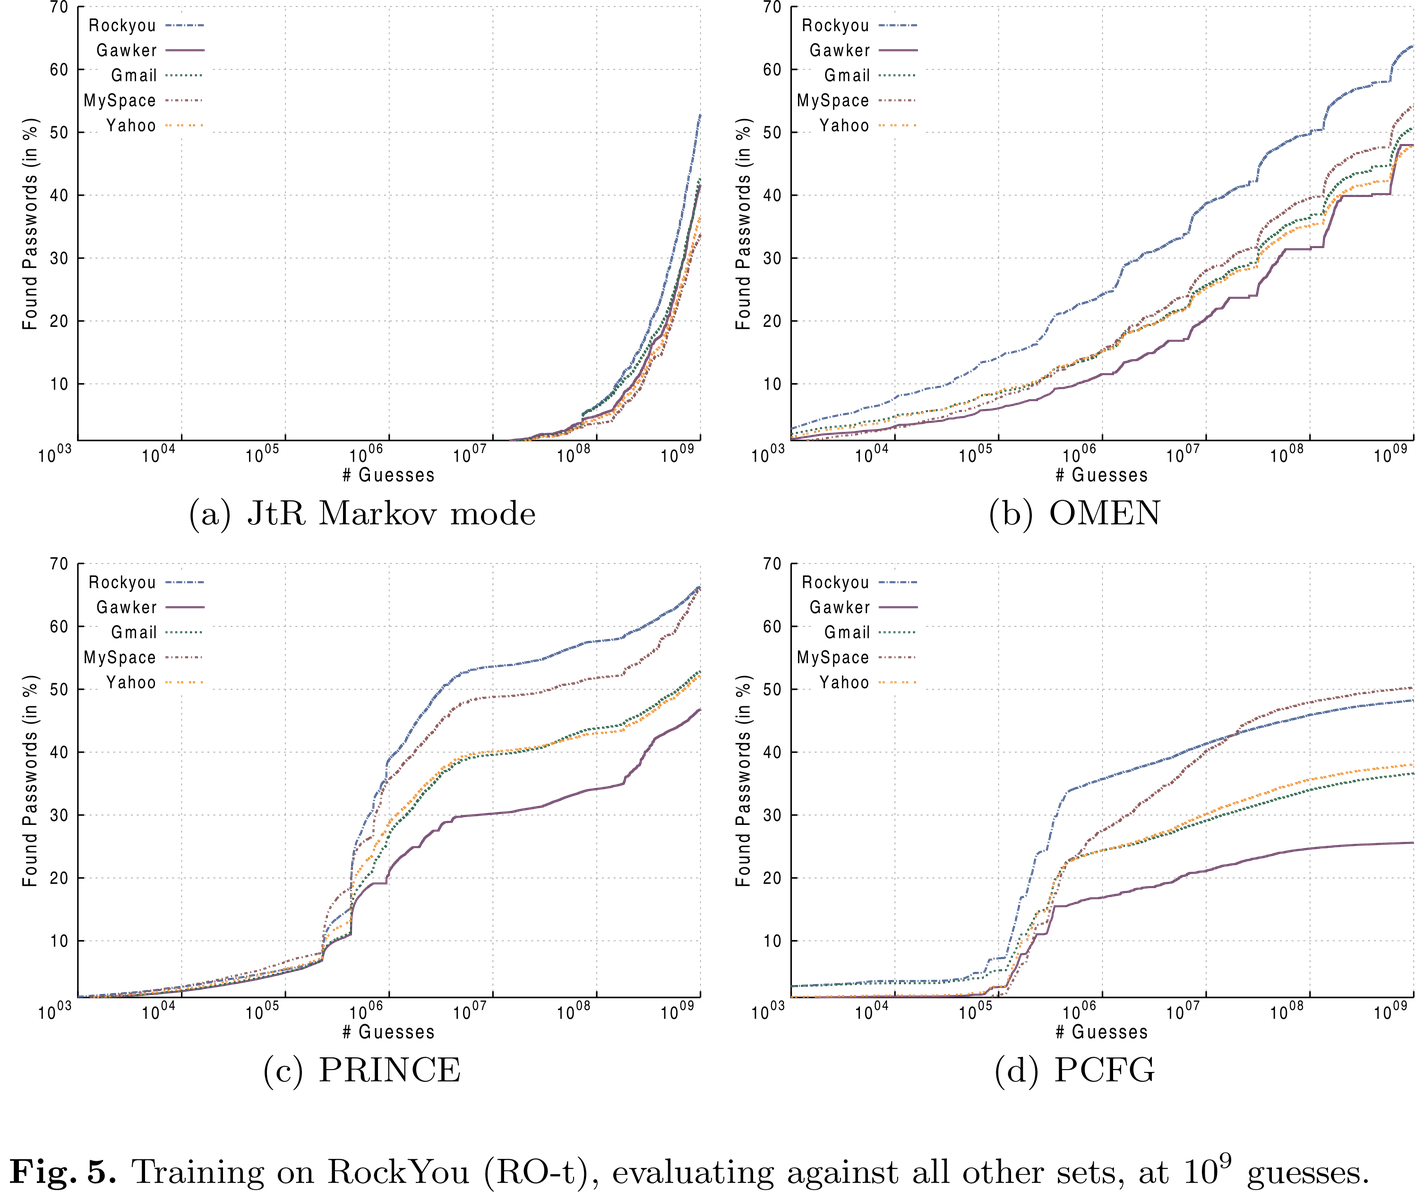 rub-syssec/omen
Markov model-based password guesser in C that enumerates candidates by probability, generating most likely passwords first for hash cracking via…
 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 bandrel/hashcatrosetta
Hashcat rule analyzer and interpreter - A Rosetta Stone for decoding hashcat rule syntax
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
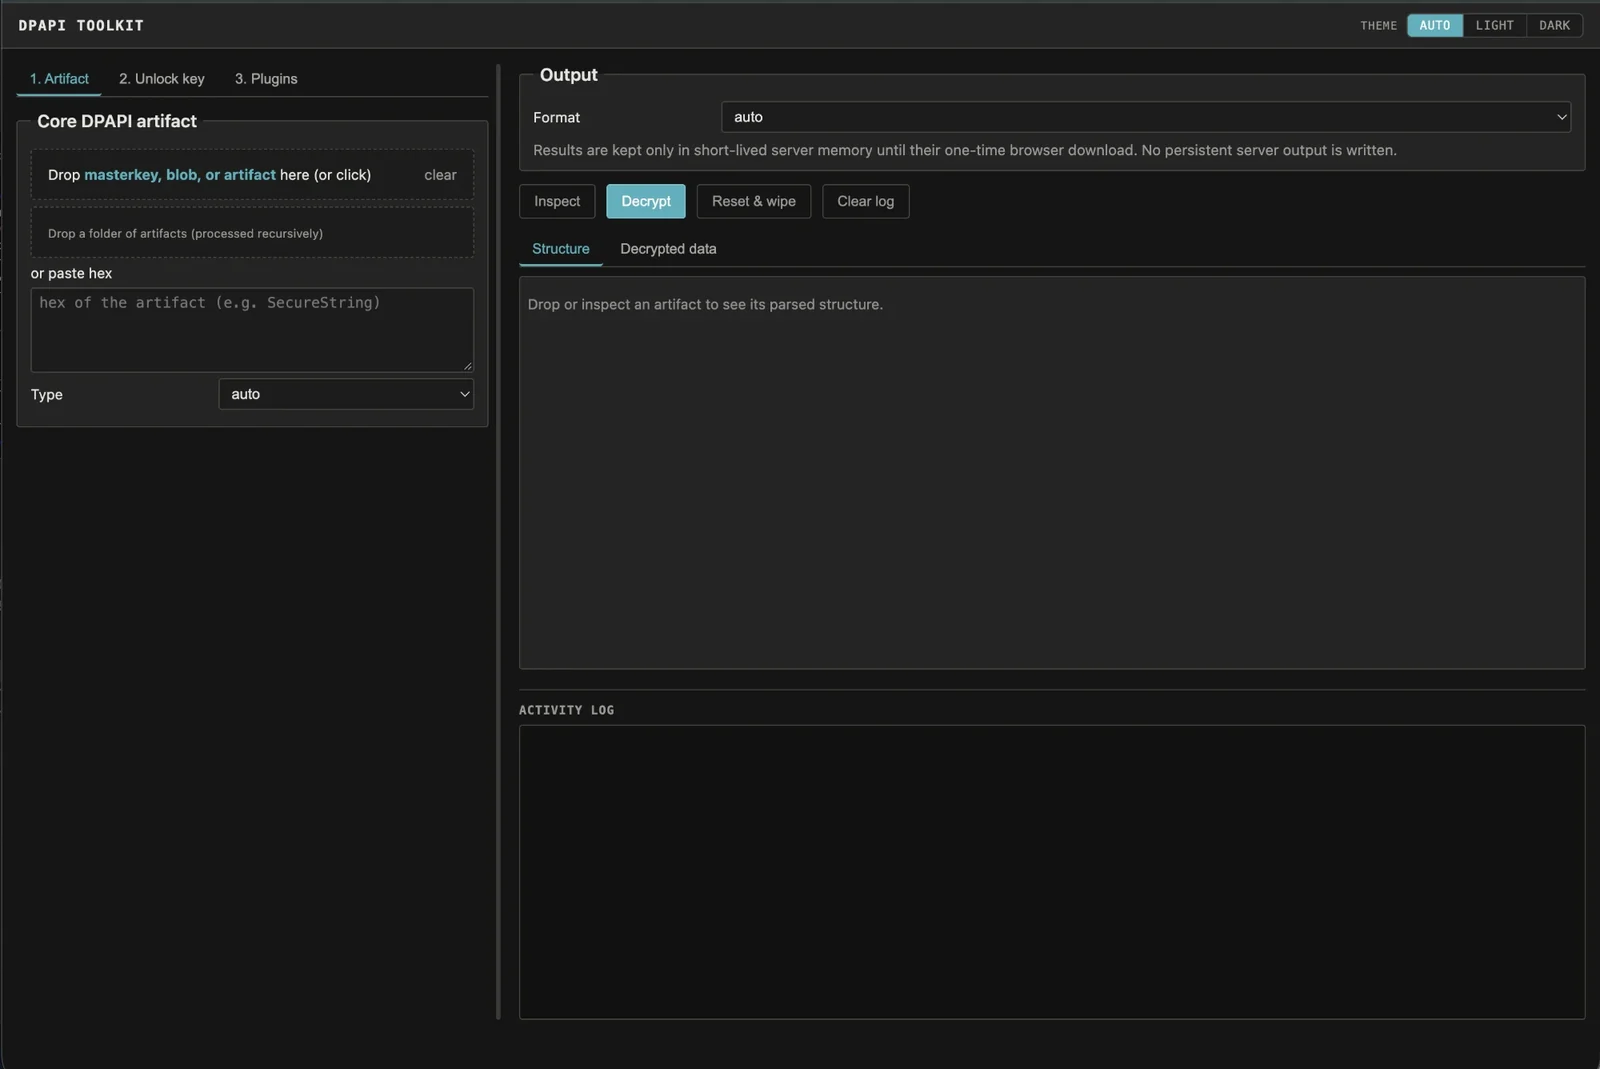 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…