DeadMatter
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
data-recoverydigital-forensicsforensics+7
qsecure-labs/deadmatterOffset Independent Credential Extraction Tool
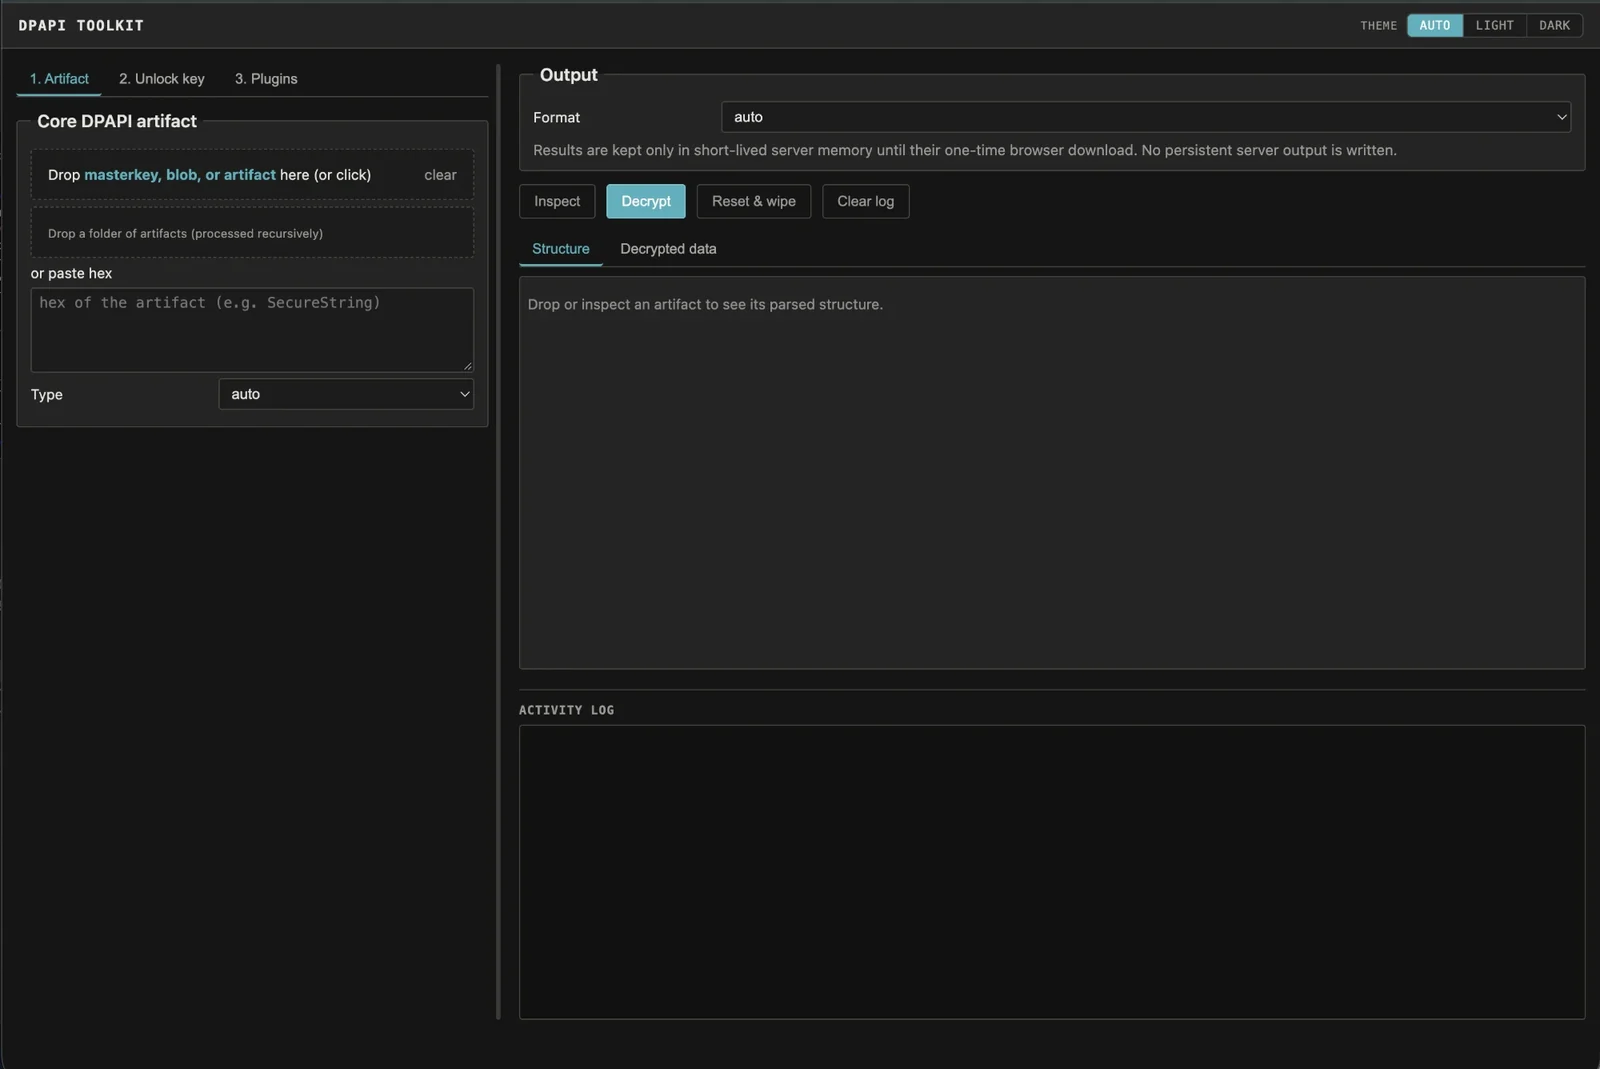 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
 legrandin/pycryptodome
A self-contained cryptographic library for Python
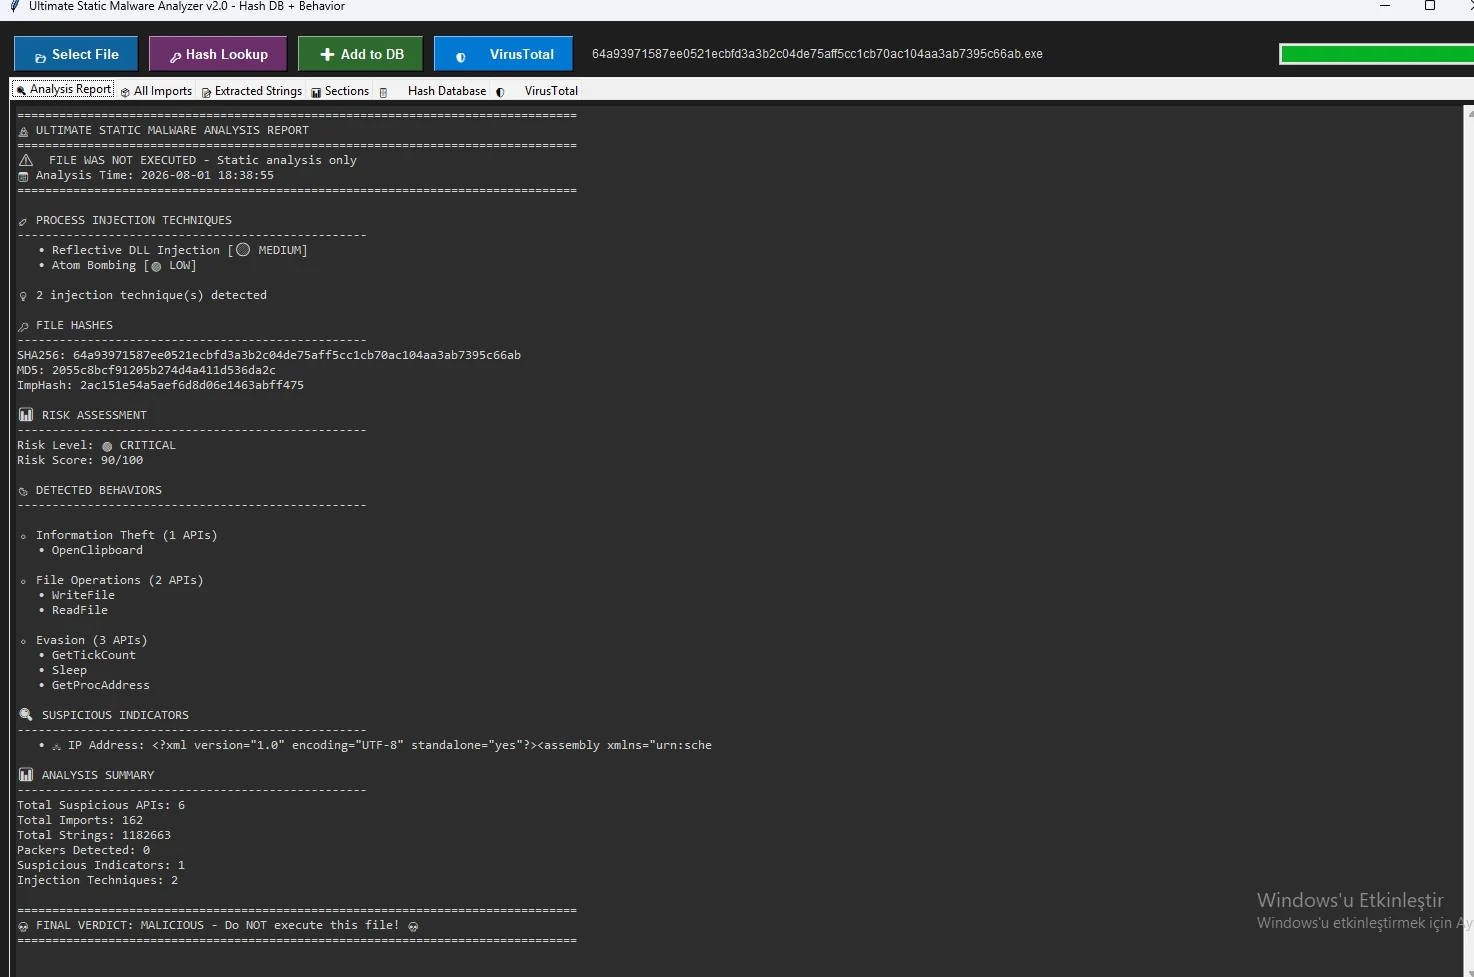 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
 microsoft/symcrypt-openssl
OpenSSL engine for use with SymCrypt cryptographic library
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
 squiblydoo/certreport
A tool to support the reporting of Authenticode Certificates by reducing the effort on individuals to report.
 evilmog/ntlmv1-multi
NTLMv1 Multitool
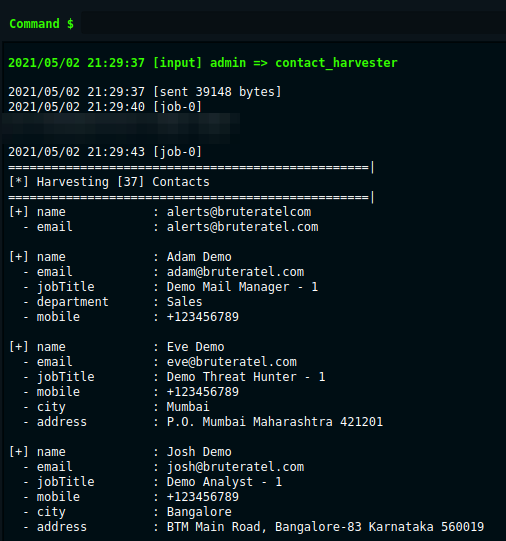 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 nccgroup/pip3line
The Swiss army knife of byte manipulation
 uthrasri/g2.5_openssl_v_1_0_1g
Full-strength cryptographic library with SSL/TLS protocol support, encryption, decryption, hashing, and X.509 certificate management for secure…
 uthrasri/openssl_g2.5_new
Industry-standard open-source toolkit implementing SSL/TLS protocols and a comprehensive cryptography library for encryption, decryption, hashing,…
 uthrasri/openssl_g2.5_v1_0_1g
Robust open-source cryptography library implementing SSL/TLS protocols, general encryption, and X.509 certificate handling for secure communications.
 satheesh575555/openssl_1.0.1g_after
Open-source toolkit implementing SSL/TLS protocols and a full-strength cryptography library with encryption, decryption, certificate management, and…
 synacktiv/radmin3-password-cracker
Radmin Server 3 credentials dumper/cracker