

DeadMatter
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
data-recoverydigital-forensicsforensics+7
qsecure-labs/deadmatterOffset Independent Credential Extraction Tool
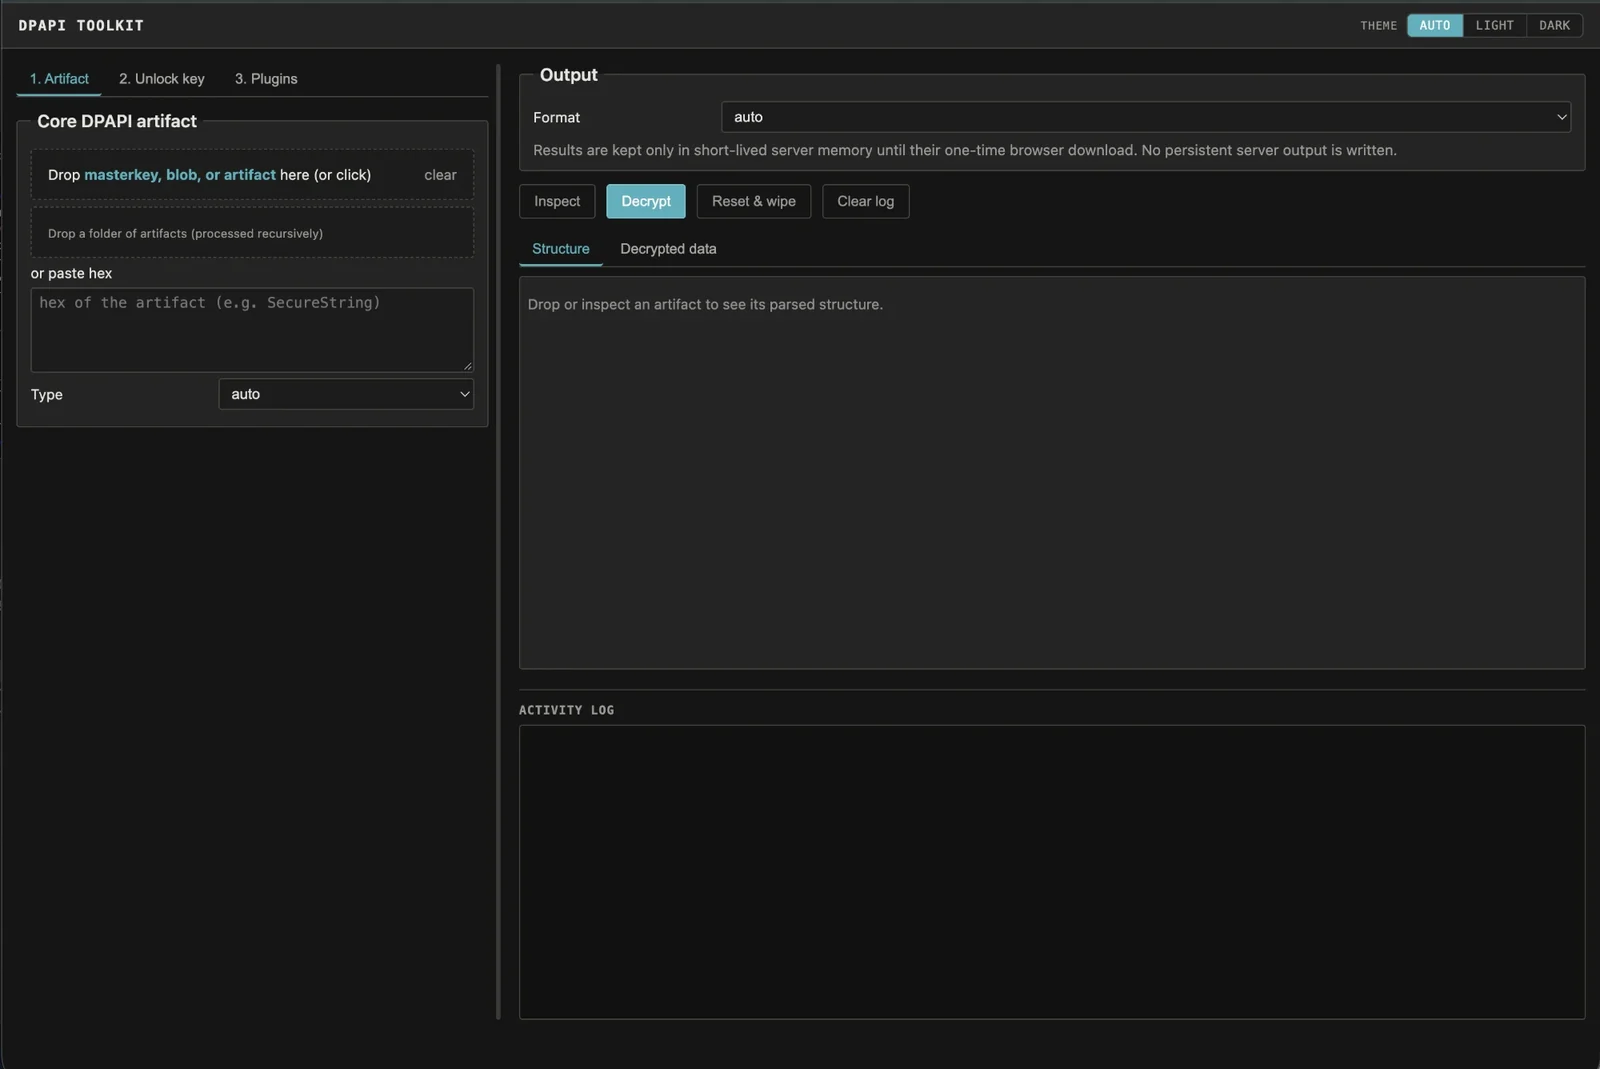 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
 legrandin/pycryptodome
A self-contained cryptographic library for Python
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 microsoft/symcrypt-openssl
OpenSSL engine for use with SymCrypt cryptographic library
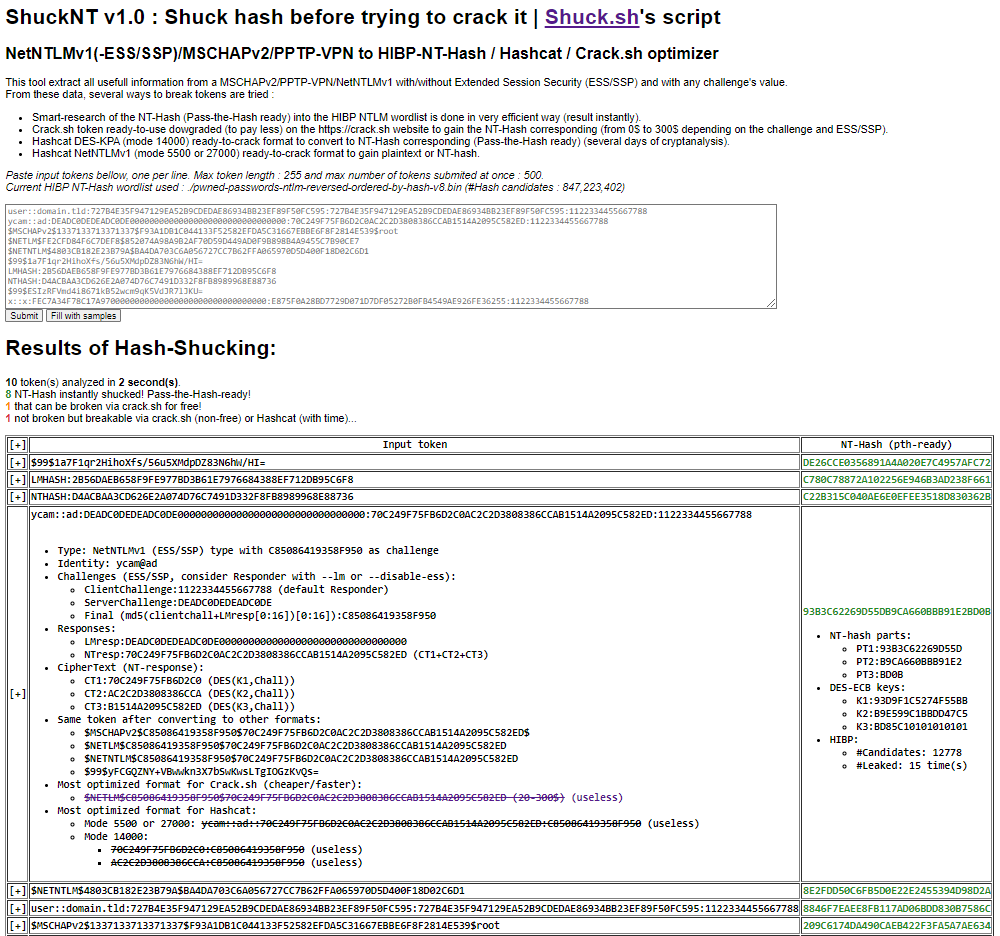 yanncam/shucknt
ShuckNT is the script of Shuck.sh online service for on-premise use. It is design to dowgrade, convert, dissect and shuck authentication token based…
 evilmog/ntlmv1-multi
NTLMv1 Multitool
 george0papasotiriou/cve-2026-22016-ipfs-cid-spoofing-via-multihash-length-extension
Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…
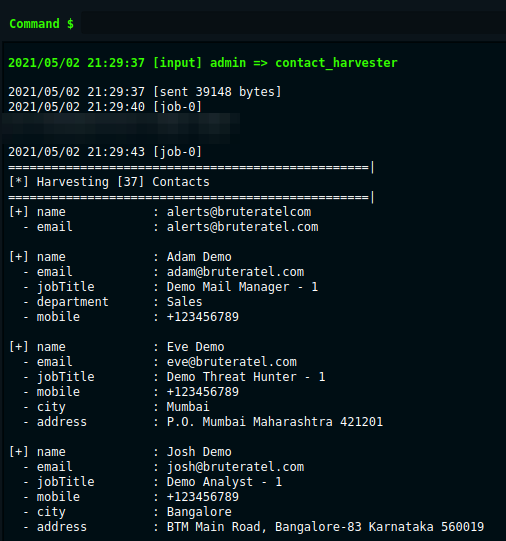 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 nccgroup/pip3line
The Swiss army knife of byte manipulation
 uthrasri/g2.5_openssl_v_1_0_1g
Full-strength cryptographic library with SSL/TLS protocol support, encryption, decryption, hashing, and X.509 certificate management for secure…
 uthrasri/openssl_g2.5_new
Industry-standard open-source toolkit implementing SSL/TLS protocols and a comprehensive cryptography library for encryption, decryption, hashing,…
 uthrasri/openssl_g2.5_v1_0_1g
Robust open-source cryptography library implementing SSL/TLS protocols, general encryption, and X.509 certificate handling for secure communications.
 golang/crypto
[mirror] Go supplementary cryptography libraries
 dcit/perl-cryptx
Perl cryptographic toolkit providing symmetric ciphers, AEAD modes, hash functions, MACs, public-key cryptography, key derivation, and secure random…
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing