

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
79 results
GateX preview

GateX

GitHubabraxas/gatex

FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…

binary-analysisbinary-exploitationcryptography+8
11 month ago
Random-Scripts preview

Random-Scripts

GitHubstar-sg/random-scripts

Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…


digital-forensicsforensicshash-analysis+5
23 years ago
higernes preview

higernes

GitLabjankoboy88/higernes

a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.

dns-subdomain-enumerationemail-harvestinghash-analysis+8
4 days ago
higernes preview

higernes

GitLabvqkro/higernes

a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.

dns-subdomain-enumerationemail-harvestinggeneral-purpose-utilities+9
4 days ago
DeadMatter preview

DeadMatter

GitHubqsecure-labs/deadmatter

Offset Independent Credential Extraction Tool
data-recoverydigital-forensicsforensics+7
691 year ago
dpapi-toolkit preview

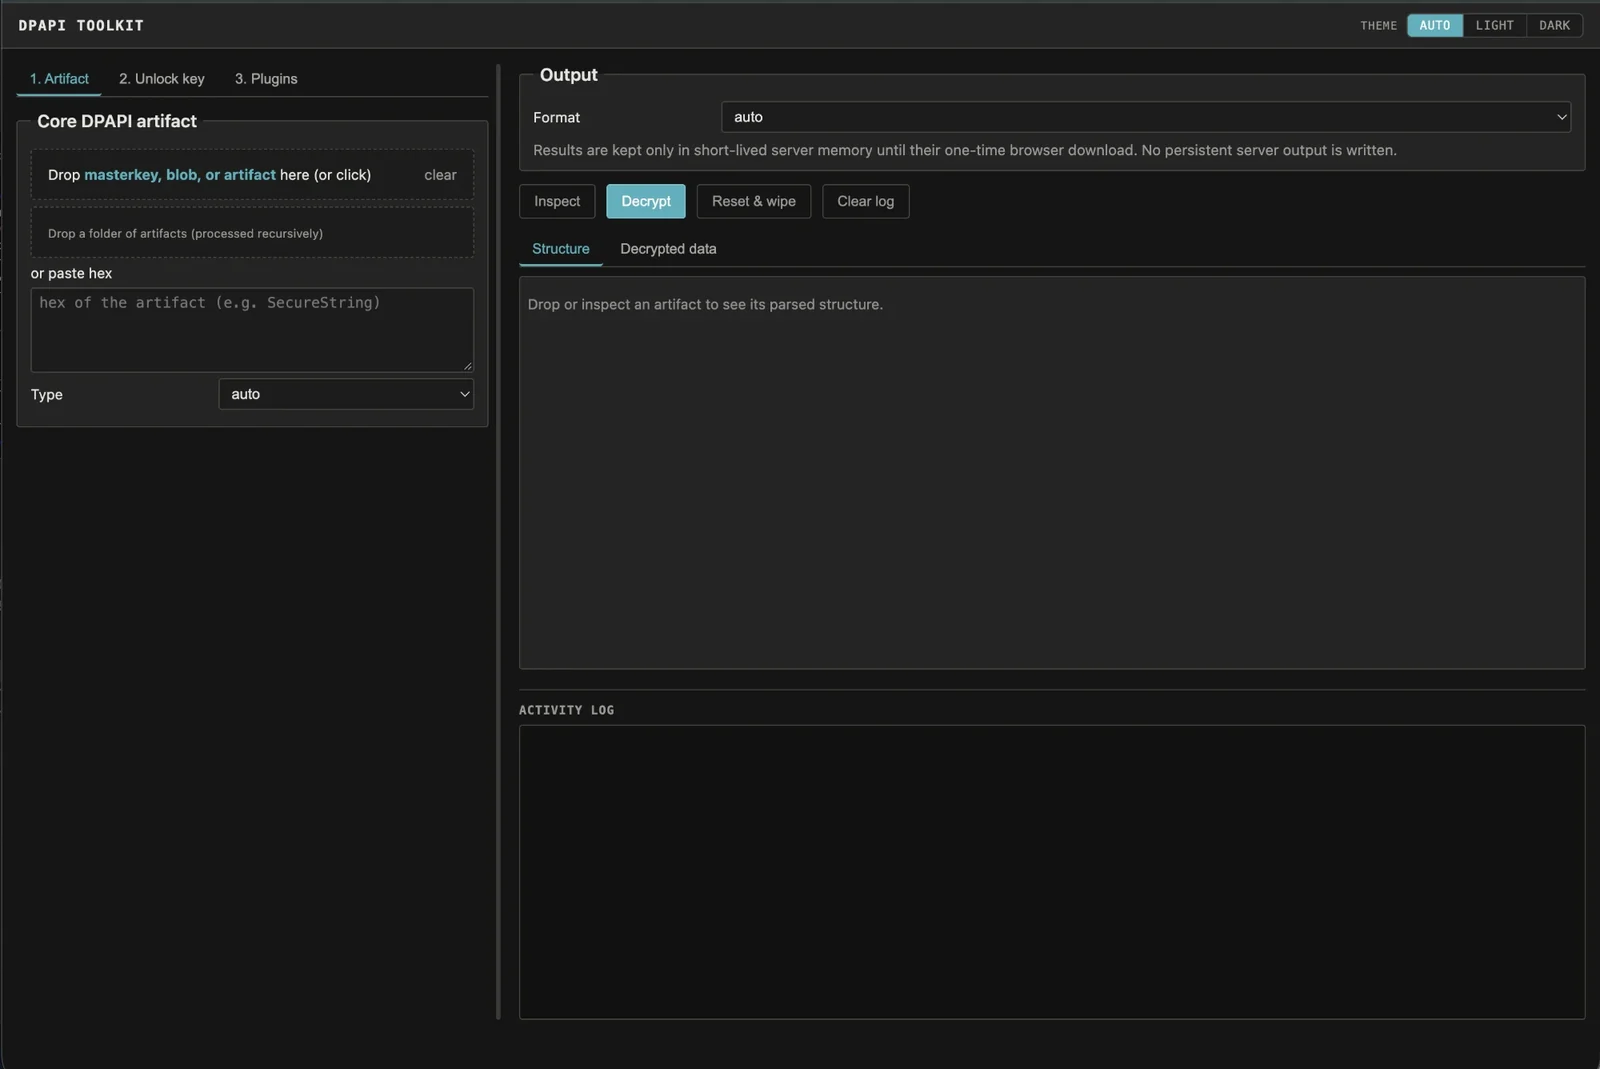
dpapi-toolkit

GitHubcrypt0p3g/dpapi-toolkit

Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
digital-forensicsencryption-decryption-toolsforensics+7
2814 days ago
Hundred OSINT preview

Hundred OSINT

GitLabt-beckett/h-osint

Local-first, keyboard-driven OSINT workbench for the terminal with 28 modules covering username, domain, IP, email, breach, and geolocation lookups…
dns-analysiseducationemail-harvesting+7
26 days ago
MalwareForge---Advanced-Static-Malware-Analyzer preview

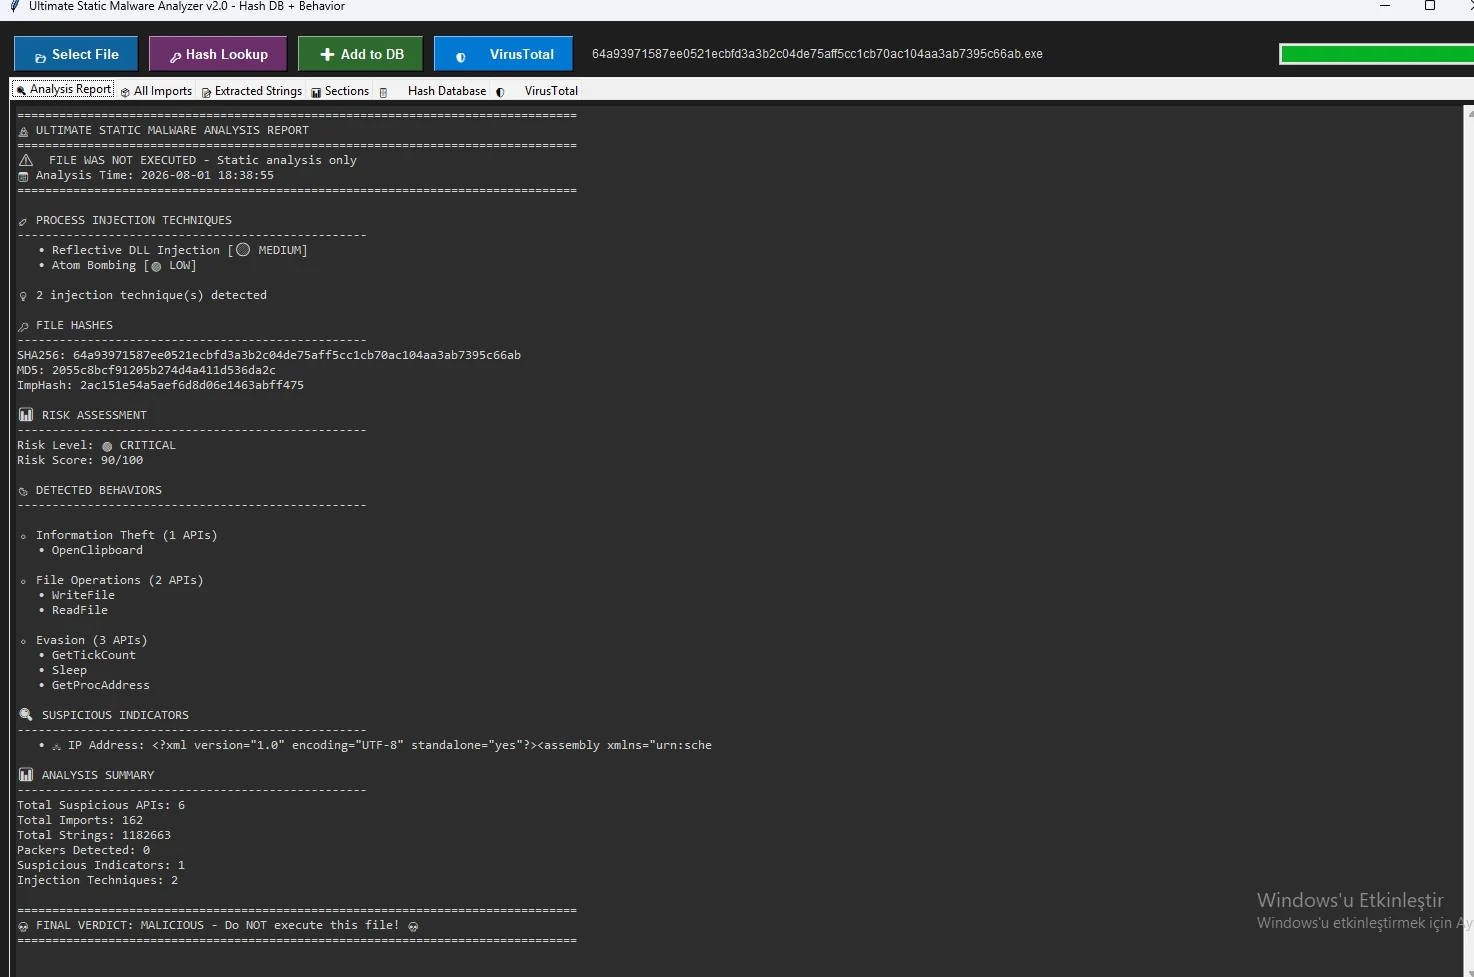
MalwareForge---Advanced-Static-Malware-Analyzer

GitHubkaandemir993/malwareforge---advanced-static-malware-analyzer

Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

binary-analysishash-analysismalware-analysis+2
41 month ago
custom-oscp-tooling preview

custom-oscp-tooling

GitLabwattocyber/custom-oscp-tooling

OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
database-securitydns-analysishash-analysis+9
1 month ago
MSSQL-Pentest-Cheatsheet preview

MSSQL-Pentest-Cheatsheet

GitHubignitetechnologies/mssql-pentest-cheatsheet

Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…

curated-resourcesdatabase-securityexploitation+8
2706 months ago
SharpNTLMRawUnHide preview

SharpNTLMRawUnHide

GitHubx-c3ll/sharpntlmrawunhide

C# version of NTLMRawUnHide

hash-analysisnetwork-securitypacket-sniffing-analysis+2
724 years ago
Windows-SignedBinary preview

Windows-SignedBinary

GitHubmr-un1k0d3r/windows-signedbinary

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
adversarial-attackbinary-analysishash-analysis+4
2617 years ago
python-inquestlabs preview

python-inquestlabs

GitHubinquest/python-inquestlabs

A Pythonic interface and command line tool for interacting with the InQuest Labs API.
email-securityhash-analysisinformation-gathering+4
3710 months ago
hashmuncher preview

hashmuncher

GitHublkarlslund/hashmuncher

Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
hash-analysisinformation-gatheringpacket-sniffing-analysis+3
1273 years ago
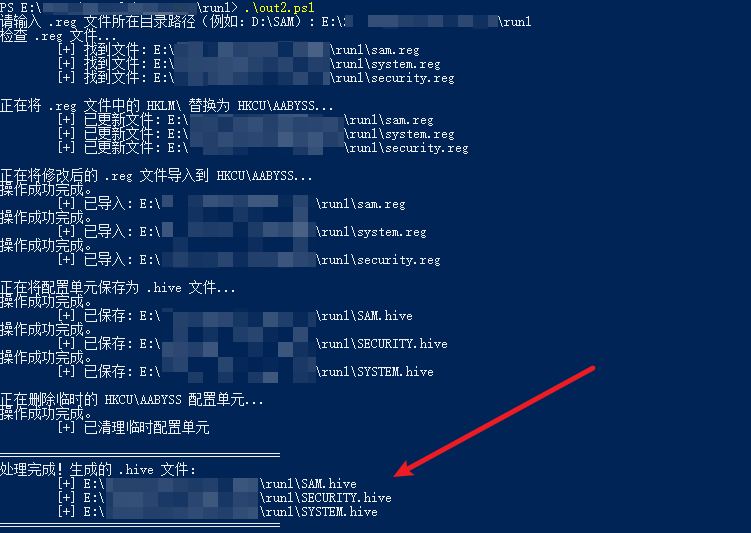
HashDump-BypassEDR preview

HashDump-BypassEDR

GitHubaabysszg/hashdump-bypassedr

Windows绕过EDR实现DumpHash
hash-analysisids-ips-evasionpassword-attacks+3
2642 months ago
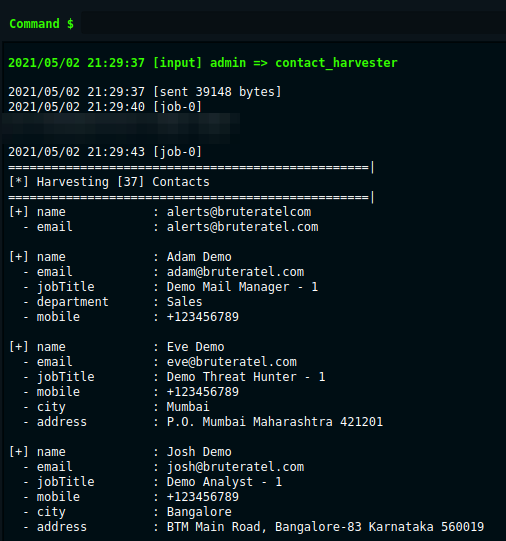
BRC4-BOF-Artillery preview

BRC4-BOF-Artillery

GitHubparanoidninja/brc4-bof-artillery

Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
command-and-controlencryption-decryption-toolshash-analysis+5
15111 months ago
ForensiX preview

ForensiX

GitHubtheevidencehunter/forensix

Digital Forensics Intelligence Framework

digital-forensicsdisk-forensicsforensics+4
5 months ago
G2.5_Openssl_V_1_0_1g preview

G2.5_Openssl_V_1_0_1g

GitHubuthrasri/g2.5_openssl_v_1_0_1g

Full-strength cryptographic library with SSL/TLS protocol support, encryption, decryption, hashing, and X.509 certificate management for secure…

authenticationcryptographyencryption-decryption-tools+2
2 years ago
Previous12345Next