
DPAPISnoop
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
hash-analysispassword-attackspassword-cracking+2
146
leftp/dpapisnoopA C# tool to output crackable DPAPI hashes from user MasterKeys
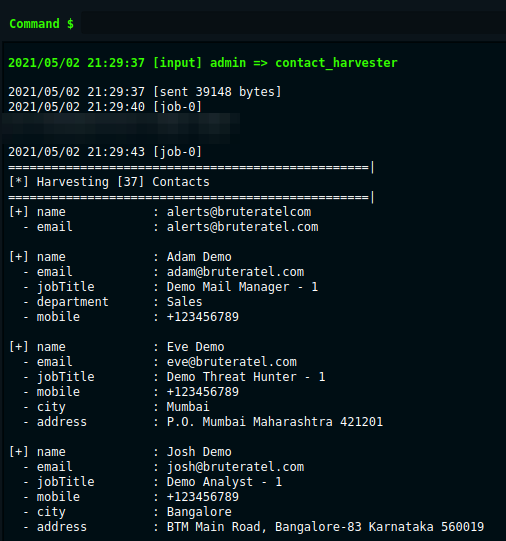 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
 nccgroup/pip3line
The Swiss army knife of byte manipulation
 s3l33/cve-2022-25012
Updated version of this weak password encryption script
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
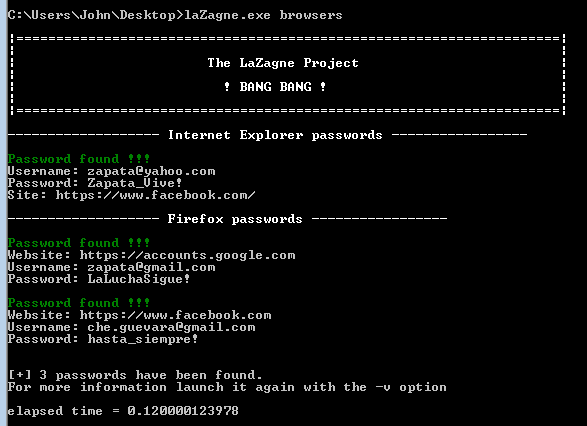 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 gentilkiwi/mimikatz
A little tool to play with Windows security
 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
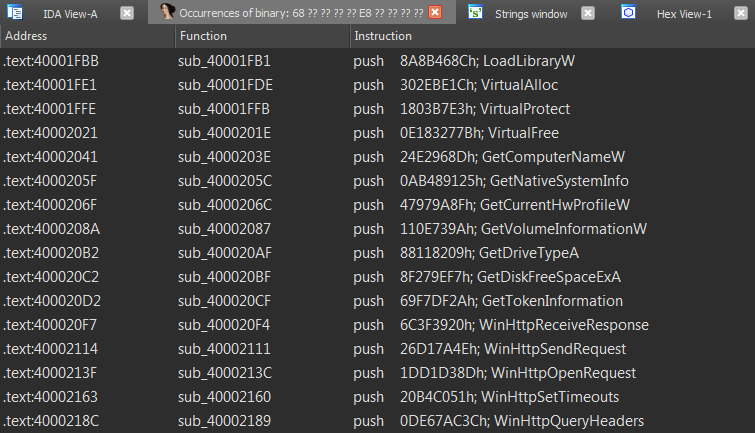 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
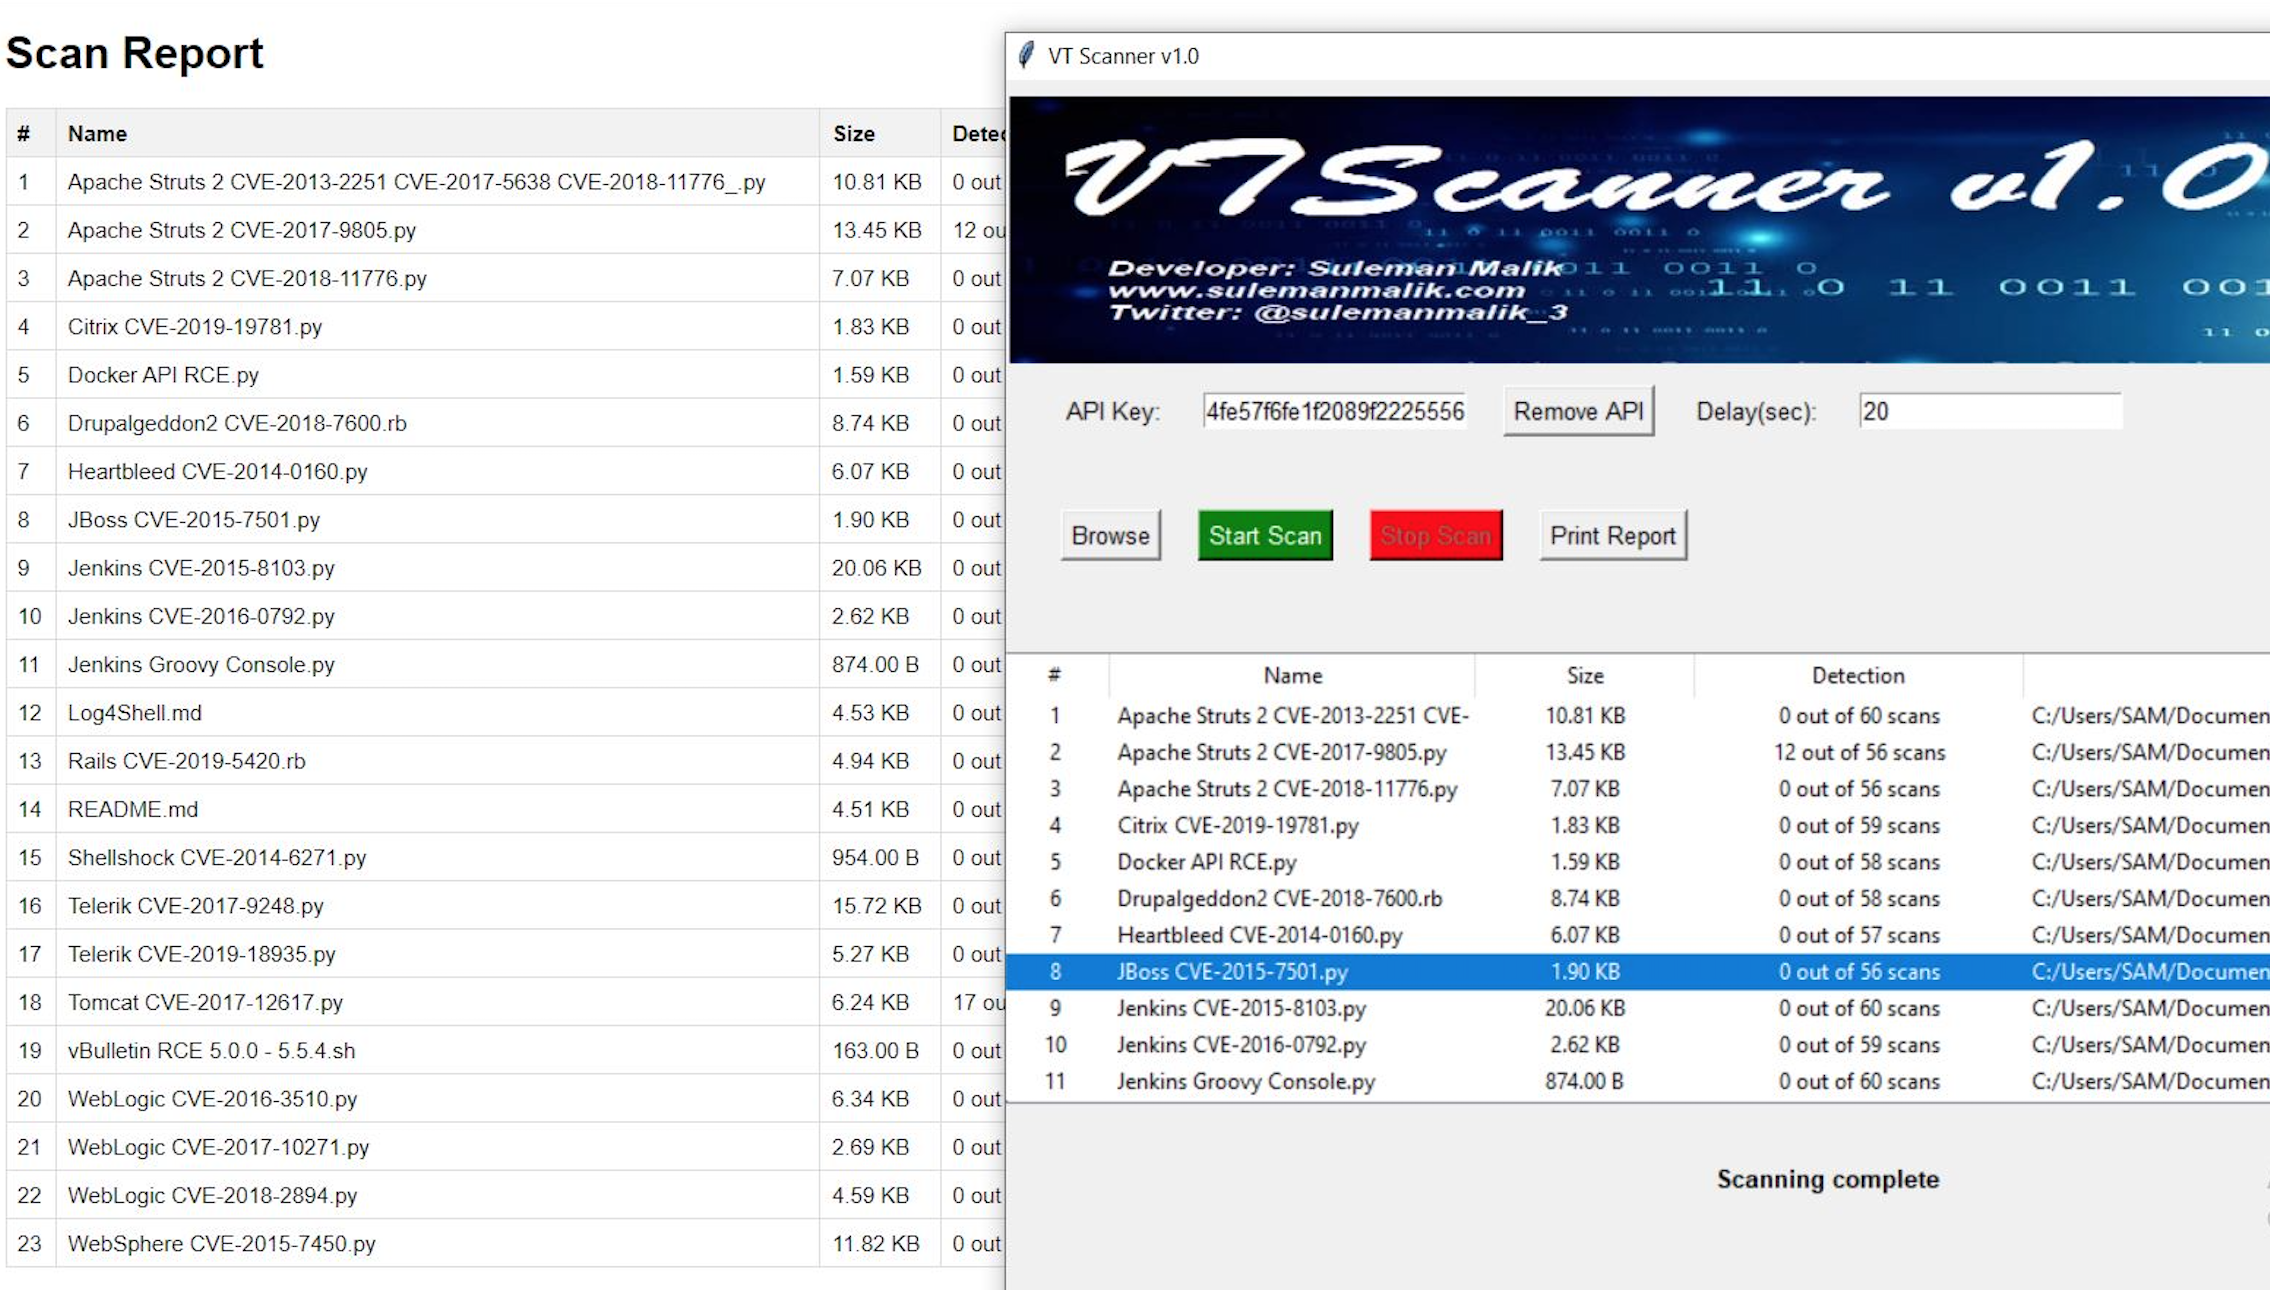 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.