
CVE-2023-38829-NETIS-WF2409E_Report
 victorique-123/cve-2023-38829-netis-wf2409e_report
对NETIS WF2409E路由器进行的一次完整硬件安全分析研究。通过对设备进行拆解分析、调试接口识别、固件提取等工作,记录了硬件分析的全过程、漏洞细节以及相应的安全建议,希望能帮助提高物联网设备的安全性。
educationembedded-systems-securityfirmware-analysis+6
victorique-123/cve-2023-38829-netis-wf2409e_report对NETIS WF2409E路由器进行的一次完整硬件安全分析研究。通过对设备进行拆解分析、调试接口识别、固件提取等工作,记录了硬件分析的全过程、漏洞细节以及相应的安全建议,希望能帮助提高物联网设备的安全性。
 cwjchoi01/cve-2025-66678
Proof-of-concept exploit for CVE-2025-66678 demonstrating arbitrary MSR and physical memory read/write via a vulnerable hardware utility driver to…
 pedrolucasoliva/spectre-attack-demo
Example of using revealed "Spectre" exploit (CVE-2017-5753 and CVE-2017-5715)
 hunt-benito/samsung-exynos-sms-stack-overflow-cve-2025-54328-critical-zero-click-baseband-rce
Conceptual PoC for CVE-2025-54328, a critical zero-click stack buffer overflow in Samsung Exynos baseband firmware's SMS RP-DATA parser, enabling…
 nadafarafat/bd-alaris-firmware-analysis
Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…
 horkimhab/cve-2022-25477
CVE Realtek SD card reader. CVE-2022-25477, CVE-2022-25478, CVE-2022-25479, CVE-2022-25480, CVE-2024-40432, CVE-2024-40431
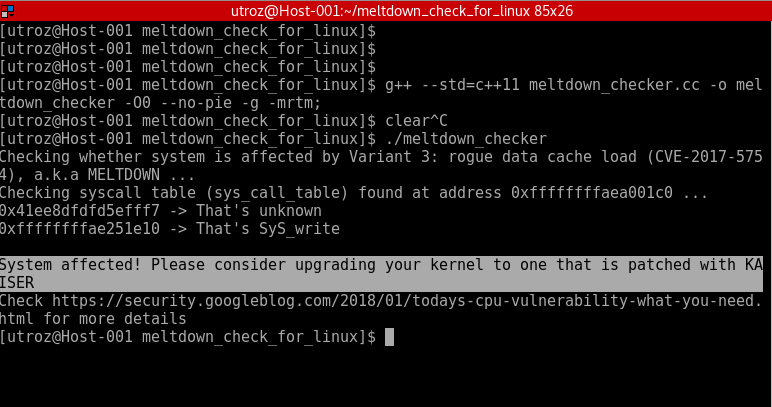 speecyy/am-i-affected-by-meltdown
Proof-of-concept / Exploit / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a
 iamshivambhatt/hardware-vulnerability-with-proof-of-concept-
Research and hands-on PoC of Spectre Variant 2 (CVE-2017-5715), a hardware side-channel vulnerability exploiting CPU speculative execution and branch…
 crimsonfiedofficial/cve-2026-29114
Dahua CVE-2026-29114
 star-laboratory/prism
PrISM: A Scalable Probabilistic RowHammer Mitigation (ISCA 2026). Ramulator2 source code and evaluation scripts.
 cryptoadvocate/dcsgonebadge
The hardware engineering home of the Circuit Crafters first electronic badge project.
 supermagnum/gr-qradiolink
GNU Radio out-of-tree (OOT) module for QRadioLink blocks.
 demining/ramnesia-attack
Scientific investigation of hardware vulnerabilities (CVE-2025-6202, CVE-2023-39910) enabling ECDSA key recovery from Bitcoin infrastructure via…
 albertleecn/cve-2017-5753
OSX 10.13.2, CVE-2017-5753, Spectre, PoC, C, ASM for OSX, MAC, Intel Arch, Proof of Concept, Hopper.App Output
 cryptoadvocate/cryptohackfirm
The firmware engineering home of the Cryptohack electronic badge project.
 simoesctt/lctt-apple-silicon--resonance-vulnerability-cve-2024-23296
Research on a temporal coherence vulnerability in Apple Silicon M-series chips, exploiting golden ratio harmonic clock frequencies to potentially…
 14mb1v45h/cve-2025-38676
Stack buffer overflow during cmdline parsing
 bytereaper77/avx-side-channel
AVX-Based Timing Side Channel — ASLR Detection