

wmi-static-spoofer
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
exploitationhardware-hackinghardware-iot-security+4
508
alex3434/wmi-static-spooferSpoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
 laginimaineb/extractkeymaster
Exploit that extracts Qualcomm's KeyMaster keys using CVE-2015-6639 and CVE-2016-2431
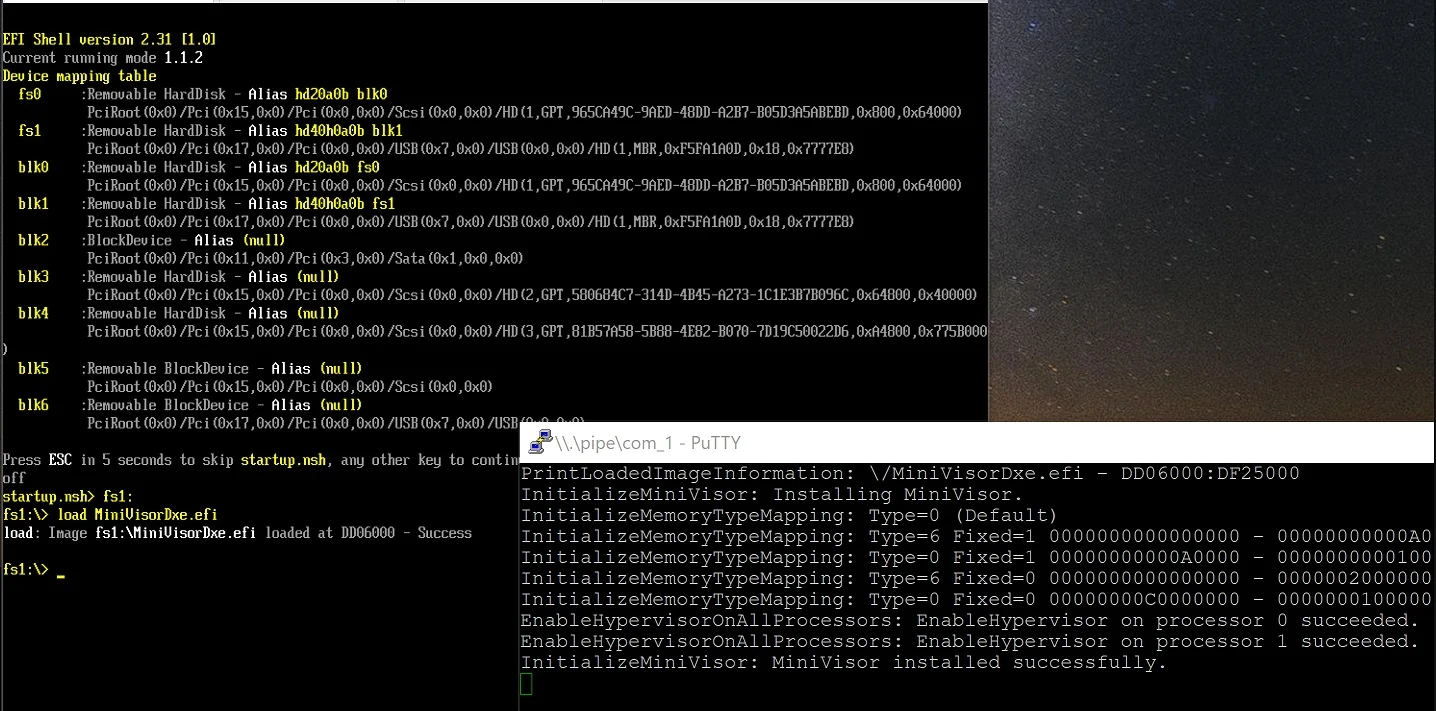 tandasat/minivisorpkg
The research UEFI hypervisor that supports booting an operating system.
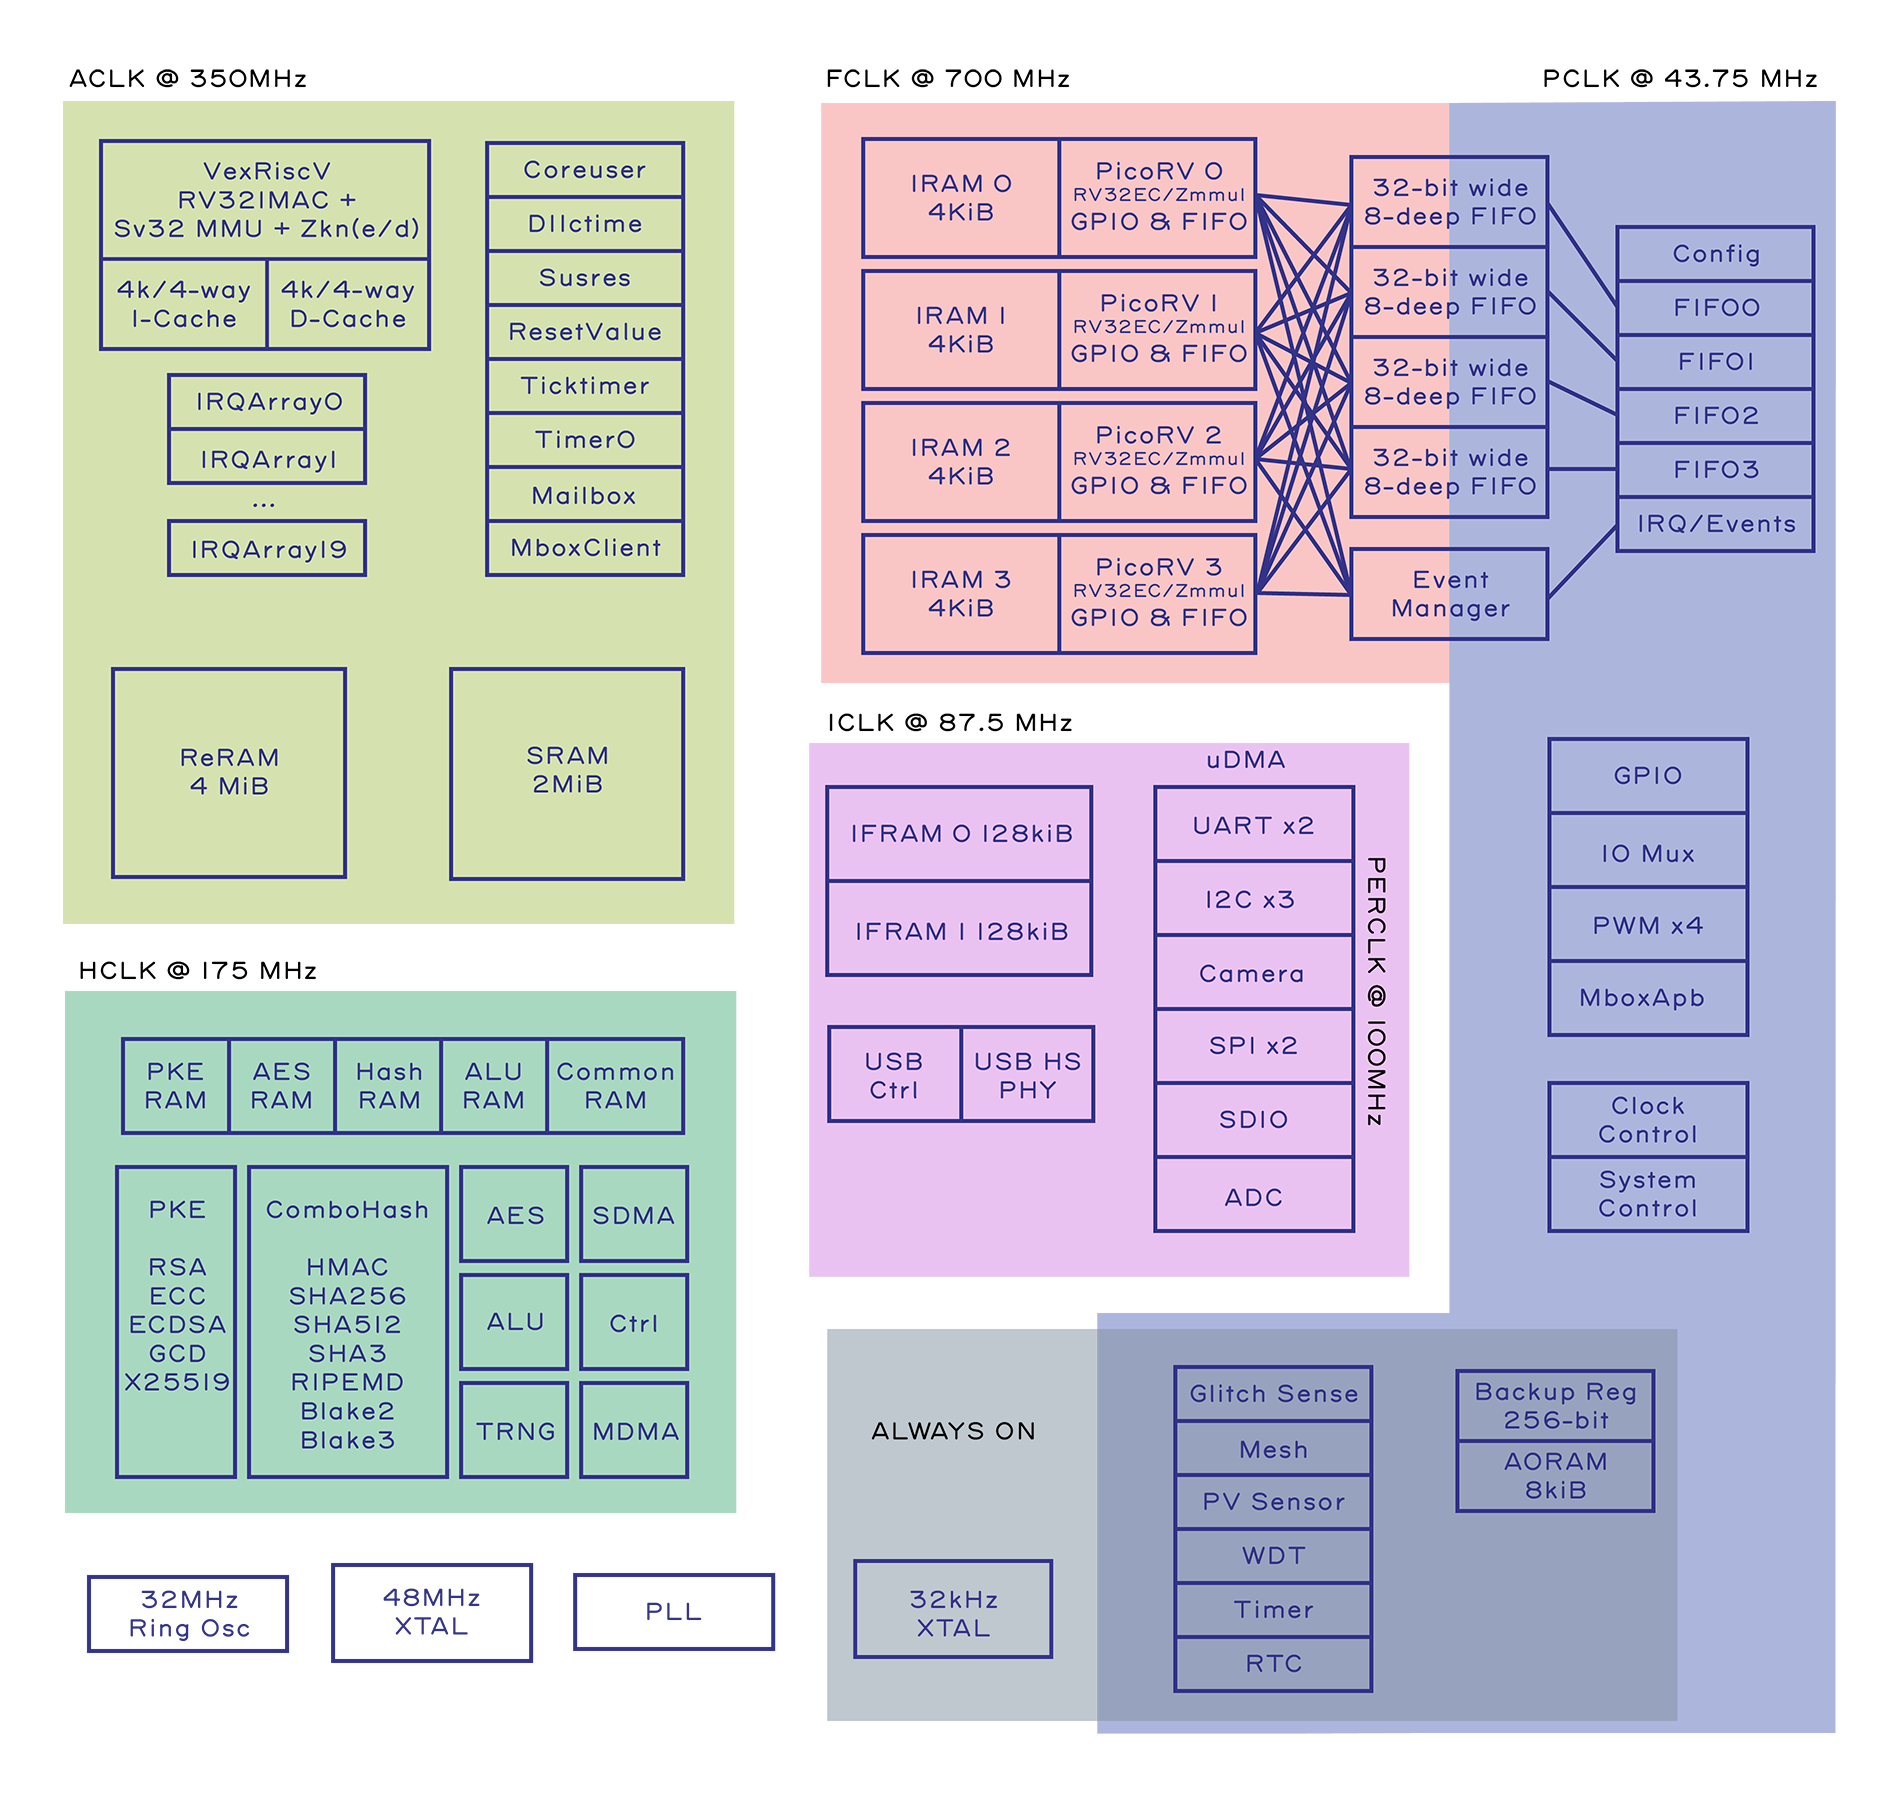 baochip/baochip-1x
Open-source silicon RTL and simulation tools for the Baochip 1x SoC, featuring a VexRiscv CPU, Verilator-based verification, and documentation for…
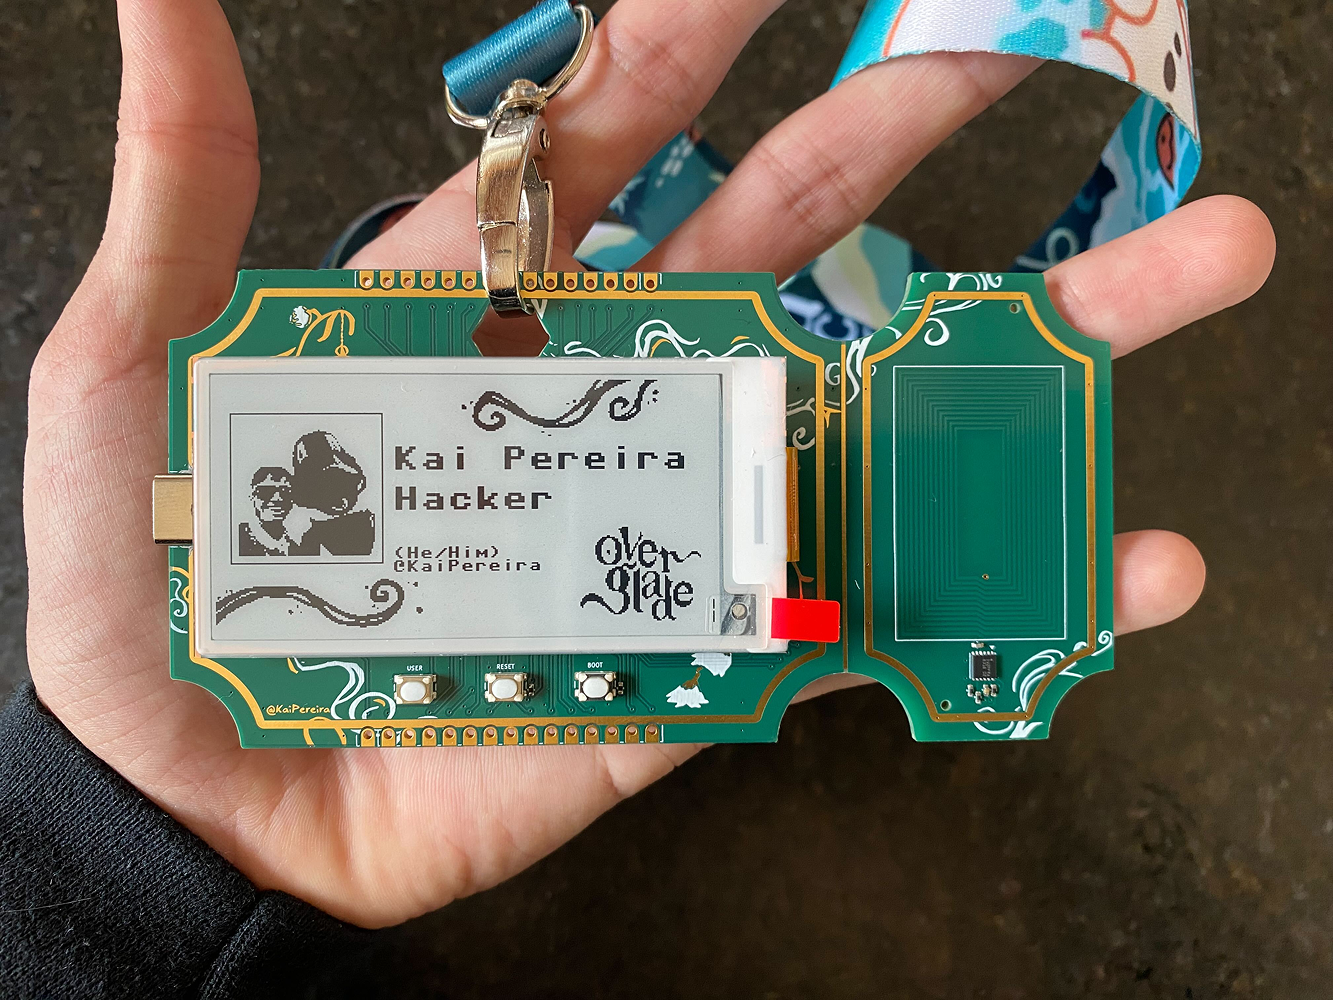 kaipereira/overglade-badges
NFC hackathon badges for the Overglade game jam in Singapore!
 tandasat/hello-vt-rp
A simple hypervisor demonstrating the use of the Intel VT-rp (redirect protection) technology.
 inokinoki/attesor
AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…
 kasnria001/pwnage24mtk
Cert exploit for MTK devices.There is a logic flaw in MTK cert verification process.Similar to CVE-2023-20696.
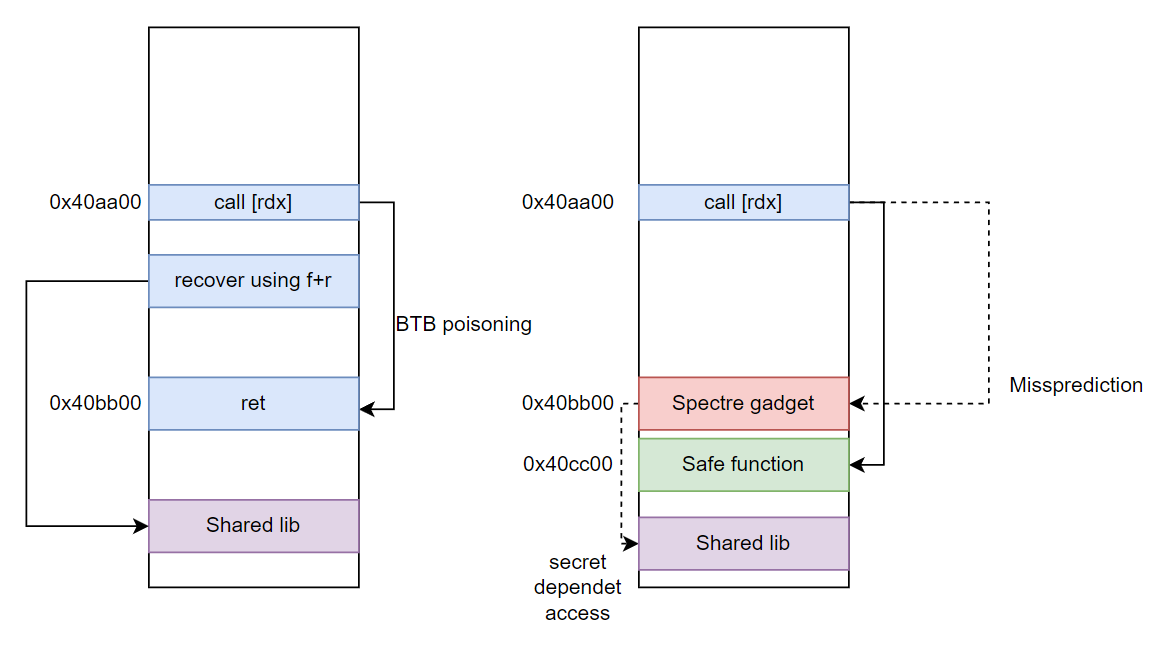 es0j/execaslr-ekoparty
Proof-of-concept exploit that bypasses ASLR on Intel CPUs by abusing branch target buffer and speculative execution to leak randomized addresses via…
 msm8916-mainline/cve-2022-22063
Security issue in the hypervisor firmware of some older Qualcomm chipsets
 cunninglogic/pixeldump_cve-2016-8462
Pixel bootlaoder exploit for reading flash storage
 ioallocate/immapper
Demonstration of Abusing the Vulnerable driver AmdTools64.sys for Physical R/W.
 spawn451/cve-2025-8061-exploit
Exploit LnvMSRIO.sys vulnerable driver
 analyticeth/chronomaly-webos
CVE-2025-38352 kernel exploit for LG webOS Smart TVs (ARM64). Achieves persistent root on real consumer hardware with novel exploitation techniques.…
 wack0/dubiousdisk
The Porygon-Z that's super effective against Secure Boot! (CVE-2022-30203, CVE-2023-21560, CVE-2023-28269, CVE-2023-28249, and more...)
 ramenfast/zenfone9-root
Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.
 d0rb/logofail-poc
This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.
 ritwick7/sudostamp
Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…