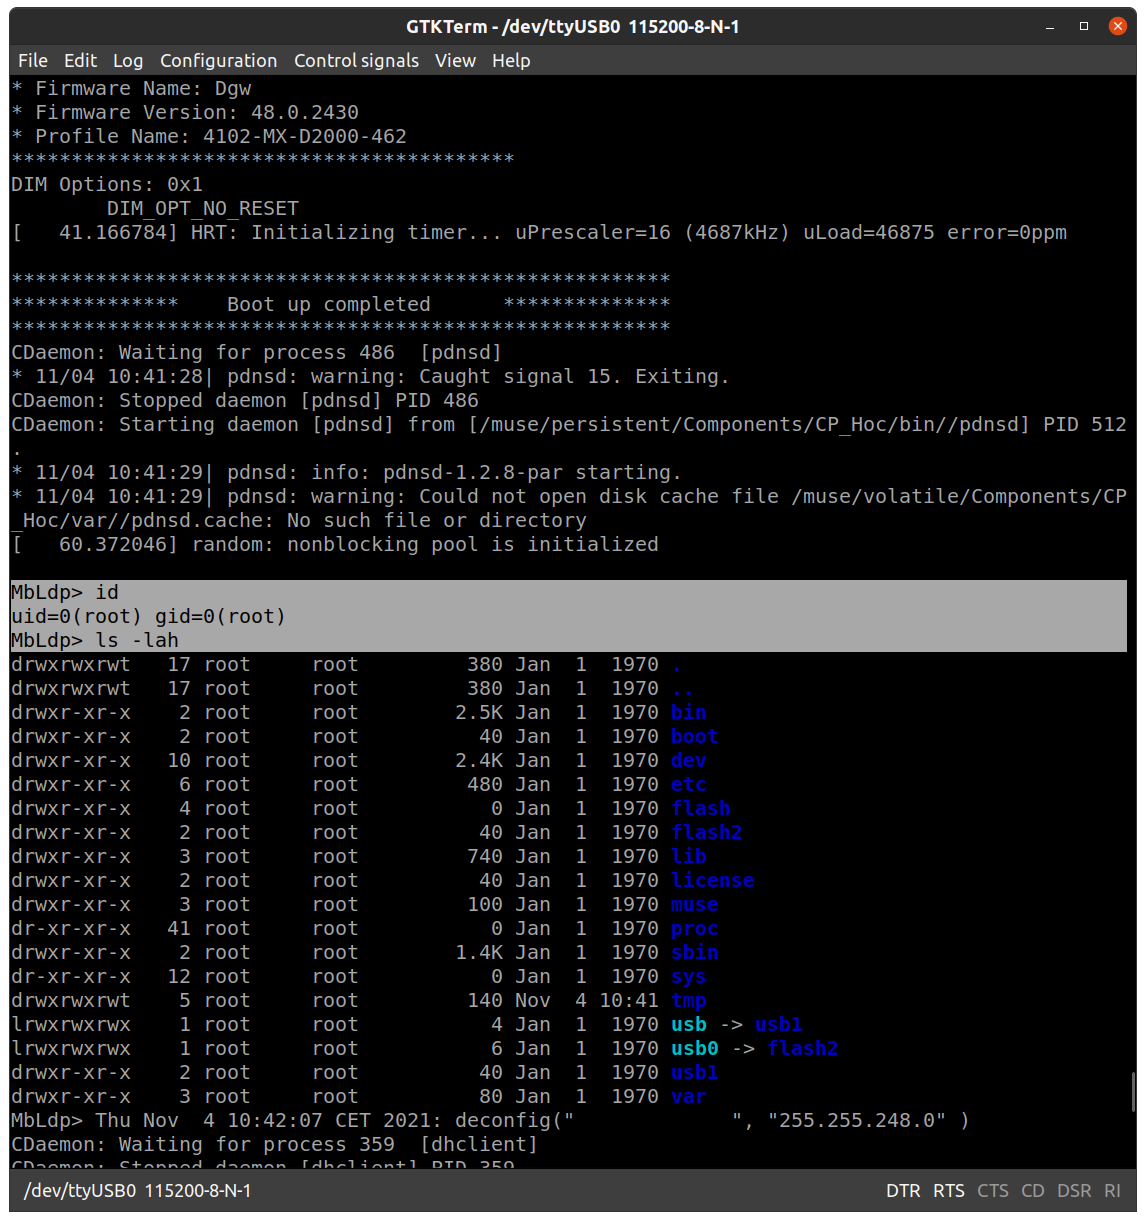
Mediatrix-CVE-2022-43096

Proof-of-concept exploit for CVE-2022-43096, demonstrating local root access via UART port on Mediatrix 4102 devices before v48.5.2718.

Proof-of-concept exploit for CVE-2022-43096, demonstrating local root access via UART port on Mediatrix 4102 devices before v48.5.2718.

Proof-of-concept demonstrating bypass of TPM-bound LUKS disk encryption on Linux systems, extracting volume keys via custom root filesystem attack.

Proof-of-concept for CVE-2025-63895: Bluetooth Classic LMP buffer overflow exploitation in JXL 9-inch Android car infotainment systems, enabling…

Proof-of-concept exploit for CVE-2025-45467, demonstrating remote code execution on Unitree Go1 robotic dogs via insecure MD5-based firmware…

Proof-of-concept exploit for CVE-2023-26976, a stack overflow vulnerability in Tenda AC6 routers, enabling remote code execution via crafted HTTP…

Proof-of-Concept for CVE-2025-2082, demonstrating function pointer overwrite via signed-to-unsigned integer conversion bug in Tesla VCSEC, leading to…

Documentation of CVE-2025-67399: physical UART debug interface exploitation on AIRTH Smart Home AQI Monitor (BK7231N SoC) enabling unauthorized…

Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…

A bunch of routers firmware images. Principally those that are not available and they do need to be extracted via JTAG, UART, desoldering flash or…

Disclosure of client-side authentication bypass in AVer camera web interface exposing unencrypted credentials via network traffic monitoring.

Minimalistic VT-x hypervisor for Windows x64 providing syscall, MSR, IDT, and kernel inline hooks plus EPT-based page substitution and TLB splitting.

Seemingly normal USB drive with a hidden security feature


Automated Vulnerability Detection Framework for Transient Execution Vulnerabilities (IEEE S&P '26)

Artifacts for the Branch Target Reuse (BTR) Spectre-v2 attack research, including microarchitecture experiments, attack-surface analysis of JIT…

CVE-2022-25375 - Demo exploit of RNDIS USB Gadget

Proof-of-concept exploiting the Toshiba qiomem.sys driver to achieve arbitrary physical memory read/write from ring 3, with a companion writeup.

Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.