
CVE-2021-3972
 killvxk/cve-2021-3972
Proof-of-concept exploit for CVE-2021-3972, demonstrating UEFI firmware variable manipulation to disable Secure Boot and change legacy boot settings.
binary-exploitationexploitationfirmware-analysis+2
4
killvxk/cve-2021-3972Proof-of-concept exploit for CVE-2021-3972, demonstrating UEFI firmware variable manipulation to disable Secure Boot and change legacy boot settings.
 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
 gmh5225/cve-2022-34683
NVIDIA GPU Display Driver for Windows contains a vulnerability in the kernel mode layer (nvlddmkm.sys) handler for DxgkDdiEscape, where a…
 risuxx/cve-2023-34853
Disclosure of CVE-2023-34853: a stack overflow vulnerability in Supermicro X12DPG-QR BIOS firmware allowing local privilege escalation to DXE Runtime…
 wack0/bitlocker-attacks
A list of public attacks on BitLocker
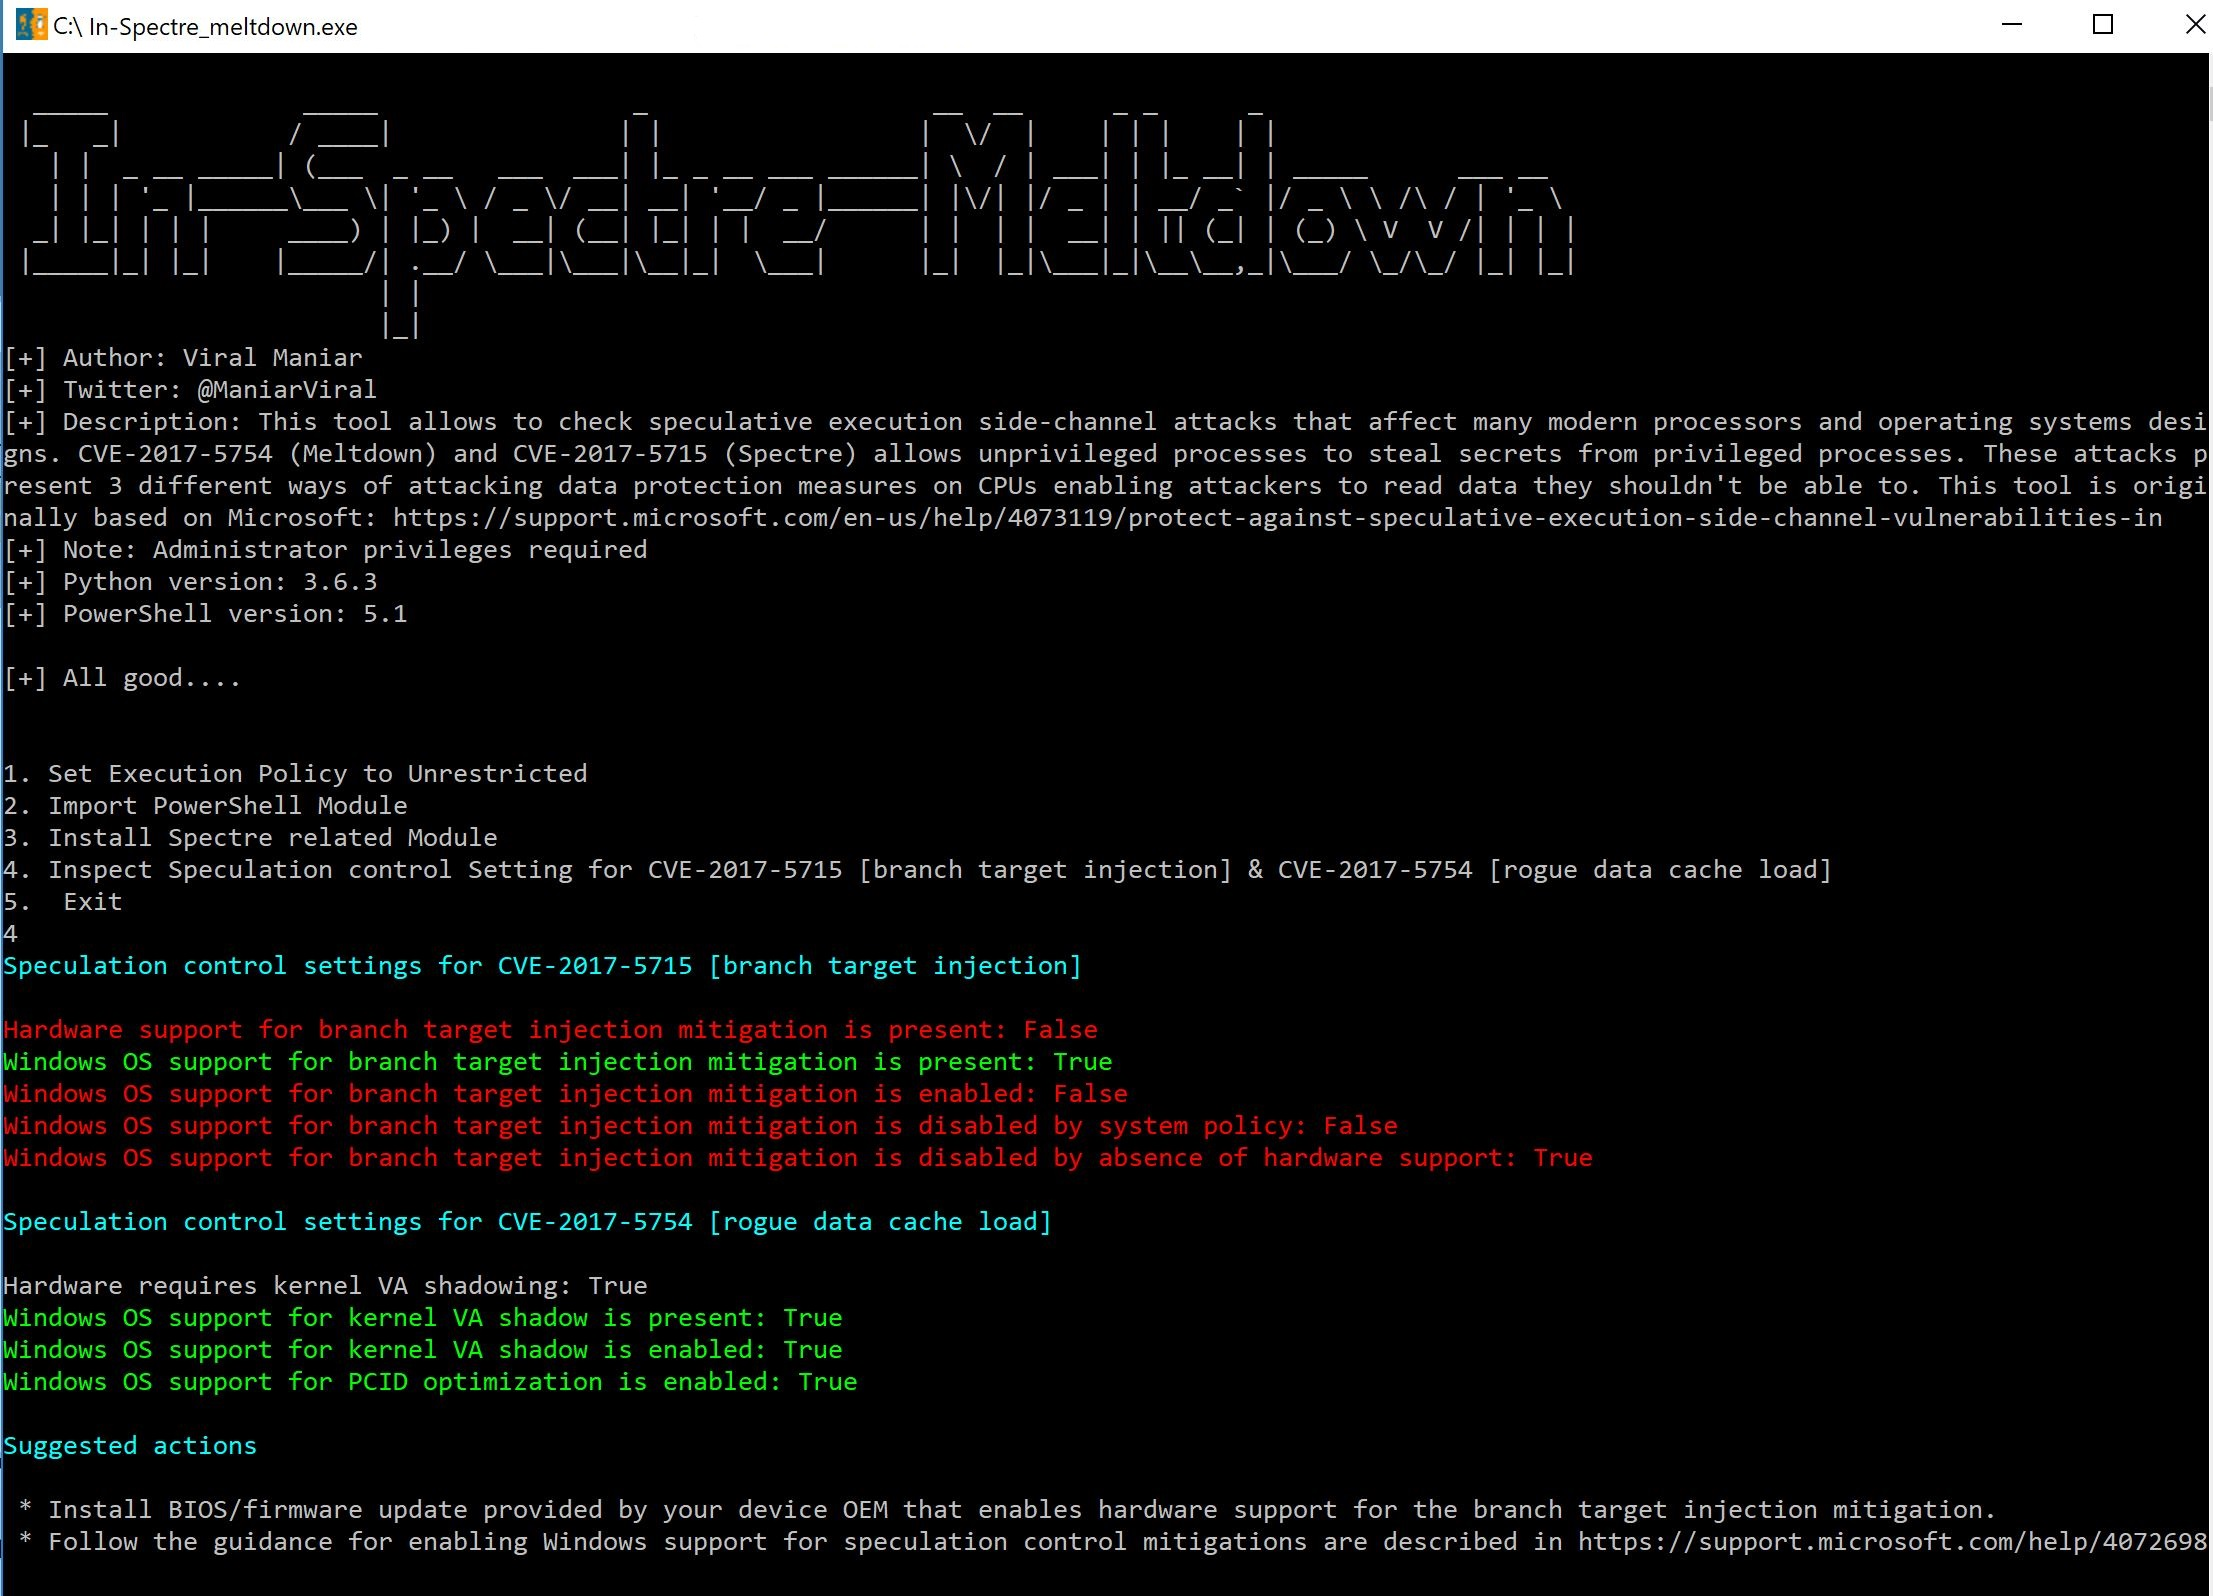 viralmaniar/in-spectre-meltdown
This tool allows to check speculative execution side-channel attacks that affect many modern processors and operating systems designs. CVE-2017-5754…
 embedi/smm_usbrt_poc
CVE-2017-5721 Proof-of-Concept
 416rehman/asus-bsitf-0-day-poc
PoC for CVE-2026-13585
 wack0/dubiousdisk
The Porygon-Z that's super effective against Secure Boot! (CVE-2022-30203, CVE-2023-21560, CVE-2023-28269, CVE-2023-28249, and more...)
 szymonh/zephyr_cve-2021-3625
CVE-2021-3625 - Sample exploits for Zephyr
 pqsec/uboatdemo
A demo server for CVE-2016-3955 (UBOAT)
 ph4r05/ledger-app-monero-1.42-vuln
PoC repository for CVE-2020-6861: Ledger Monero App Spend key Extraction
 themalwareguardian/cve-2026-79298
Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…
 bazad/iofirewirefamily-overflow
CVE-2016-7608: Buffer overflow in IOFireWireFamily.
 luismirandaacebedo/cve-2025-65855
Security advisory for CVE-2025-65855 - Multiple vulnerabilities in HelpFlash IoT OTA update mechanism
 hivesecurity/pso-printer-security-offensive
Offensive security tool for printer pentesting
 abhijithaj/dorset_smartlock_vulnerability
This repository is for Dorset_SmartLock_vulnerability. CVE-2025-25650 is suggested by MITRE which is yet to confirm.
 nsacyber/detect-cve-2017-15361-tpm
Detects Windows and Linux systems with enabled Trusted Platform Modules (TPM) vulnerable to CVE-2017-15361. #nsacyber