
CVE-2025-9961
 yt2w/cve-2025-9961
Exploit for TP-Link AX10/AX1500 stack buffer overflow in CWMP (TR-069) enabling remote code execution via ret2libc with ASLR bypass. Includes…
binary-exploitationembedded-systems-securityexploitation+5
6
yt2w/cve-2025-9961Exploit for TP-Link AX10/AX1500 stack buffer overflow in CWMP (TR-069) enabling remote code execution via ret2libc with ASLR bypass. Includes…
 retr0reg/tenda-ac8v4-rop
Exploits for Tenda Ac8v4 stack-based overflow to Remote-Code Execution via Mipsel Ropping (CVE-2023-33669 - CVE-2023-33675)
 ahmaaaaadbntaaaaa-byte/tid-the-instant-destroyer
Hardware-level security protocol for mitigating cache-based side-channel attacks.
 isec-tugraz/cjag
C implementation of a cache-based jamming agreement that establishes a cross-VM cache covert channel between co-located virtual machines for research…
 nccgroup/frisbeelite
A GUI-based USB device fuzzer
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
 iceman1001/proxmark3
[Deprecated] Iceman Fork, the most totally wicked fork around if you are into proxmark3
 nervosnetwork/ckb-vm
CKB's vm, based on open source RISC-V ISA
 nccgroup/umap2
Umap2 is the second revision of NCC Group's python based USB host security assessment tool.
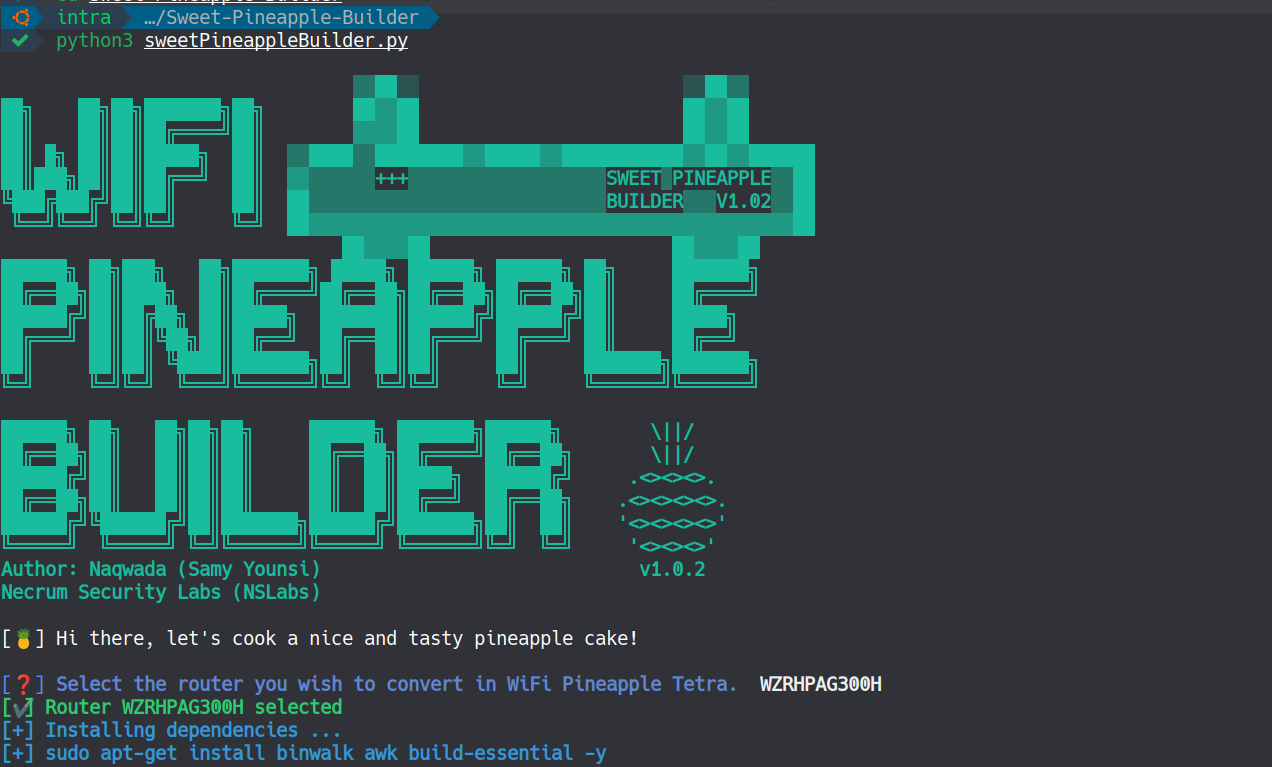
 0xsamy/sweet-pineapple-builder
Build your own custom WiFi Pineapple Tetra firmware tailored to any based MIPS 24Kc architecture router. (WiFi Pineapple Tetra DIY)
 gmh5225/disk-spoofer
Kernel driver based disk size and sector query spoofing program, can evade Windows WMIC query.
 lnversed/cve-2020-10882
cve based on vulnerable cisco's Archer A7 routers
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
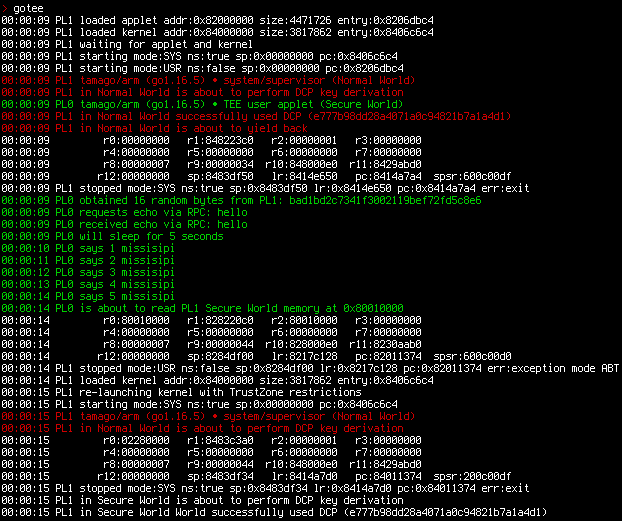 usbarmory/gotee
Go Trusted Execution Environment (TEE)
 nullpxl/banrays
Glasses to detect smart-glasses that have cameras. Ray-BANNED
 schumilo/vusbf
A QEMU/KVM-based USB fuzzing framework that finds device-driver bugs via reproducible VM execution, multiprocessing, and XML testcase generation.
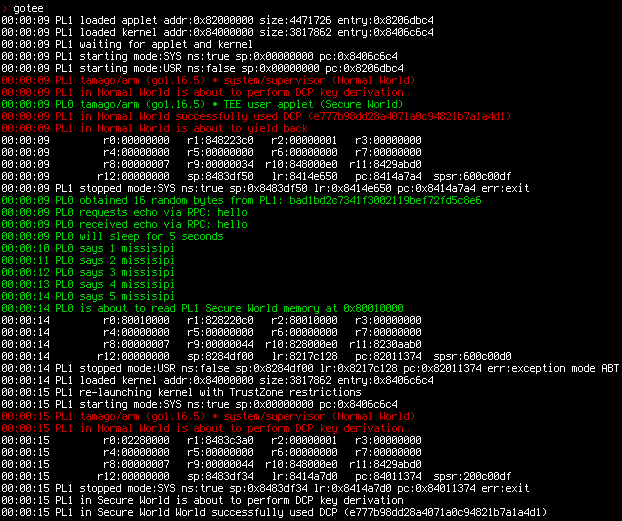 usbarmory/gotee-example
GoTEE - example application
 nccgroup/cecster
A GUI-based tool to perform security testing against the HDMI CEC (Consumer Electronics Control) and HEC (HDMI Ethernet Channel) protocols