

flipperzero-firmware
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
bluetooth-securityembedded-systems-securityhardware-hacking+6
16.8k
flipperdevices/flipperzero-firmwareFlipper Zero firmware source code
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 adamlaurie/rfidiot
Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
 ramenfast/zenfone9-root
Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.
 sunnypatell/basalt
World's first hazard checker for NVIDIA Blackwell (sm_120), with an assembler and scheduler matched against their own compiler byte for byte. The…
 cecio/usbvalve
Expose USB activity on the fly
 symbrkrs/ps5-uart
Interface for interacting with PlayStation 5 EMC and EFC
 inokinoki/attesor
AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…
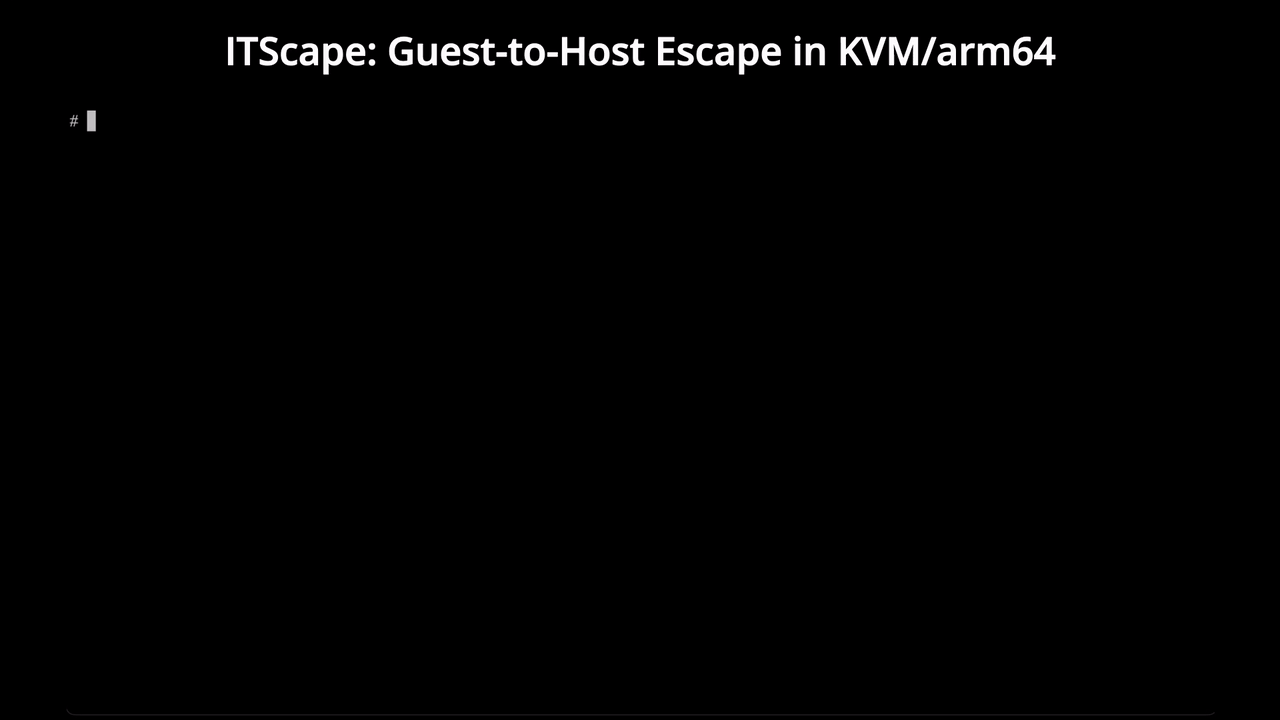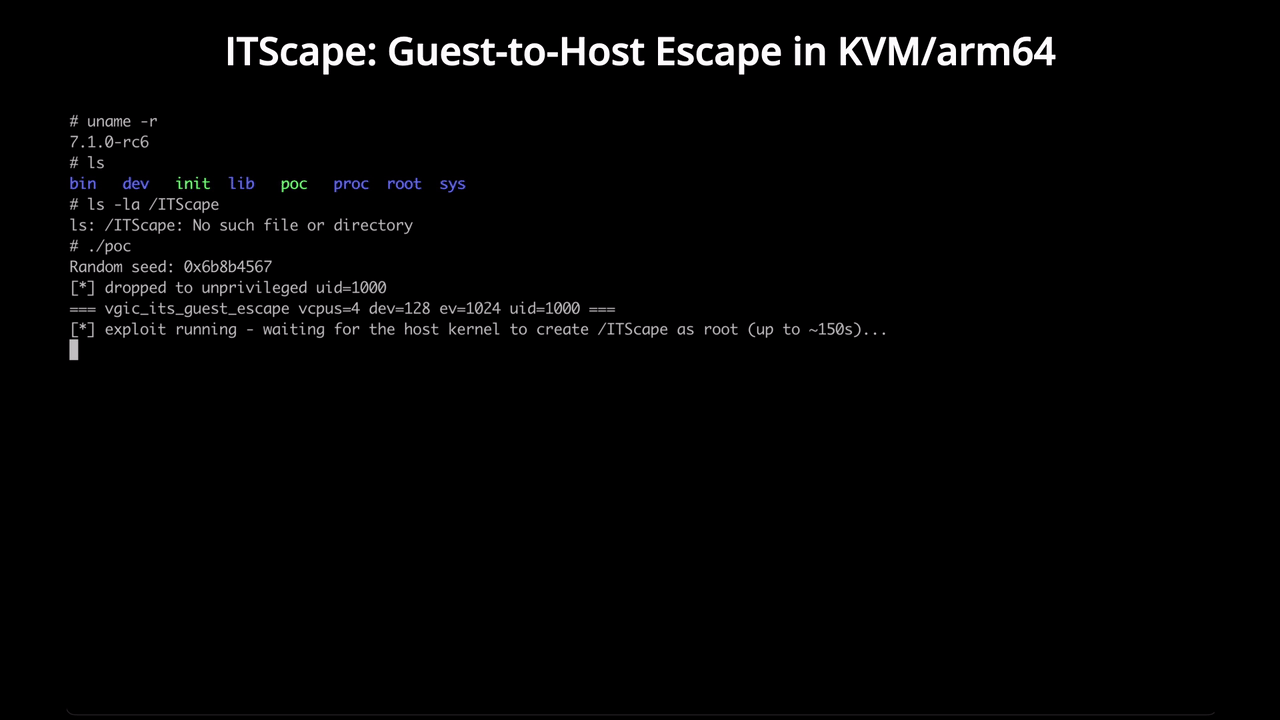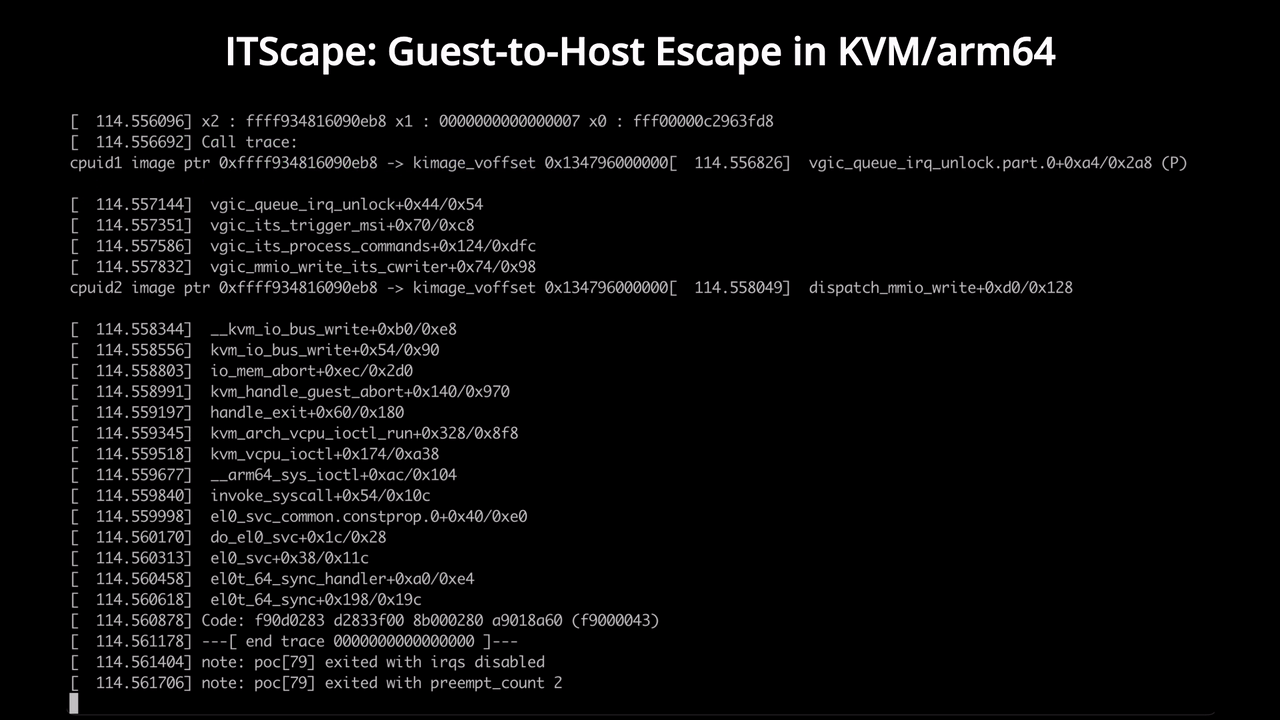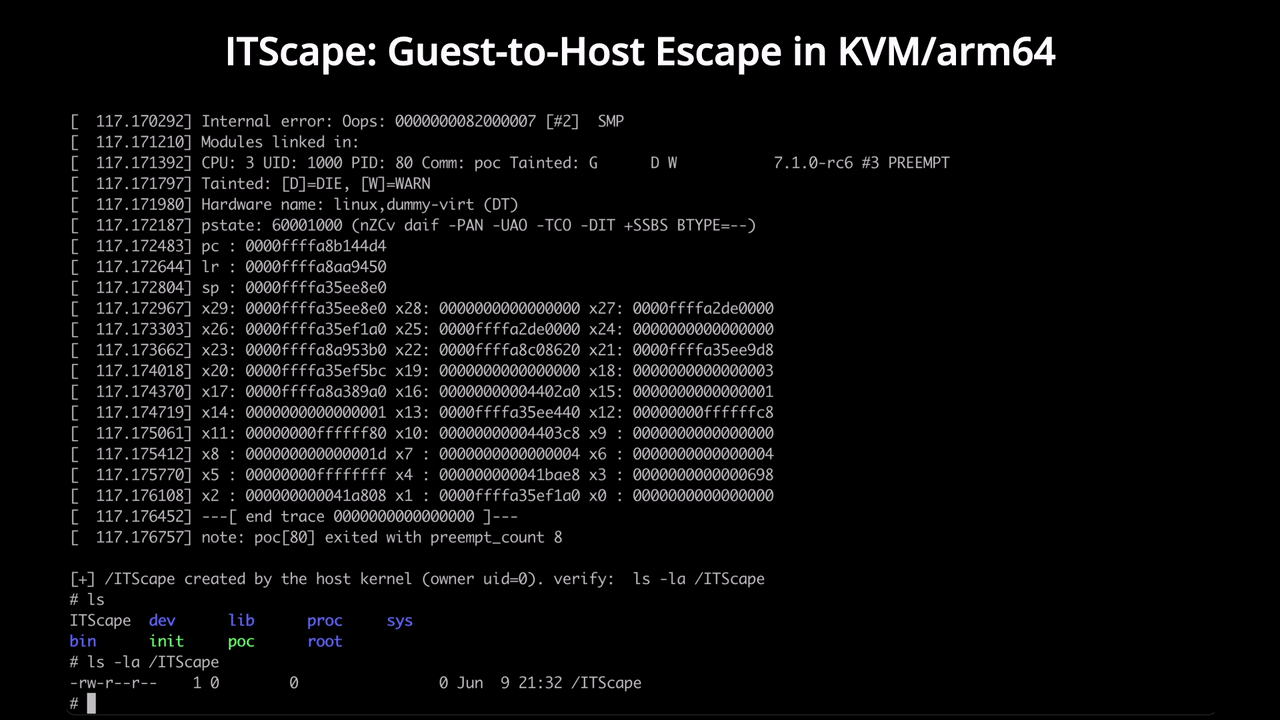 v4bel/itscape
CVE-2026-46316 guest-to-host KVM/arm64 escape exploit exploiting a race condition in vGIC-ITS emulation to achieve host kernel code execution from an…
 george0papasotiriou/cve-2026-22013-hardware-wallet-usb-descriptor-buffer-overflow
Stack buffer overflow PoC for a hardware wallet USB descriptor parser (CVE-2026-22013), showing return-address overwrite and code execution via…
 keowu/sjcam
Reverse engineering research and custom firmware for Allwinner V3-based IoT cameras, including firmware parsers, an AVIOCTRL client, and a…
 redr0nin/code-27-companion-hub-exploits
Proof of concept for CVE-2026-36027 and CVE-2026-36028
 christbowel/cve-2026-56111
Proof-of-concept exploit for CVE-2026-56111, an out-of-bounds write in the M421 G-code handler of Marlin Firmware, demonstrating constrained memory…
 hunt-benito/samsung-exynos-sms-stack-overflow-cve-2025-54328-critical-zero-click-baseband-rce
Conceptual PoC for CVE-2025-54328, a critical zero-click stack buffer overflow in Samsung Exynos baseband firmware's SMS RP-DATA parser, enabling…
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 0xblackash/cve-2026-11499
CVE-2026-11499