
ThrottleStopPoC
 wqsv/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
binary-exploitationexploitationhardware-security+5
18
wqsv/throttlestoppocCVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 eiln/ane
Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 gmh5225/disk-spoofer
Kernel driver based disk size and sector query spoofing program, can evade Windows WMIC query.
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 themalwareguardian/cve-2026-79298
Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 doctormord/philips-pm-5139-5138a-5136-firmware-project
Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…
 eddinos2/cve-2026-64747
Root-cause analysis and reachability PoC for CVE-2026-64747, a buffer overflow in the AppleAVE2 kernel extension. Includes reversed IOKit wire…
 al3xtjames/ghidra-firmware-utils
Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 isukasanuj/cve-2026-85769
Proof-of-concept exploit for CVE-2026-85769, a heap out-of-bounds read in libtpms TPM 2.0 state deserialization, demonstrating denial of service via…
 sys-dissect/jiopc-architecture-whitepaper
Technical whitepaper dissecting JioPC cloud VDI architecture, including hardware specs, session termination mechanisms, and security limitations,…
 bakos-sandor-nx/teamcity-cve-2026-63077-remediation
JetBrains TeamCity On-Premises CVE-2026-63077 Emergency Hardening & Patch Runbook Package
 withsecurelabs/usb-ninja-detection-poc
Detects USB Ninja keystroke injection attacks by logging keystrokes and application events, providing a proof-of-concept for defensive monitoring.
 pq-code-package/mlkem-native
Secure, fast, and portable C90 implementation of ML-KEM / FIPS 203
 renich/pyrite
Hardware-bound & Cloud-gated binary execution, cryptographic provenance, and anti-tamper envelope sealing for Crystal.
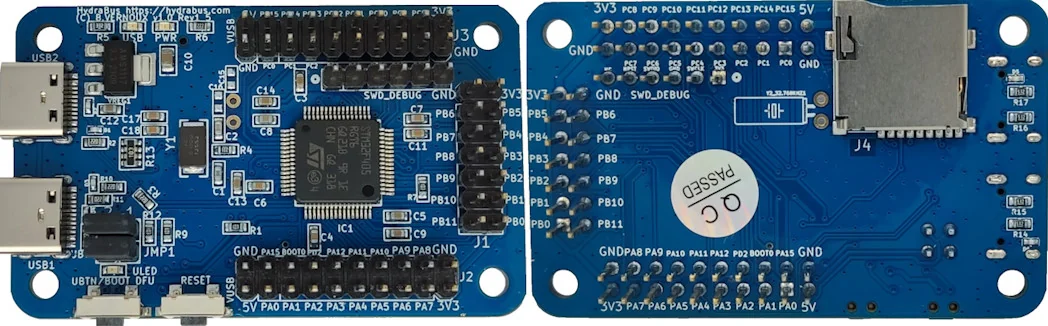 hydrabus/hydrafw
Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…