
ane
 eiln/ane
Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…
ai-securitybinary-analysisembedded-systems-security+3
535
eiln/aneReverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 al3xtjames/ghidra-firmware-utils
Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 isukasanuj/cve-2026-85769
Proof-of-concept exploit for CVE-2026-85769, a heap out-of-bounds read in libtpms TPM 2.0 state deserialization, demonstrating denial of service via…
 withsecurelabs/usb-ninja-detection-poc
Detects USB Ninja keystroke injection attacks by logging keystrokes and application events, providing a proof-of-concept for defensive monitoring.
 pq-code-package/mlkem-native
Secure, fast, and portable C90 implementation of ML-KEM / FIPS 203
 owasp/owasp-top-10-ai-infrastructure-security-risks
A practical framework identifying and prioritizing the top security risks in AI datacenter infrastructure, covering hardware, networking, management…
 adamlaurie/rfidiot
Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…
 nfc-tools/libfreefare
A convenience API for NFC cards manipulations on top of libnfc.
 nfc-tools/mfcuk
Recovers cryptographic keys from MiFare Classic RFID cards using DarkSide and nested-auth attacks for security testing of NFC/RFID systems.
 rfidresearchgroup/chameleonultra
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…
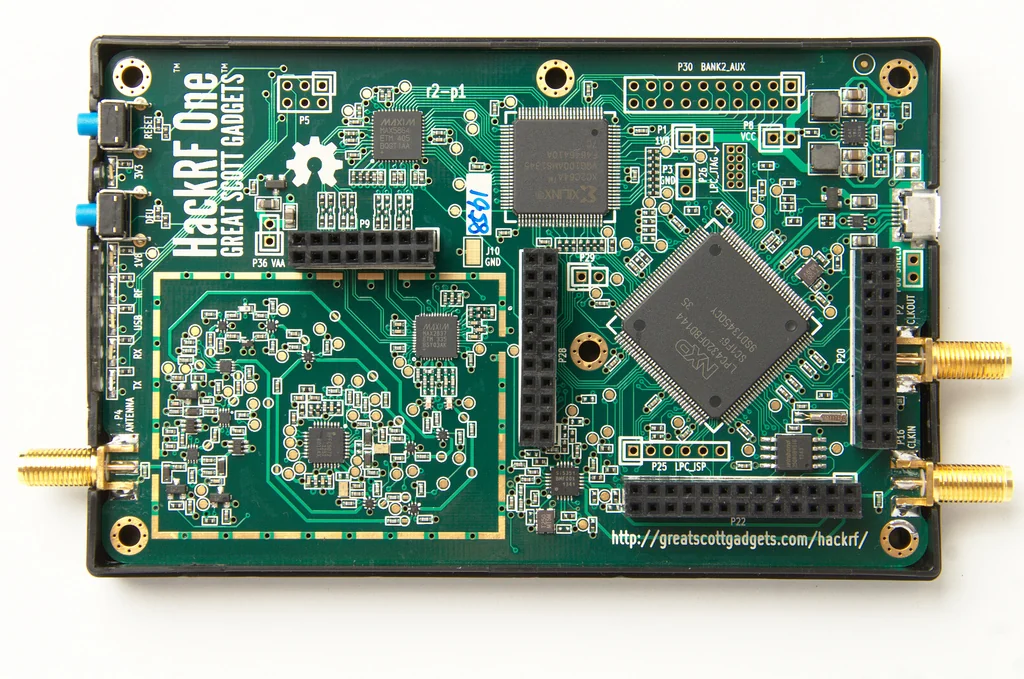 greatscottgadgets/hackrf
Low-cost open-source software-defined radio platform with hardware designs and firmware for RF transmission, reception, and signal analysis from 1…
 newaetech/chipwhisperer
Open-source hardware security toolchain for power trace capture, side-channel analysis, and glitching/fault-injection attacks on embedded devices and…
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 sigrokproject/libsigrok
C library providing a portable API for acquiring signals from logic analyzers, oscilloscopes, multimeters, and other test instruments, with…
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…