

Barzakh
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
defensive-toolsembedded-systems-securityfirmware-analysis+6
7
yasindce1998/barzakhRing -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 mein-0/gvcidrv64
Proof-of-concept exploit for Gigabyte's GVCIDrv64.sys kernel driver, achieving local privilege escalation via arbitrary physical memory and I/O port…
 foxboron/attezt
An open-source TPM device-attest-01 CA server
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 ramenfast/zenfone9-root
Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 sys-dissect/jiopc-architecture-whitepaper
Technical whitepaper dissecting JioPC cloud VDI architecture, including hardware specs, session termination mechanisms, and security limitations,…
 bakos-sandor-nx/teamcity-cve-2026-63077-remediation
JetBrains TeamCity On-Premises CVE-2026-63077 Emergency Hardening & Patch Runbook Package
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
 renorobert/virtualbox-cve-2018-2844
C-based proof-of-concept exploit for VirtualBox CVE-2018-2844, demonstrating a heap overflow vulnerability in the hypervisor's network driver for…
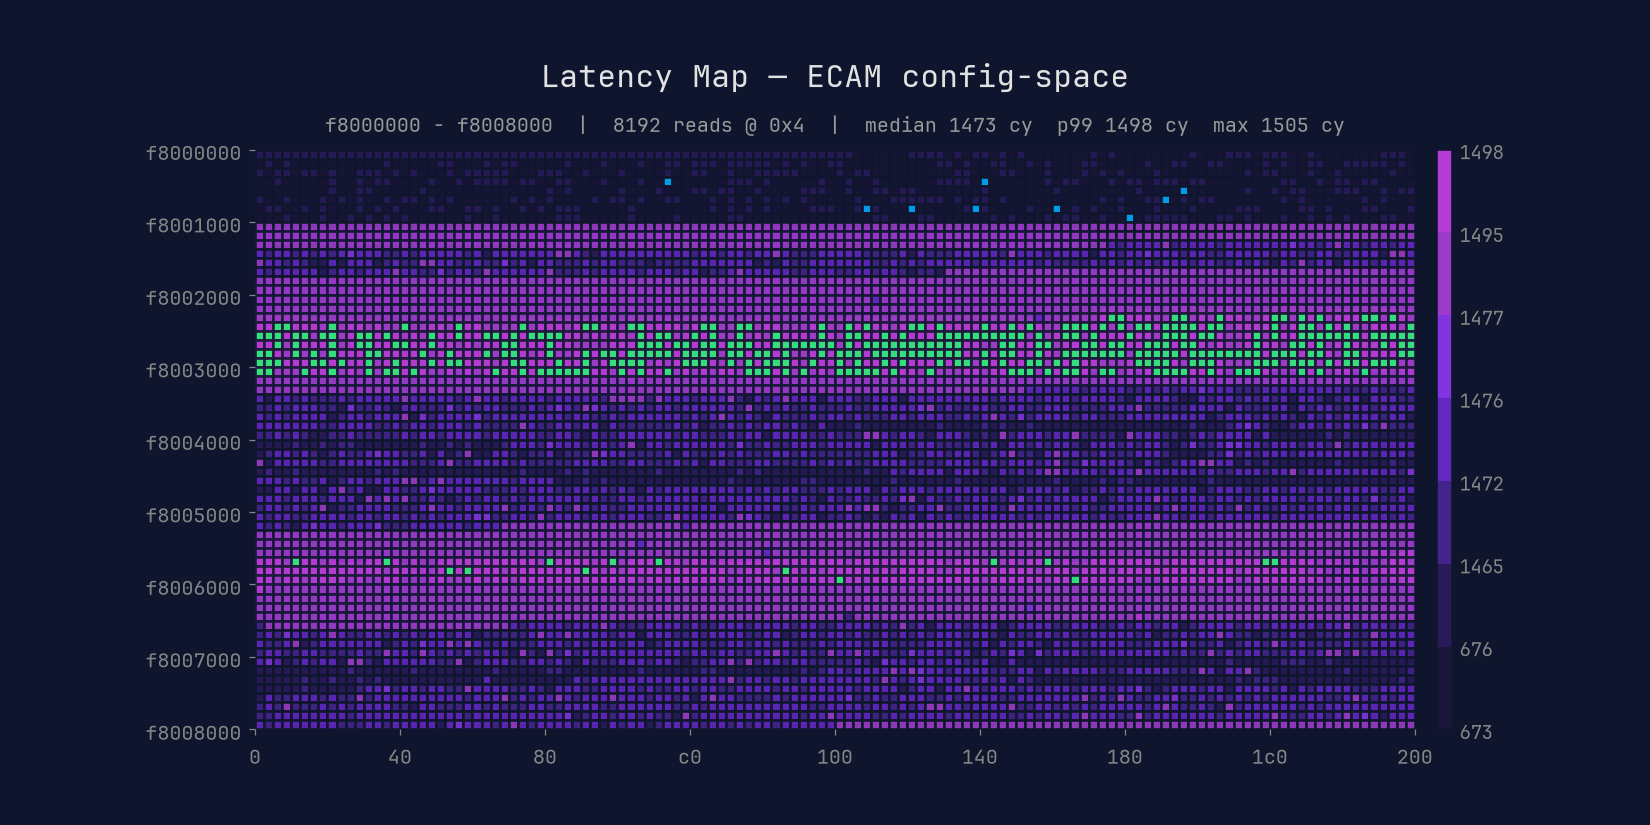 xoreaxeaxeax/mmiotic
Latency x-ray for undocumented hardware
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
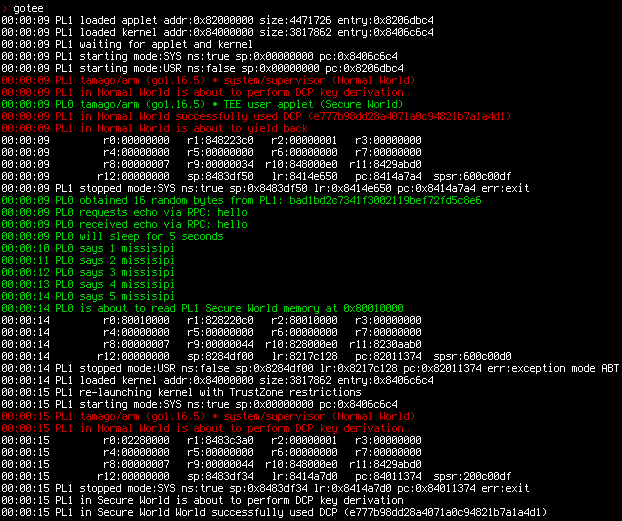 usbarmory/gotee-example
GoTEE - example application
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 intellabs/kafl
A fuzzer for full VM kernel/driver targets