
mousejack
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
exploitationfirmware-analysishardware-iot-security+3
1.4k
bastilleresearch/mousejackResearch tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
 hunt-benito/go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset
PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.
 steveakawlabs/marmalade-2-cve-2025-67780-exploit
Exploit PoCs for MARMALDE 2 (CVE-2025-67780) vulnerability in Starlink Dishes
 xoreaxeaxeax/rosenbridge
Hardware backdoors in x86 CPUs
 entysec/camraptor
CamRaptor is a tool that exploits several vulnerabilities in popular DVR cameras to obtain network camera credentials.
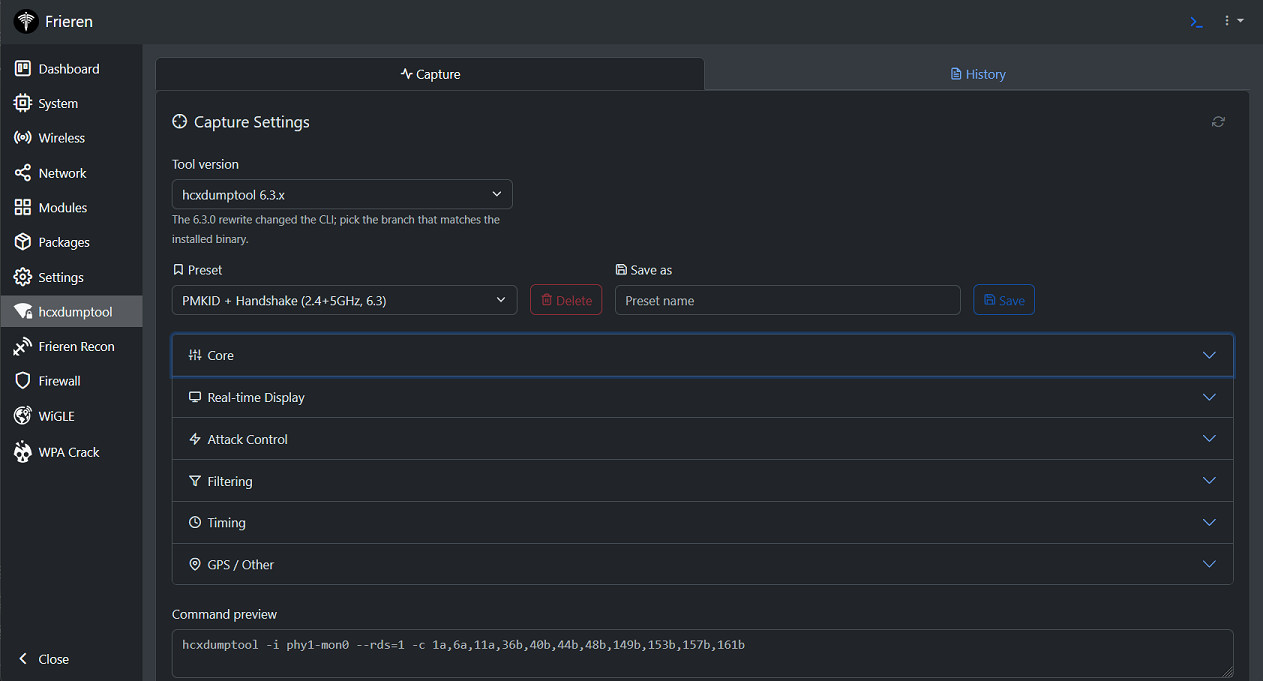 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 luismirandaacebedo/security_articles
Technical articles detailing IoT vulnerability research, including WiFi communication flaws and firmware update weaknesses in connected devices, with…
 hacefresko/cve-2021-4045
Exploit for command injection vulnerability found in uhttpd binary from TP-Link Tapo c200 IP camera
 syss-research/radio-hackbox
PoC tool to demonstrate vulnerabilities in wireless input devices
 marcnewlin/presentation-clickers
Keystroke injection vulnerabilities in wireless presentation clickers
 dpt/chasehq
Chase H.Q. for ZX Spectrum — reverse-engineered and reconstructed in portable C
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.
 park07/amradio
FPGA-based 12-channel AM radio broadcast system with formal verification of a hardware watchdog for fail-safe emergency alert transmission in…
 mr-xn/cve-2022-25064
Python exploit for TP-Link TL-WR840N RCE (CVE-2022-25064) via crafted IPv6 address payload in the router's CGI interface, enabling remote command…
 enki-kr/cve-2026-32223-usbprint-exploit
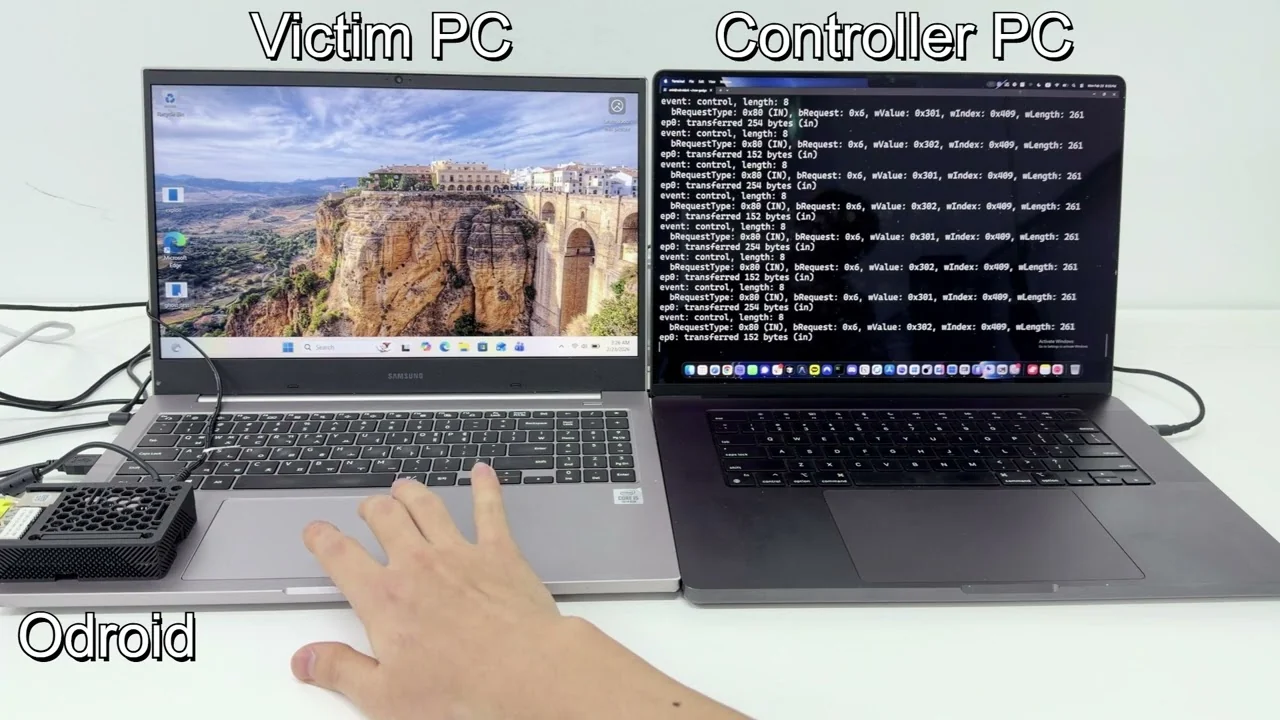
Proof-of-concept exploit for CVE-2026-32223, a heap-based buffer overflow in Windows USB print driver (usbprint.sys), achieving local privilege…
 h00die/msf-testing-scripts
Metasploit modules in testing
 demining/bluetooth-attacks-cve-2025-27840
Bitcoin Cryptanalysis: CVE-2025-27840 Vulnerability in ESP32 Microcontrollers Puts Billions of IoT Devices at Risk via Wi-Fi & Bluetooth
 dozernz/bugstropics
Supporting material for the "Hunting Bugs In The Tropics" DEFCON 30 talk