

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
20 results
hal preview

hal

GitHubemsec/hal

HAL – The Hardware Analyzer

binary-analysiseducationembedded-systems-security+6
8404h 26m ago
CVE-2021-44827 preview

CVE-2021-44827

GitHubfull-disclosure/cve-2021-44827

Proof-of-concept exploit for authenticated remote code execution (CVE-2021-44827) targeting TP-Link Archer C20i routers. Provides post-exploitation…
embedded-systems-securityexploitationhardware-iot-security+4
44 years ago
CVE-2018-20162-digi-lr54-restricted-shell-escape preview

CVE-2018-20162-digi-lr54-restricted-shell-escape

GitHubstigtsp/cve-2018-20162-digi-lr54-restricted-shell-escape

Proof-of-concept exploit for CVE-2018-20162: sandbox escape in Digi TransPort LR54 LTE router via SIGINT handling flaw, yielding root shell access.
embedded-systems-securityexploitationhardware-iot-security+5
7 years ago
sagemcom-fast-3890-exploit preview

sagemcom-fast-3890-exploit

GitHublyrebirds/sagemcom-fast-3890-exploit

Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…
binary-exploitationembedded-systems-securityexploitation+4
2276 years ago
hazel-cve-2026-43499 preview

hazel-cve-2026-43499

GitHubdorlow/hazel-cve-2026-43499

Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
android-securitybinary-exploitationembedded-systems-security+6
11 month ago
Podroid preview

Podroid

GitHubextv/podroid

A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.

android-securitycontainer-securityhardware-iot-security+3
3.6k7 days ago
PortGuard preview

PortGuard

GitLabk3rnix/portguard

USB port access control tool for Debian with whitelist management, automatic background scanning daemon, and CLI interface to block or allow USB…
configuration-auditingdefensive-toolshardware-iot-security+3
29 months ago
hisilicon-dvr-telnet preview
Archived

hisilicon-dvr-telnet

GitHubsnawoot/hisilicon-dvr-telnet

PoC materials for article https://habr.com/en/post/486856/
embedded-systems-securityexploitationhardware-iot-security+3
1391 year ago
samsung-q60t-exploit preview

samsung-q60t-exploit

GitHubsynacktiv/samsung-q60t-exploit

Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…
binary-exploitationembedded-systems-securityexploitation+4
934 years ago
wifisting preview

wifisting

GitHubyslxotwod/wifisting

GTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…
bluetooth-securitycommand-and-controlhardware-iot-security+9
2614 days ago
RancidCrisco preview

RancidCrisco

GitHubfullspectrumdev/rancidcrisco

Proof-of-concept exploit for CVE-2023-20126 targeting Cisco SPA phone adapters. Uploads malicious firmware to gain a root shell on port 23000/tcp via…

embedded-systems-securityexploitationfirmware-analysis+5
243 years ago
cve-2025-21479_iqooneo8 preview

cve-2025-21479_iqooneo8

GitHubqingizi7/cve-2025-21479_iqooneo8

Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
android-securitybinary-exploitationexploitation+6
61 month ago
cve-2026-1668-poc preview

cve-2026-1668-poc

GitHubwuyou6956-glitch/cve-2026-1668-poc

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
binary-exploitationembedded-systems-securityexploitation+6
6 months ago
tesla-security-research preview

tesla-security-research

GitHubanalyticeth/tesla-security-research

Vulnerability research on Tesla Model 3/Y infotainment systems. 6 vulnerabilities, 4 CVEs (CVE-2022-42005 through CVE-2022-42008). Root shell,…
command-and-controldata-exfiltrationeducation+7
74 months ago
CVE-2020-25749 preview

CVE-2020-25749

GitHubjet-pentest/cve-2020-25749

Proof-of-concept exploit for CVE-2020-25749 targeting Rubetek cameras with hardcoded Telnet credentials, enabling remote root shell access and full…
embedded-systems-securityexploitationhardware-iot-security+3
6 years ago
dlink_shell_poc preview
Archived

dlink_shell_poc

GitHubcr0n1c/dlink_shell_poc

Dlink 615/815 shell PoC

exploitationhardware-iot-securityiot-security+2
498 years ago
samsung_tizen_tv_root preview

samsung_tizen_tv_root

GitHubcommit-regrets/samsung_tizen_tv_root

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…
binary-exploitationembedded-systems-securityexploitation+8
1510h 51m ago
spectre-meltdown-checker preview

spectre-meltdown-checker

GitHubspeed47/spectre-meltdown-checker

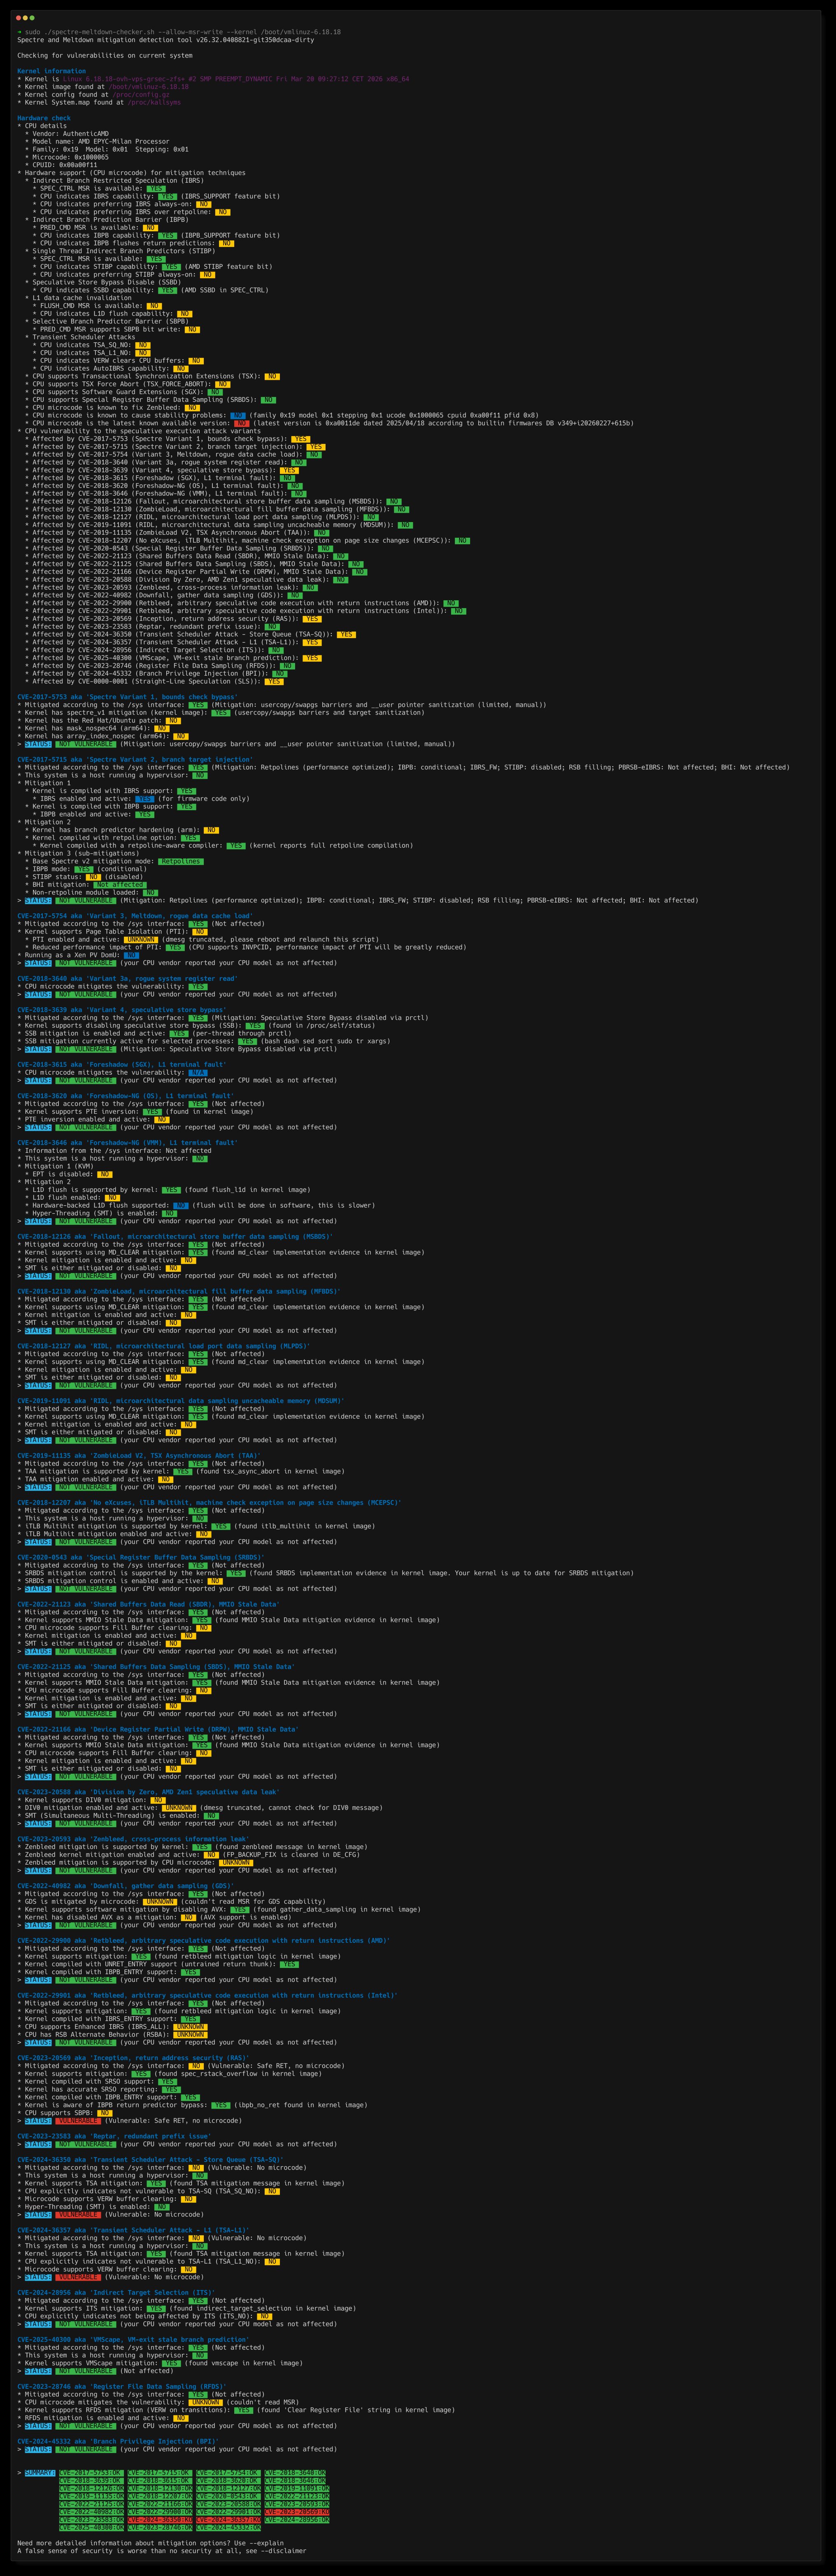
Reptar, Downfall, Zenbleed, ZombieLoad, RIDL, Fallout, Foreshadow, Spectre, Meltdown vulnerability/mitigation checker for Linux & BSD

defensive-toolseducationhardware-iot-security+5
4.0k1 month ago
Previous12Next