CVE-2026-32223-USBPrint-Exploit

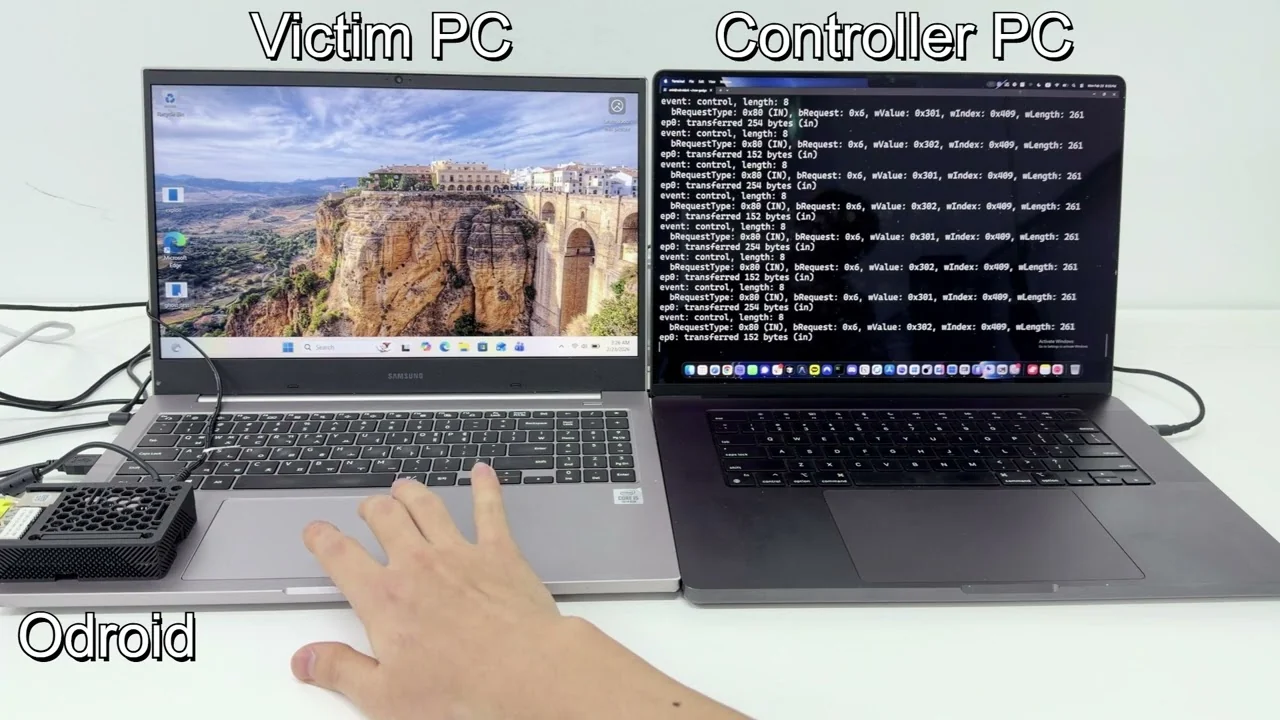
Proof-of-concept exploit for CVE-2026-32223, a heap-based buffer overflow in Windows USB print driver (usbprint.sys), achieving local privilege…

Proof-of-concept exploit for CVE-2026-32223, a heap-based buffer overflow in Windows USB print driver (usbprint.sys), achieving local privilege…

Local streaming tool for cheap WiFi cameras that bypasses cloud services and phone apps. Discovers cameras on your network, authenticates via PPPP…

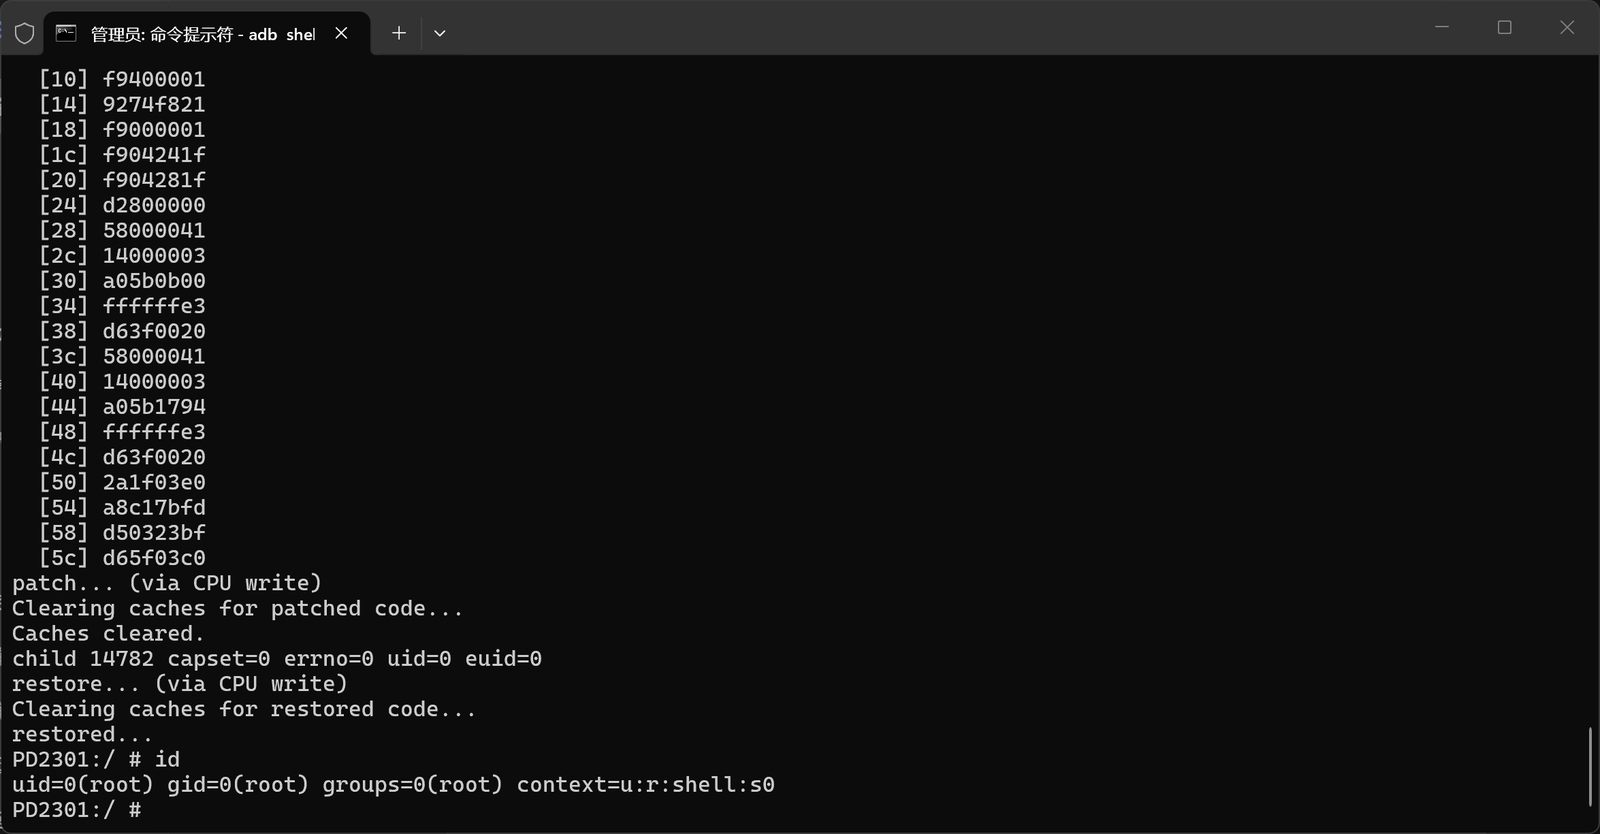
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell

Proof-of-concept exploit for TP-Link TDDP authentication bypass (CVE-2026-0834) that sends crafted packets to execute administrative commands like…

An issue in Shenzen Tenda Technology CP3V2.0 V11.10.00.2311090948 allows a local attacker to obtain sensitive information via the password component.

Sets up a local Tapo C200 using CVE-2021-4045

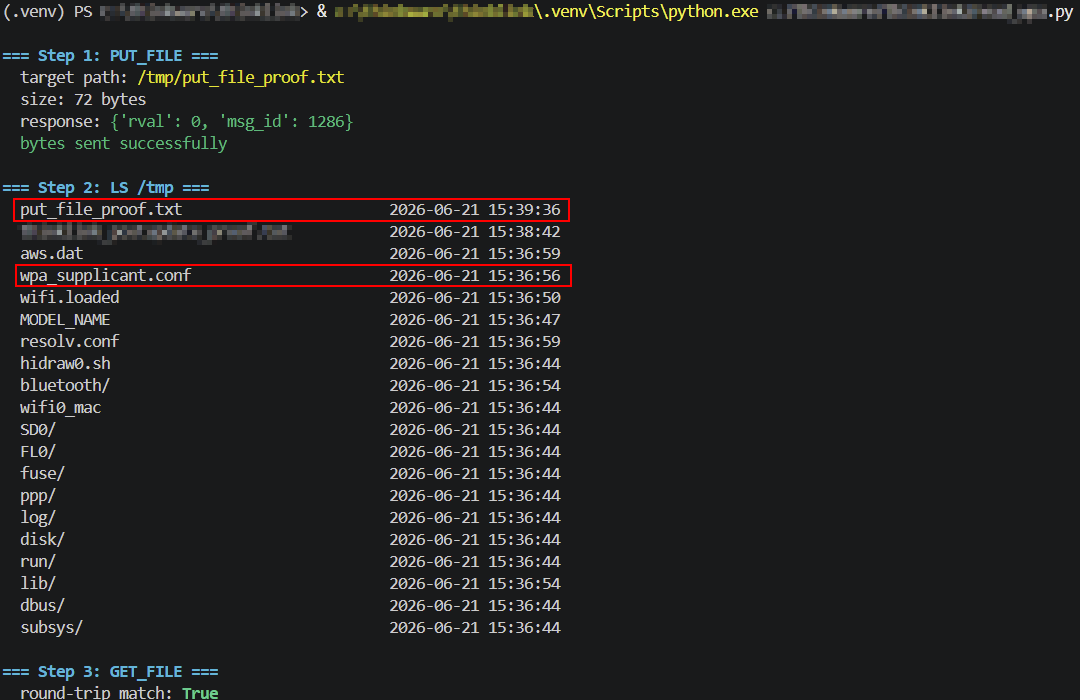
Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…

Three unauthenticated vulnerabilities in the Thinkware U3000 dashcam's local WiFi control protocol: arbitrary file write, arbitrary file read, and…

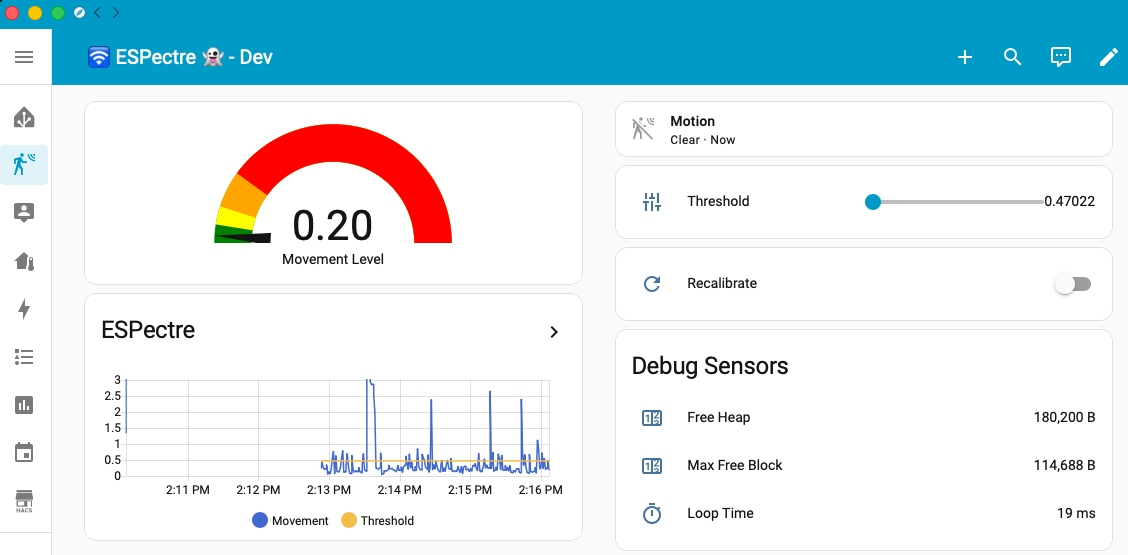
ESPectre - Motion detection system based on Wi-Fi spectre analysis (CSI), with Home Assistant integration.

HomePwn - Swiss Army Knife for Pentesting of IoT Devices

Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…

Red portatil de reconocimiento inteligente con IA offline

PoC for CVE-2024-5633