
Antecursor
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
command-and-controlexploitationhardware-iot-security+5
5
antecursor/antecursorAutonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 lyrebirds/sagemcom-fast-3890-exploit
Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…
 synacktiv/cve-2021-27246_pwn2own2020
Exploit code for CVE-2021-27246 targeting TPLink Archer routers, demonstrated at Pwn2Own 2020 Tokyo. Includes proof-of-concept for remote code…
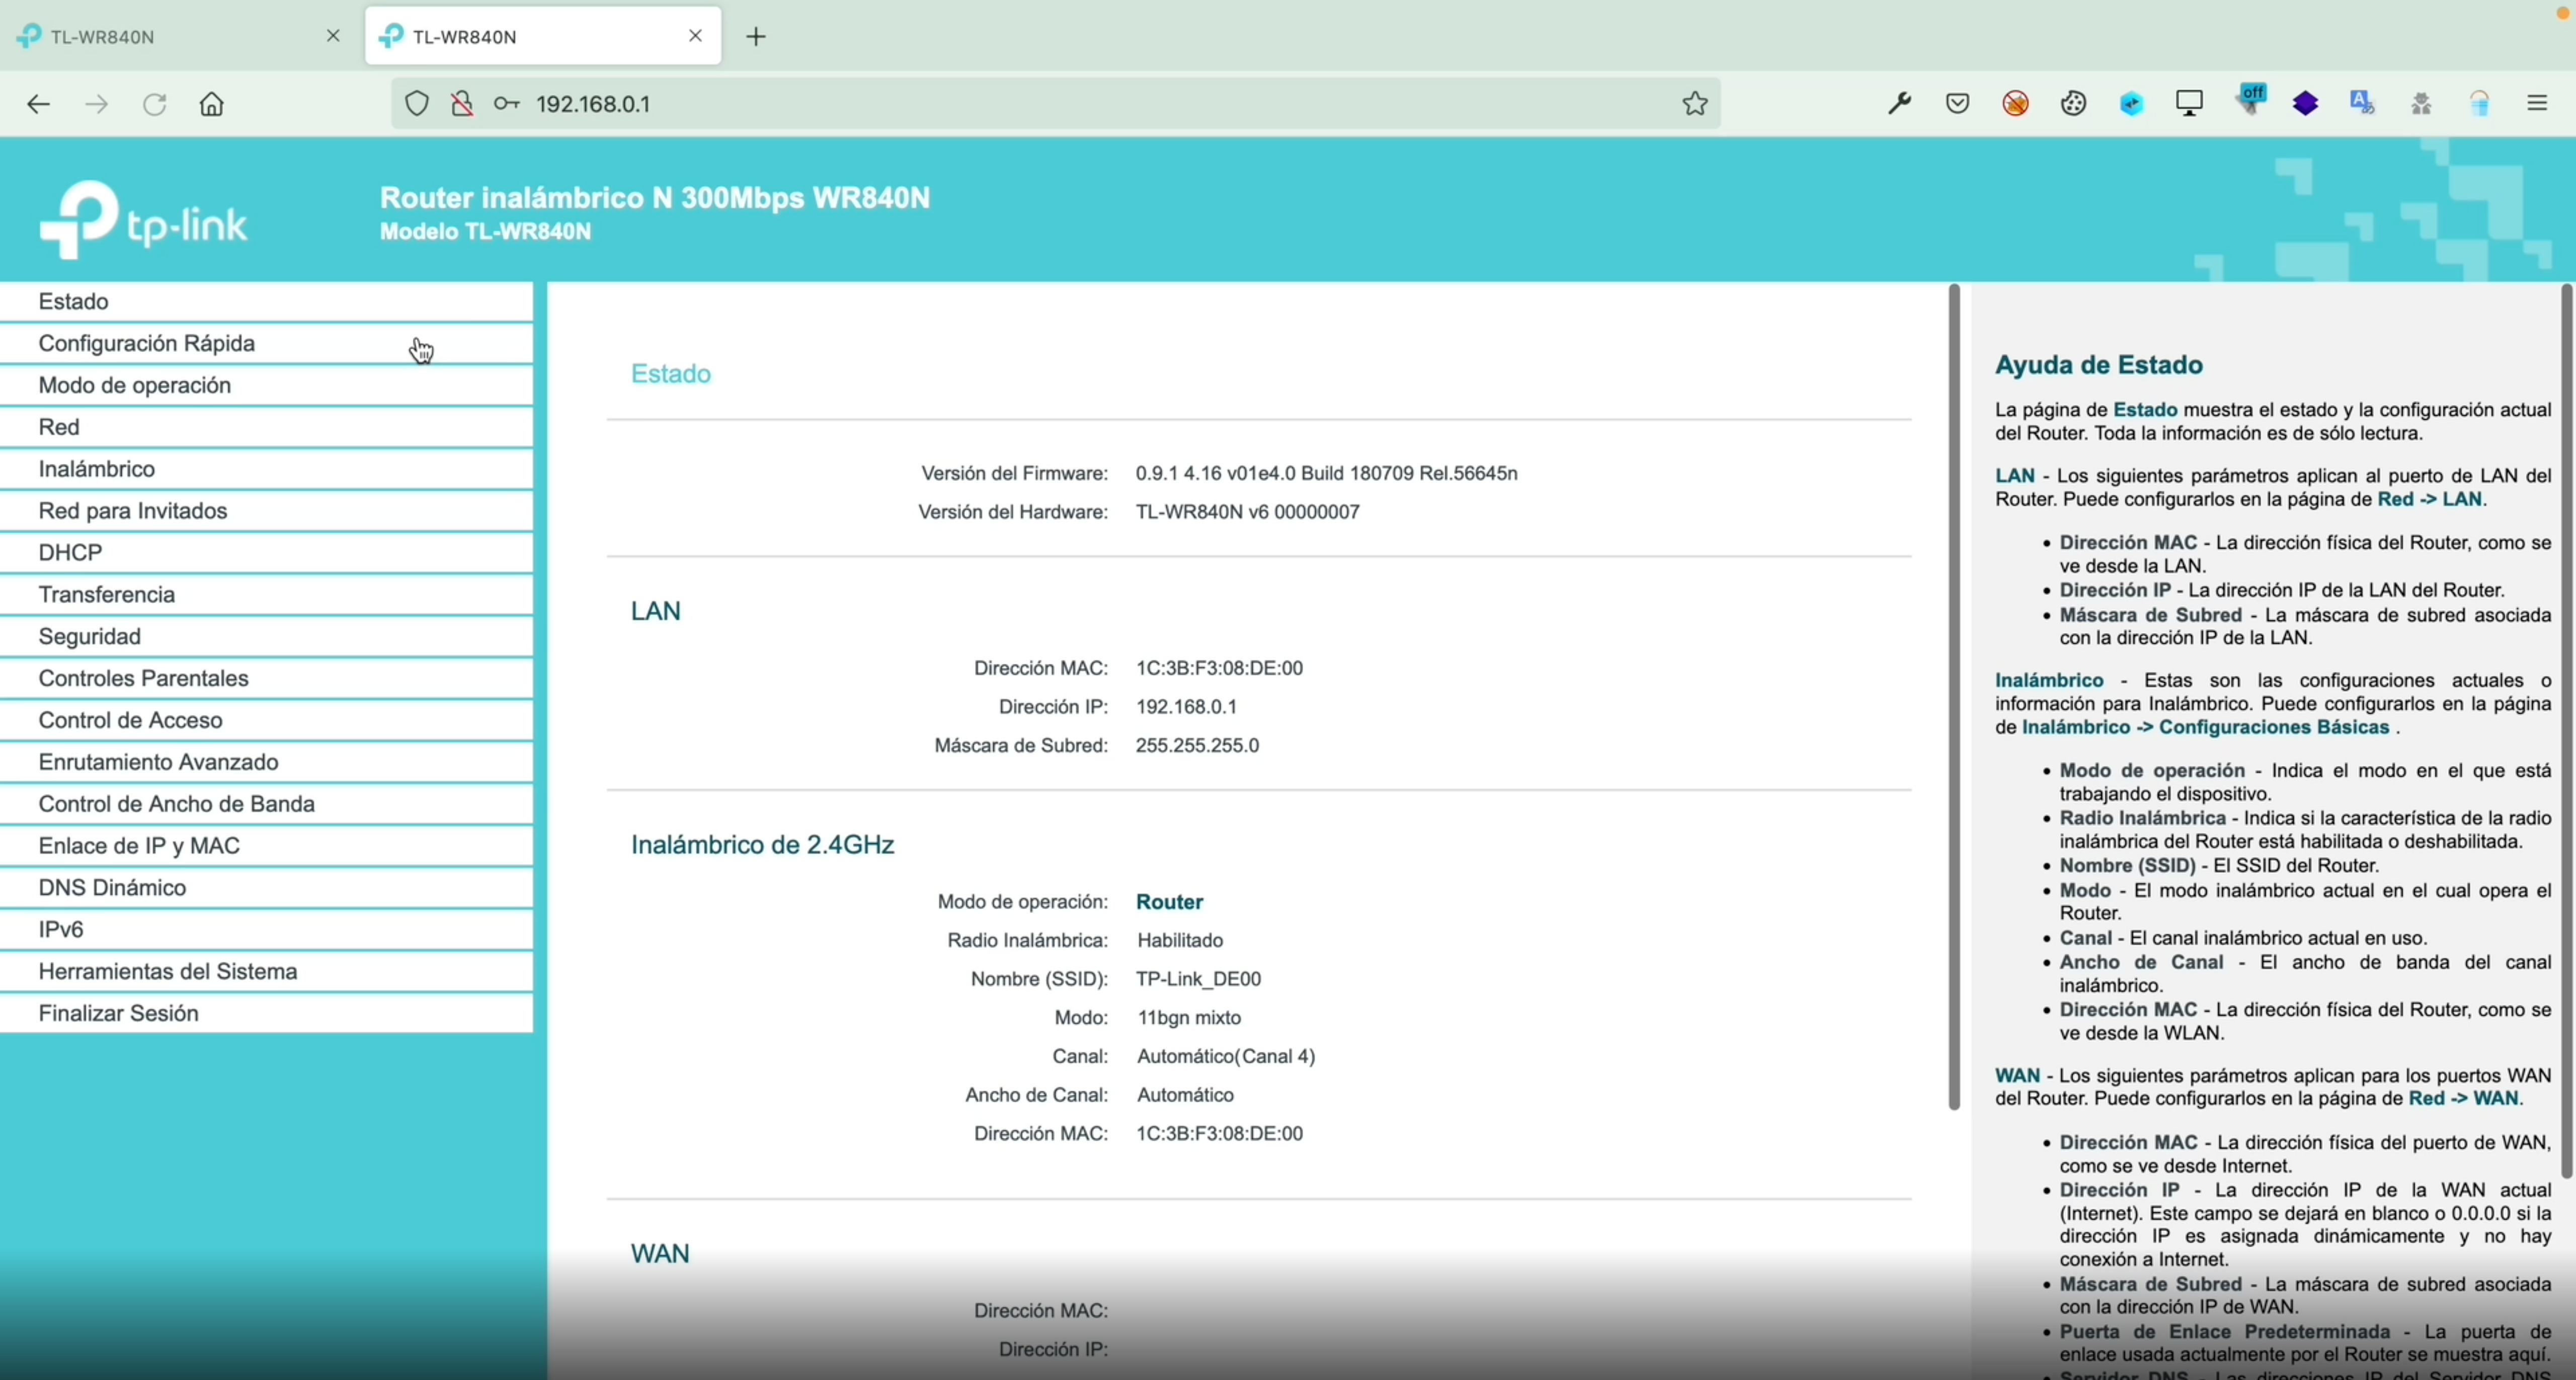 mr-xn/cve-2022-25064
Python exploit for TP-Link TL-WR840N RCE (CVE-2022-25064) via crafted IPv6 address payload in the router's CGI interface, enabling remote command…
 90n45-d3v/bluebunny
BLE-based C2 server for Hak5 Bash Bunny enabling wireless command injection, payload delivery, and remote control over Bluetooth Low Energy.
 thewhiteh4t/cve-2020-9375
TP-Link Archer C50 V3 devices before Build 200318 Rel. 62209 allows remote attackers to cause a denial of service via a crafted HTTP Header…
 otsmane-ahmed/cve-2025-29384-poc
Proof-of-concept exploit for CVE-2025-29384, a critical stack-based buffer overflow in Tenda AC9 routers. Includes Python and Metasploit modules for…
 9lyph/cve-2022-43704
Sinilink XY-WFTX Wifi Remote Thermostat Module Temperature Controller
 lakwsh/cve-2020-8597
Exploit for CVE-2020-8597 targeting RM2100 routers, providing proof-of-concept code for remote code execution via buffer overflow in the router's web…
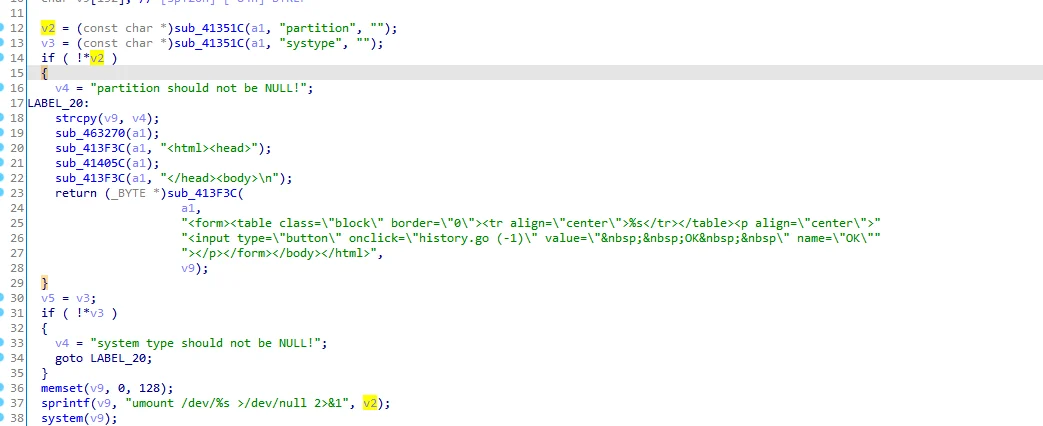 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 full-disclosure/cve-2021-44827
Proof-of-concept exploit for authenticated remote code execution (CVE-2021-44827) targeting TP-Link Archer C20i routers. Provides post-exploitation…
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…
 symbolexe/cve-2024-1642470
CVE-2024-1642470 is a critical vulnerability discovered in the Windows USB Generic Parent Driver. The vulnerability arises due to improper input…
 danish1162/cve-2026-2035703-x300
Tozed ZLT X300 5G CPE — Remote Root Code Execution via SDR Rogue Base Station (CVE-2026-2035703, CWE-78, CVSS 9.8) — Coordinated Disclosure
 sermikr0/cve-2026-38422
CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)
 rhestcorp/tp-l-nk-sizma-explo-t
TP-Link Router Authenticated RCE Exploit (CVE-2022-30075) Bu araç, TP-Link Archer AX50 ve bazı diğer TP-Link router modellerinde bulunan…
 jet-pentest/cve-2020-25749
Proof-of-concept exploit for CVE-2020-25749 targeting Rubetek cameras with hardcoded Telnet credentials, enabling remote root shell access and full…