
UniPwn
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
bluetooth-securityexploitationexploit-frameworks+4
417
bin4ry/unipwnBLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
 lyrebirds/sagemcom-fast-3890-exploit
Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…
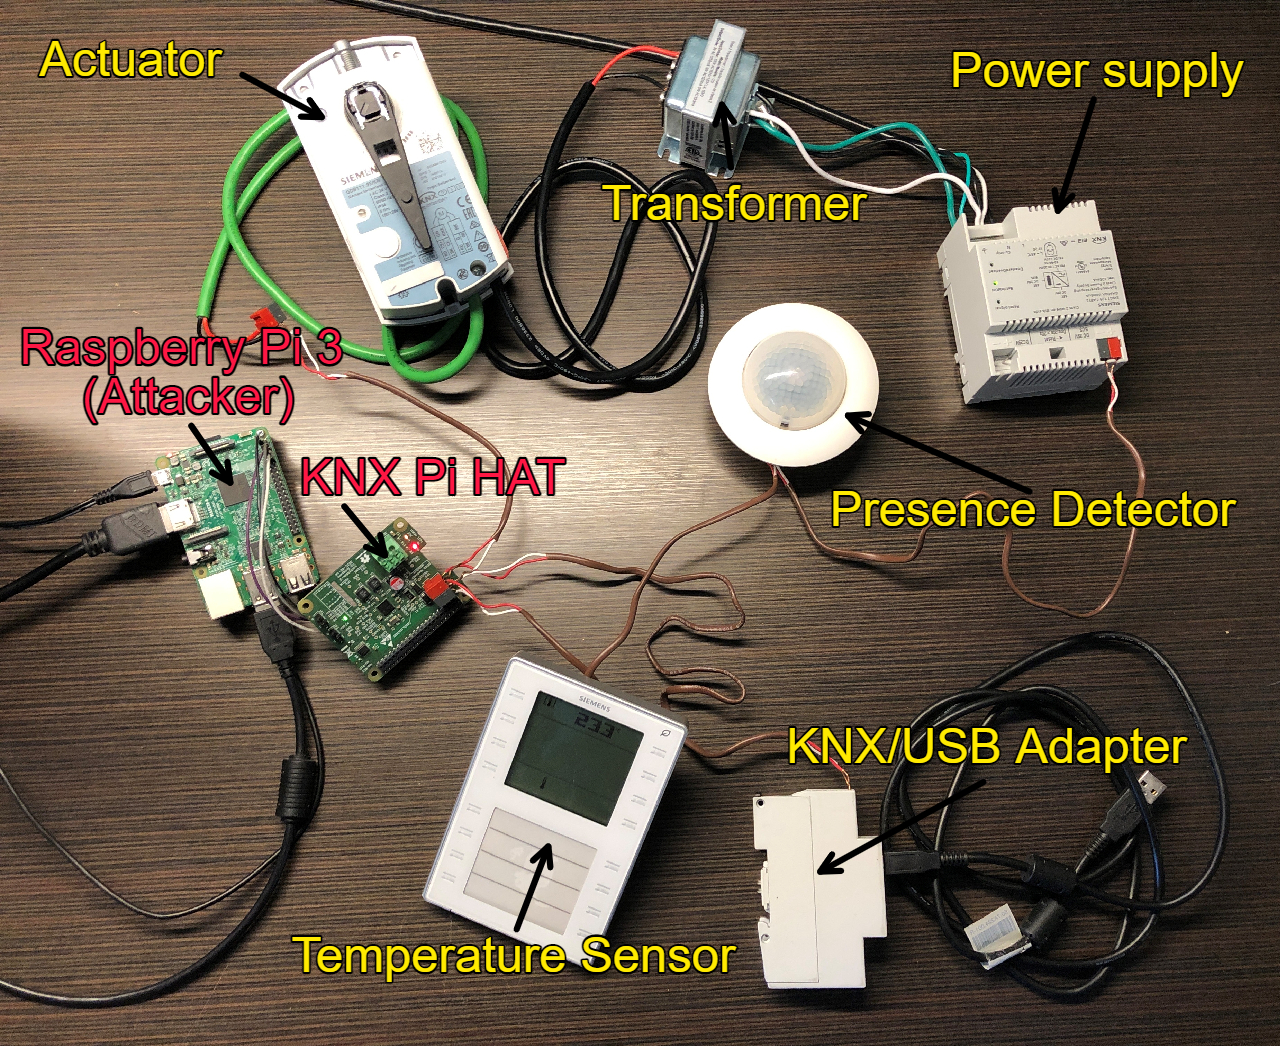 chrism09/knx-bus-dump
A tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…
 joelczk/cve-2025-52688
Proof-of-concept exploits for CVE-2025-52688: unauthenticated command injection and arbitrary file read vulnerabilities in Alcatel AP13161 enterprise…
 steveakawlabs/marmalade-2-cve-2025-67780-exploit
Exploit PoCs for MARMALDE 2 (CVE-2025-67780) vulnerability in Starlink Dishes
 laskdjlaskdj12/cve-2024-35106-poc
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 scriptingxss/iotgoat
IoTGoat is a deliberately insecure firmware based on OpenWrt.
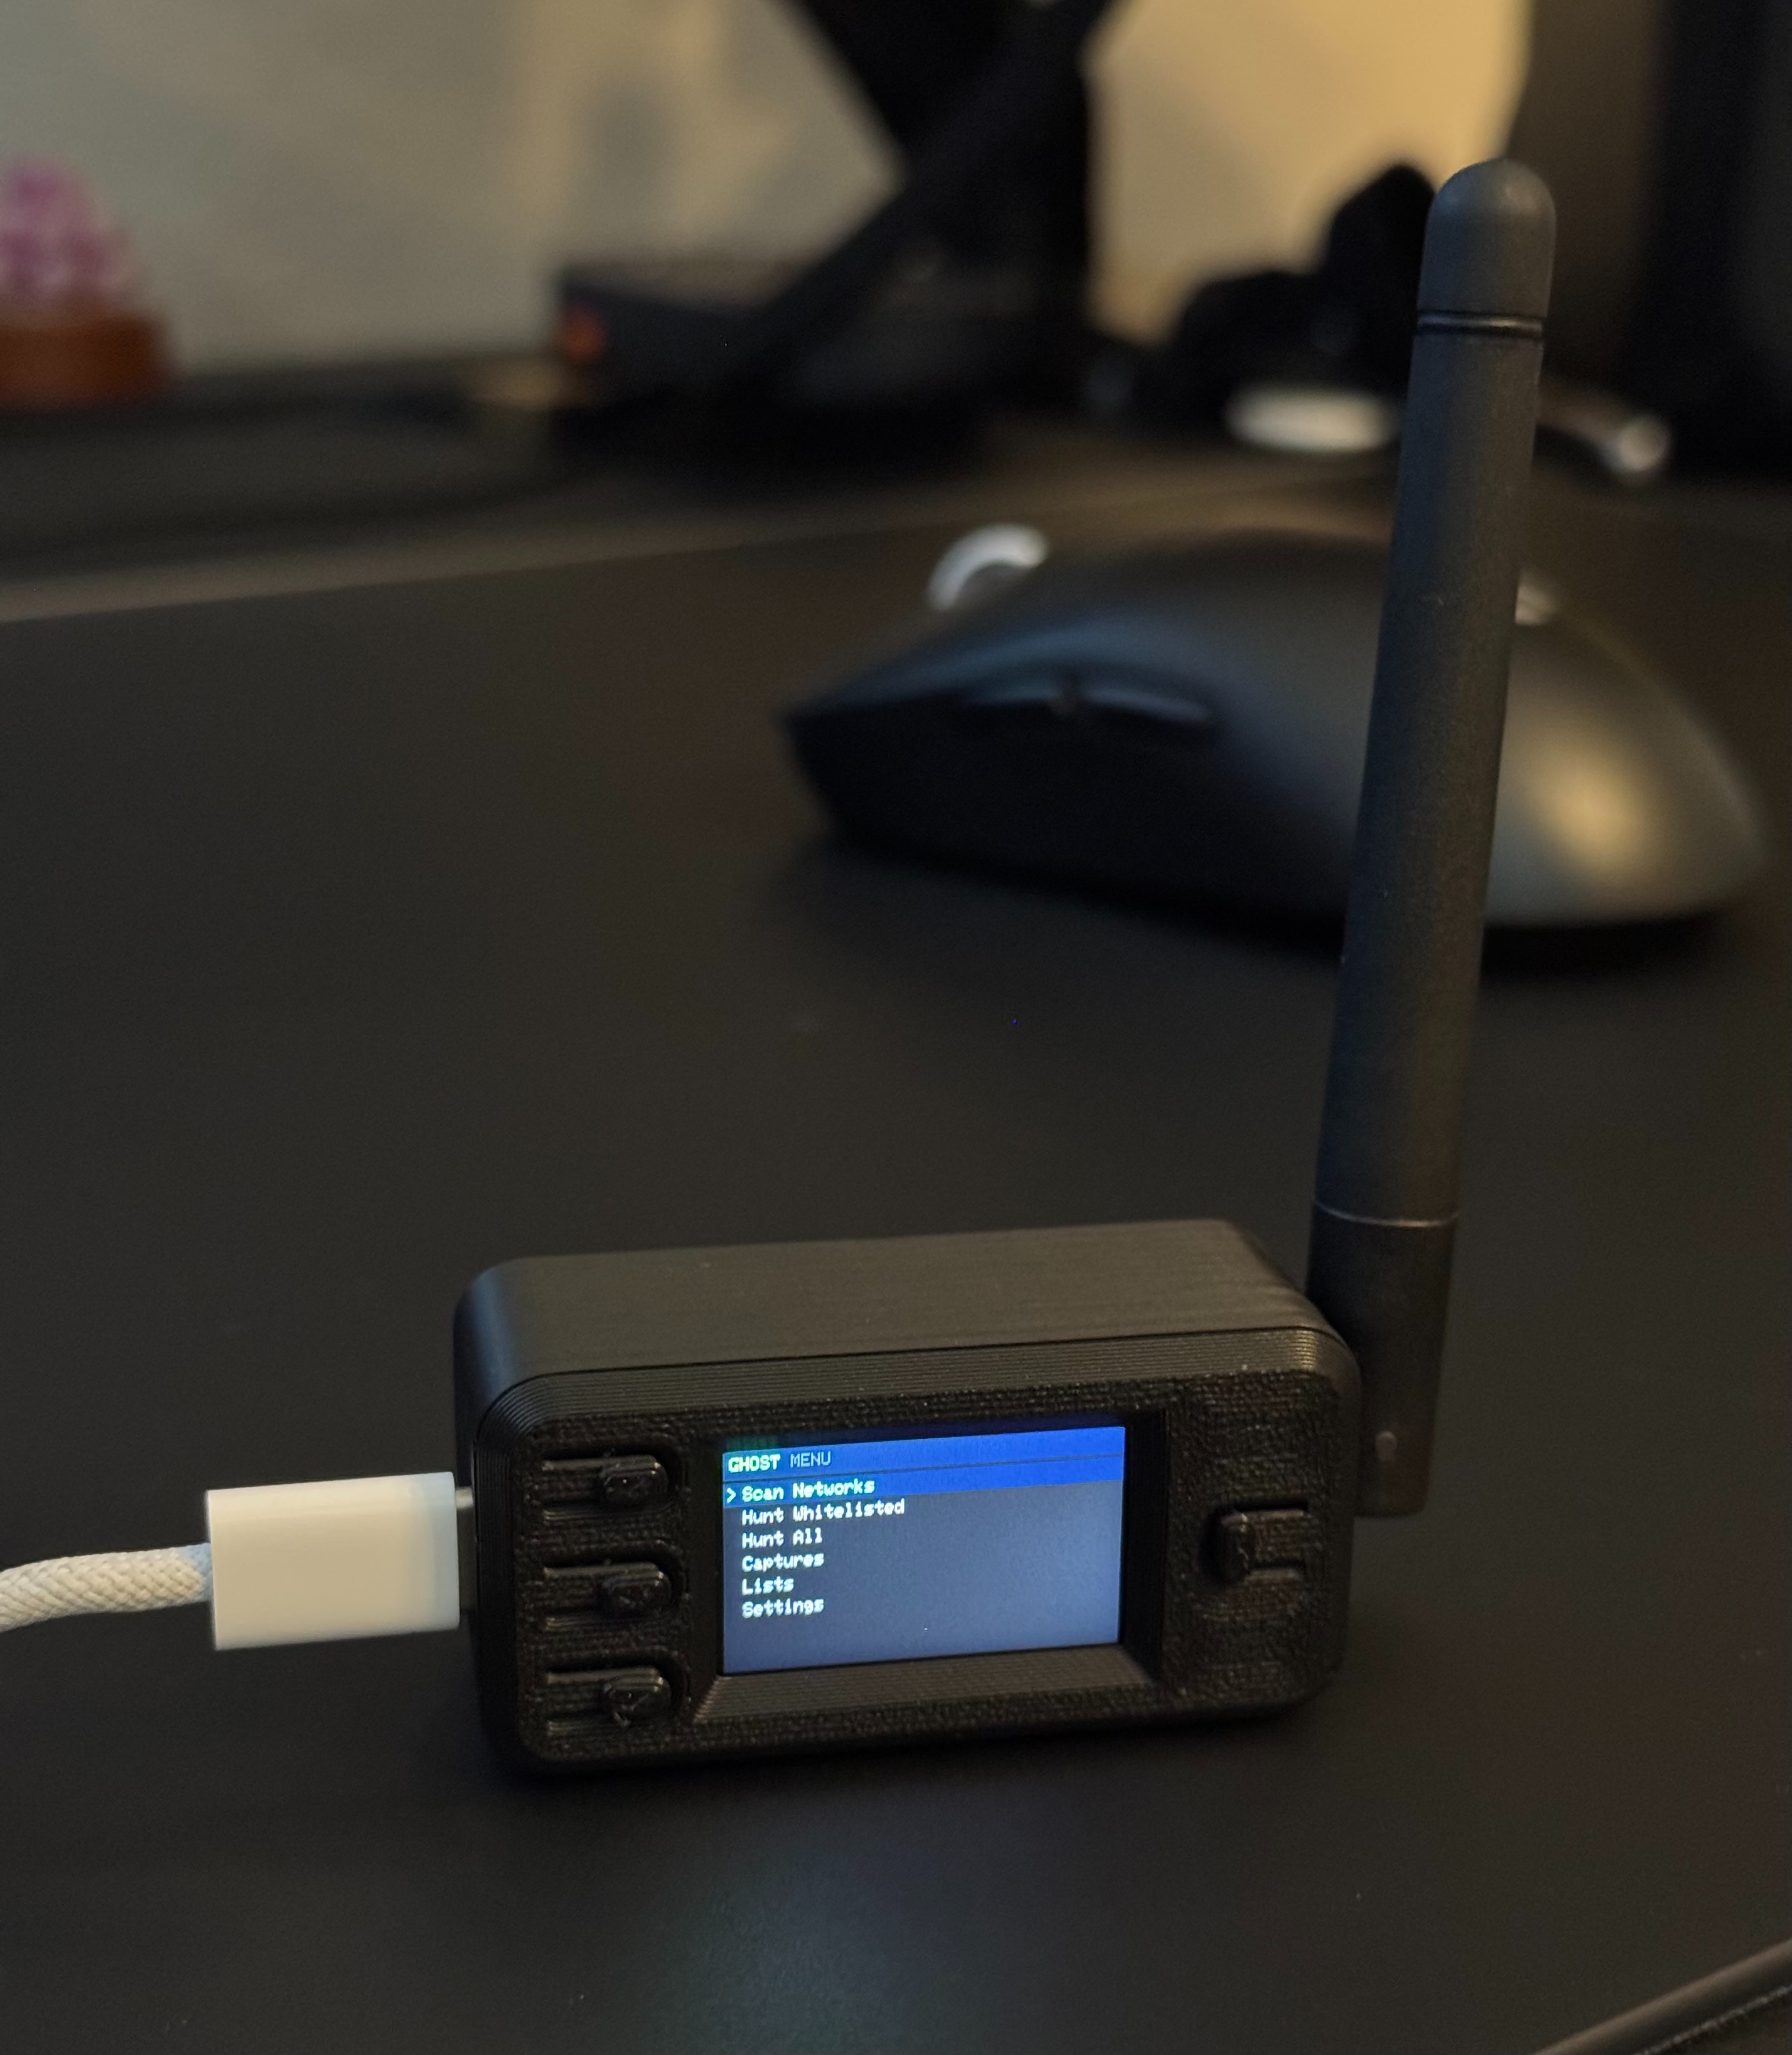 razkom/ghost
ESP32-S3 firmware for standalone WPA/WPA2 handshake capture and deauthentication testing via TFT UI, with pcap download over WiFi AP.
 themalwareguardian/cve-2021-27289
CVE-2021-27289: Playback Protection Bypass on Ksix Zigbee devices
 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
 rfidresearchgroup/chameleonultra
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…
 luispl77/433screen-signalhacker
Full duplex 433 MHz Signal jammer, recorder, decoder and hacking multitool device based on ESP32 microcontroller and RFM69HW radios. This version of…
 qkaiser/awind-research
This repository holds interesting bits and pieces related to research I performed on wireless presentation devices manufactured by Awindinc and…
 zhubaohe123/ghostlock-kit
One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.
 k-o-n-t-o-r/ghostlock-sabrina
CVE-2026-43499 GhostLock root exploit for Chromecast with Google TV (sabrina)
 ggfuchsi-oss/lg-webos-kexec
Boots a custom Linux kernel on rooted LG webOS TVs via kexec, with reverse-engineered SoC watchdog support, framebuffer payloads, and an initramfs…