
CVE-2023-33669
 dhammerg/cve-2023-33669
Stack overflow exploit for Tenda AC8 router (CVE-2023-33669) targeting firmware US_AC8V4.0si_V16.03.34.06 with emulation and RCE via TFTP.
binary-exploitationeducationembedded-systems-security+3
2
dhammerg/cve-2023-33669Stack overflow exploit for Tenda AC8 router (CVE-2023-33669) targeting firmware US_AC8V4.0si_V16.03.34.06 with emulation and RCE via TFTP.
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 dorskfr/tapodate
Sets up a local Tapo C200 using CVE-2021-4045
 miapatsune/cve-2026-43499
Kernel exploit for Redmi Pad Pro (dizi) / POCO Pad 5G with browser-based upload and execution interface, admin panel for log management, and…
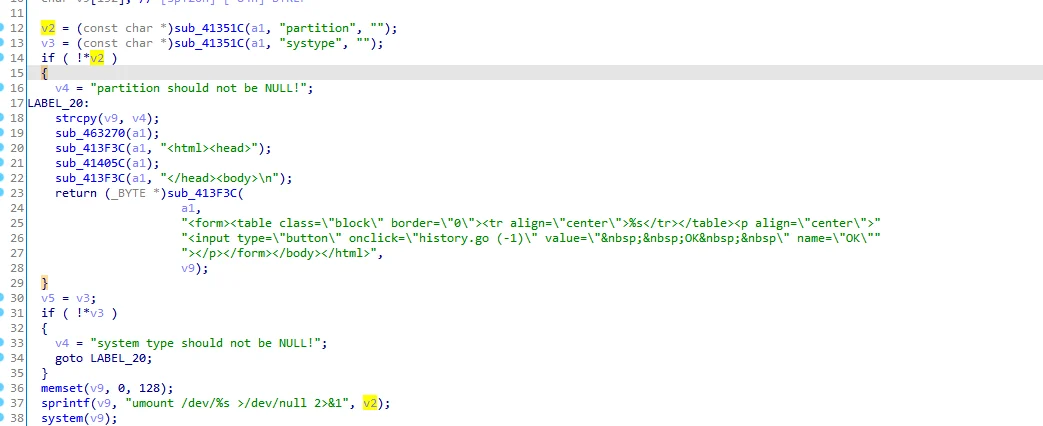 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 harryanon/poc-cve-2018-4327-and-cve-2018-4330
Proof-of-concept exploit for iOS Bluetooth stack vulnerabilities CVE-2018-4327 and CVE-2018-4330, enabling ARM PC register control on iPhone 6S via…
 spiralbl0ck/sigint_through_brother_printers
Exploit vulnerable Brother printers via CVE-2017-7588, collect data, and develop custom firmware implants for attack simulation.
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
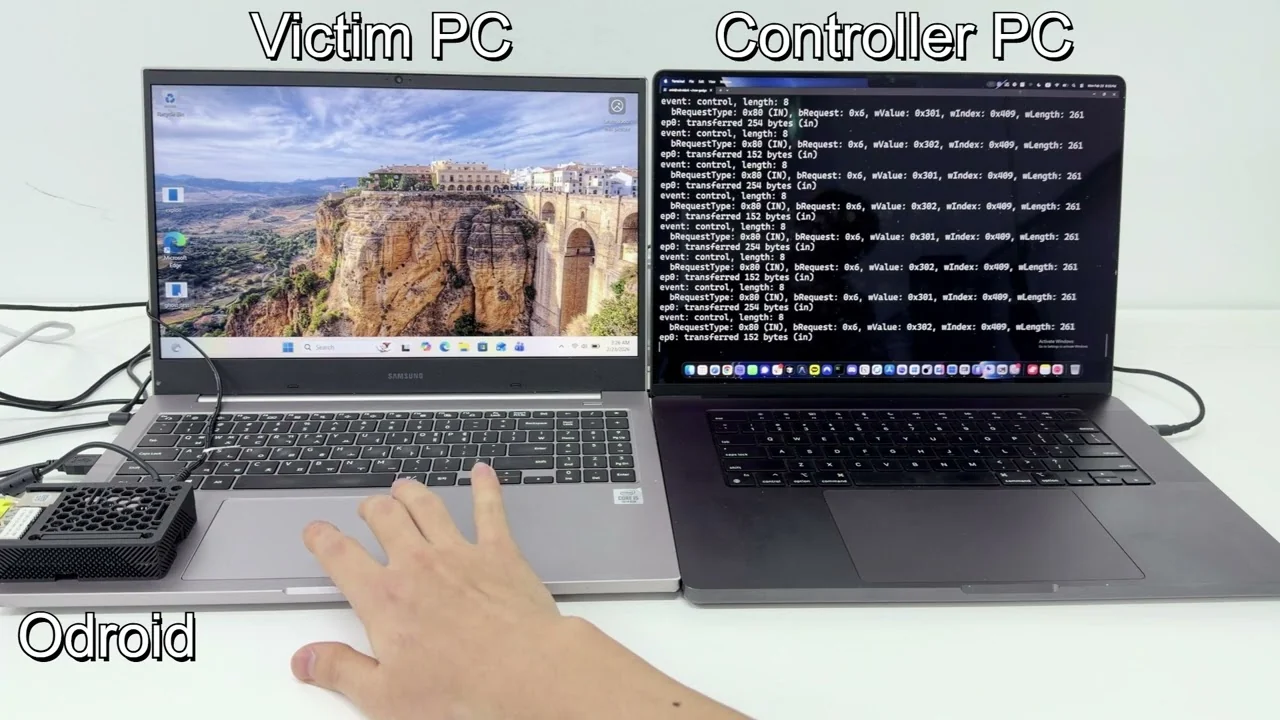 enki-kr/cve-2026-32223-usbprint-exploit
Proof-of-concept exploit for CVE-2026-32223, a heap-based buffer overflow in Windows USB print driver (usbprint.sys), achieving local privilege…
 otsmane-ahmed/cve-2025-29384-poc
Proof-of-concept exploit for CVE-2025-29384, a critical stack-based buffer overflow in Tenda AC9 routers. Includes Python and Metasploit modules for…
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
 mattgsys/cve-2026-0834
Proof-of-concept exploit for TP-Link TDDP authentication bypass (CVE-2026-0834) that sends crafted packets to execute administrative commands like…
 s0tr/cve-2023-33781
Proof-of-concept exploit for CVE-2023-33781 enabling arbitrary binary execution on D-Link DIR-842V2 routers via telnet and backup/restore…
 azhariramadhan/cve-2025-45512
Proof-of-concept exploit suite for U-Boot bootloader vulnerabilities, including insecure update mechanisms, hardcoded credentials, debugging…
 george0papasotiriou/cve-2026-21006-zigbee-light-link-factory-reset-exploit
Simulated Zigbee Light Link (ZLL) factory reset exploit for CVE-2026-21006, demonstrating unauthenticated TouchLink command injection that wipes…
 mbanyamer/px4-military-uav-autopilot-1.12.3-stack-buffer-overflow-exploit-cve-2025-5640-
Proof-of-concept exploit for CVE-2025-5640, a stack buffer overflow in PX4 Military UAV Autopilot <=1.12.3. Sends crafted MAVLink packets to trigger…
 vidura2/cve-2024-46451
Python exploit for TOTOLINK AC1200 T8 buffer overflow vulnerability (CVE-2024-46451) with customizable payload generation and response logging for…