
CVE-2025-1242
 michaeladamgroberman/cve-2025-1242
CVE-2025-1242: Hardcoded iothubowner Connection String — Gardyn Home Kit (ICSA-26-055-03)
authenticationcloud-securityfirmware-analysis+4
michaeladamgroberman/cve-2025-1242CVE-2025-1242: Hardcoded iothubowner Connection String — Gardyn Home Kit (ICSA-26-055-03)
 the-girl-who-lived/cve-2020-11539
Improper Access Control in Tata Sonata Smartband
 fr0stm0urne/cve-2023-33768
DoS against Belkin smart plugs via crafted firmware injection
 dorskfr/tapodate
Sets up a local Tapo C200 using CVE-2021-4045
 acen28/cve-2026-26399-disclosure
Disclosure of a stack-based use-after-return vulnerability in Arduino_Core_STM32, detailing technical root cause, affected versions, and fix, with…
 remenis/cve-2025-63667
Vatilon-based IP camera firmwares issue Session-Id tokens without verifying credentials, allowing attackers to obtain sessions and retrieve plaintext…
 rhestcorp/tp-l-nk-sizma-explo-t
TP-Link Router Authenticated RCE Exploit (CVE-2022-30075) Bu araç, TP-Link Archer AX50 ve bazı diğer TP-Link router modellerinde bulunan…
 nomis/eero-zero-length-ipv6-options-header-dos
eeroOS Ethernet Interface Denial of Service Vulnerability (CVE-2023-5324)
 edwins907/-cve-2024-45352
Technical report about a critical vulnerability in Xiaomi (CVE-2024-45352)
 0xqrx/cve-2024-6333
Authenticated Remote Code Execution vulnerability in Xerox WorkCentre printers via the Network Troubleshooting Log feature.
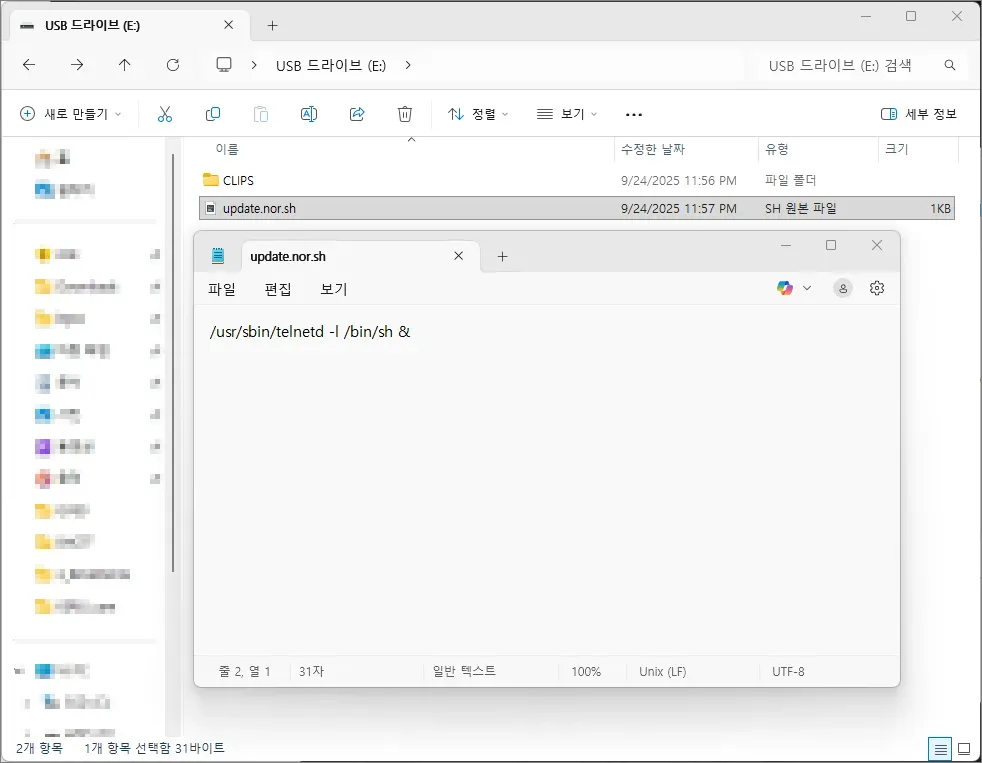 t4e-3/cve-2025-63296
KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability
 yoshida-git-ai/spacex-starlink-router-gen-2-xss
CVE-2023-49965 | SpaceX / Starlink Router Gen 2 XSS
 nastycrow/cve-2025-51643
Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…
 zgsnj123/cve-2025-45466
It is the details of CVE-2025-45466
 xernary/cve-2025-63820
Proof-of-concept of vulnerability found in Totolink A720R router
 cipherx1802/cve-2025-69822-atomberg_erica_smatfan_security_assessment
This vulnerability impacts device availability and reliable operation of Atomberg Erica Smart Fan(Firmware Version 1.0.36). The issue arises due to a…
 cipherx1802/cve-2025-69821-beat-xp-vega-smartwatch-security-assessment
A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…