Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
436 results
tesla-security-research preview

tesla-security-research

GitHubanalyticeth/tesla-security-research

Vulnerability research on Tesla Model 3/Y infotainment systems. 6 vulnerabilities, 4 CVEs (CVE-2022-42005 through CVE-2022-42008). Root shell,…

command-and-controldata-exfiltrationeducation+7
6
4 months ago
CVE-2018-16706 preview

CVE-2018-16706

GitHubnurdilin/cve-2018-16706

Or how I turn off my TV via a cronjob

exploitationhardware-iot-securityiot-security+3
67 years ago
CVE-2026-63563 preview

CVE-2026-63563

GitHubredr0nin/cve-2026-63563

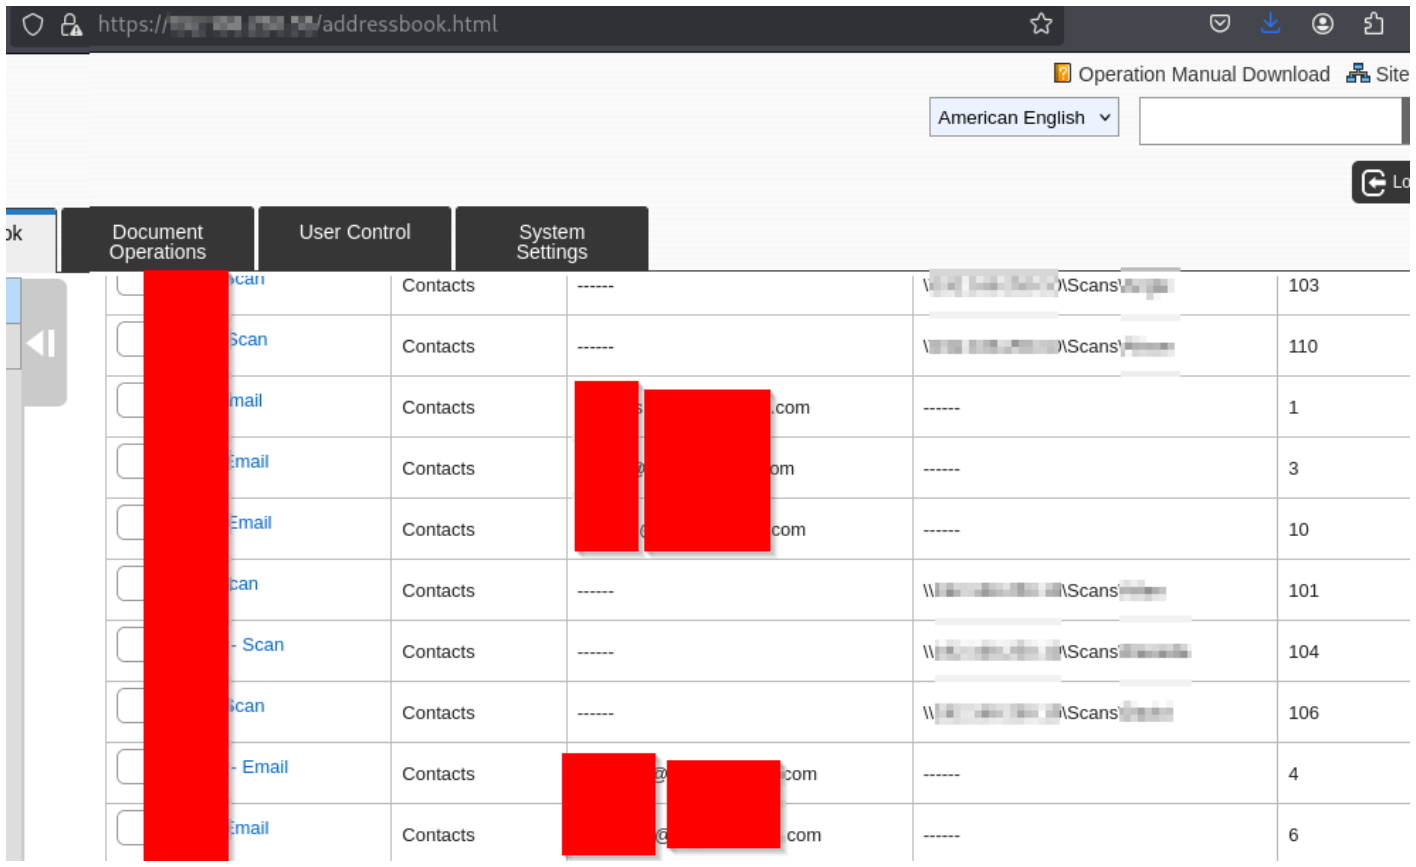
Unauthenticated Address Book Modification on Sharp MX/BP Multifunction Printers

data-exfiltrationexploitationhardware-iot-security+3
21 month ago
CVE-2025-65857 preview

CVE-2025-65857

GitHubluismirandaacebedo/cve-2025-65857

Xiongmai XM530 IP Camera Hardcoded RTSP Credentials Exposure

embedded-systems-securityexploitationhardware-iot-security+3
59 months ago
ESPTouchCatcher preview

ESPTouchCatcher

GitHubsalgio/esptouchcatcher

eWeLinkESPT is a tool that automatically decodes and decrypts the WiFi network credentials transmitted to a supported ESP-based IoT device by the…

cryptographyexploitationhardware-iot-security+4
55 years ago
CVE-2026-95675 preview

CVE-2026-95675

GitHubd6fault/cve-2026-95675

Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…

embedded-systems-securityexploitationfirmware-analysis+6
117 days ago
CVE-2026-77812 preview

CVE-2026-77812

GitHubwh02m1/cve-2026-77812

Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…

bluetooth-securityexploitationhardware-iot-security+4
118 days ago
CVE-2024-24488 preview

CVE-2024-24488

GitHublegacyobj/cve-2024-24488

An issue in Shenzen Tenda Technology CP3V2.0 V11.10.00.2311090948 allows a local attacker to obtain sensitive information via the password component.

embedded-systems-securityexploitationhardware-iot-security+3
52 years ago
CVE-2022-26269 preview

CVE-2022-26269

GitHubnsbogam/cve-2022-26269

Suzuki connect app is used to get the car information like Fuel, Ignition status, Current location, Seat buckle status etc. In Ignis, Zeta variant…

embedded-systems-securityexploitationfuzzing+2
24 years ago
CVE-2026-51585 preview

CVE-2026-51585

GitHubcatforgor/cve-2026-51585

rt26cx21x64.sys exploit (Realtek PCIe GbE/2.5GbE/5GbE family)

binary-exploitationexploitationhardware-iot-security+2
35 months ago
WebcamViewer preview

WebcamViewer

GitHubosy/webcamviewer

Proof-of-concept demonstrating CVE-2021-30731, allowing unauthorized USB webcam access on macOS. Built with libuvc, it previews connected webcams on…

exploitationhardware-iot-securitypenetration-testing+2
54 years ago
CVE-2026-1122-IoT-Firmware-Update-Signature-Bypass-via-Low-Order-Point-Injection preview

CVE-2026-1122-IoT-Firmware-Update-Signature-Bypass-via-Low-Order-Point-Injection

GitHubgeorge0papasotiriou/cve-2026-1122-iot-firmware-update-signature-bypass-via-low-order-point-injection

Demonstrates CVE-2026-1122 Ed25519 signature bypass via low-order point injection, forging malicious IoT firmware updates with Python and C verifier…

cryptographyembedded-systems-securityexploitation+4
2 months ago
CVE-2026-22017-Firmware-Update-via-BLE-Without-Authentication preview

CVE-2026-22017-Firmware-Update-via-BLE-Without-Authentication

GitHubgeorge0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication

Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…

bluetooth-securityembedded-systems-securityexploitation+4
2 months ago
CVE-2025-70962 preview

CVE-2025-70962

GitHubnamaek2/cve-2025-70962

CVE-2025-70962 PoC

exploitationfirmware-analysishardware-iot-security+3
2 months ago
CVE-2025-15474 preview

CVE-2025-15474

GitHubnsm-barii/cve-2025-15474

A denial-of-service vulnerability in the AuntyFey BLE smart padlock allows unauthenticated connection floods to lock out legitimate users. …

bluetooth-securityeducationexploitation+4
49 months ago
CVE-2026-38577 preview

CVE-2026-38577

GitHubpoxsky/cve-2026-38577

Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…

embedded-systems-securityexploitationfirmware-analysis+5
1 month ago
CVE-2026-9254 preview

CVE-2026-9254

GitHubslagzz/cve-2026-9254

TP-Link Archer BE800 V1 — Parental Control LAN RCE

exploitationhardware-iot-securityiot-security+3
1 month ago
CVE-2026-9090-Modbus-TCP-Write-to-Read-Only-Coils-via-Function-Code-Spoofing preview

CVE-2026-9090-Modbus-TCP-Write-to-Read-Only-Coils-via-Function-Code-Spoofing

GitHubgeorge0papasotiriou/cve-2026-9090-modbus-tcp-write-to-read-only-coils-via-function-code-spoofing

PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.

exploitationhardware-iot-securitymisconfiguration+4
2 months ago
Previous1…202122…25Next