

pwndbg
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
ai-assisted-reversingbinary-analysisbinary-exploitation+12
pwndbg/pwndbgExploit Development and Reverse Engineering with GDB & LLDB Made Easy
 rfidresearchgroup/chameleonultra
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…

 mister-devel/main_mister
FPGA-based hardware emulation platform main binary and documentation for retro system development, firmware compilation, and hardware security…
 nmatt0/moria
IoT firmware identification and extraction
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 e-m-b-a/emba
EMBA - The firmware security analyzer
 faicalom/zte-mf904q-reverse-engineering
Open research documentation and source review for ZTE MF904Q bootloader, firmware extraction, and reverse engineering.
 yslxotwod/imsisting
GTK4 and CLI cellular security toolkit with 57 modules for 2G GSM, 3G UMTS, 4G LTE and 5G NR air interface, core network, SIM identity, RF tracking,…
 atao/raspberrypi-setup
Ansible playbook for rapid Raspberry Pi setup with modular roles for wireless security testing, RFID/NFC tools, SDR, Docker, Tor proxy, and standard…
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.

 c4psu13/mali-pagecache-root
TCL 50C721 (RTD1319 / Mali-G31) root toolkit — autonomous CVE-2022-22706 exploit chain
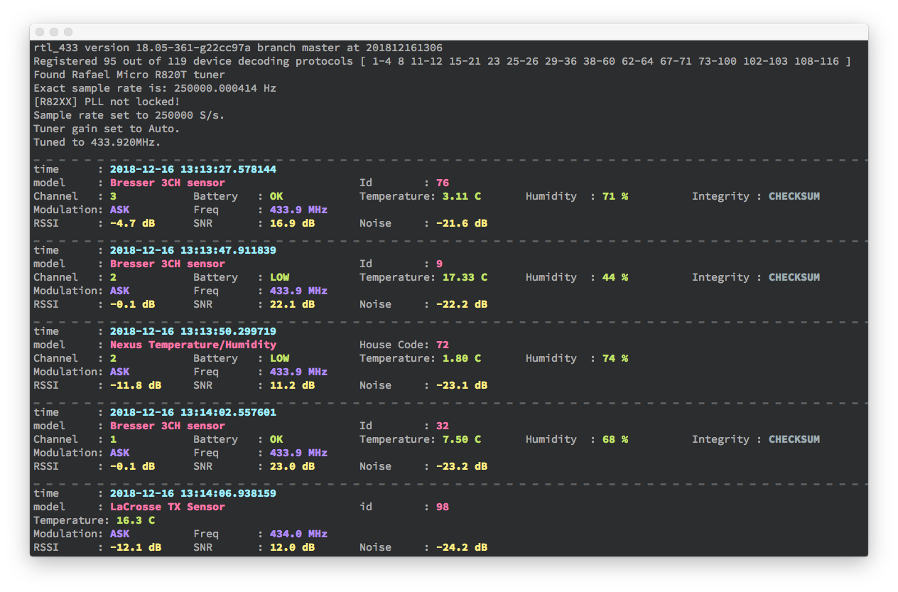 merbanan/rtl_433
Program to decode radio transmissions from devices on the ISM bands (and other frequencies)
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
 thebadinteger/p2pwn
Dahua cameras security scanner via P2P
 adamlaurie/rfidiot
Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…
 pepsipu/ns2jb
Console jailbreak demo that executes native functions inside the Switch 2 filesystem process via SmileBASIC, verifies results, and restores original…