
intercept
 smittix/intercept
iNTERCEPT, a free and open-source platform that unites the best signal intelligence tools into a single, accessible interface.
bluetooth-securityeducationembedded-systems-security+7
2.2k
smittix/interceptiNTERCEPT, a free and open-source platform that unites the best signal intelligence tools into a single, accessible interface.
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
 c8dhjp4tyv-bit/jbl-wave-buds2-firmware-research
Reverse-engineering notes and Python tooling for JBL Wave Buds 2 (BES1306) firmware: OTA container format, flash layout, BLE/GATT protocol, and…
 quarkslab/conf-presentations
Quarkslab conference talks
 whad-team/whad-client
Protocol client and CLI framework for interacting with wireless hacking devices, enabling security researchers to explore, test, and automate…
 yslxotwod/wifisting
GTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…
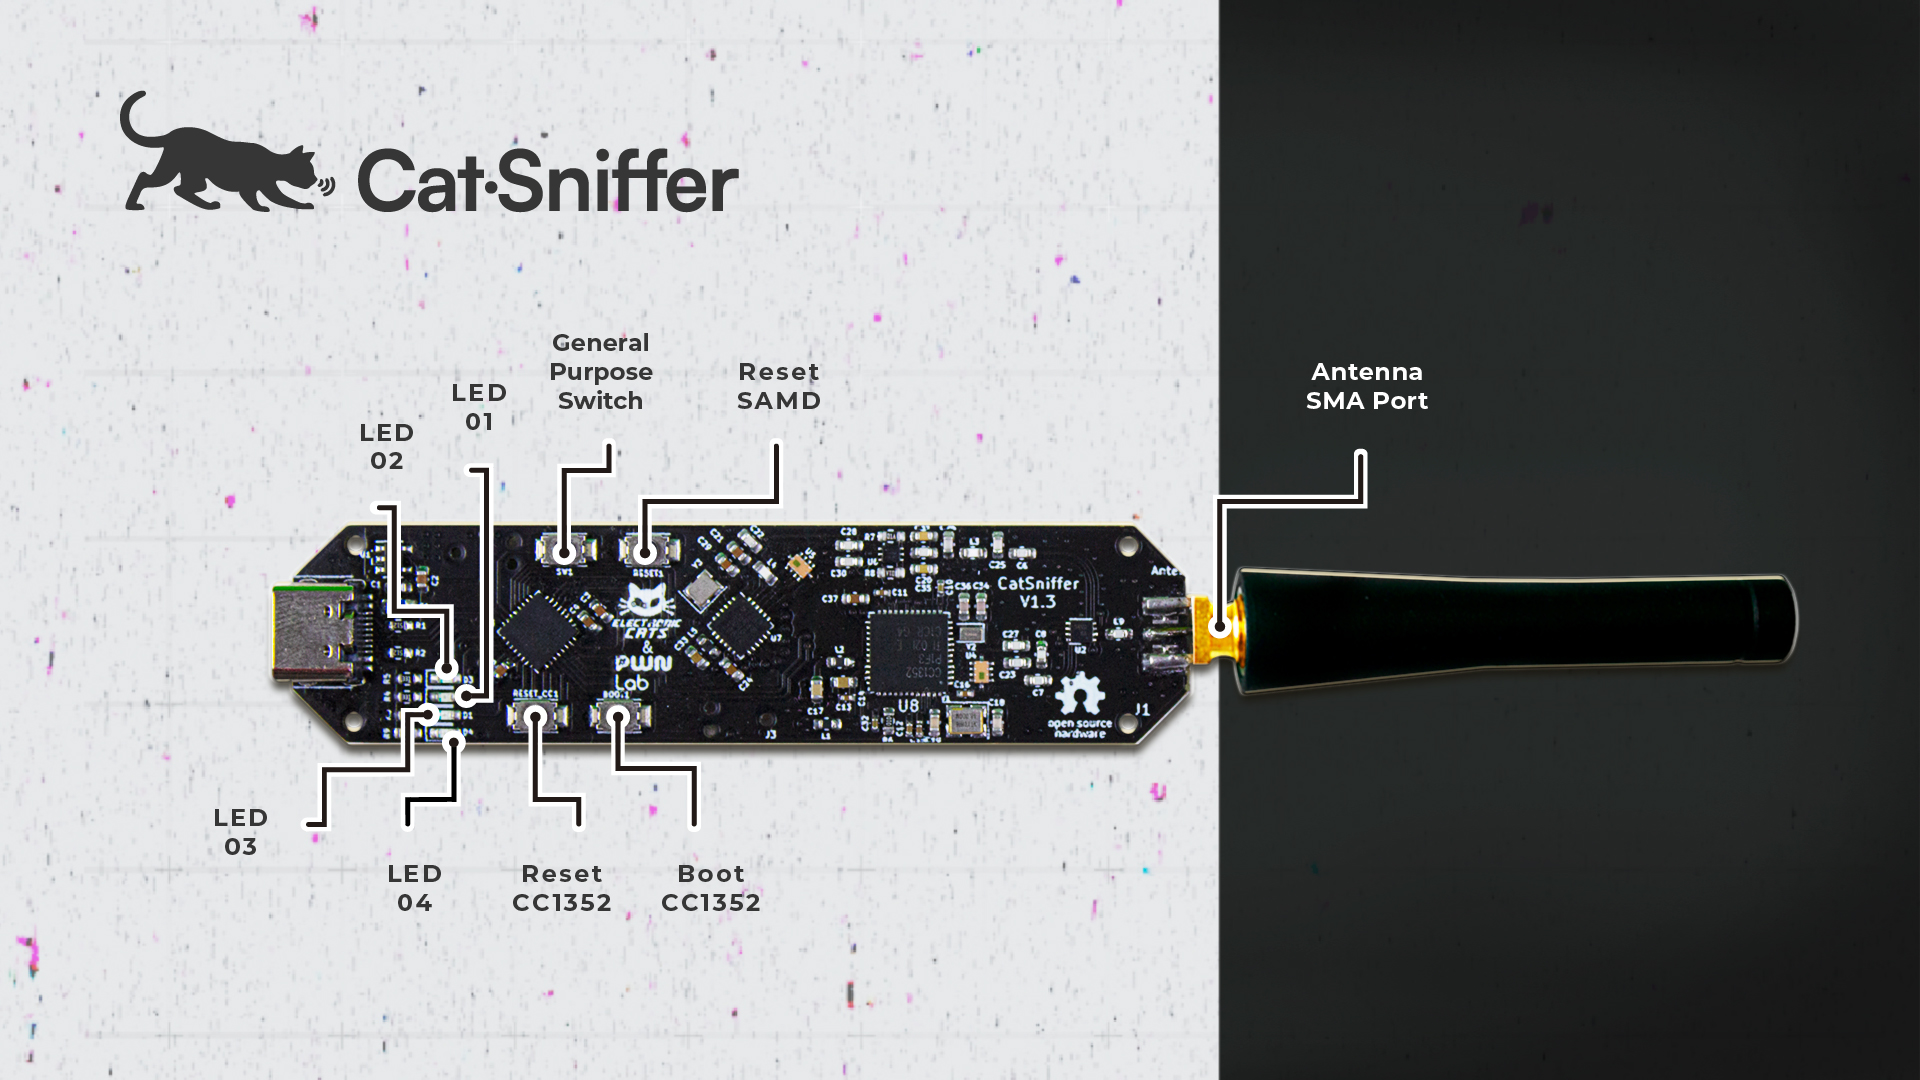 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 phantom-brigade1/wifisting
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…
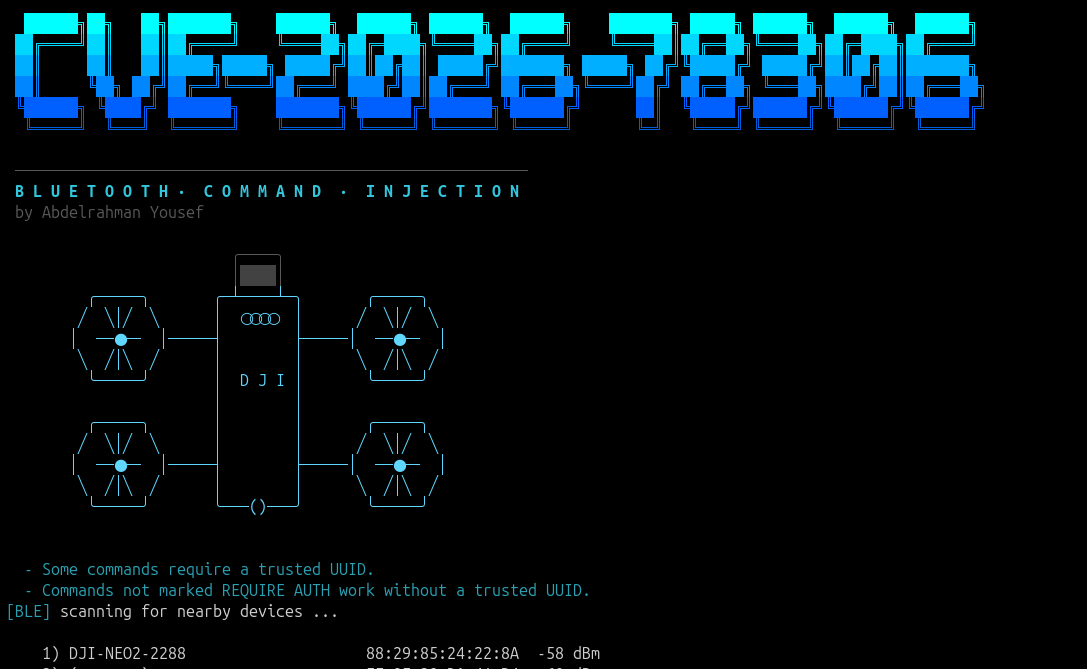 wh02m1/cve-2026-78306
Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…
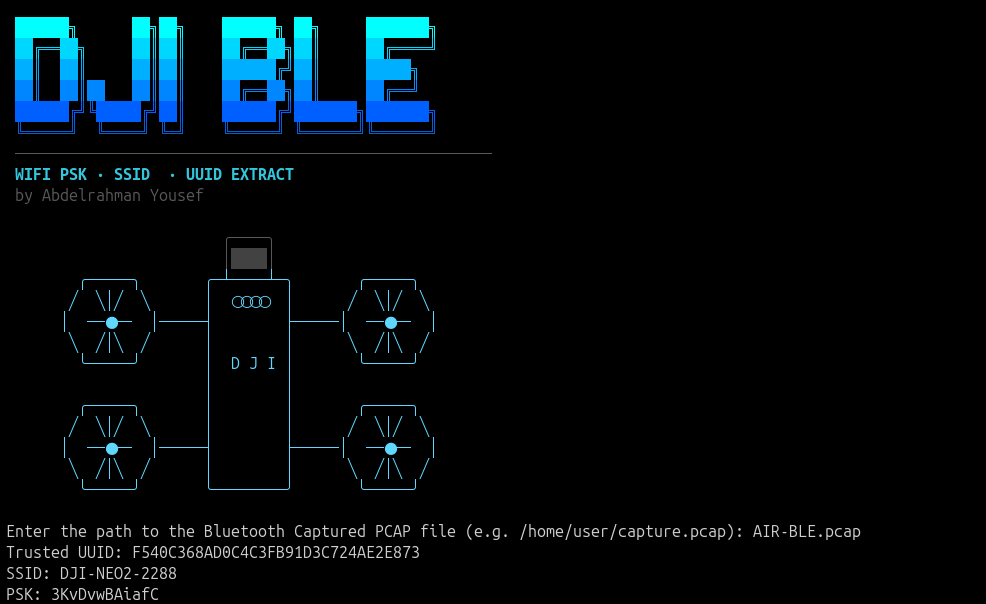 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
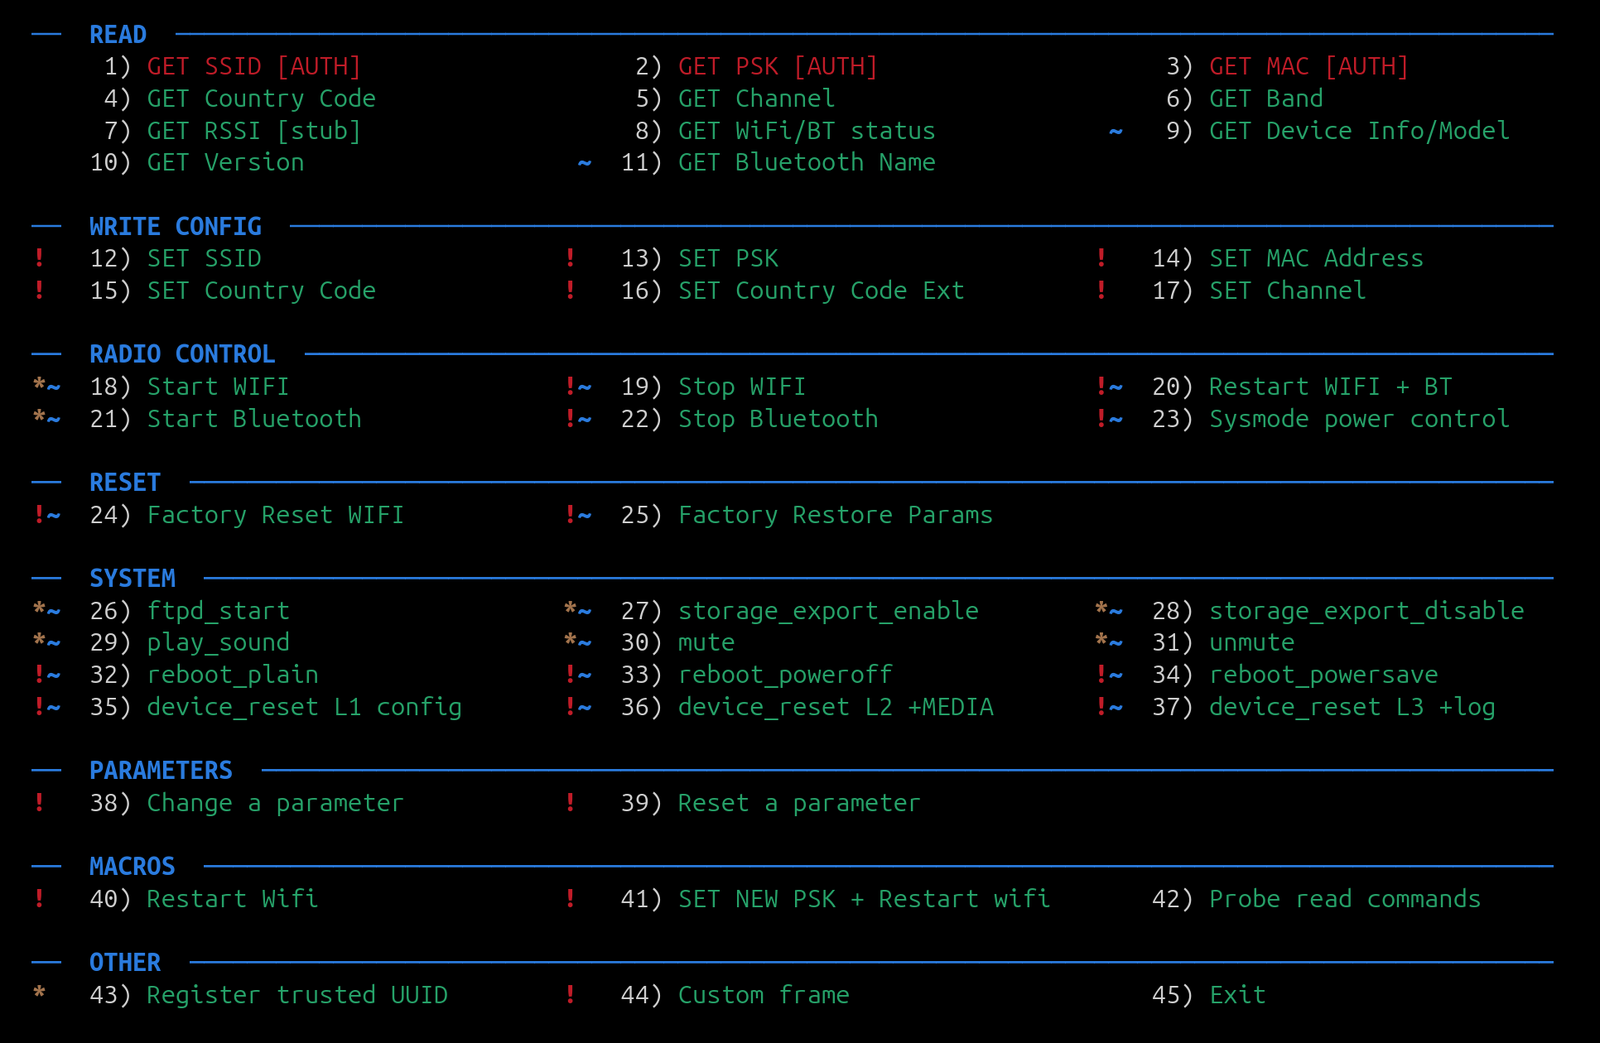 feedbeef/dji_ble_vuln
DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
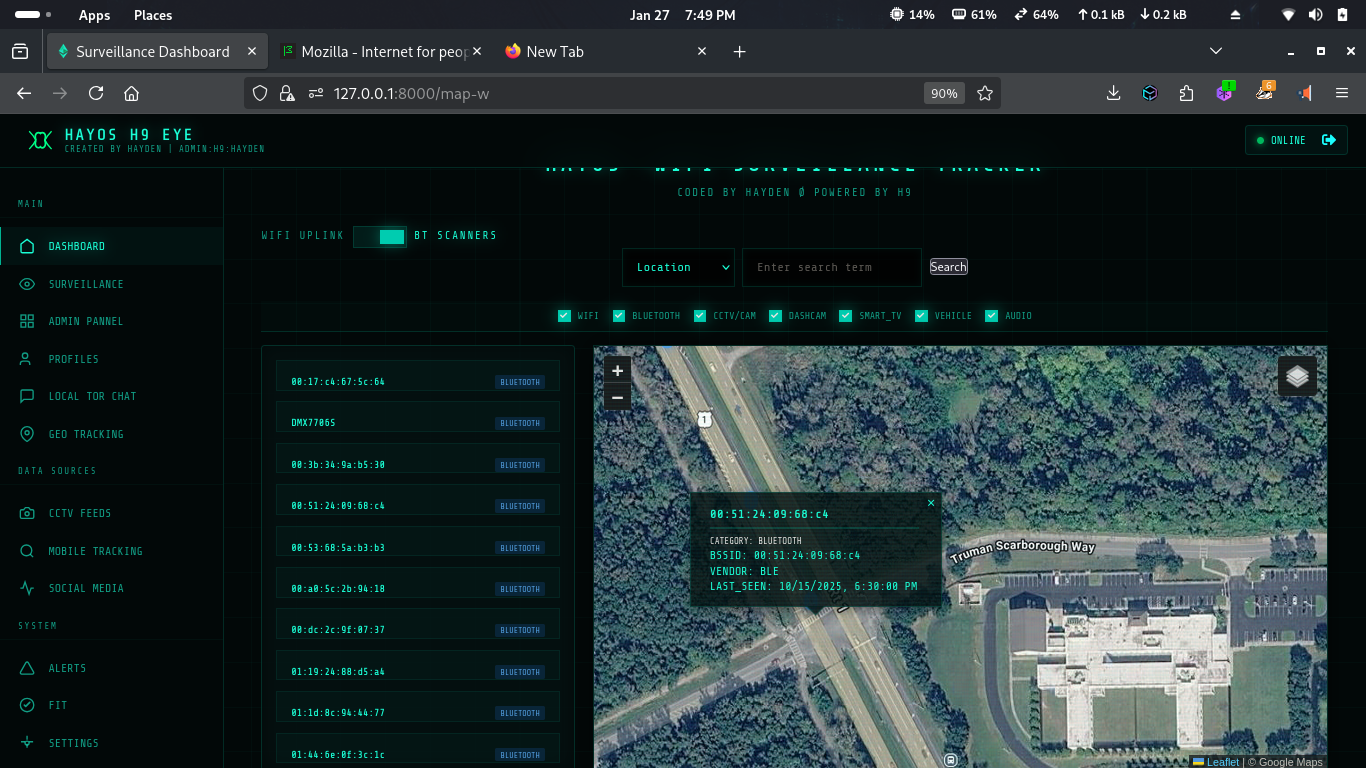 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
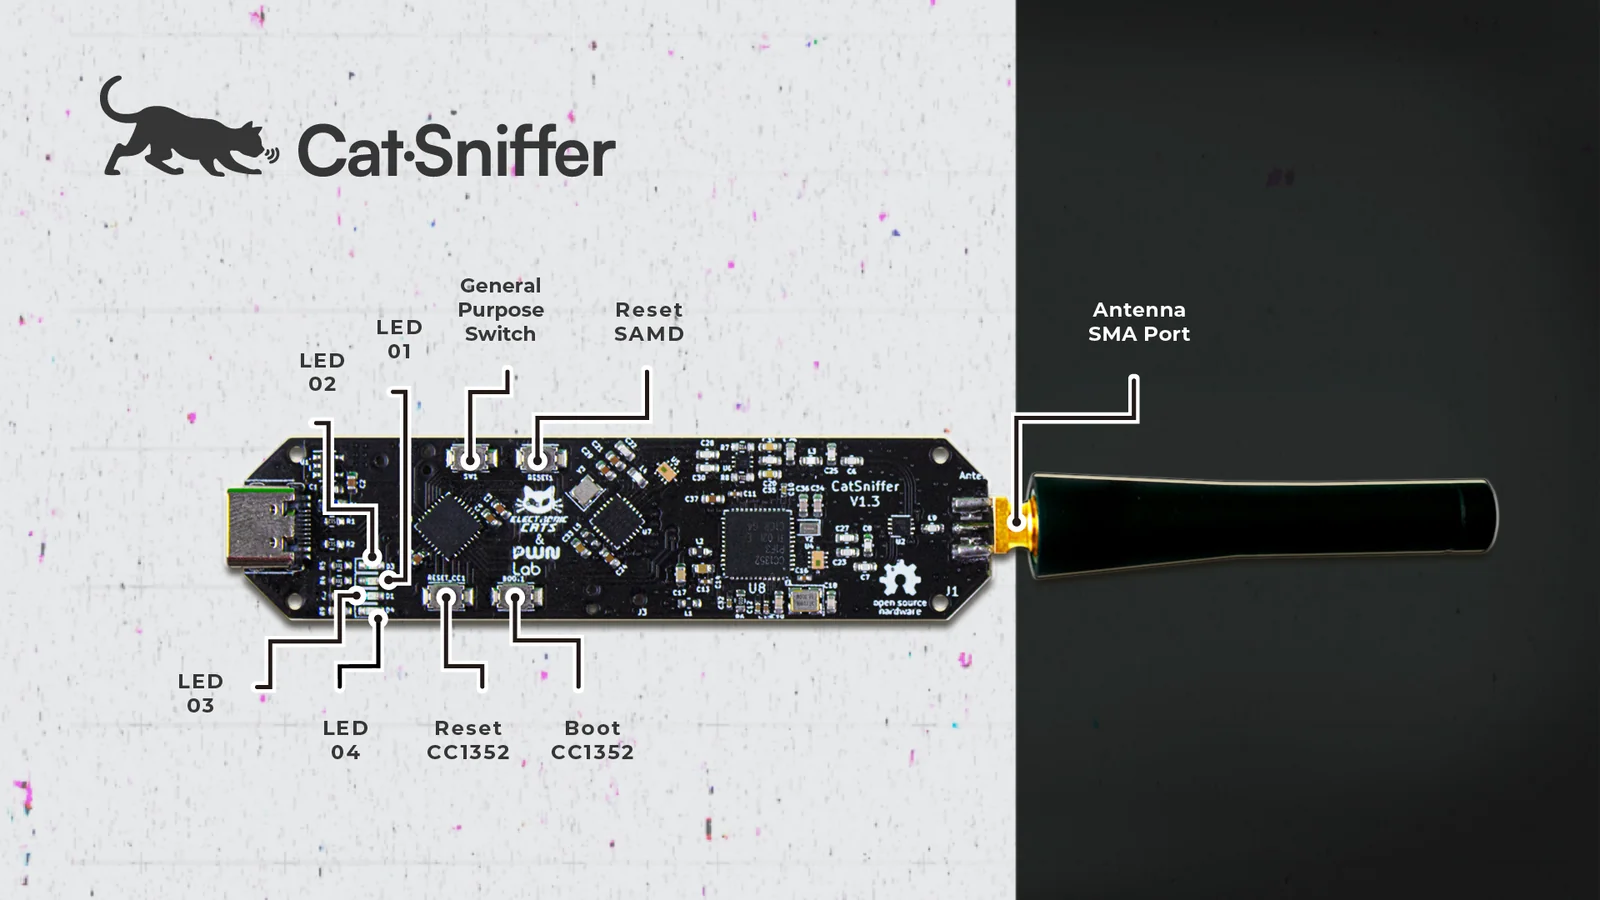 electroniccats/catsniffer-firmware
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 olivierlaflamme/unibleed
Unitree G1 RCE PoC & Scripts (CVE-2026-76639 / CVE-2026-76640) technical details at boschko.ca/g1-ble-rce/
 george0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication
Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…
 praetorian-inc/caeruleus
Single Go binary for Bluetooth Low Energy security testing on Linux/BlueZ: scan, enumerate GATT, read/write/notify, fuzz characteristics, and run…