
Loracrack
 applied-risk/loracrack
LoRaWAN session cracker - A PoC for exploiting weak or shared Application Keys
cryptographyexploitationhardware-iot-security+3
20
applied-risk/loracrackLoRaWAN session cracker - A PoC for exploiting weak or shared Application Keys
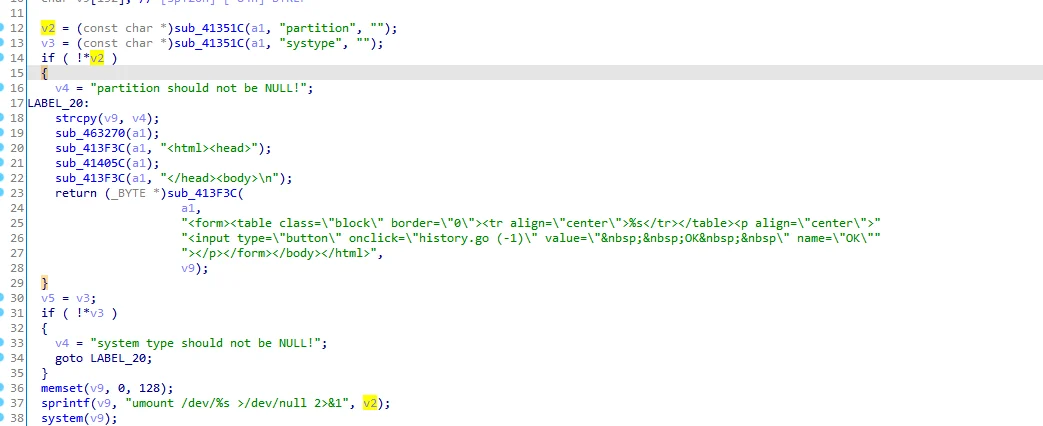 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 withsecurelabs/usb-ninja-detection-poc
Detects USB Ninja keystroke injection attacks by logging keystrokes and application events, providing a proof-of-concept for defensive monitoring.
 mattgsys/cve-2026-0834
Proof-of-concept exploit for TP-Link TDDP authentication bypass (CVE-2026-0834) that sends crafted packets to execute administrative commands like…
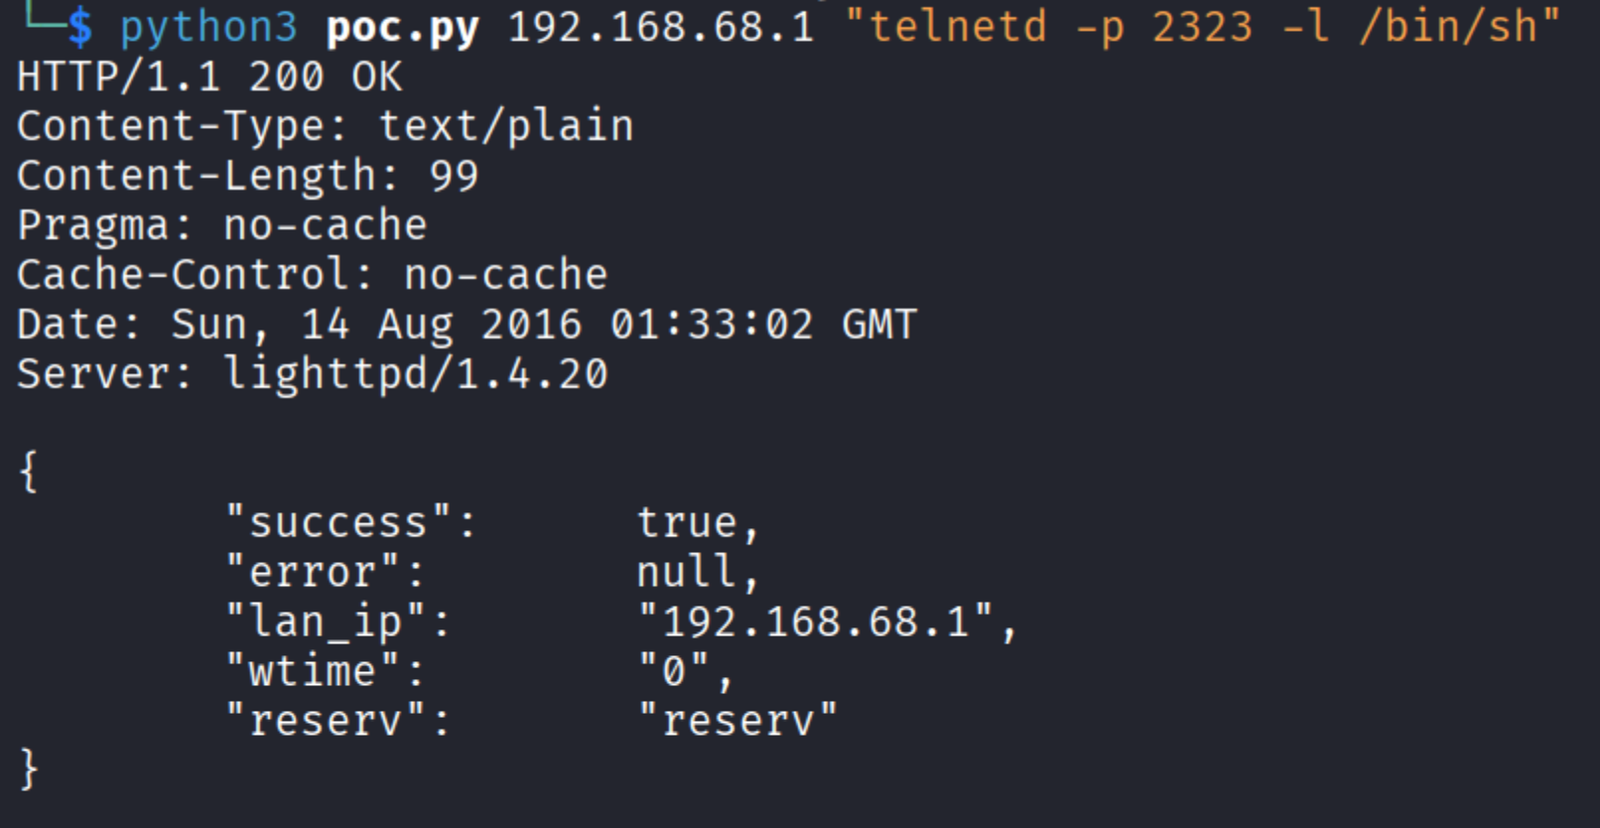 finnvle/cve-2022-28906-poc
Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands…
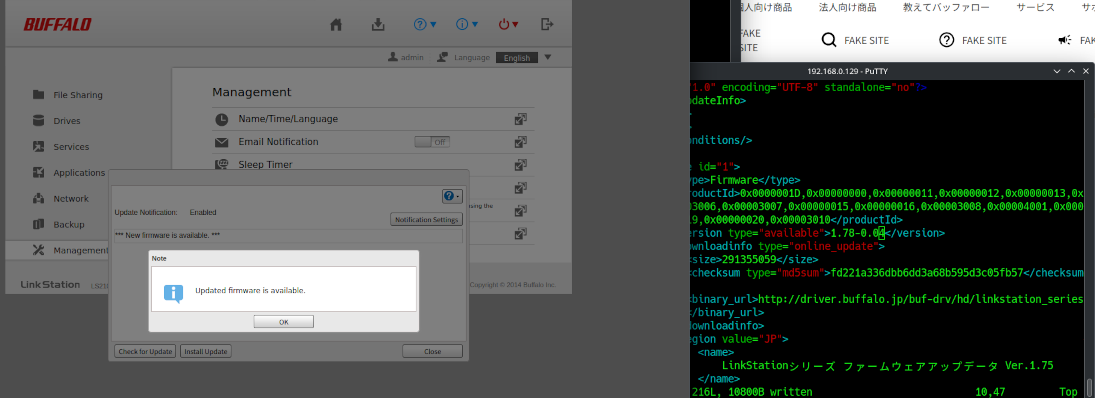 christopher-pace/cve-2023-51073
Firmware Update Server Verification Vulnerability on Buffalo LS210D Version 1.78-0.03
 slagzz/cve-2026-9254
TP-Link Archer BE800 V1 — Parental Control LAN RCE
 unknownpwn-zz/unknownpwn.github.io
infosec enthusiast and madman
 veygax/horizonstack
CVE-2026-43499 for the Meta Quest
 ebux/cable-modems
Black-box security evaluation of five ISP cable modem/router gateways, analyzing firmware images and documenting 35+ vulnerabilities including…
 aseemjakhar/kcmd
Kankun Smart Socket Hijacker and Sniffer. The kankun smart socket and its mobile app use a hardcoded AES 256 bit key to encrypt and decrypt…
 vanlam2001/netis-n5vn-ac1200-dos
Proof-of-concept exploit for a buffer overflow vulnerability (CVE-2024-44596) in Netis N5VN AC1200 routers, causing a denial of service by crashing…
 lequockhanh2k/tool_camera_exploit_netwave_cve-2018-6479
Exploit tool for CVE-2018-6479, a denial-of-service vulnerability in Netwave IP cameras. Targets IoT devices to trigger temporary service disruption…
 yoshida-git-ai/spacex-starlink-router-gen-2-xss
CVE-2023-49965 | SpaceX / Starlink Router Gen 2 XSS
 kostasereksonas/xm_onvif_auth_bypass
Proof-of-concept code (Bash and Python) for CVE-2025-65856 where ONVIF implementation in in Xiongmai XM530 IP cameras allows for unauthenticated …
 dorskfr/tapodate
Sets up a local Tapo C200 using CVE-2021-4045
 otsmr/internet-of-vulnerable-things
The results of my small term paper on the topic of the Internet of Vulnerable Things and the exploit for CVE-2022-48194.
 salgio/ewelink-qr-code
This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).