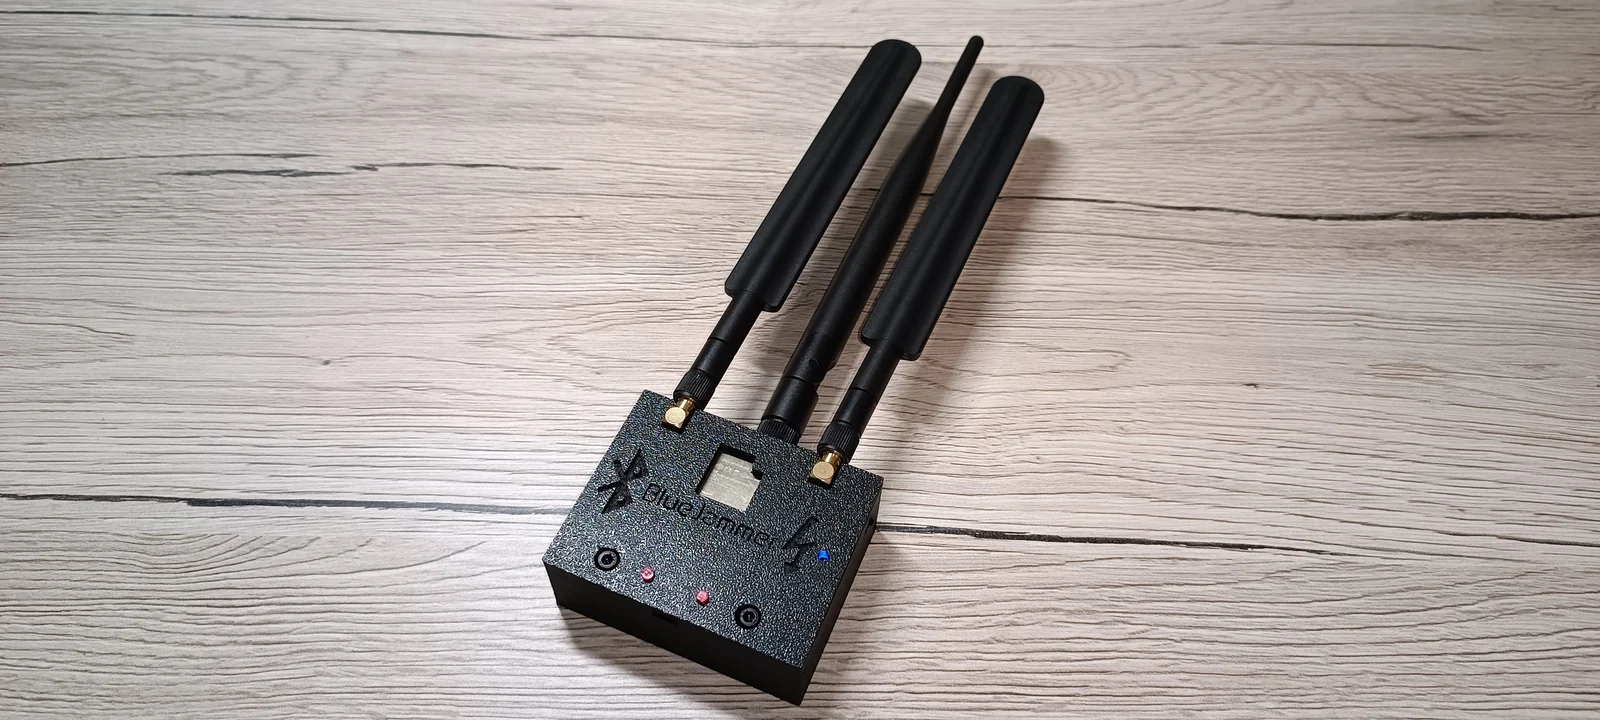

ESP32-BlueJammer
ESP32 and nRF24 based 2.4GHz jammer that disrupts Bluetooth, BLE, WiFi, and RC channels via noise and packet flooding for controlled security testing.

ESP32 and nRF24 based 2.4GHz jammer that disrupts Bluetooth, BLE, WiFi, and RC channels via noise and packet flooding for controlled security testing.

Single Go binary for Bluetooth Low Energy security testing on Linux/BlueZ: scan, enumerate GATT, read/write/notify, fuzz characteristics, and run…

Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…

Tool for testing and auditing Bluetooth device pairing security, identifying vulnerabilities in wireless pairing protocols and hardware IoT…

Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…

BLE-Replay is a Bluetooth Low Energy (BLE) peripheral assessment tool

BLESuite is a Python package that provides an easier way to test Bluetooth Low Energy (BLE) device

A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)

Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…

Scans Bluetooth Low Energy devices for Fast Pair vulnerabilities (CVE-2025-36911), testing if accessories accept unencrypted Key-Based Pairing…

PoC tool to demonstrate vulnerabilities in wireless input devices

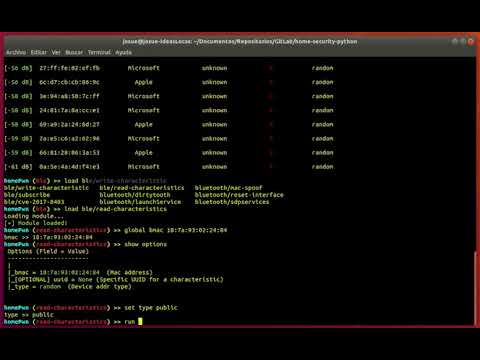
HomePwn - Swiss Army Knife for Pentesting of IoT Devices

Curated guide to IoT penetration testing hardware and software tools for 2025, covering Bluetooth, Zigbee, Z-Wave, WiFi, RFID, automotive, and…