cve-2026-43499-firetv-sheldonp-writeup

Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.

Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.

One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.

PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…

Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…

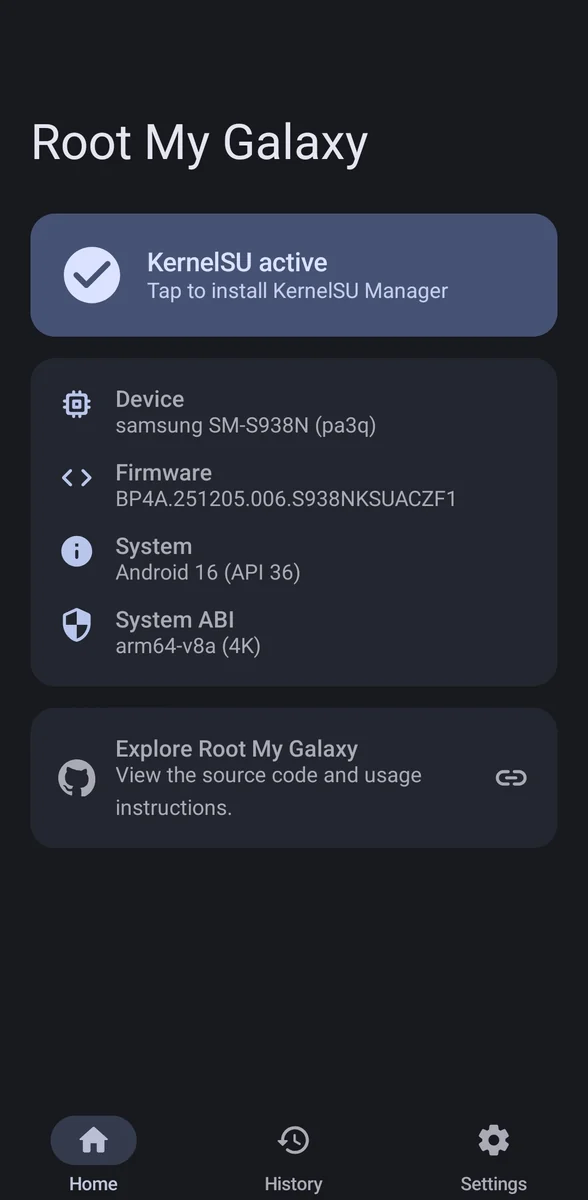
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499

Backports of three published f_hid fixes (incl. CVE-2026-31721, CVE-2026-31606) to an EOL Linux 4.14.190 Android vendor kernel, with on-device…

Proof-of-concept exploit for CVE-2021-34600, demonstrating a key generation vulnerability in Telenot access control systems using Proxmark3 RFID…

Proof-of-concept demonstrating CVE-2021-30731, allowing unauthorized USB webcam access on macOS. Built with libuvc, it previews connected webcams on…

Exploit or analysis code for CVE-2021-0510, a vulnerability in Android hardware interfaces, targeting A10_r33 builds.

Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell

Unlock the bootloader of any exploitable device vulnerable to CVE-2021-30327

Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…

PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.

Metasploit modules in testing

A ZigBee hacking toolkit by Bishop Fox

This repository contains a few vulnerabilities that were found and reported during vulnerability assessments.

This app checks if you're vulnerable to CVE-2016-8467 and/or if your bootmode property has been tampered with.

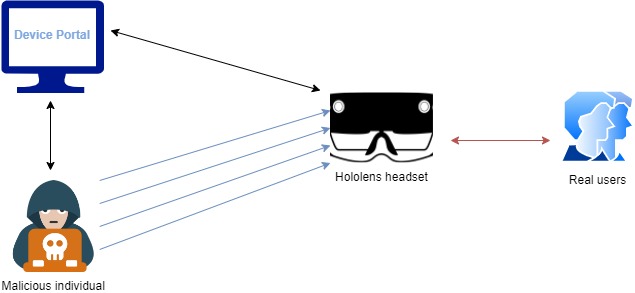
Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.