

moria
 nmatt0/moria
IoT firmware identification and extraction
binary-analysisdigital-forensicsembedded-systems-security+7
nmatt0/moriaIoT firmware identification and extraction
 ironfox-oss/ironfox
Hardened Android web browser forked from Mull/Firefox with privacy-focused patches, anti-fingerprinting, telemetry removal, and secure defaults for…
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 adamlaurie/rfidiot
Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…
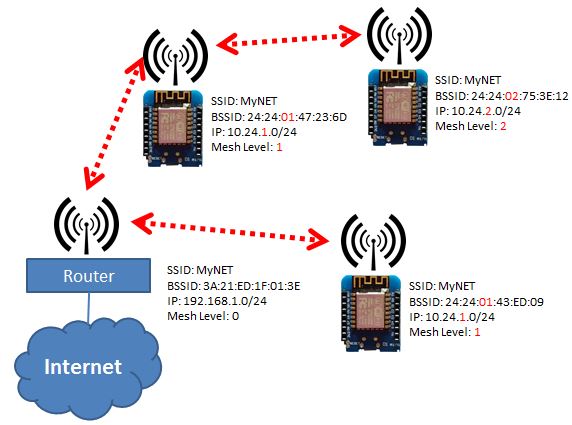 martin-ger/esp_wifi_repeater
A full functional WiFi NAT Router (and now also a WiFi Repeater)
 nicholasaleks/damn-vulnerable-drone
Damn Vulnerable Drone is an intentionally vulnerable drone hacking simulator based on the popular ArduPilot/MAVLink architecture, providing a…
 the-girl-who-lived/cve-2020-11539
Improper Access Control in Tata Sonata Smartband
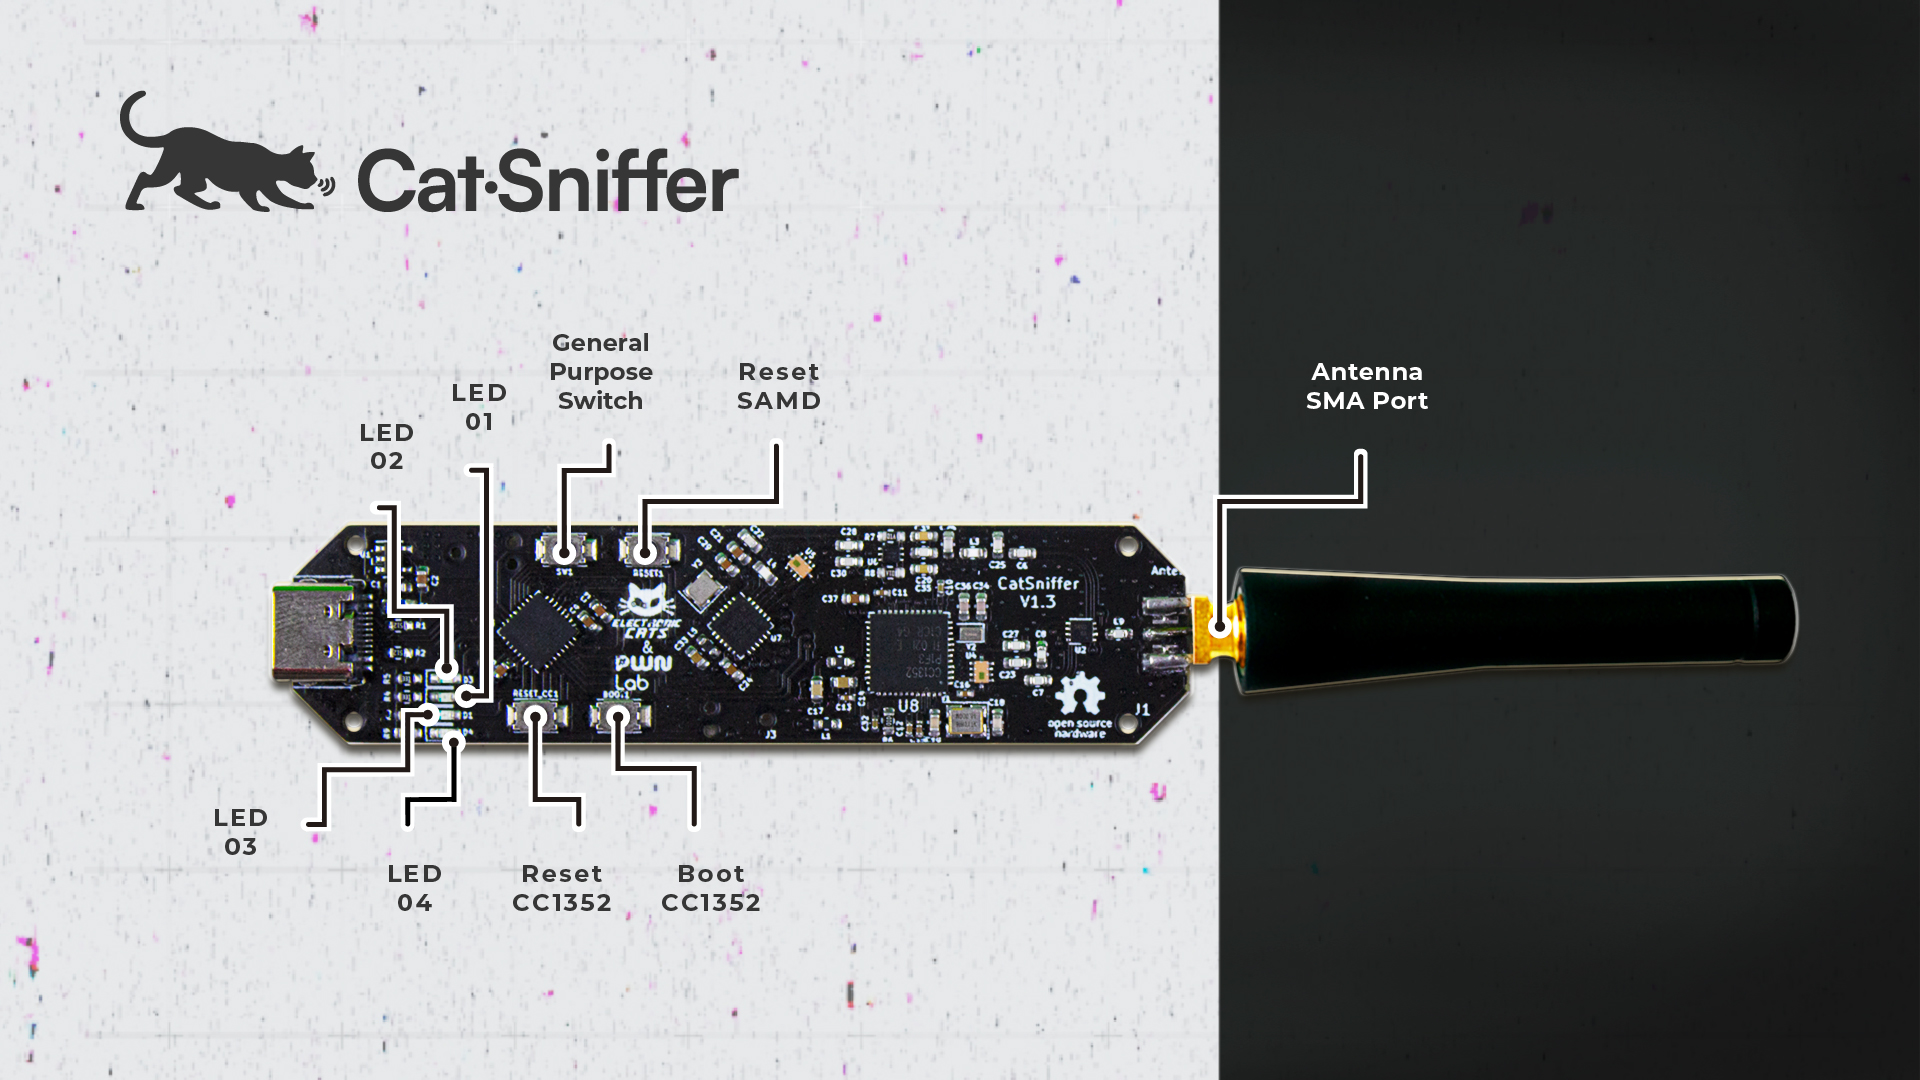 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 p-state/ida-efitools2
IDA plugin for extending UEFI reverse engineering capabilities
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
 steveakawlabs/marmalade-2-cve-2025-67780-exploit
Exploit PoCs for MARMALDE 2 (CVE-2025-67780) vulnerability in Starlink Dishes
 osy/webcamviewer
Proof-of-concept demonstrating CVE-2021-30731, allowing unauthorized USB webcam access on macOS. Built with libuvc, it previews connected webcams on…
 zgsnj123/cve-2025-45466
It is the details of CVE-2025-45466
 swiftloke/fusee-toy
Implementation of CVE-2018-6242 (AKA Fusée Gelée, AKA shofel2)
 absholi7ly/poc-cve-2024-57040
CVE-2024-57040 is a security vulnerability found in certain TP-Link TL-WR845N router models. Specifically, it involves a "hardcoded" password for the…
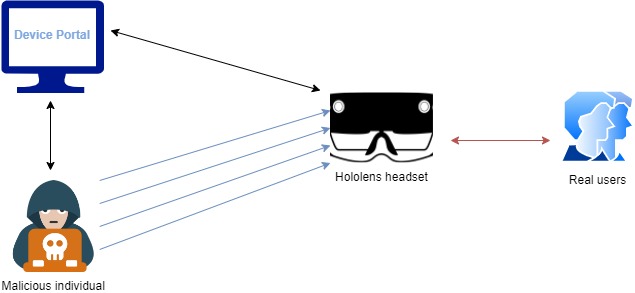 tania-silva/cve-2024-57972
Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.
 tacnetsol/cve-2019-10999
Full exploit for D-Link DCS-5020L, POC crash for others that are vulnerable as well.