
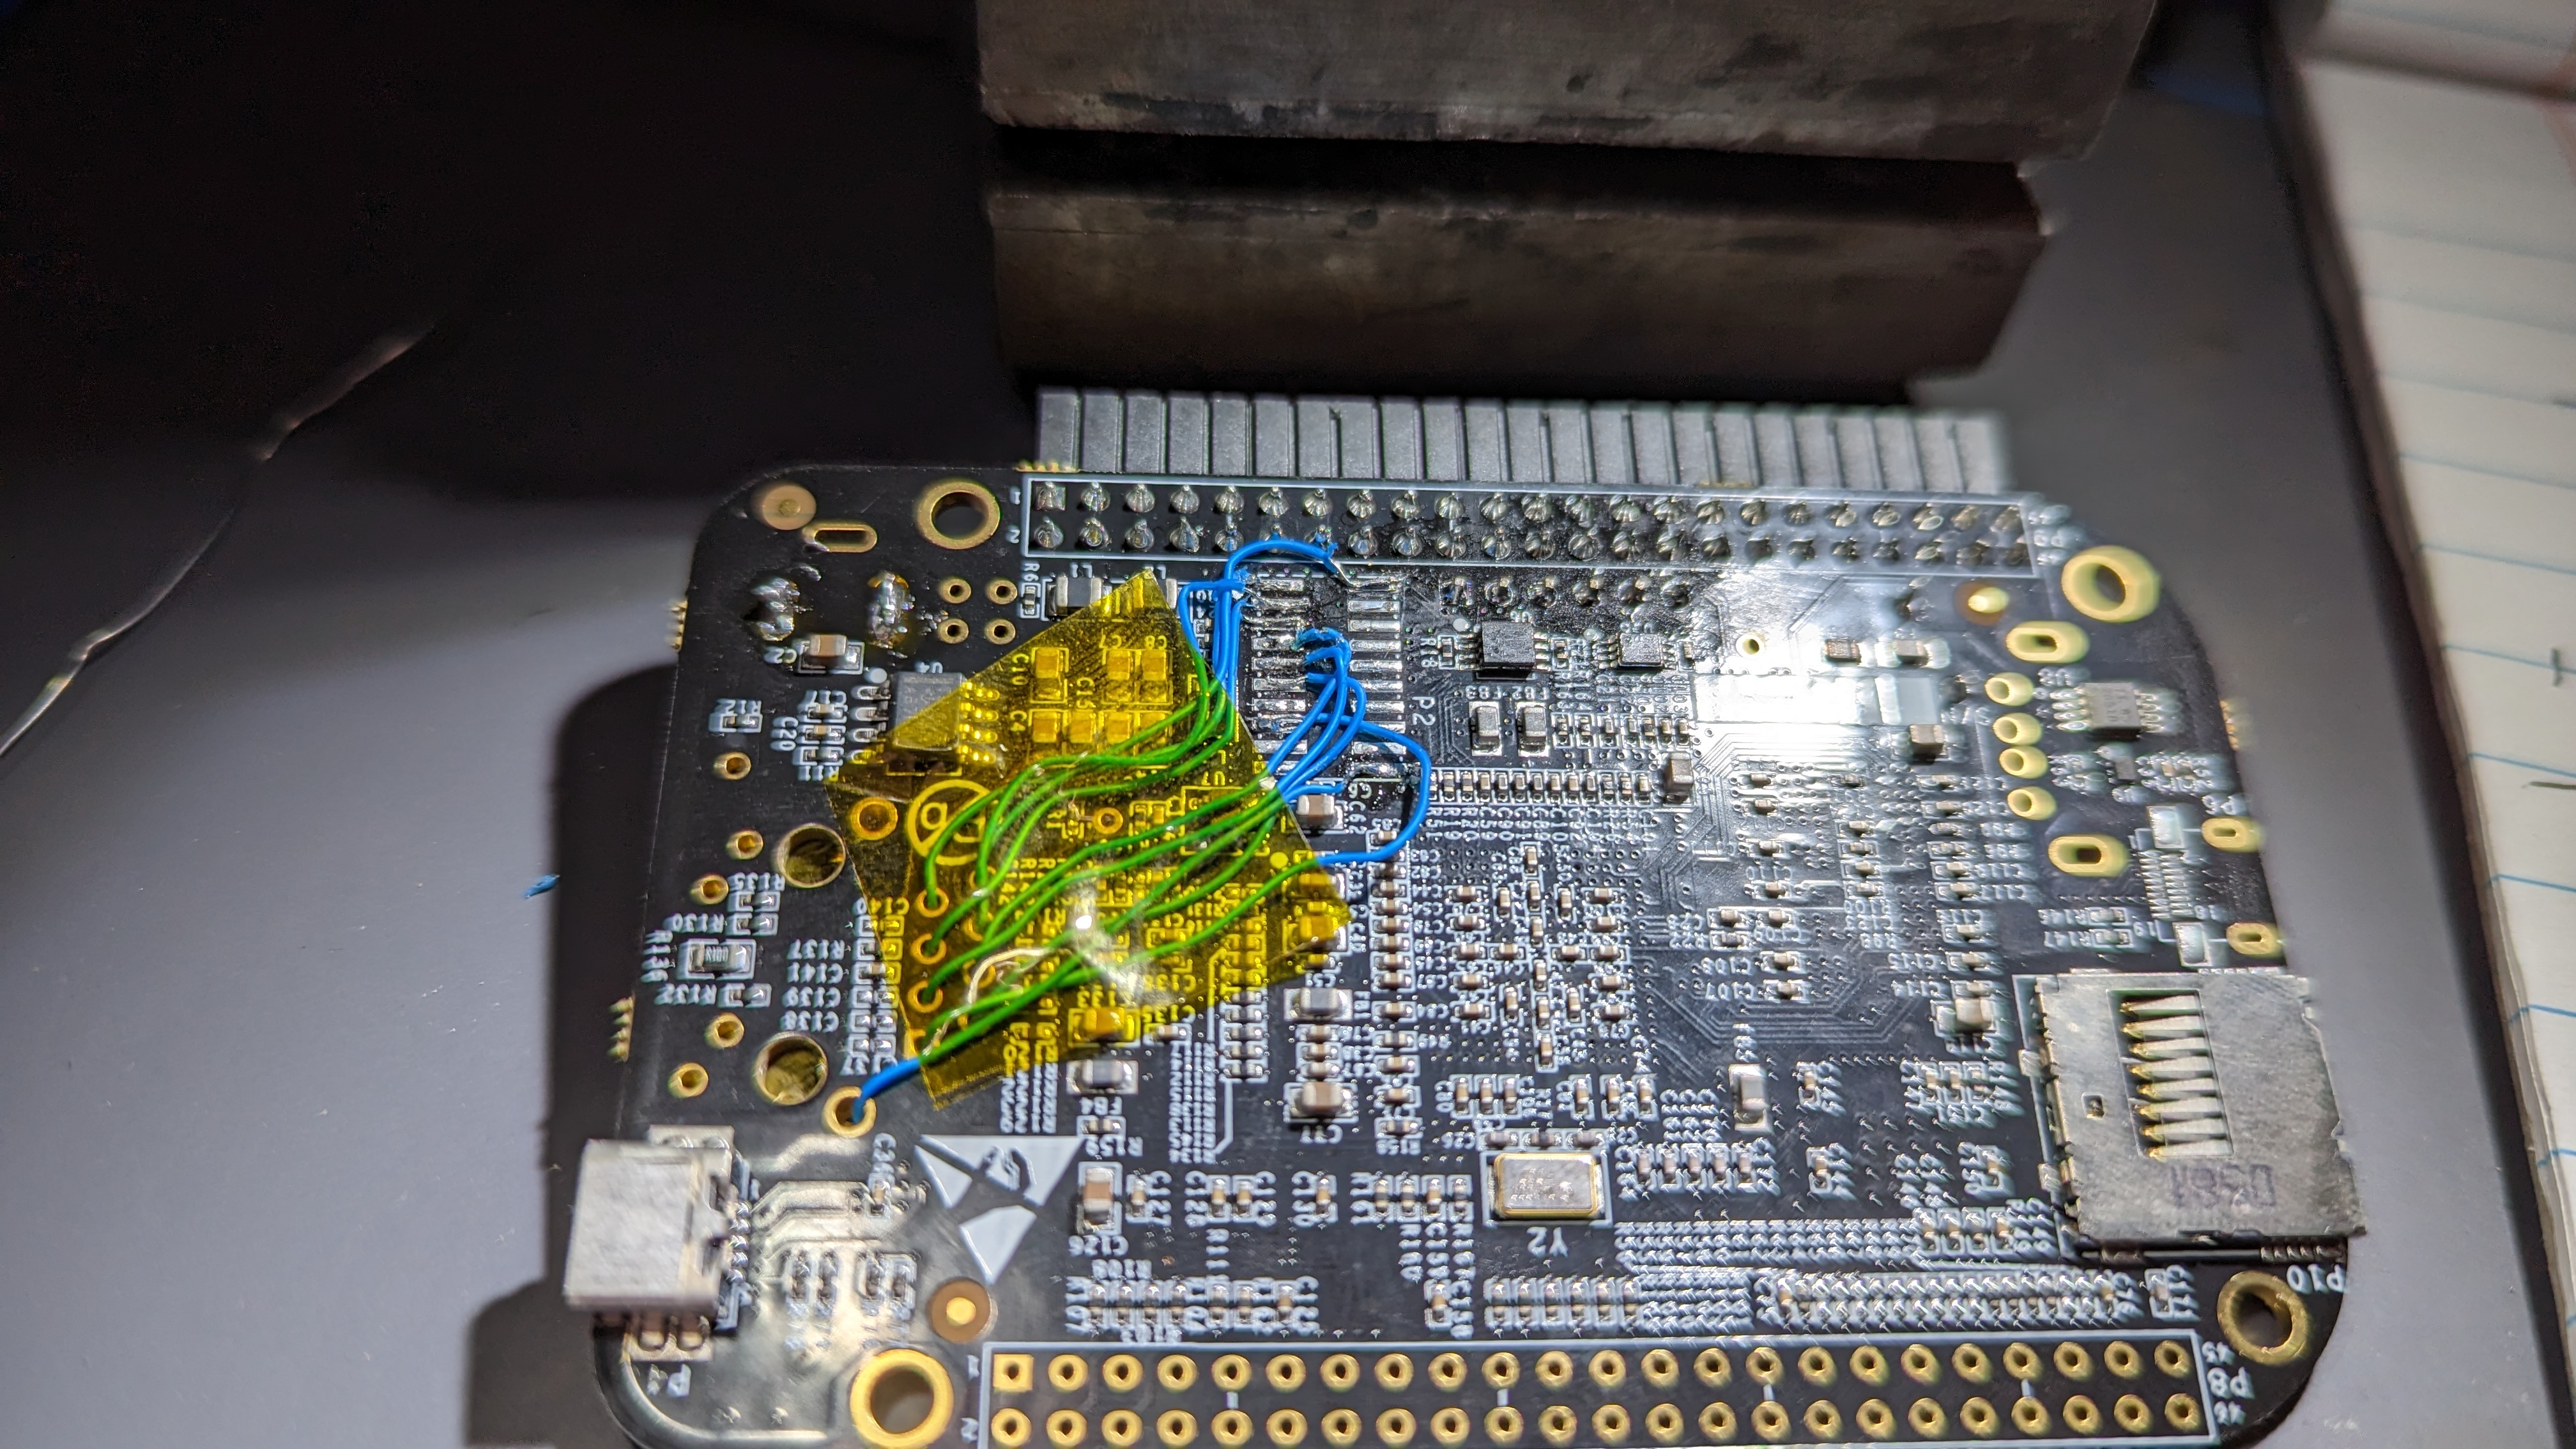
am335xbootrom
 sjgallagher2/am335xbootrom
Reverse engineering the TI AM3358 boot ROM
binary-analysisdebuggerseducation+4
sjgallagher2/am335xbootromReverse engineering the TI AM3358 boot ROM
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
 finngineering/ch55x_firmware_extractor
Firmware extractor for CH55x microprocessors
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
 beigeworm/badusb-files-for-flipperzero
A Collection of Over 60 Scripts - updated specifically for the BadUSB function on the FlipperZero.
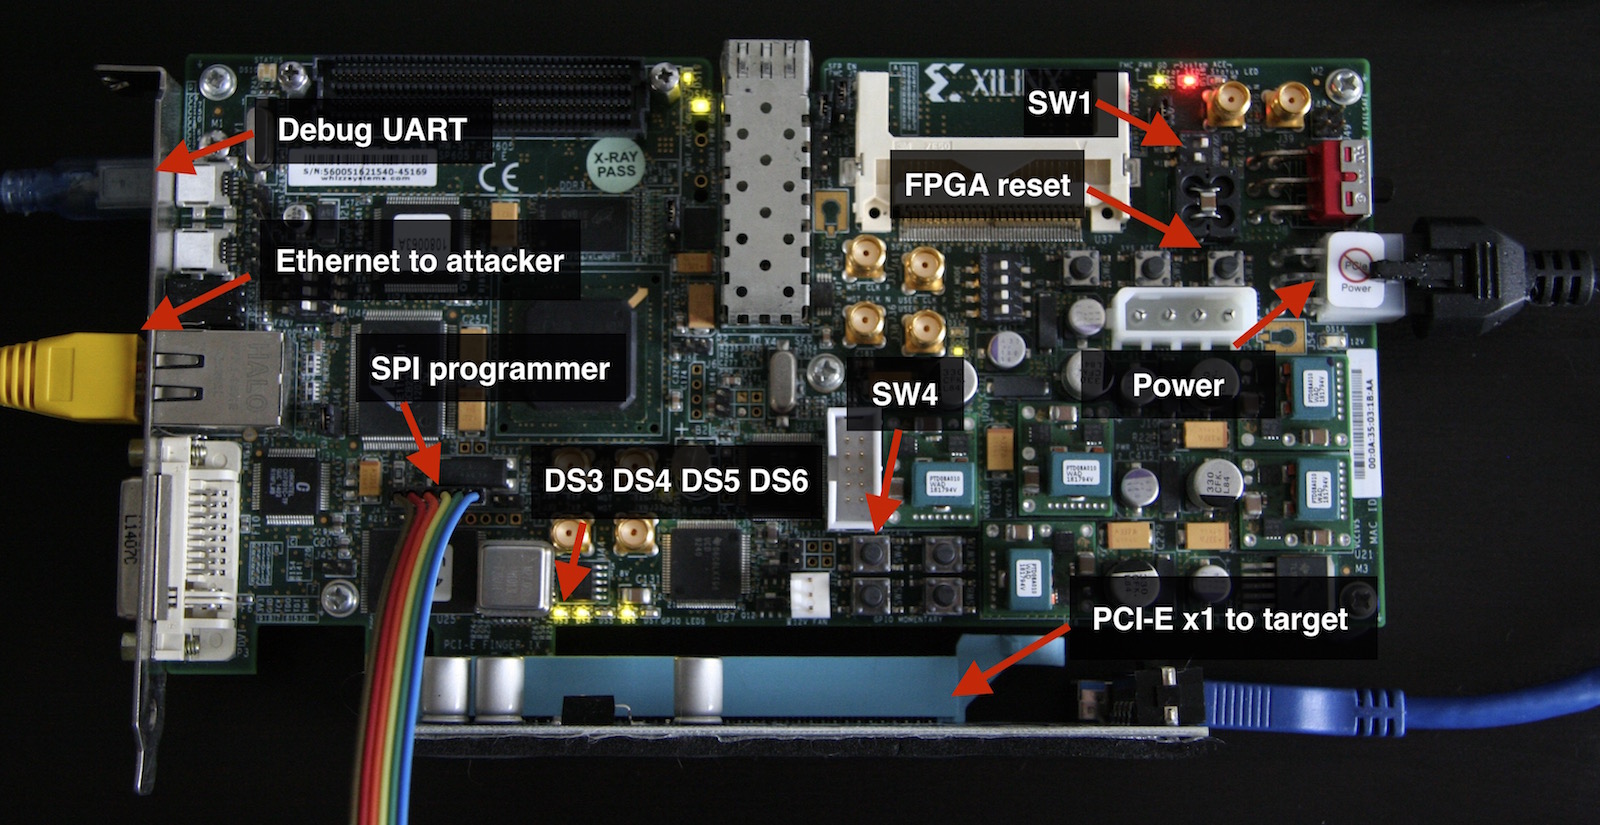 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
 zarcolio/flipperzero
This repo contains my own Ducky/BadUSB scripts, related PowerShell scripts and other Flipper Zero related stuff.
 thewhiteh4t/flashsploit
Exploitation Framework for ATtiny85 Based HID Attacks
 denandz/lpc_sniffer_tpm
A low pin count sniffer for ICEStick - targeting TPM chips
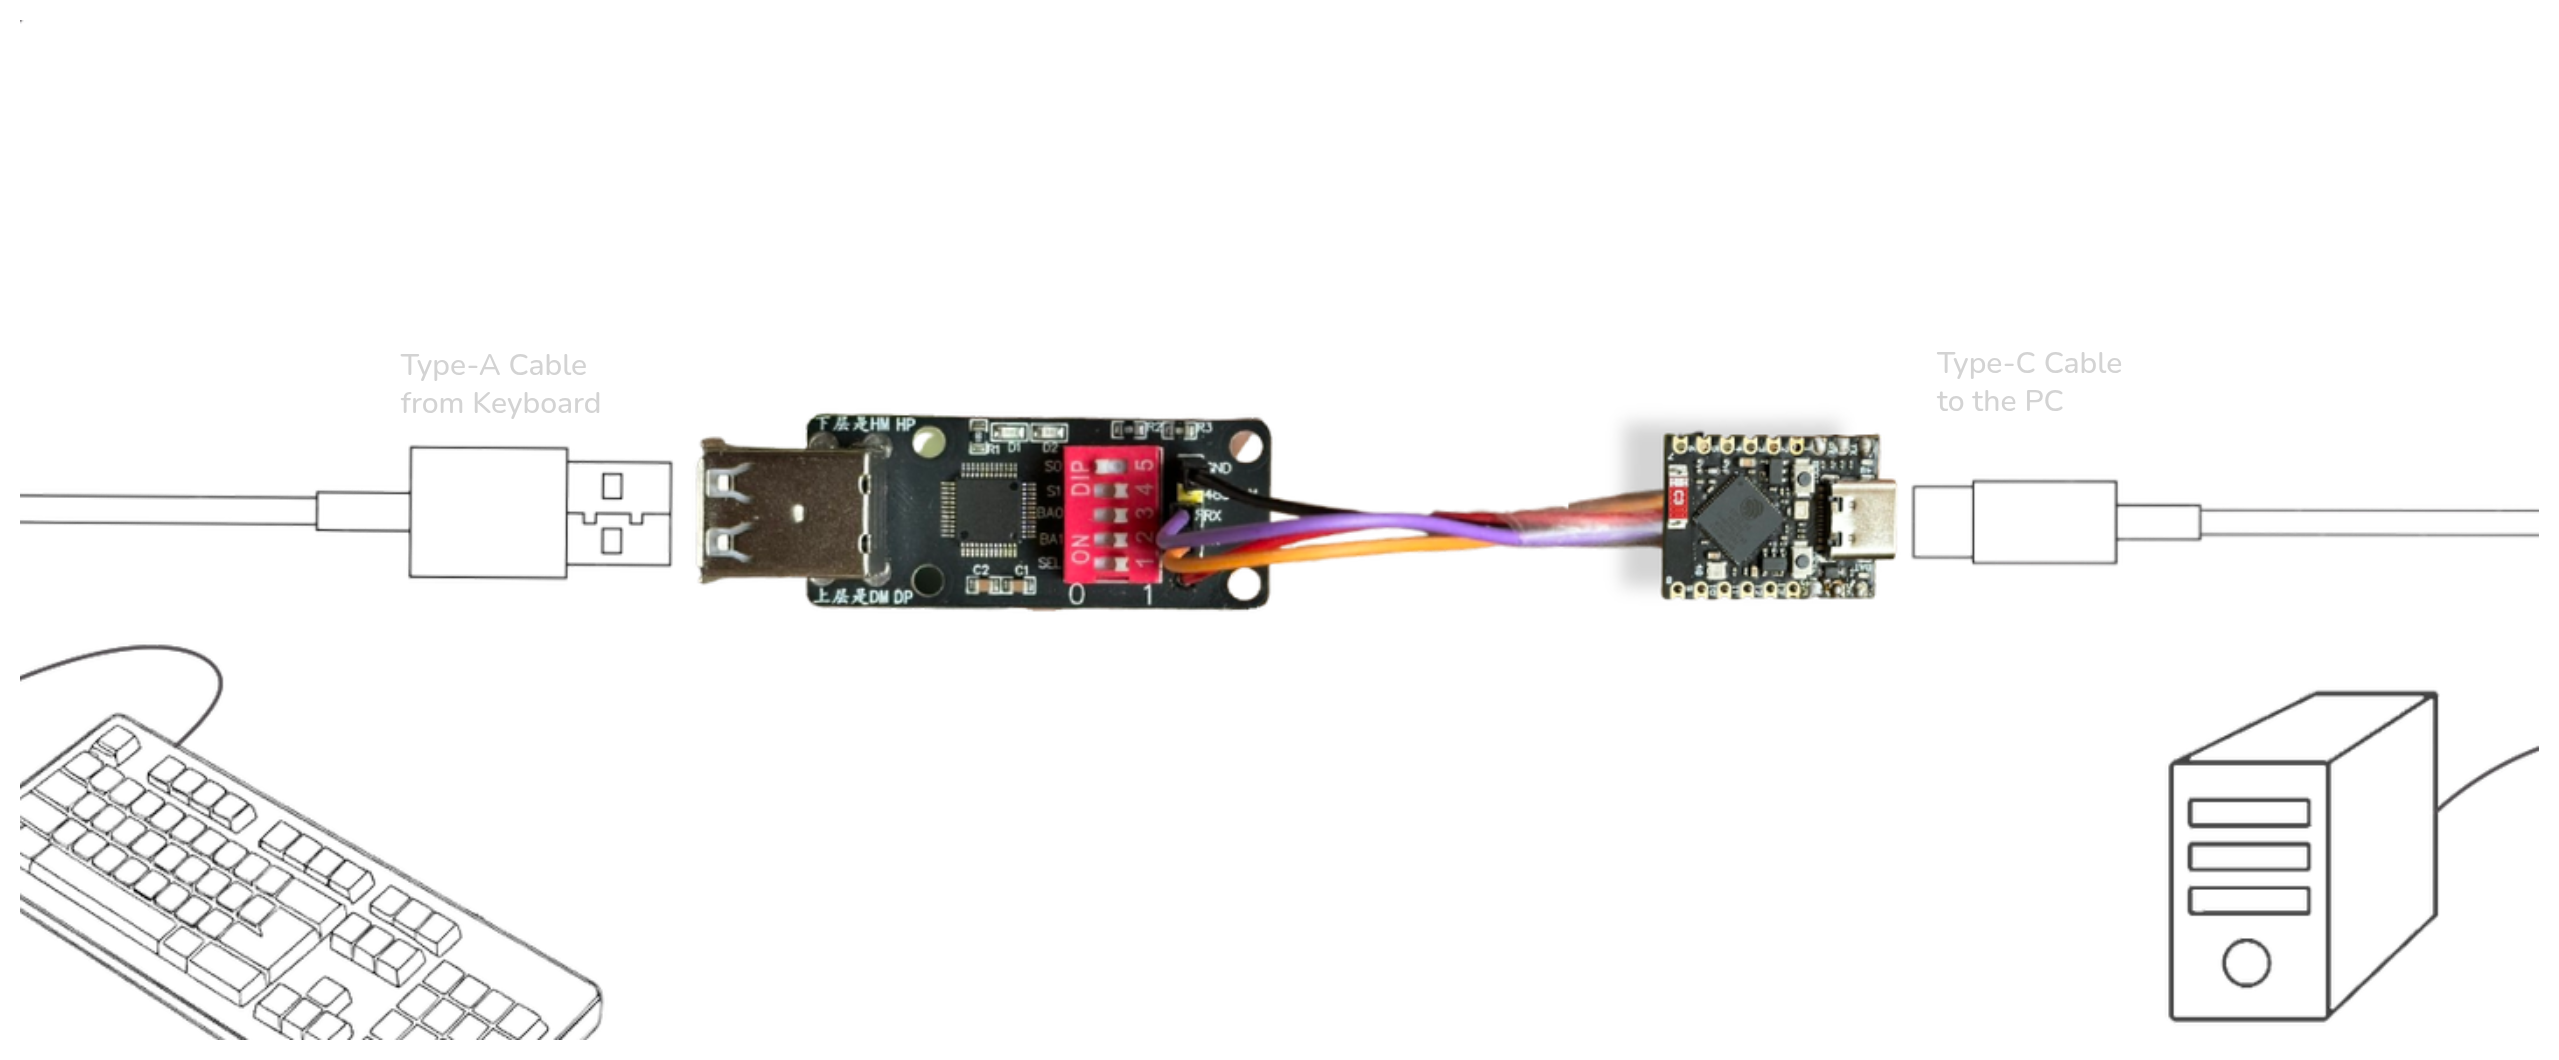 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 nastycrow/cve-2025-51643
Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device