
Fault-Injection-Finder
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
binary-analysisembedded-systems-securityexploitation+5
14
geeoon/fault-injection-finderAutomatically find and execute fault injection attacks
 fxrstor/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
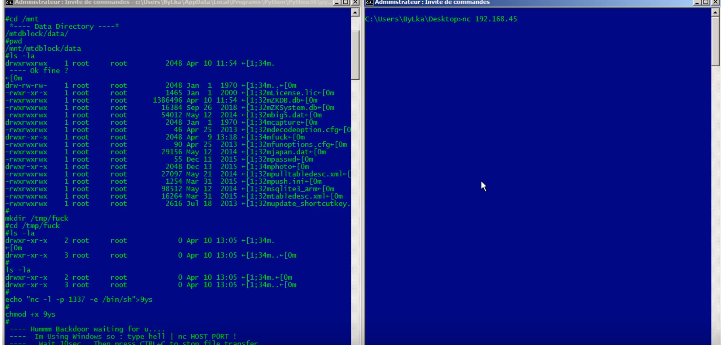 9aylas/backdooring-zmm100-fingerprint-devices
AuthBypass & Auto Backdooring Devices
 drapl0n/pwnkit
USB Rubber Ducky payload that exploits CVE-2021-4034 to escalate privileges and spawn a root shell on Unix-like systems in under 10 seconds.
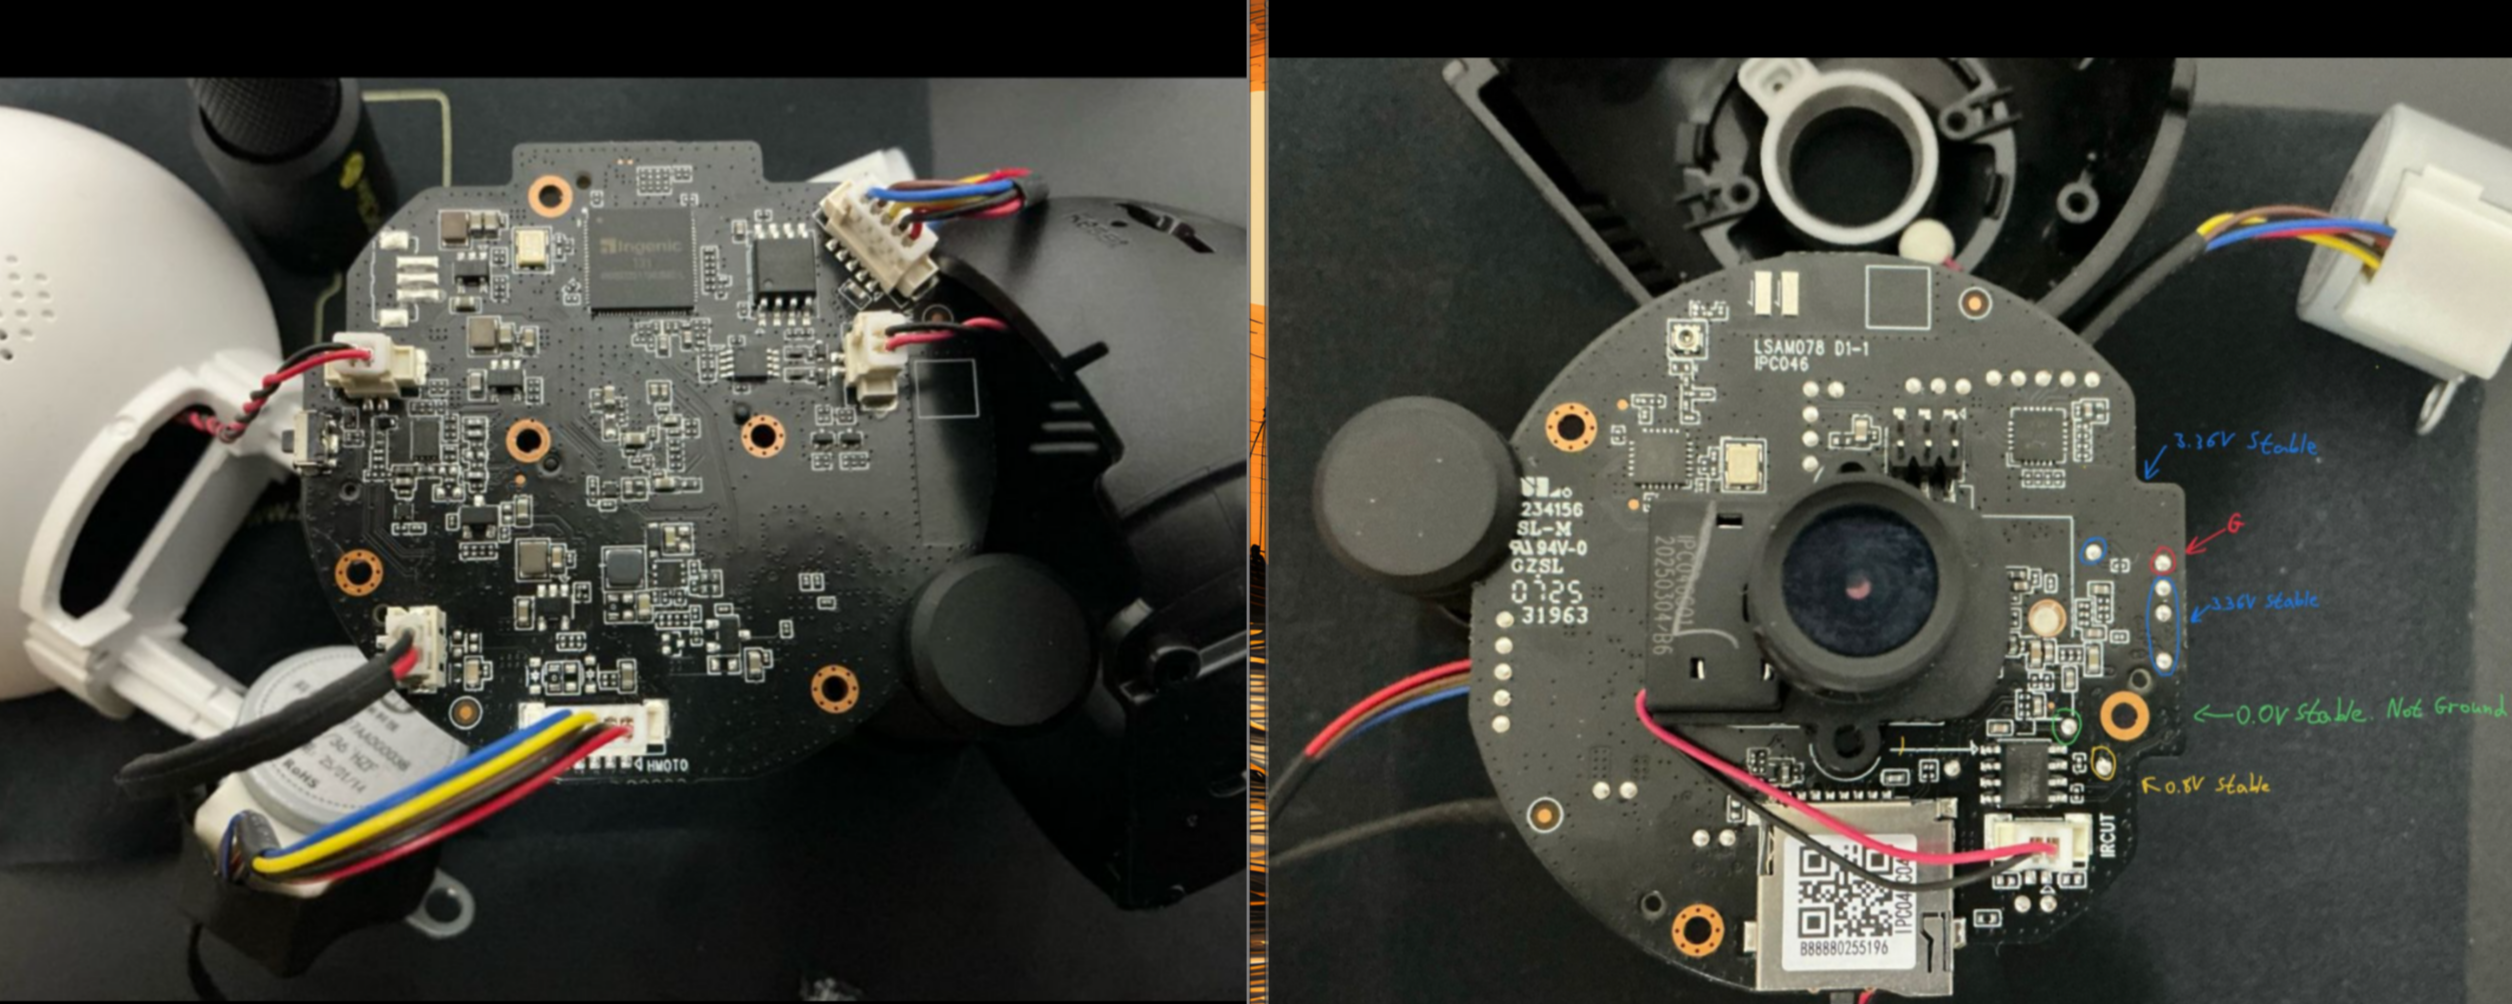 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 infobyte/symax5sw-rx-tx
Syma X5SW Telemetry and Transmissor
 adrihd/shiningappmask-reverseengineering
Reverse Engineering of the Shining App Mask
 sacriphanius/zhilly
🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…
 drmnsamoliu/cve-2019-17147_practice_material
This repo contains dumped flash partitions with firmware version vulnerable to CVE-2019-17147, and some useful binaries to downgrade and debug your…
 creased/arducky
Arducky - Arduino Ducky Script Interpreter
 aprkr/cve-2023-48034
Weak encryption in Acer Wireless Keyboard SK-9662 allows attacker in physical proximity to both decrypt wireless keystrokes and inject wireless…
 nastycrow/cve-2025-51643
Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…
 rupeshsurve04/cve-2025-67399
Documentation of CVE-2025-67399: physical UART debug interface exploitation on AIRTH Smart Home AQI Monitor (BK7231N SoC) enabling unauthorized…
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
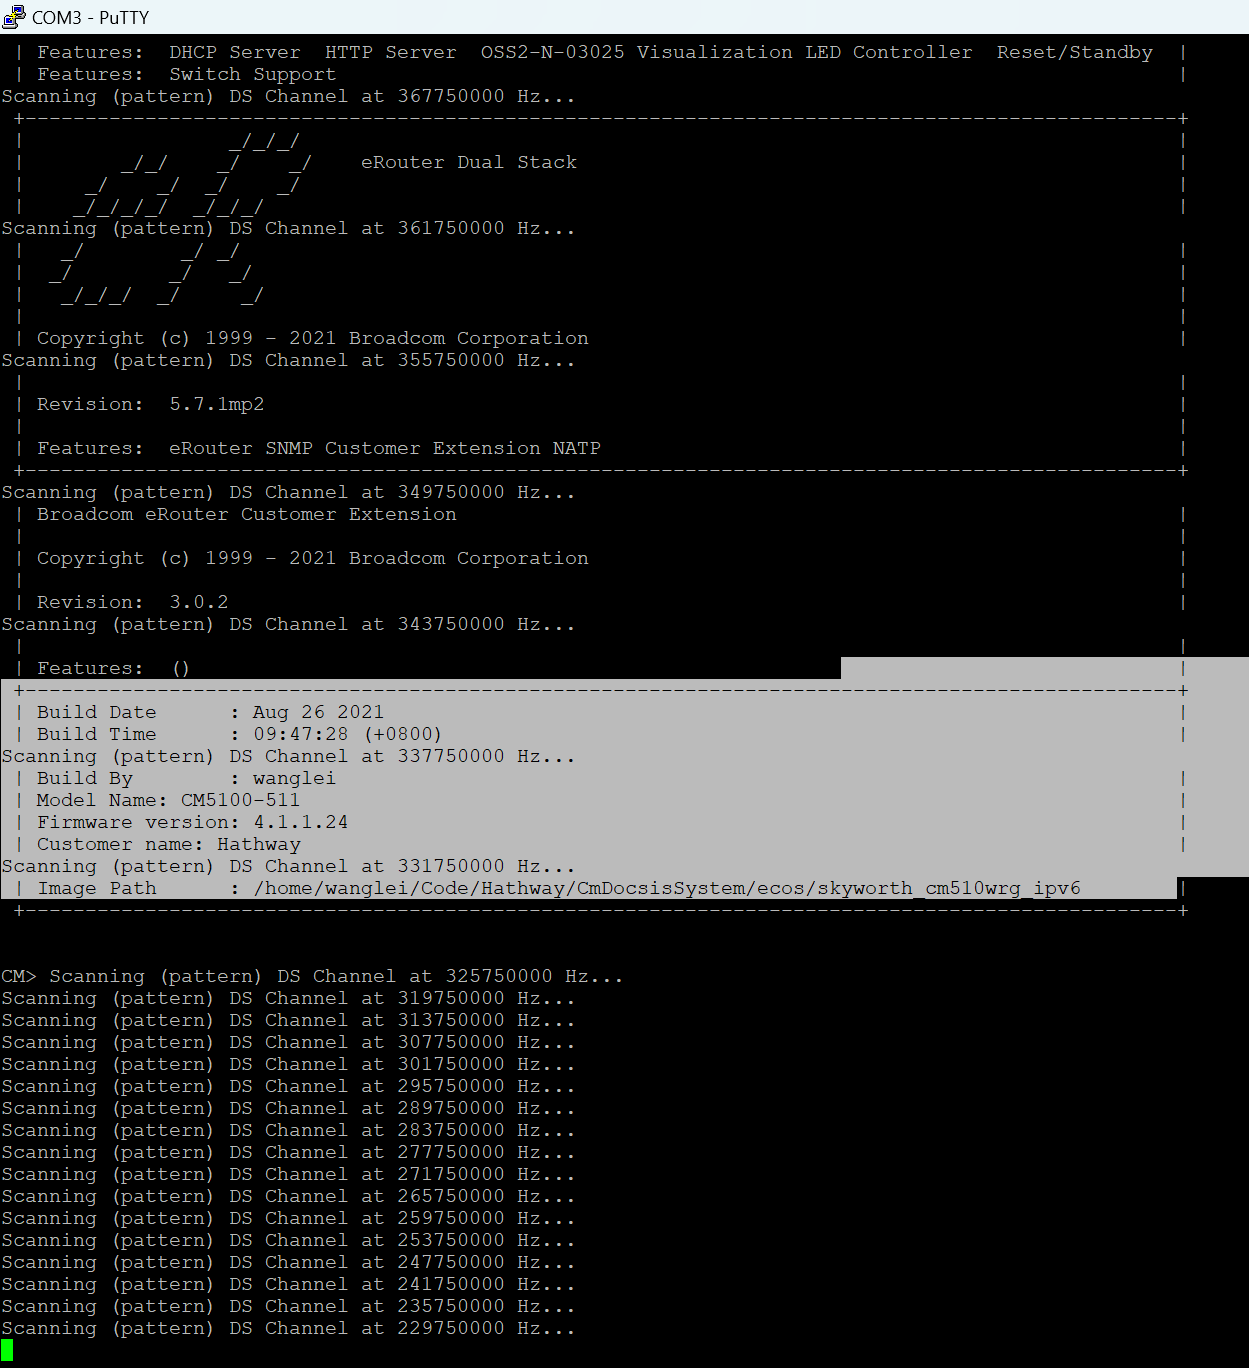 nitinronge91/extracting-user-credentials-for-web-portal-and-wifi-ap-for-hathway-router-cve-2024-44815-
CVE-2024-44815
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…
 nitinronge91/sensitive-information-disclosure-via-spi-flash-firmware-for-hathway-router-cve-2024-46383
CVE-2024-46383