

GhostESP
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
bluetooth-securityembedded-systems-securityhardware-hacking+8
ghostesp-revival/ghostespThe open-source wireless research platform for ESP32.
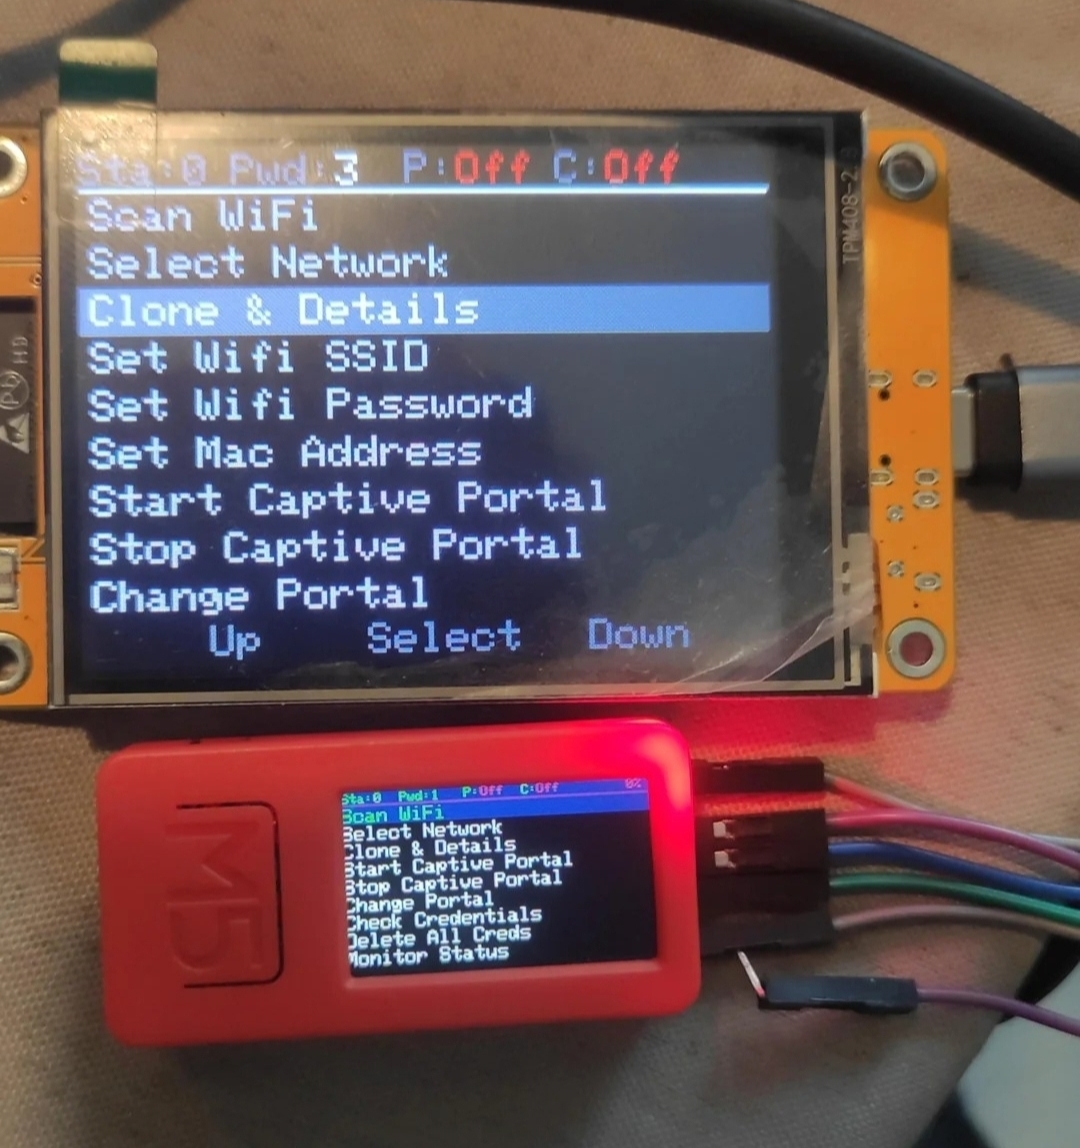 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
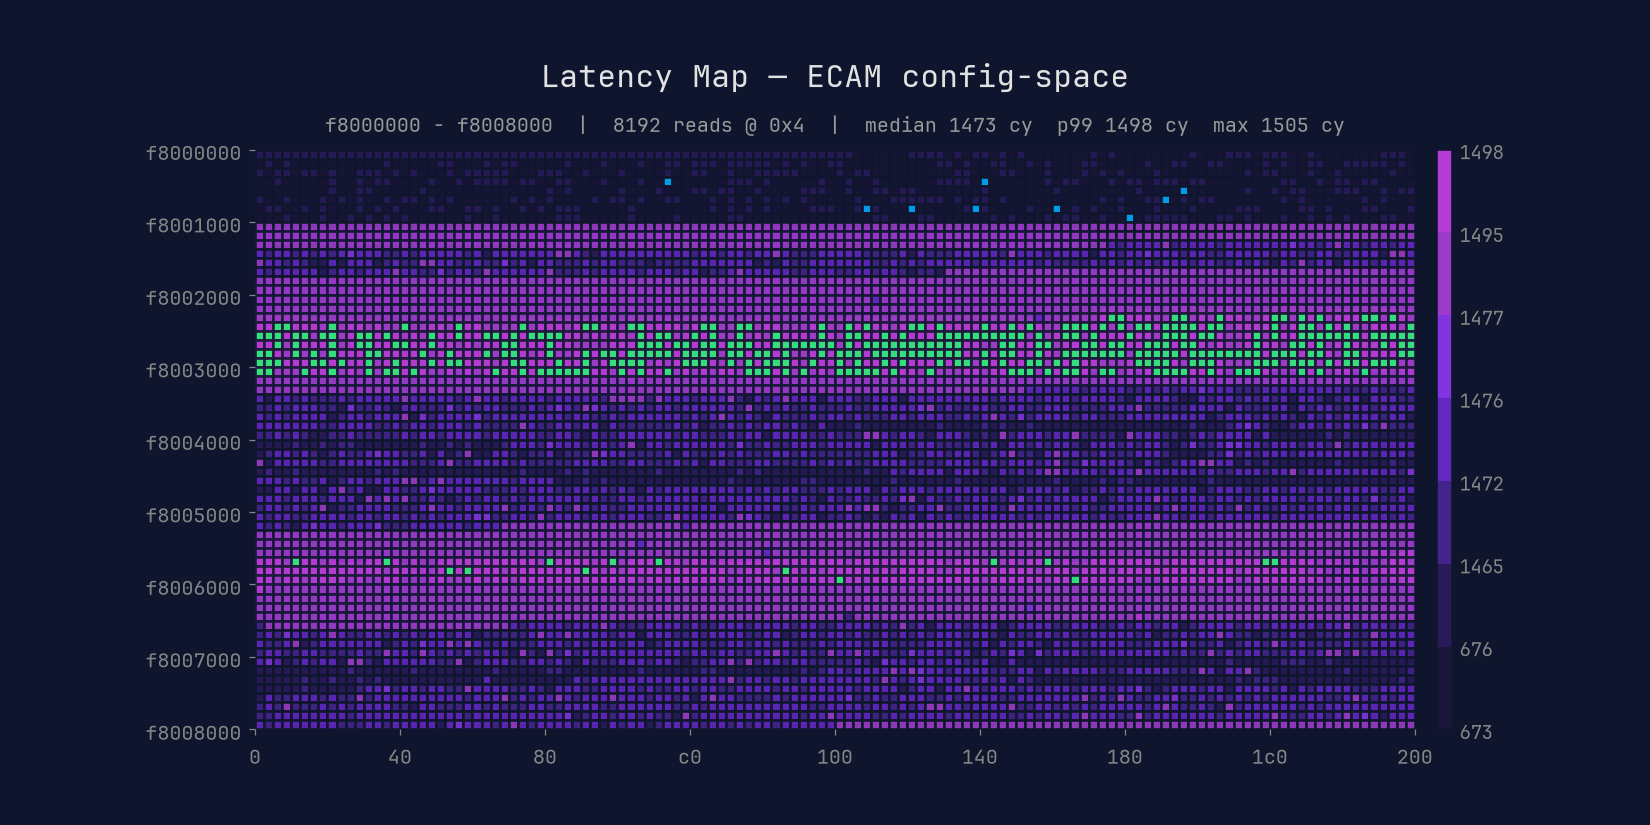 xoreaxeaxeax/mmiotic
Latency x-ray for undocumented hardware
 idoka/awesome-canbus
:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…
 sacriphanius/zhilly
🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…
 luispl77/433screen-signalhacker
Full duplex 433 MHz Signal jammer, recorder, decoder and hacking multitool device based on ESP32 microcontroller and RFM69HW radios. This version of…
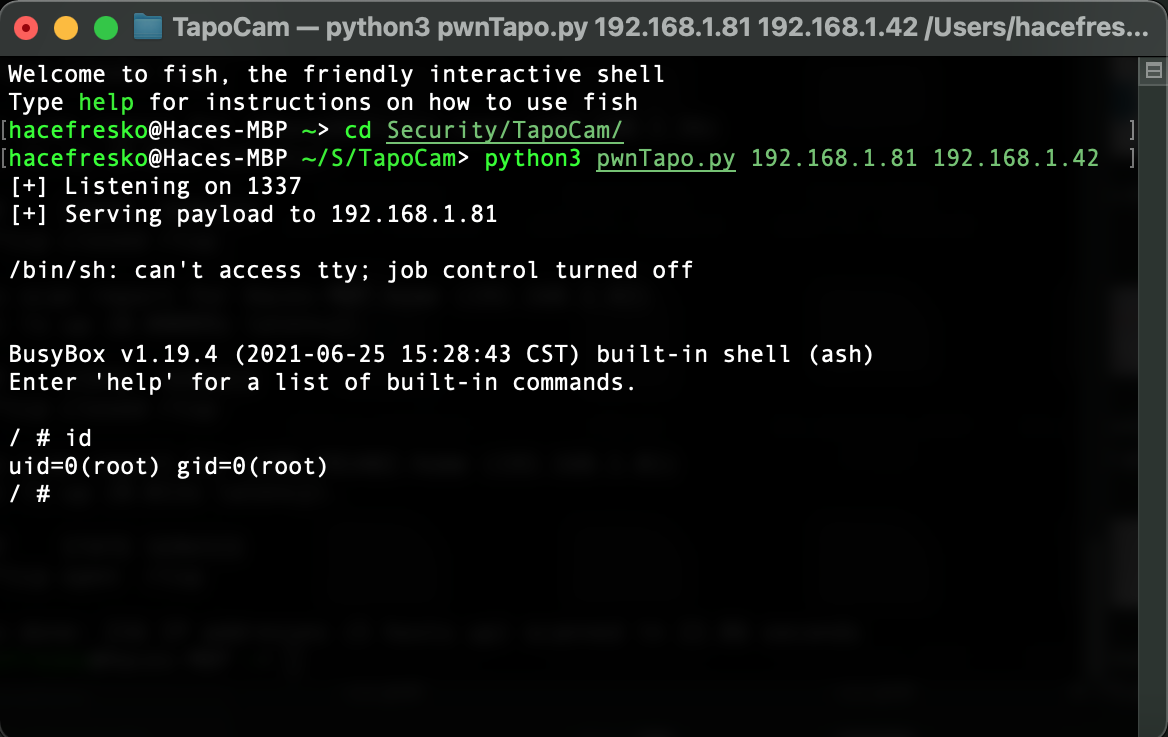 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
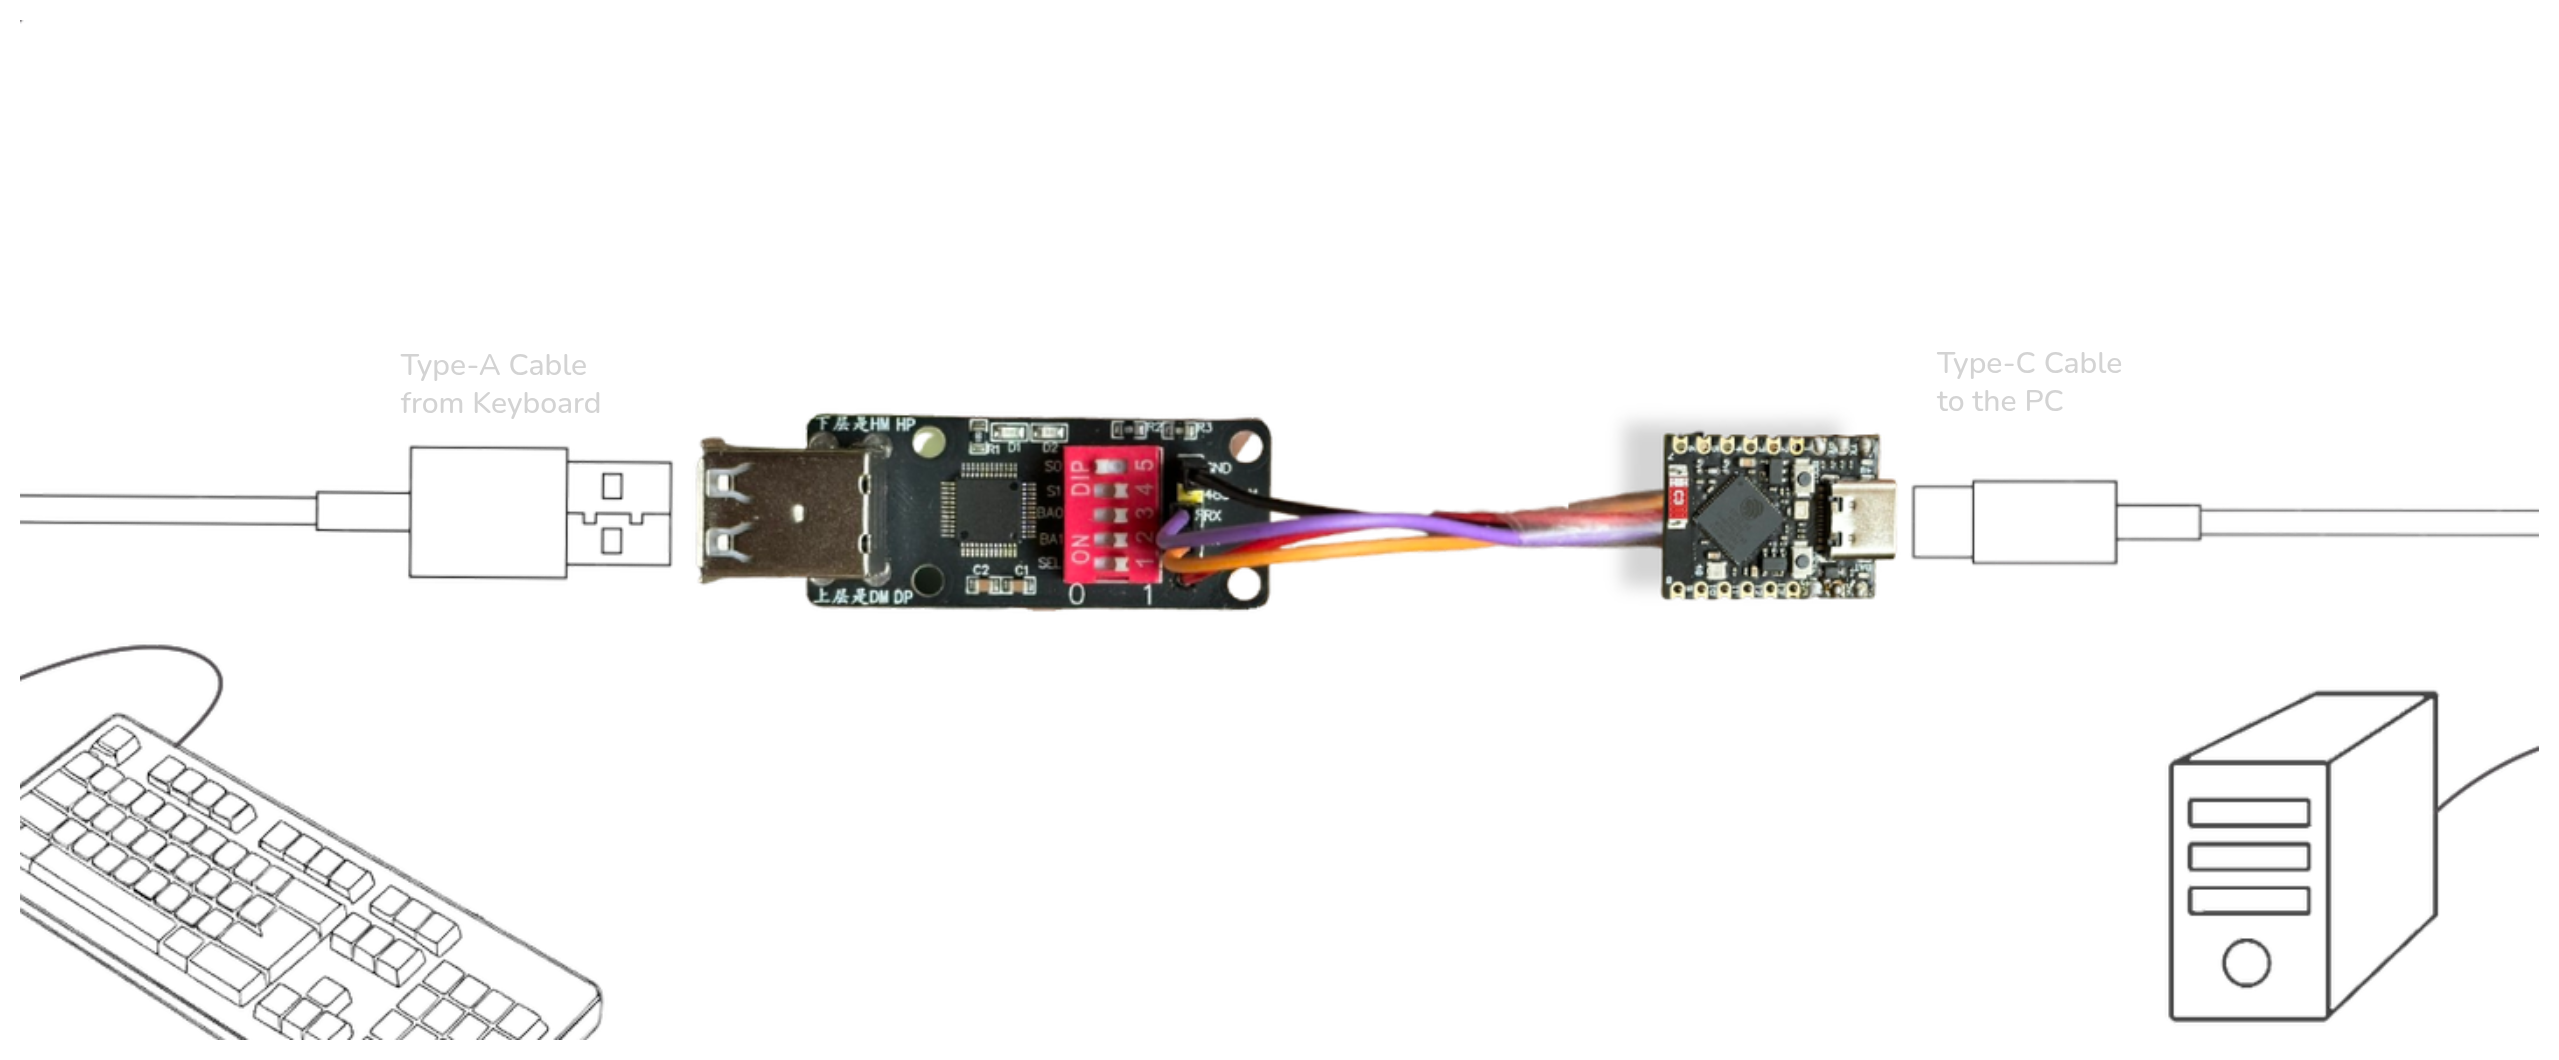 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
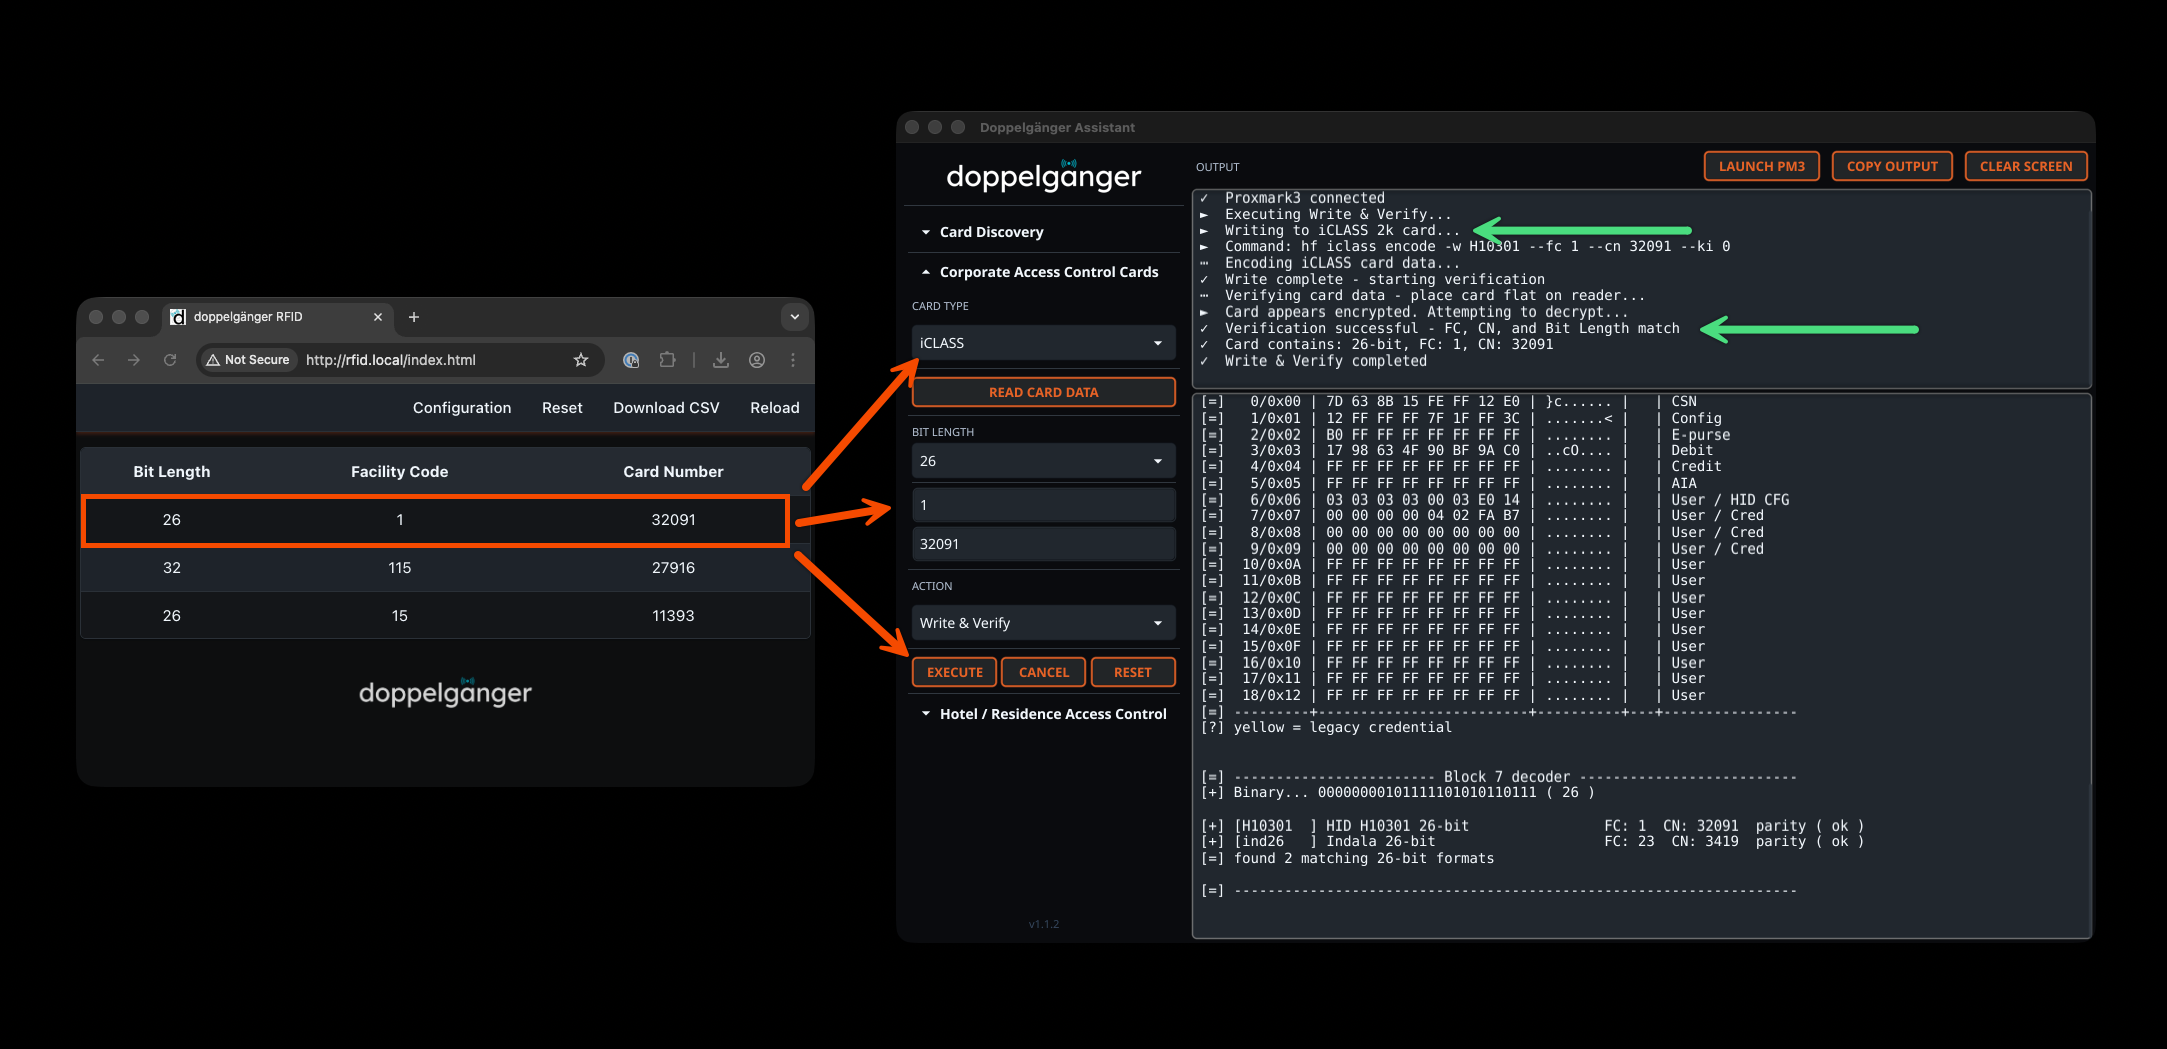 tweathers-sec/doppelganger_assistant
Card calculator and Proxmark3 Plugin for writing and/or simulating every card type that Doppelgänger Community, Pro, Stealth, and MFAS support.
 nccgroup/sniffle
Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…
 aleksamcode/wifi-password-stealer
Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).
 veereshgadige/aziot-cctv-cve-2025-50777
CVE-2025-50777: Root Access and Plaintext Credential Exposure in AZIOT Smart CCTV