

emba
 e-m-b-a/emba
EMBA - The firmware security analyzer
embedded-systems-securitystatic-analysisvulnerability-scanners+8
e-m-b-a/embaEMBA - The firmware security analyzer
 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 mister-devel/main_mister
FPGA-based hardware emulation platform main binary and documentation for retro system development, firmware compilation, and hardware security…
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 newaetech/chipwhisperer
Open-source hardware security toolchain for power trace capture, side-channel analysis, and glitching/fault-injection attacks on embedded devices and…
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 iceman1001/chameleonmini-rebooted
Chameleon Mini revE rebooted - Iceman Fork, the ChameleonMini is a versatile contactless smartcard emulator (NFC/RFID)
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 adamlaurie/rfidiot
Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
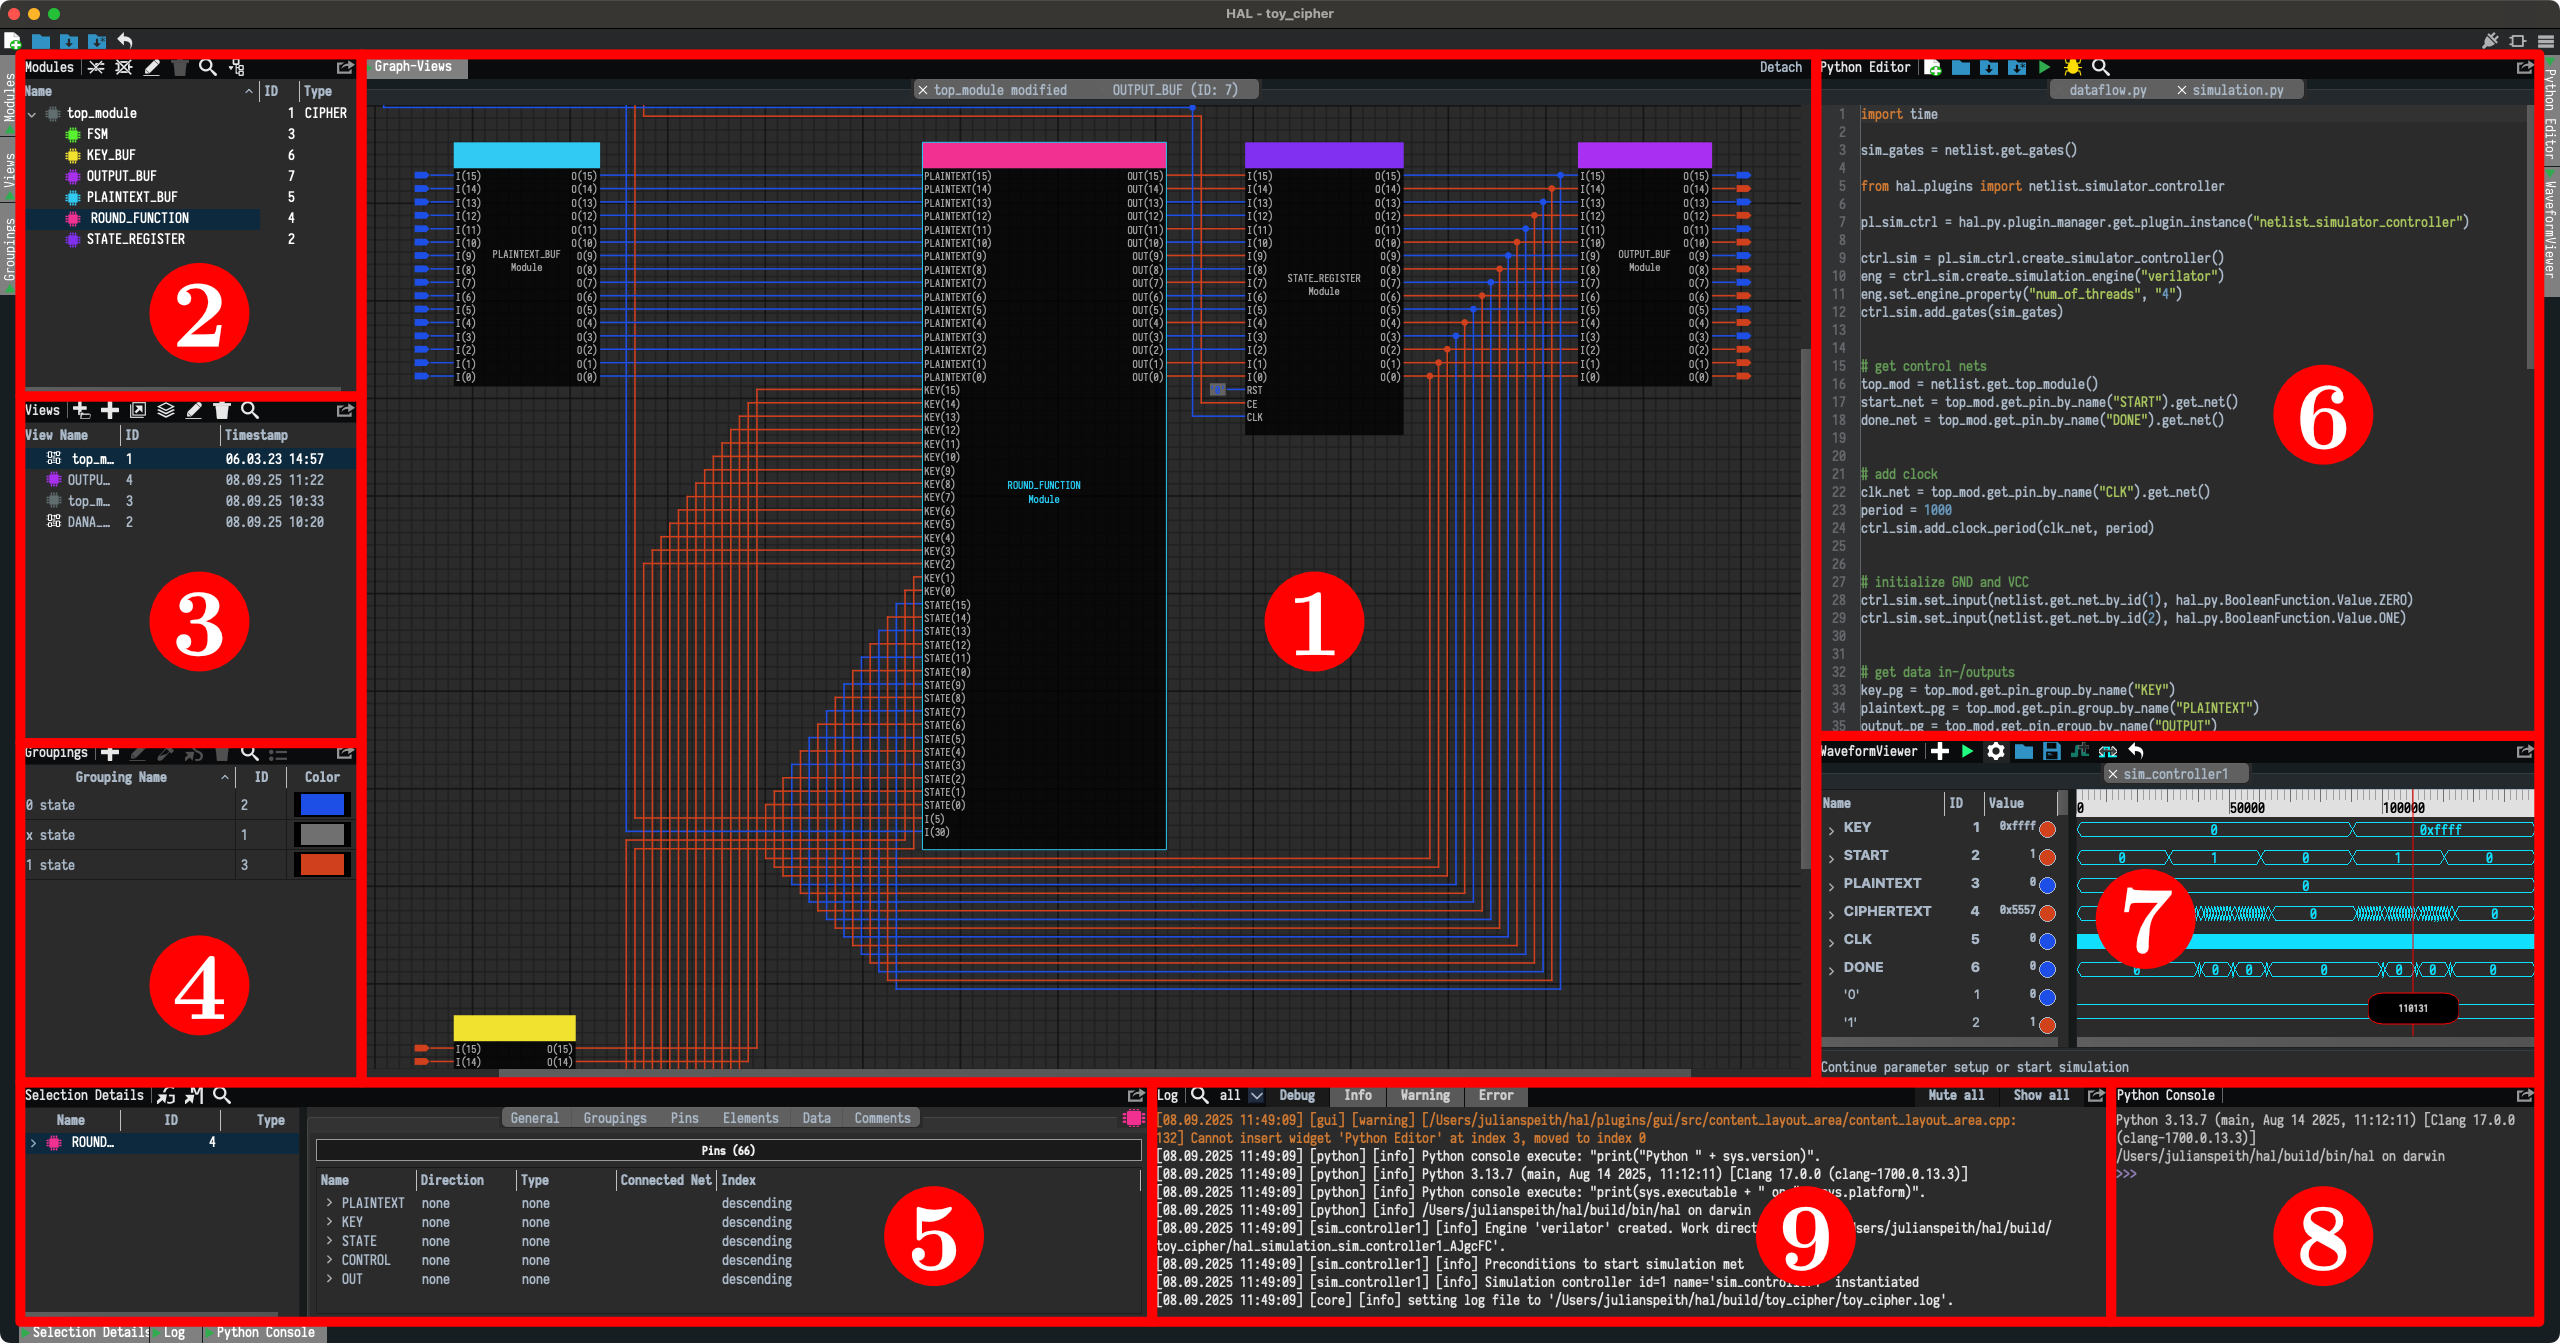 emsec/hal
HAL – The Hardware Analyzer
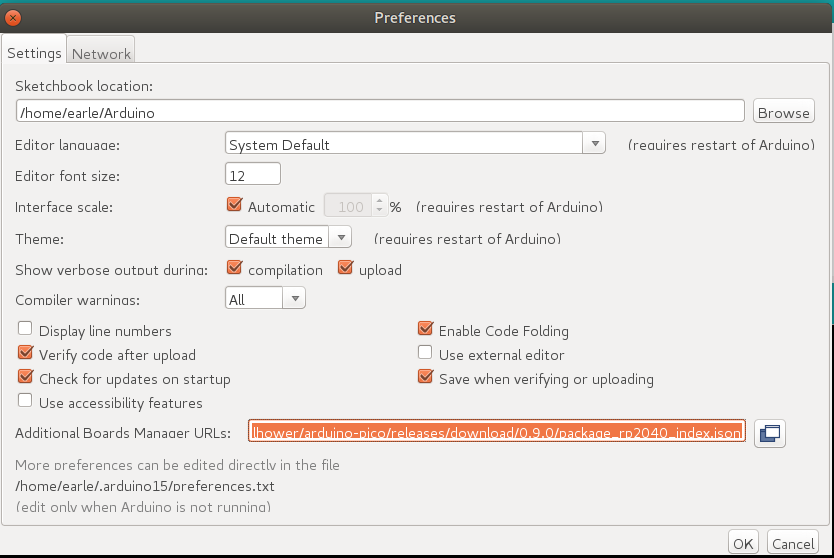 earlephilhower/arduino-pico
Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards
 openocd-org/openocd
Official OpenOCD Read-Only Mirror (no pull requests)
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…