
ghidralligator
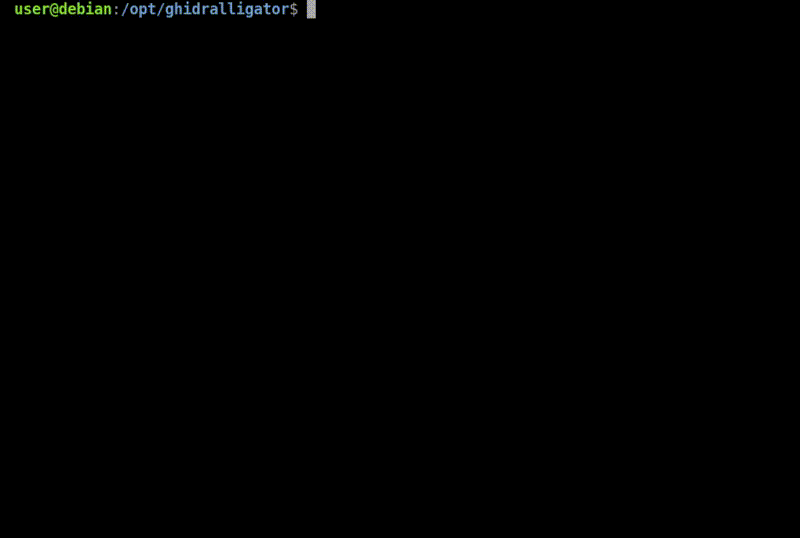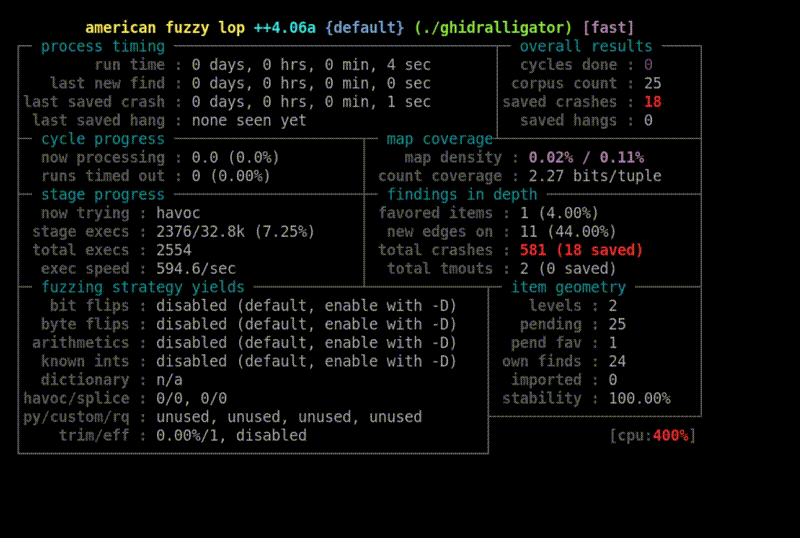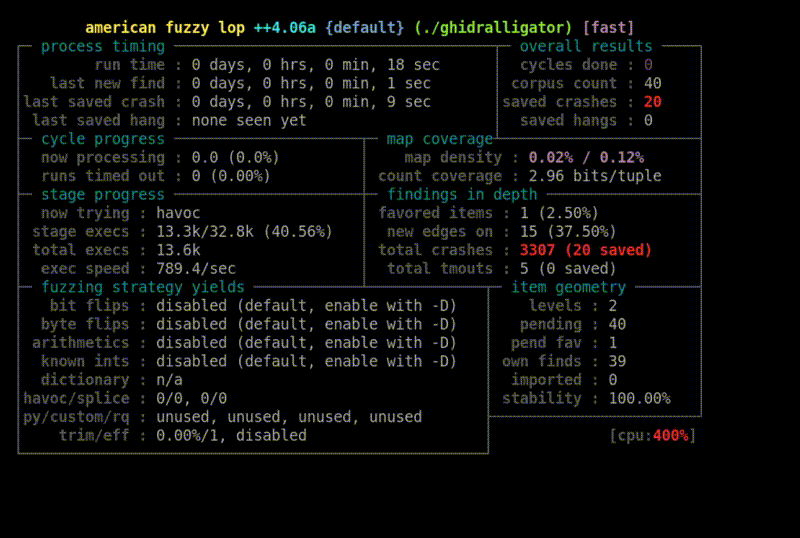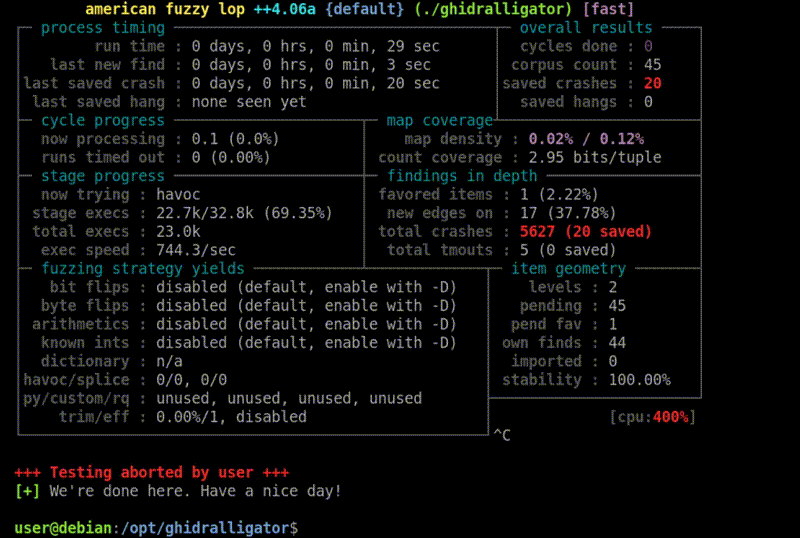
Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…

Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…

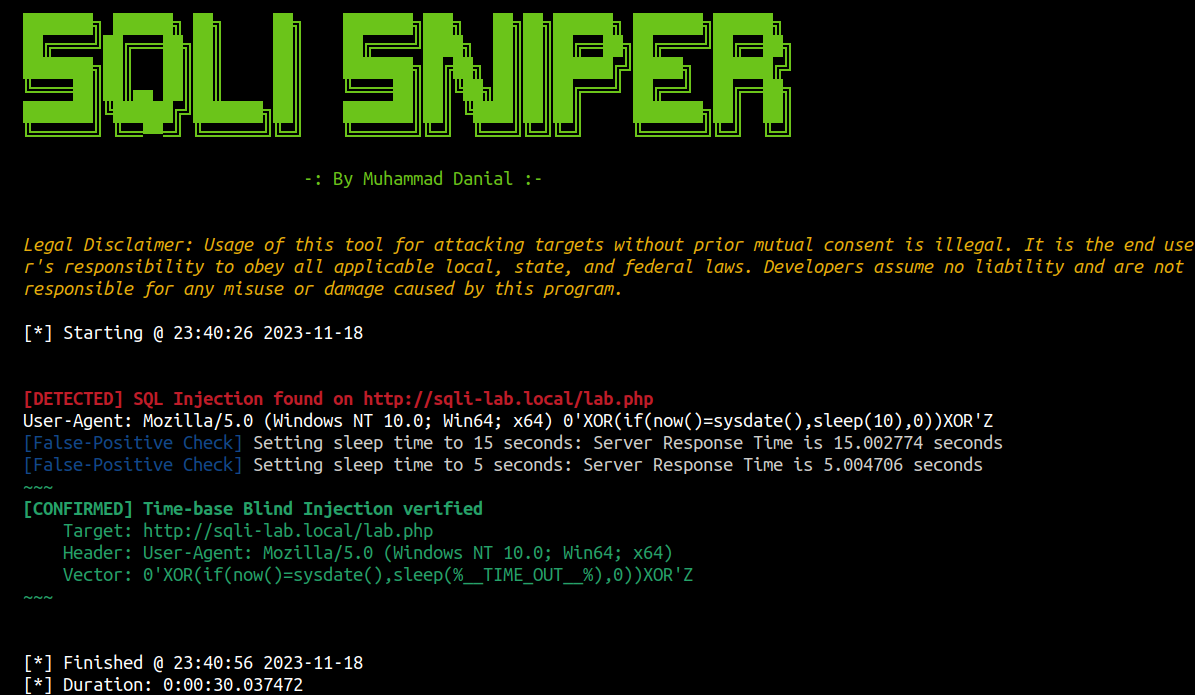
Advanced Time-based Blind SQL Injection fuzzer for HTTP Headers

CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…

Command Injection Web Fuzzer Script for mitmproxy

A structure-aware JSON fuzzer

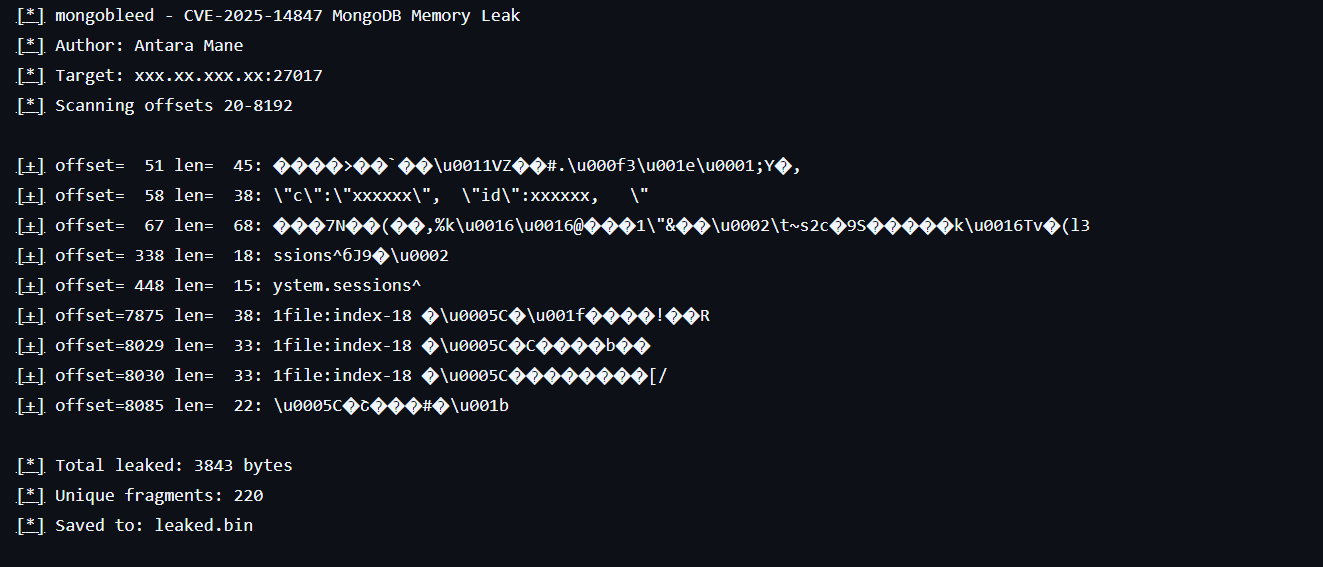
Educational research tool demonstrating CVE-2025-14847 memory disclosure in MongoDB's BSON decompression. Simulates bounds-checking failures and…

Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…

Proof-of-concept exploit for ImageMagick CVE-2017-15277 memory leak vulnerability, designed for use with the gifoeb fuzzing framework.

ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…

Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…

Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber Intelligence missions.

This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…

Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.

A hypervisor for fuzzing built with WHVP and Bochs

Proof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…

Library and CLI for mutating structured data (JSON, XML, X.509) to support grammar-based fuzzing, with multiple mutation strategies and integration…

🐢 Open-Source Evaluation & Testing library for LLM Agents

The fastest LoongArch sandbox