
B2R2
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
binary-analysisdynamic-analysis-sandboxingeducation+4
552
b2r2-org/b2r2B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 pepelux/sippts
Set of tools to audit SIP based VoIP Systems
 samsung/cotopaxi
Set of tools for security testing of Internet of Things devices using specific network IoT protocols
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
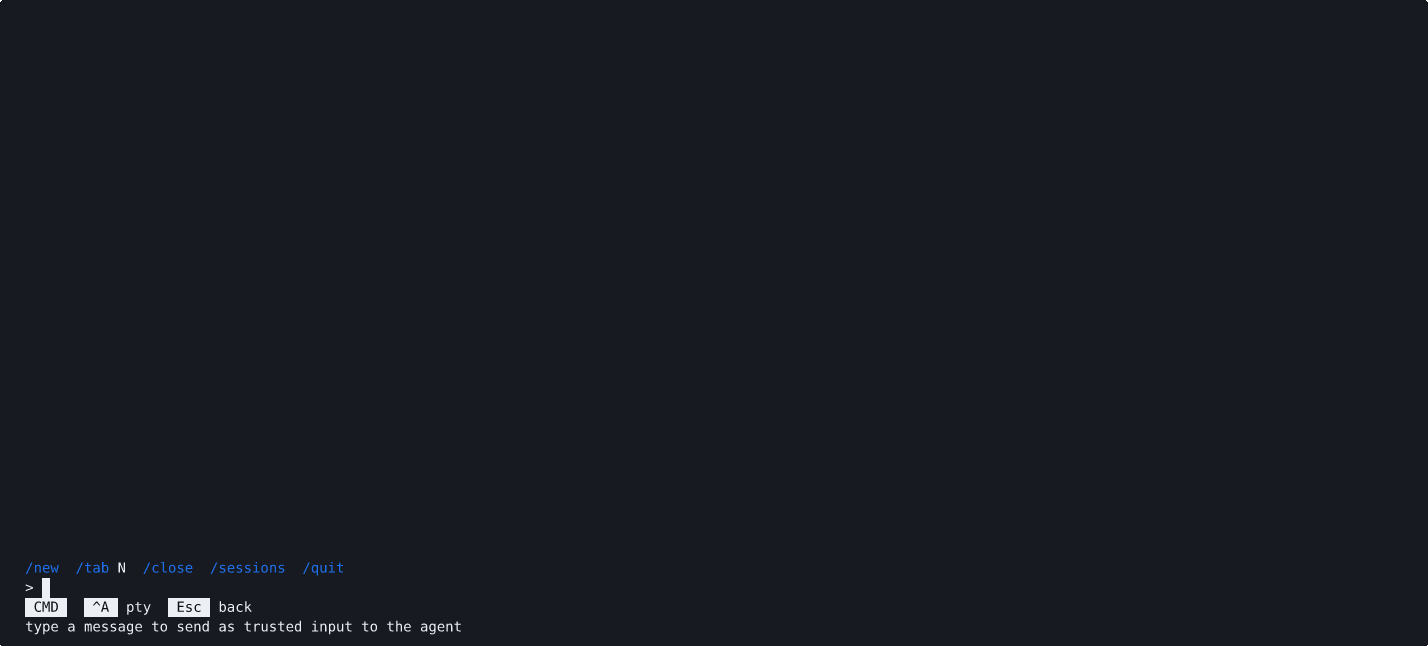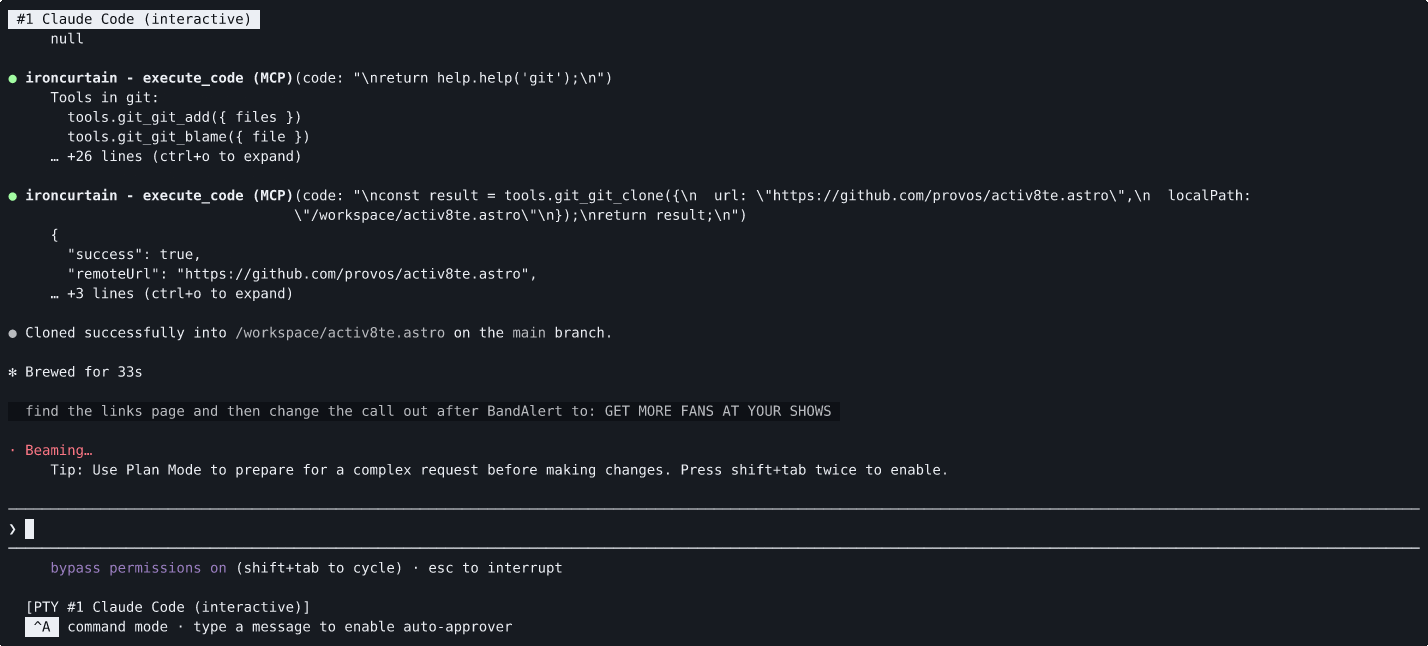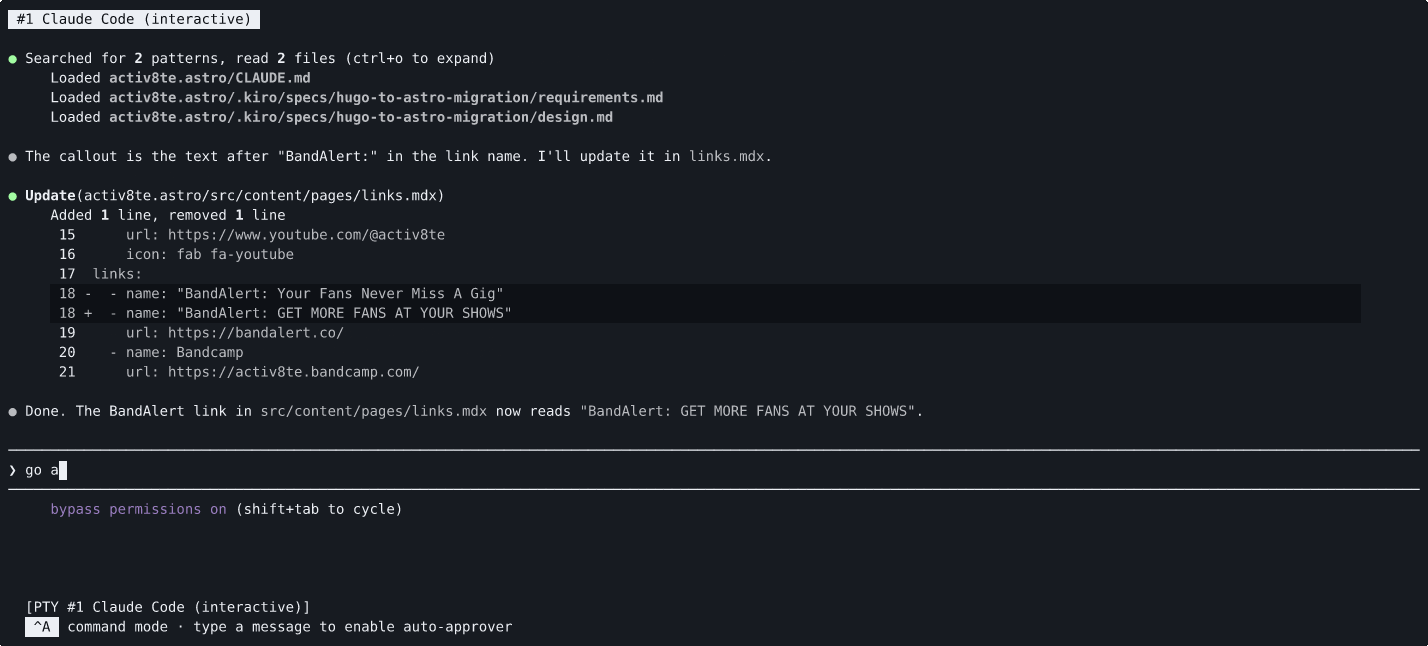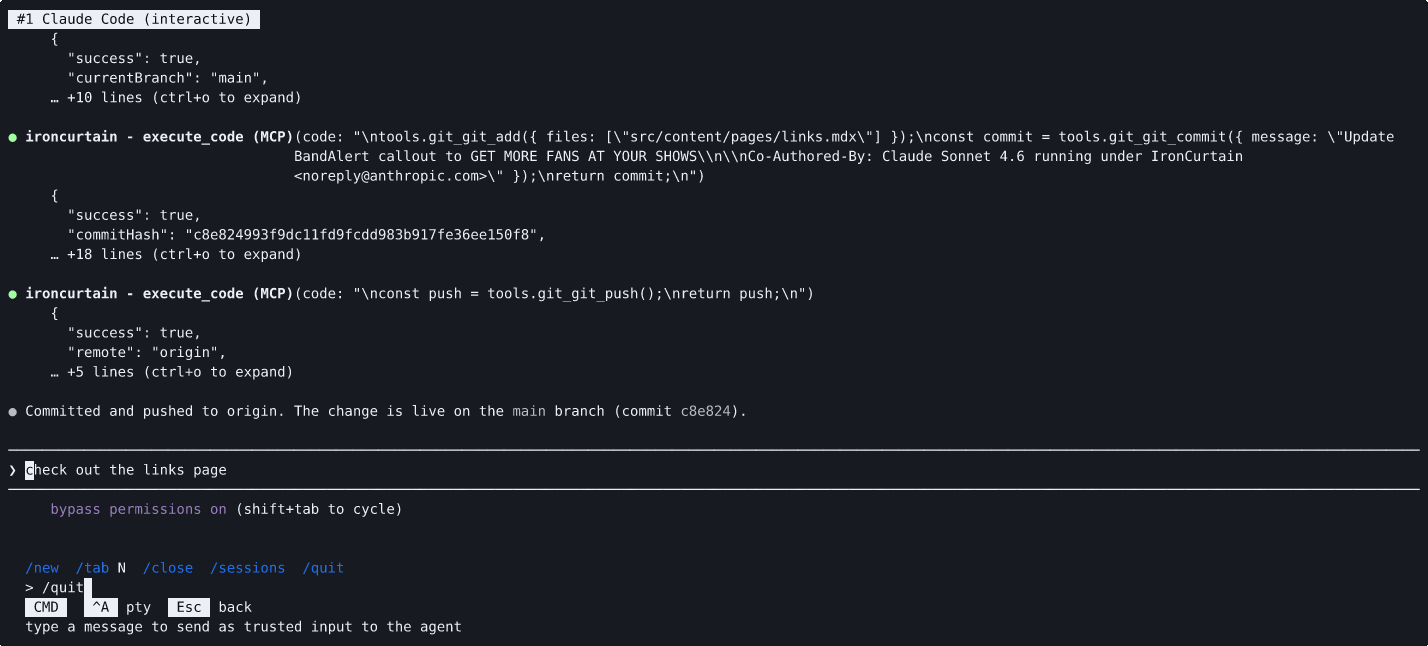 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)

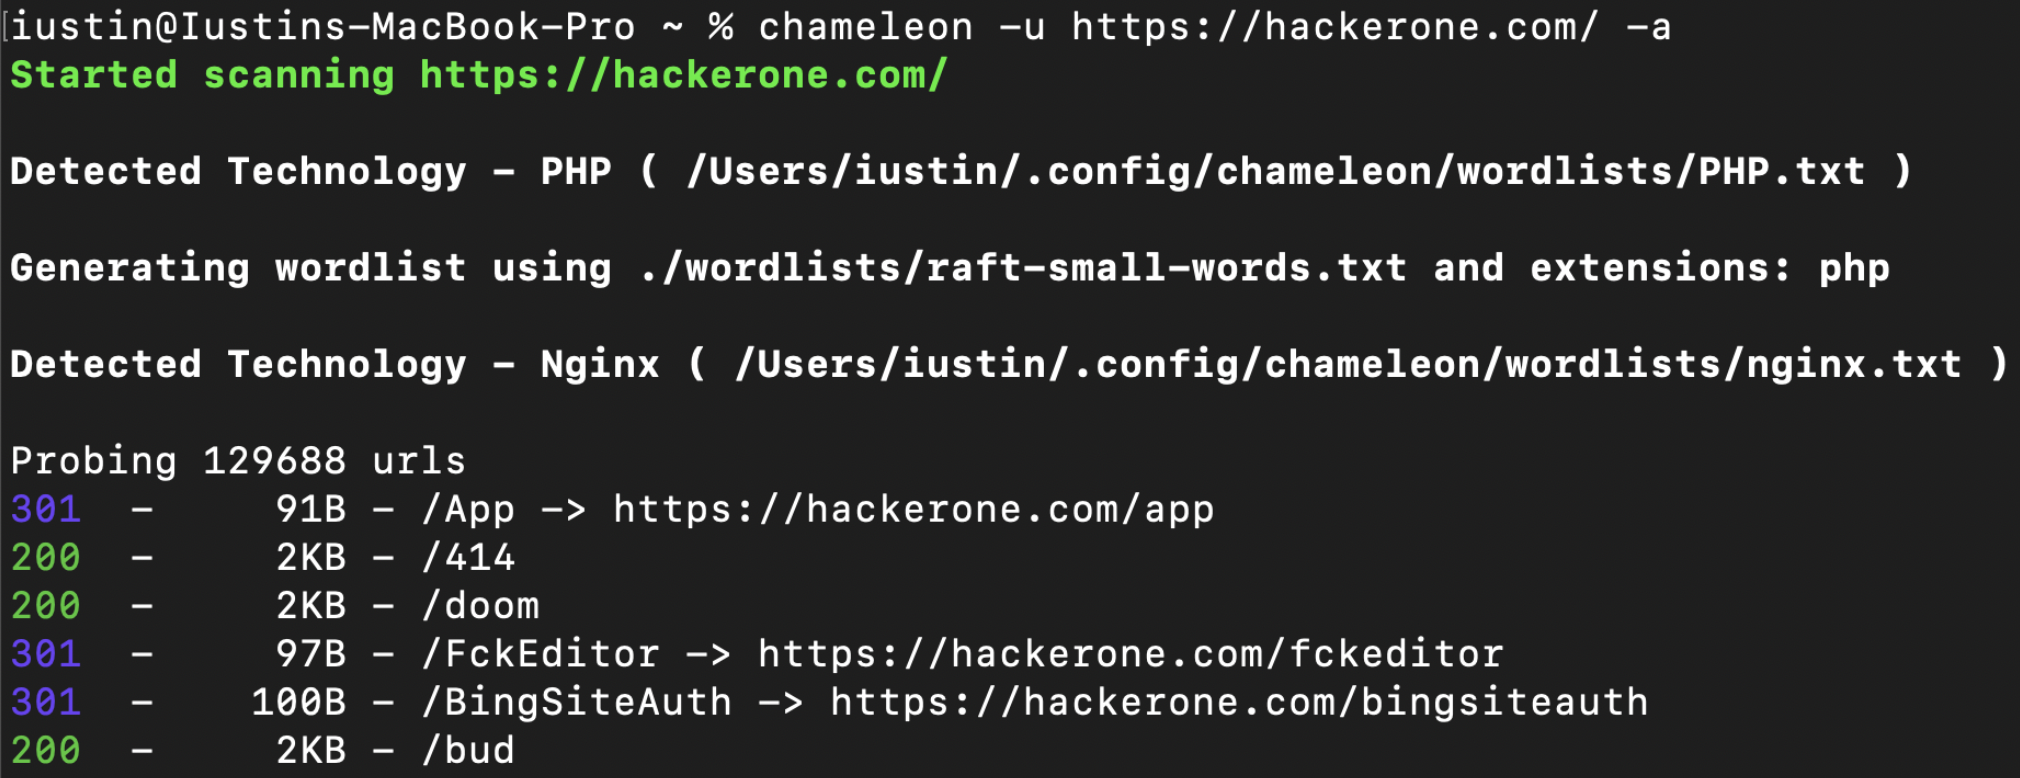 iustin24/chameleon
Technology-aware web content discovery scanner: detects Wappalyzer fingerprints, adapts wordlists/extensions, and performs fast directory bruteforce…
 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
 syss-research/wirebug
WireBug is a toolset for Voice-over-IP penetration testing
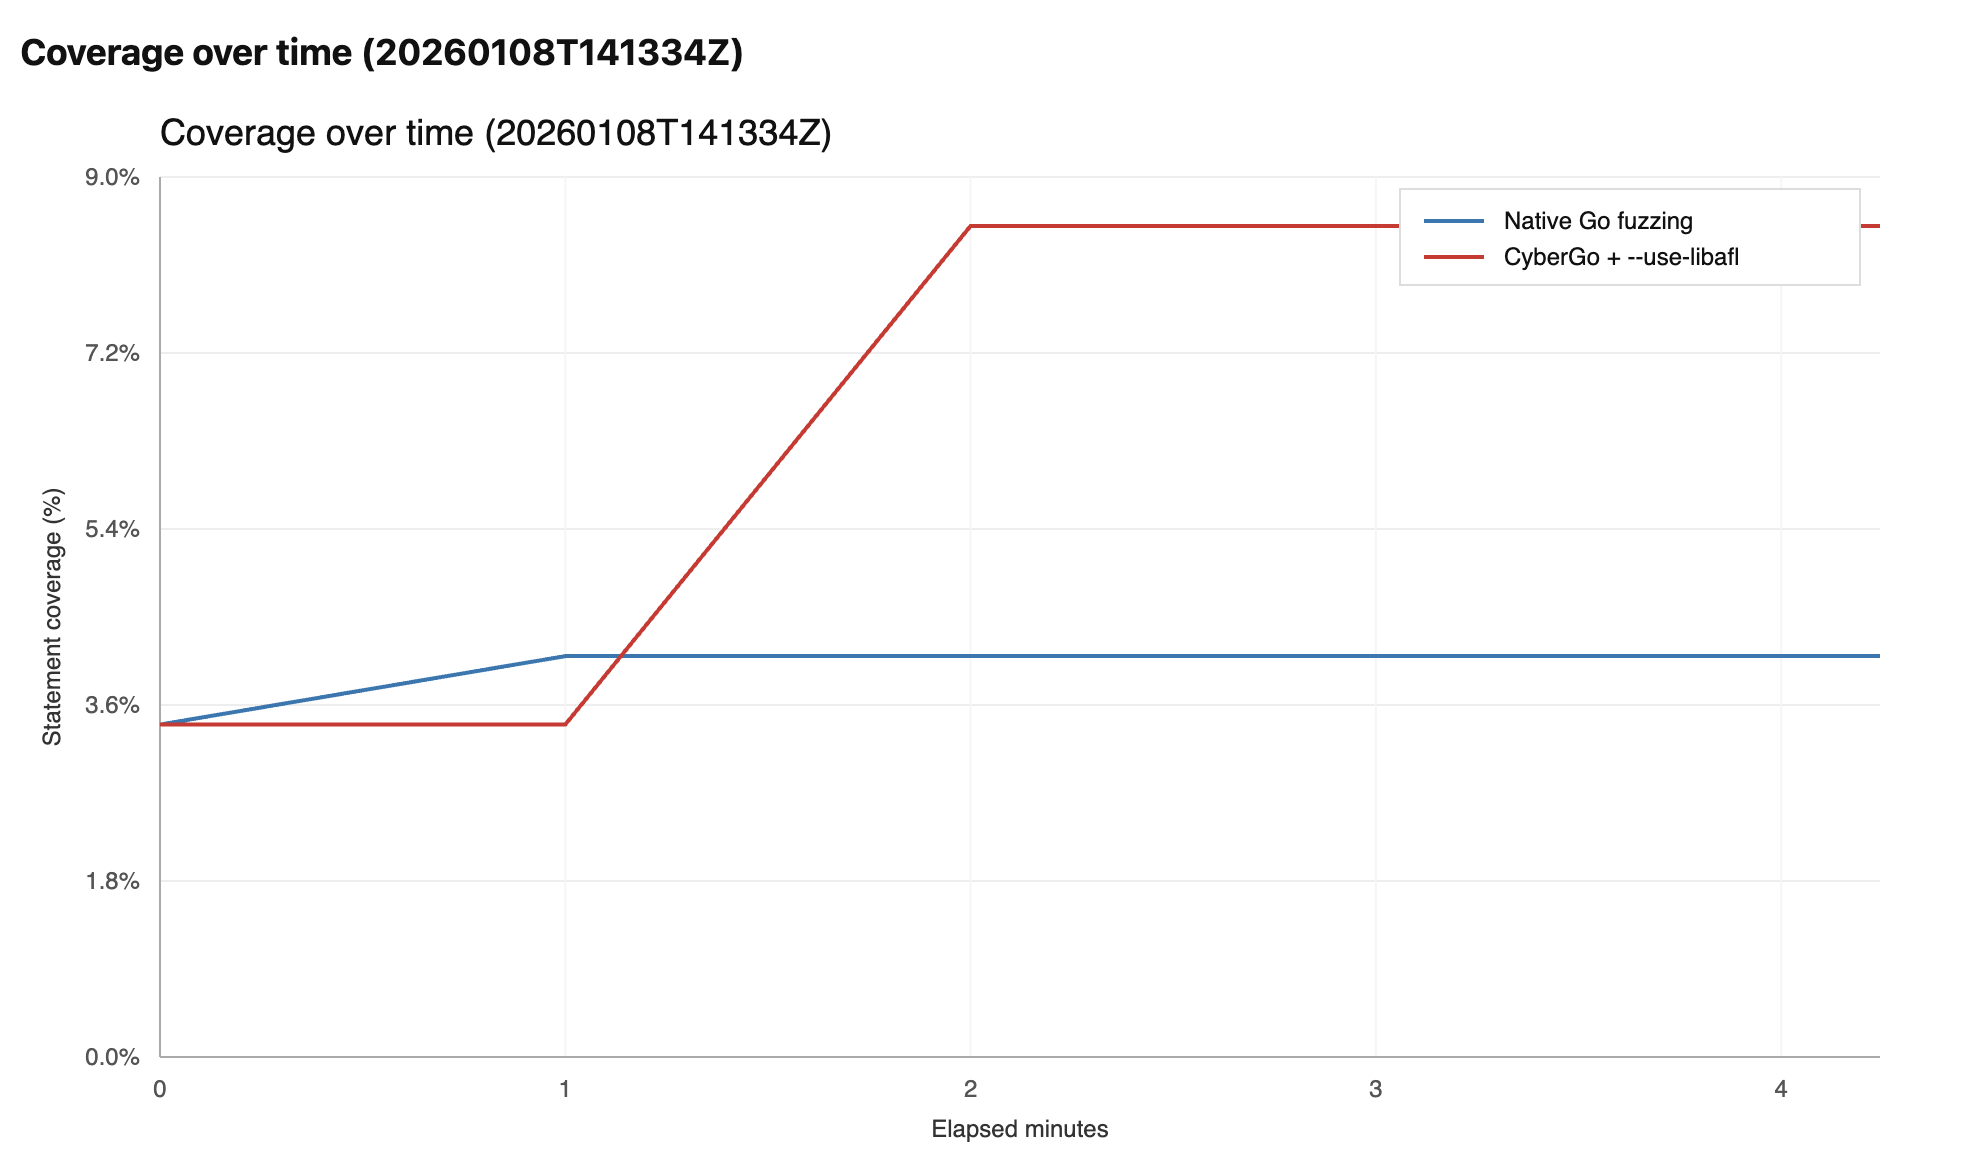 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.

 mk219533/cve-2010-1205
sample exploit of buffer overflow in libpng
 deepwoodssec/cve-2026-36522
Proof-of-concept exploit for CVE-2026-36522: unauthenticated NaN injection via MAVLink PARAM_SET in ArduPilot ArduPlane, causing DoS or silent…
 gogo2464/cve-2024-5124
Exploit for CVE-2024-5124 targeting ChuanhuChatGPT via TLS timing side-channel attack. Uses tlsfuzzer to perform character-by-character credential…
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
 k3vinlusec/r7000_httpd_bof_cve-2020-15416
Walkthrough of CVE-2020-15416 buffer overflow exploit for Netgear R7000 router, including QEMU user-mode debugging environment setup and detailed…
 googleprojectzero/brokentype
TrueType and OpenType font fuzzing toolset