
CVE-2025-30216-PoC
 oliviaisntcringe/cve-2025-30216-poc
PoC
binary-exploitationembedded-systems-securityexploitation+3
oliviaisntcringe/cve-2025-30216-pocPoC
 trinadh465/platform_external_libvpx_v1.8.0_cve-2023-5217
Patched libvpx codebase addressing CVE-2023-5217 with sanitizer support and cross-platform build configurations for secure VP8/VP9 encoding.
 ikkisoft/bradamsa
Burp Suite extension to generate Intruder payloads using Radamsa
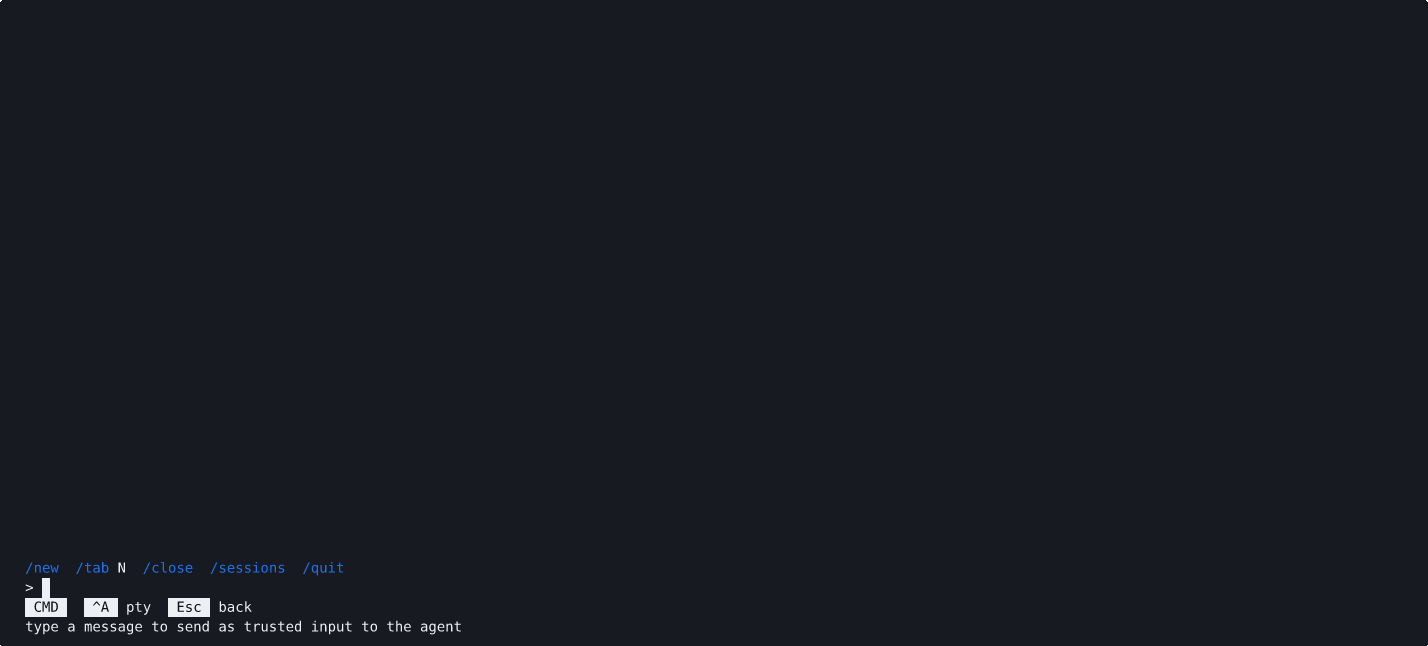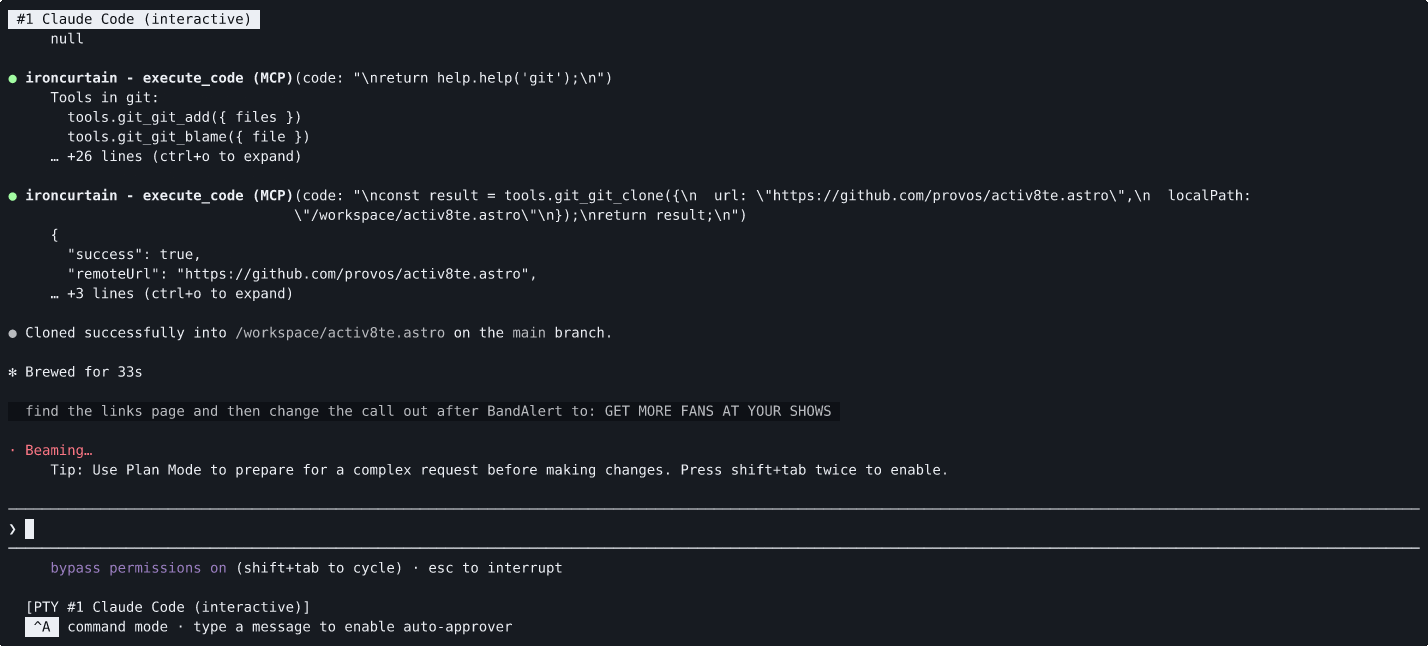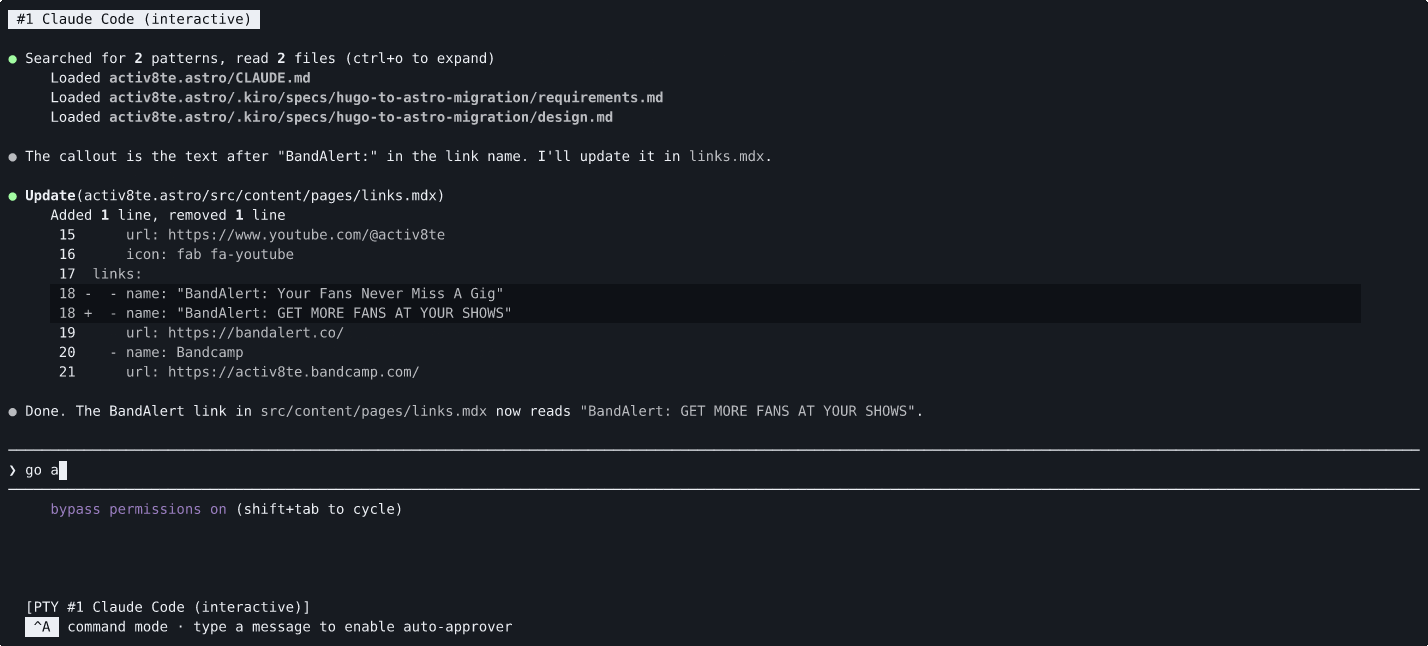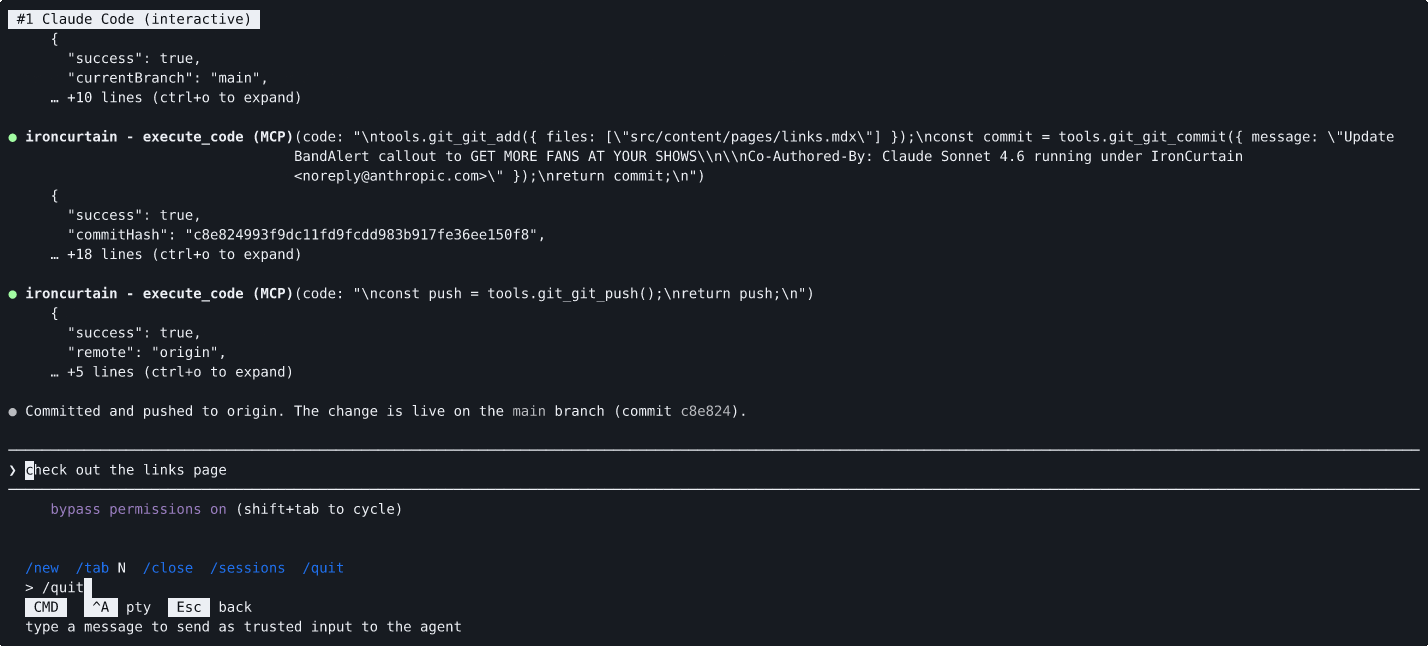 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
 libssh/libssh-mirror
C library implementing the SSH protocol for secure remote access, authentication, and encrypted communication. Includes fuzzing support via OSS-Fuzz…
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
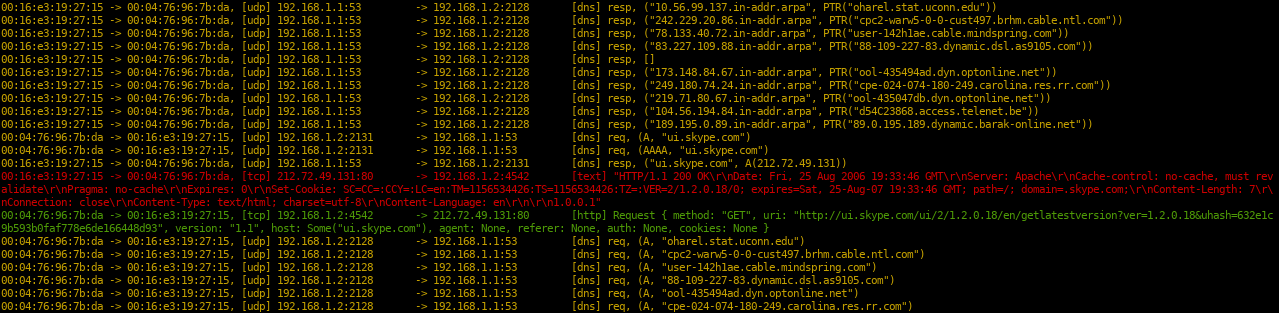 kpcyrd/sniffglue
Secure multithreaded packet sniffer
 puglia-ryan/s-v-project-implementation-of-cve-2015-3256
Reproducible crash proof-of-concept for CVE-2015-3456 (VENOM) targeting QEMU's virtual floppy disk controller. Demonstrates guest-controlled writes…
 s0duku/cve-2022-31705
CVE-2022-31705 (Geekpwn 2022 Vmware EHCI OOB) POC
 harshrajsinghania/cve-2026-90782-s2opc-status-clobber
Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
 freax13/cve-2023-20573-poc
Proof-of-concept demonstrating CVE-2023-20573: a hardware vulnerability in AMD SEV-SNP that allows exception reinjection suppression in KVM, enabling…
 bazad/iofirewirefamily-overflow
CVE-2016-7608: Buffer overflow in IOFireWireFamily.
 watsa01/cve-2019-5688
POC Code for the NVFLASH driver
 chunzhennn/cve-2023-21987-poc
Proof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…
 whypet/cve-2023-31320
DoS vulnerability in AMD driver that corrupts the display.
 0xbbdd/cve-2026-33317
Proof-of-concept for CVE-2026-33317, an out-of-bounds write in OP-TEE PKCS#11 TA, demonstrating Secure World heap corruption via a malformed…
 577industries/aegisgraph
AegisGraph: graph-based application-layer assessment evidence platform for Secure Messaging Applications (SMAs). DARPA ASEMA HR0011SB20254-12 Tier 3…