
netzob
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
binary-analysisfuzzingnetwork-security+1
833
netzob/netzobOpen-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
 cobbbex/cisco-asa-vulnerability-research
Systematic reverse engineering of Cisco ASA's lina binary to discover and analyze memory corruption vulnerabilities, including CVE-2025-20333 and…
 ifygecko/cve-2023-30226
Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…
 keensecuritylab/binabsinspector
Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…

 m4b/goblin
An impish, cross-platform binary parsing crate, written in Rust
 gjduck/e9patch
A powerful static binary rewriting tool
 schutzwerk/canalyzat0r
Security analysis toolkit for proprietary car protocols
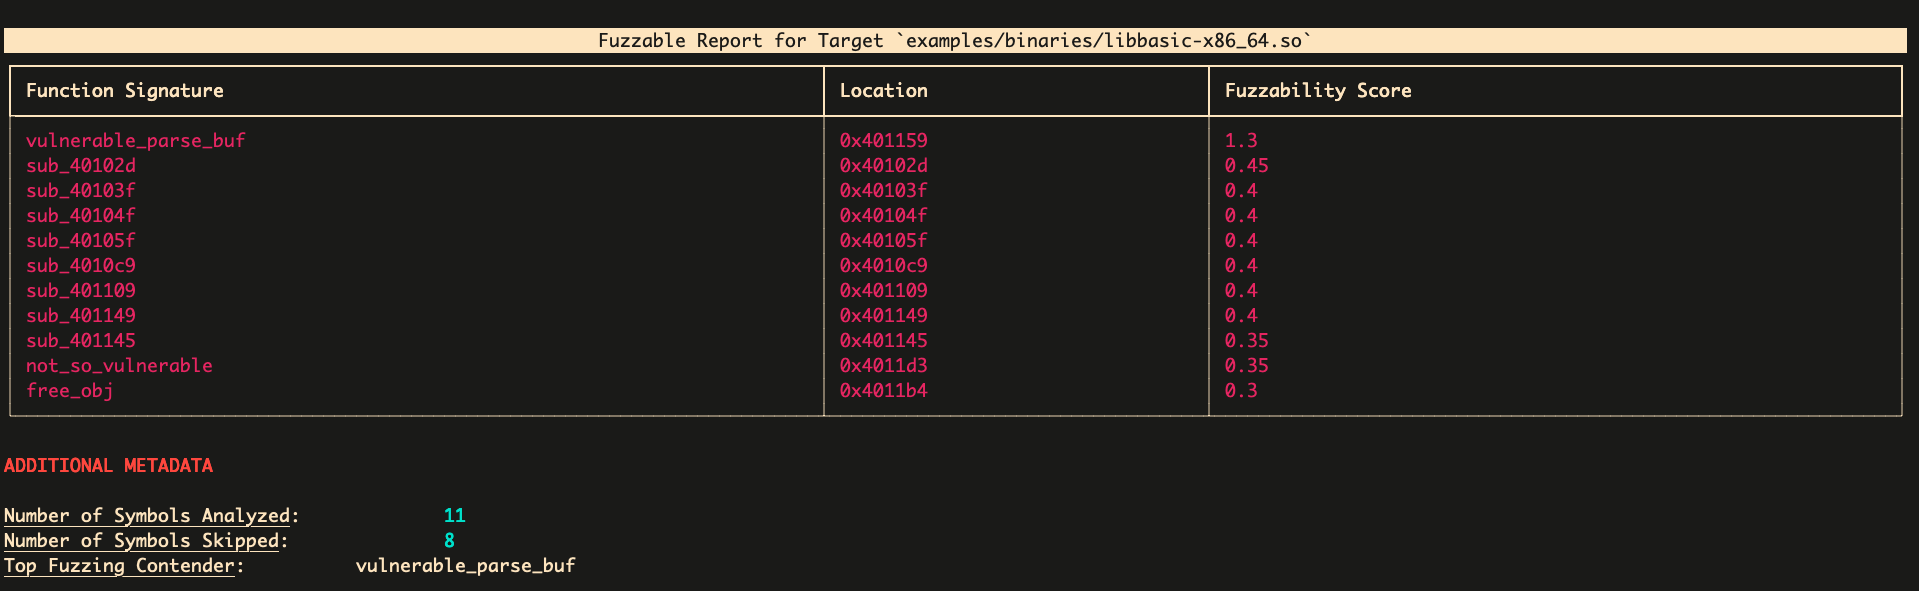 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 infobyte/pyrmax
Decoder/encoder for Ubiquiti AirMAX wireless protocol frames; parse pcap/live captures, discover devices, scan for vulnerable firmware, craft…
 spiralbl0ck/cve-2022-3653
CVE-2022-3653 just the c++ component in Vulkan for later study
 fm0ss/cve-2025-9951-ffmpeg-jp2-poc
Proof-of-concept for CVE-2025-9951 demonstrating controlled callback execution in FFmpeg via JPEG 2000 component-mapping mismatch. Includes write-up,…
 probnotanexploiter/cve-2024-26170-extended
researching for CVE-2024-26170 or cimfs.sys to find overflows or bugs that is considered a zero-day
 khoatran107/cve-2025-38001
C-based proof-of-concept exploit for CVE-2025-38001, demonstrating vulnerability exploitation and code analysis for security research.
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 tronciuvlad/cve-2024-26475
An issue in radareorg radare2 v.0.9.7 through v.5.8.6 and fixed in v.5.8.8 allows a local attacker to cause a denial of service via the…