
lazyrecon
 storenth/lazyrecon
Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.
fuzzingosintpenetration-testing+4
storenth/lazyreconWicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.
 cleov2/debuggable-app-exploit
CVE-2024-31317 Debuggable App Exploit
 amossys/memitm
Tool to make in memory man in the middle
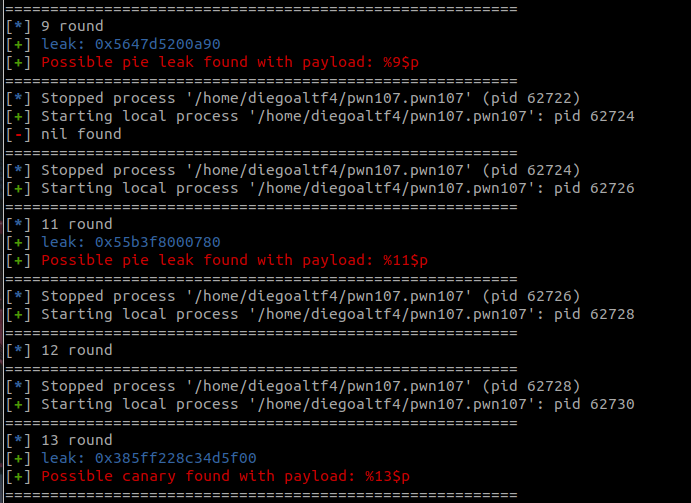 diego-altf4/glufs
Automated format string vulnerability exploitation tool for discovering stack, PIE, and canary leaks with flag search capability via %s or %p…
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
 noxxi/mime-is-broken
Test cases for broken MIME and tools to generate and process these
 puglia-ryan/s-v-project-implementation-of-cve-2015-3256
Reproducible crash proof-of-concept for CVE-2015-3456 (VENOM) targeting QEMU's virtual floppy disk controller. Demonstrates guest-controlled writes…
 almkuznetsov/cve-2024-1441
Reproduces fuzzing and crash analysis for CVE-2024-1441 using AFL++ and CASR, with detailed setup and commands for libvirt.
 mfthomps/resim
Reverse engineering software using a full system simulator
 internon/inter-recon
Script to perform automatic initial web and vulnerability recon
 sneakynachos/cve-2026-85048-the-gpu-died
Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 googleprojectzero/sockfuzzer
Coverage-guided kernel fuzzing framework that runs XNU as a userspace library and discovers vulnerabilities across BSD, Mach, virtual memory, and…
 ttdennis/fpicker
Frida-based in-process fuzzing suite with AFL++ proxy, standalone active/passive modes, and shared memory communication for high-performance…
 seemoo-lab/toothpicker
Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…
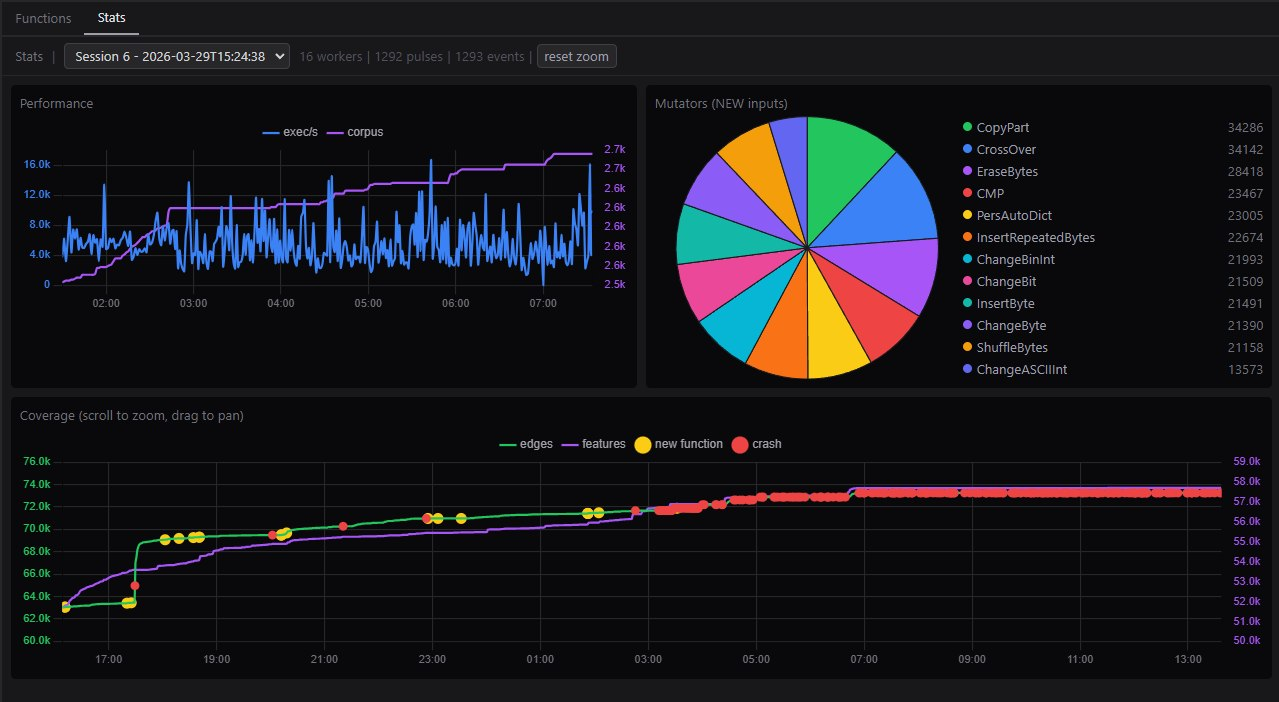 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 starrynightsecurity/cve-2025-54574-squid-heap-buffer-overflow
Vulnerability Found on Squid Proxy.