
crlfuzz
 dwisiswant0/crlfuzz
A fast tool to scan CRLF vulnerability written in Go
fuzzingvulnerability-scannersweb-security
dwisiswant0/crlfuzzA fast tool to scan CRLF vulnerability written in Go
 dwisiswant0/ppfuzz
A fast tool to scan client-side prototype pollution vulnerability written in Rust. 🦀
 damian89/extended-ssrf-search
Smart ssrf scanner using different methods like parameter brute forcing in post and get...
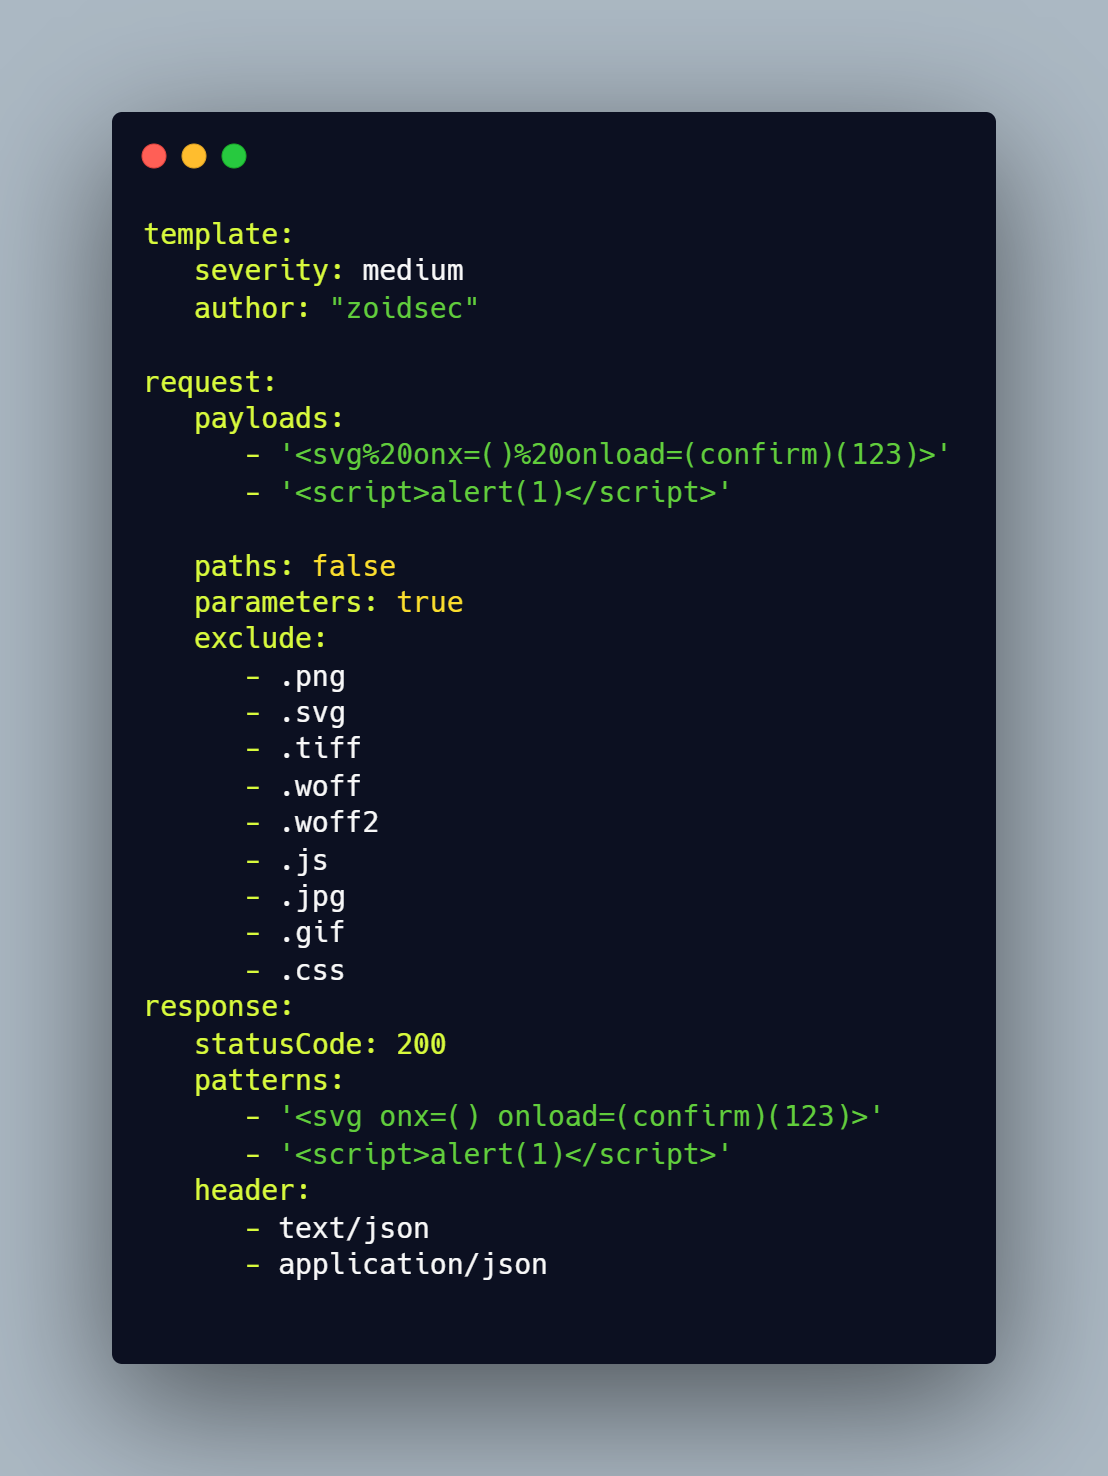 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
 rk-000/log4j_scan_advance
A fully automated, accurate, and extensive scanner for finding log4j RCE CVE-2021-44228
 khalidhusain786/scannerweb
Python3 vulnerability scanner that fuzzes all URLs of a target website and scans them for web vulnerabilities, with optional GoBuster integration for…
 devanshbatham/openredirex
A fuzzer for detecting open redirect vulnerabilities
 lc/theftfuzzer
TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.
 danialhalo/sqlisniper
Advanced Time-based Blind SQL Injection fuzzer for HTTP Headers
 brum3ns/firefly
High-performance black-box fuzzer for web applications with built-in payload engine, request verification, tampering, encoding, and advanced…
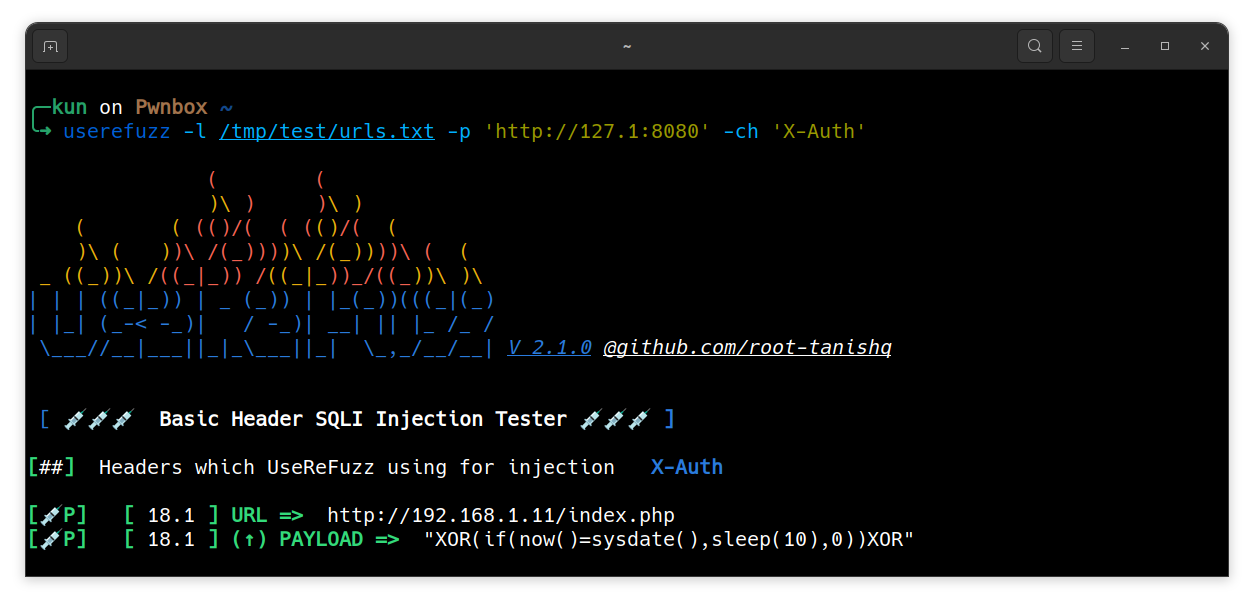 root-tanishq/userefuzz
User-Agent , X-Forwarded-For and Referer SQLI Fuzzer
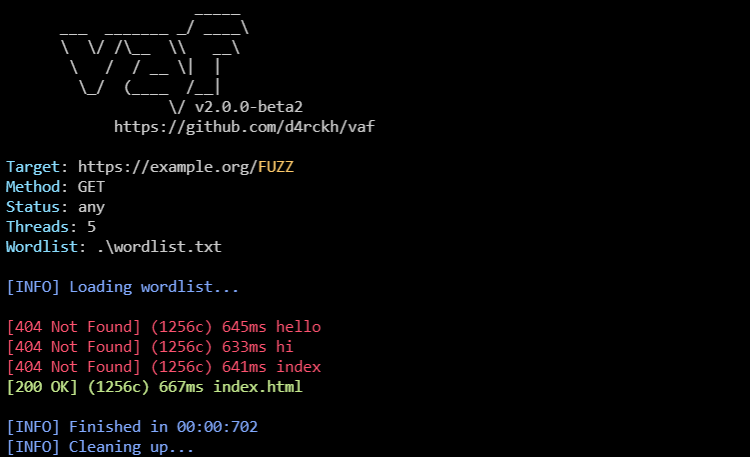 andreiverse/vaf
Multi-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…
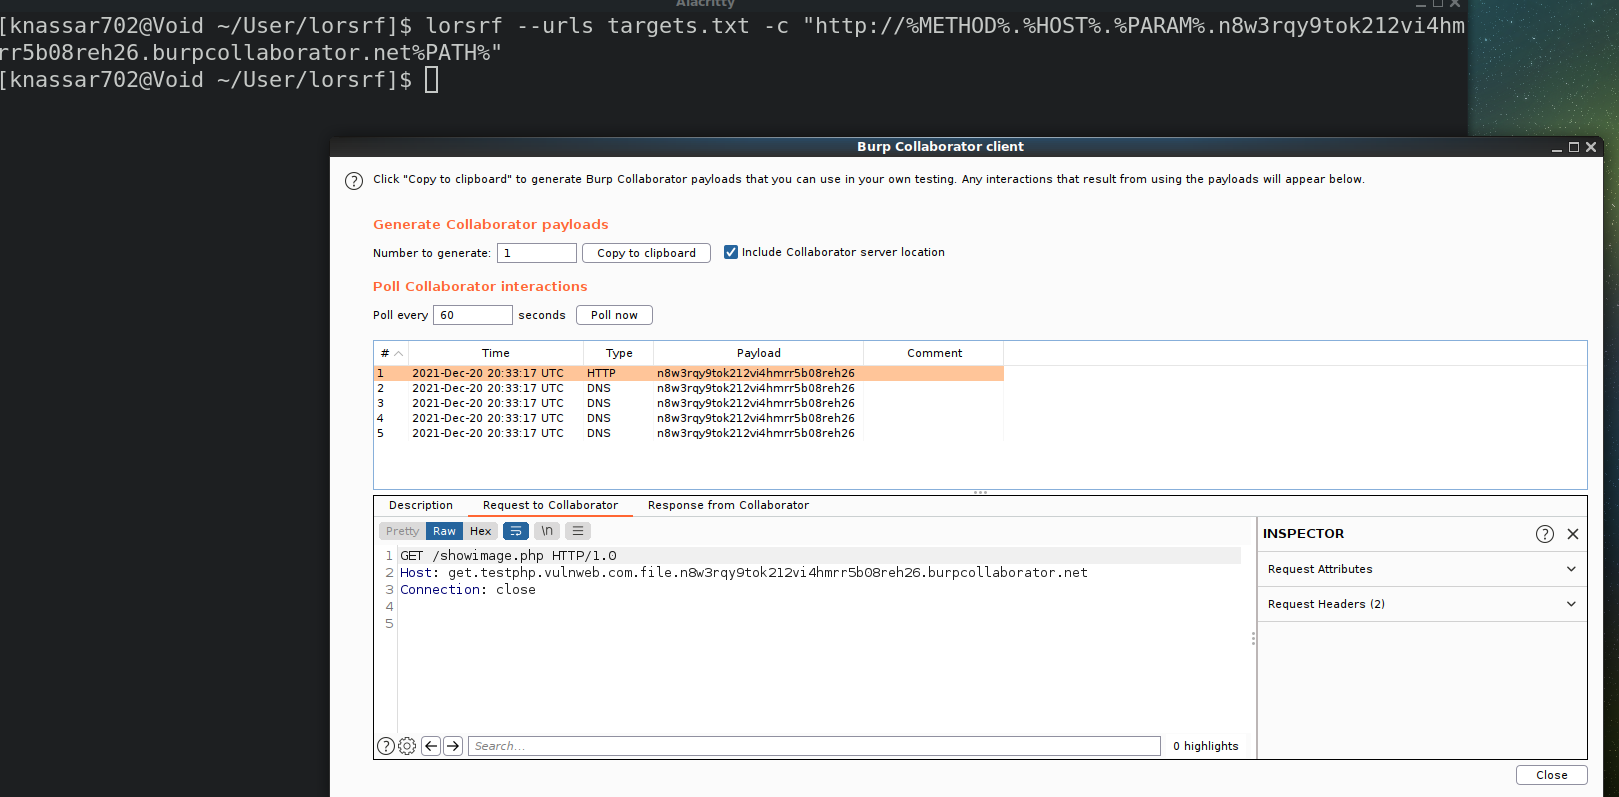 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
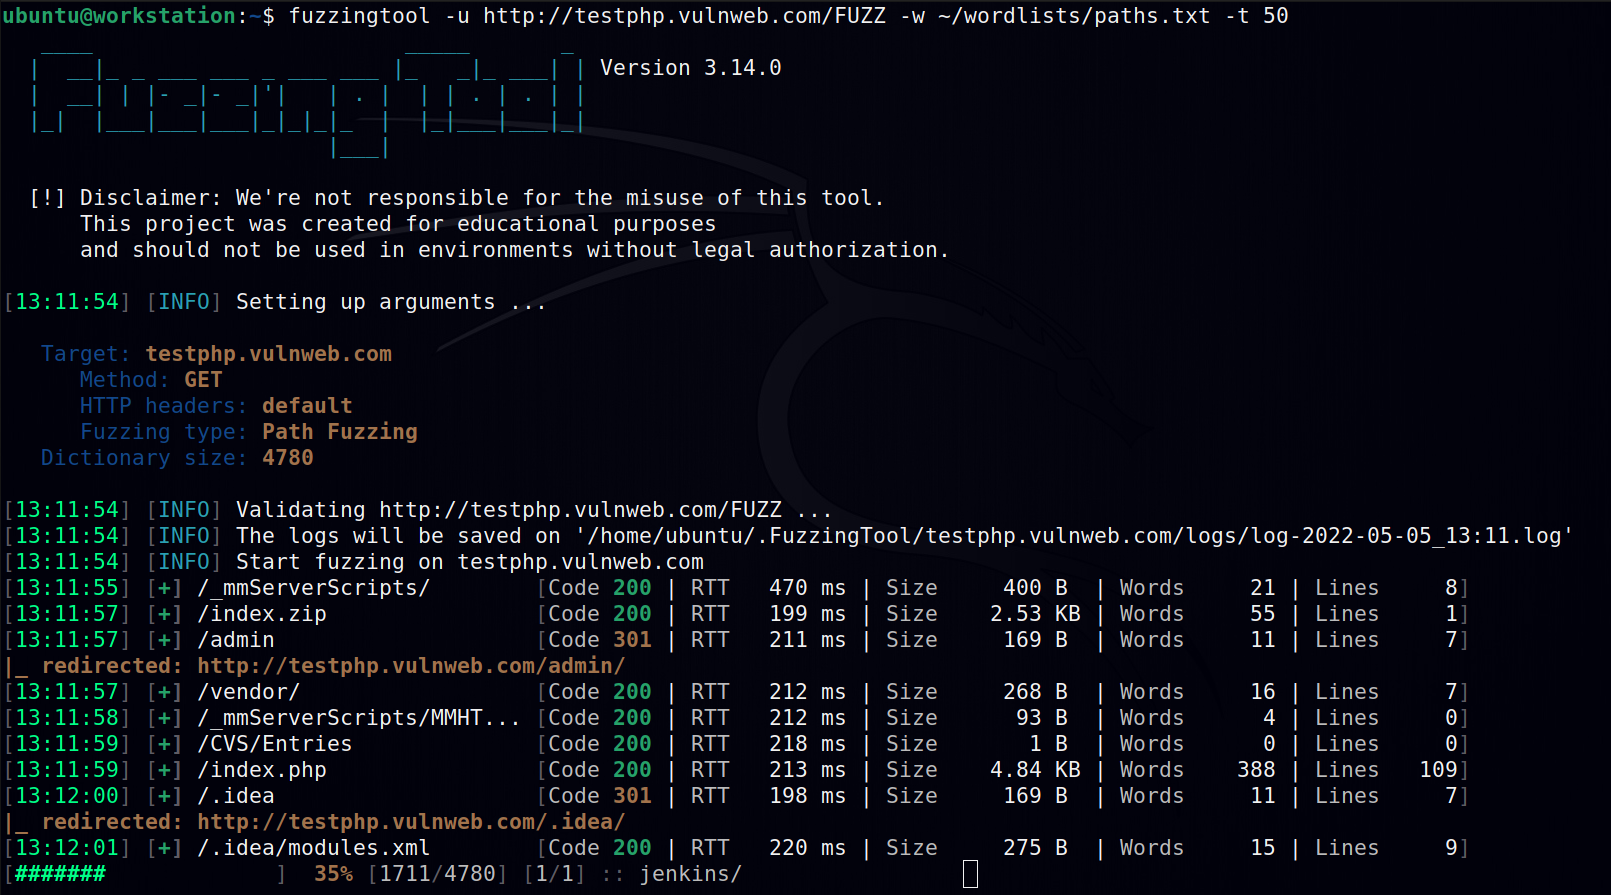 nescau-ufla/fuzzingtool
Software for fuzzing, used on web application pentestings.
 ryandamour/ssrfuzz
SSRFuzz is a tool to find Server Side Request Forgery vulnerabilities, with CRLF chaining capabilities
 hakaioffsec/navgix
Multi-threaded Go tool to detect nginx alias traversal vulnerabilities using heuristic and brute-force techniques for identifying vulnerable…
 ethicalhackingplayground/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 holo-routing/holo
Rust-based routing protocol suite implementing BGP, OSPF, IS-IS, RIP, and VRRP with YANG-modeled configuration, gNMI/gRPC automation, and built-in…