

AI_HACKING
 spiralbl0ck/ai_hacking
Collection of CVE(work) on tenserflow binary pwning it
ai-securitybinary-exploitationexploitation+3
spiralbl0ck/ai_hackingCollection of CVE(work) on tenserflow binary pwning it
 ashemery/exploitation-course
Offensive Software Exploitation Course
 0x4ndy/clif
clif is a command-line interface (CLI) application fuzzer, pretty much what wfuzz or ffuf are for web. It was inspired by sudo vulnerability…
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 amossys/memitm
Tool to make in memory man in the middle
 airbus-seclab/gustave
GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…
 mgeeky/penetration-testing-tools
A collection of more than 170+ tools, scripts, cheatsheets and other loots that I've developed over years for Red Teaming/Pentesting/IT Security…
 rub-nds/ws-attacker
WS-Attacker is a modular framework for web services penetration testing. It is developed by the Chair of Network and Data Security, Ruhr University…
 hardik05/damn_vulnerable_c_program
An example C program which contains vulnerable code for common types of vulnerabilities. It can be used to show fuzzing concepts.
 hugsy/cfb
ProcMon-style IRP monitor for Windows drivers. Captures and logs I/O Request Packets via a kernel driver and user-land broker, outputting JSON for…
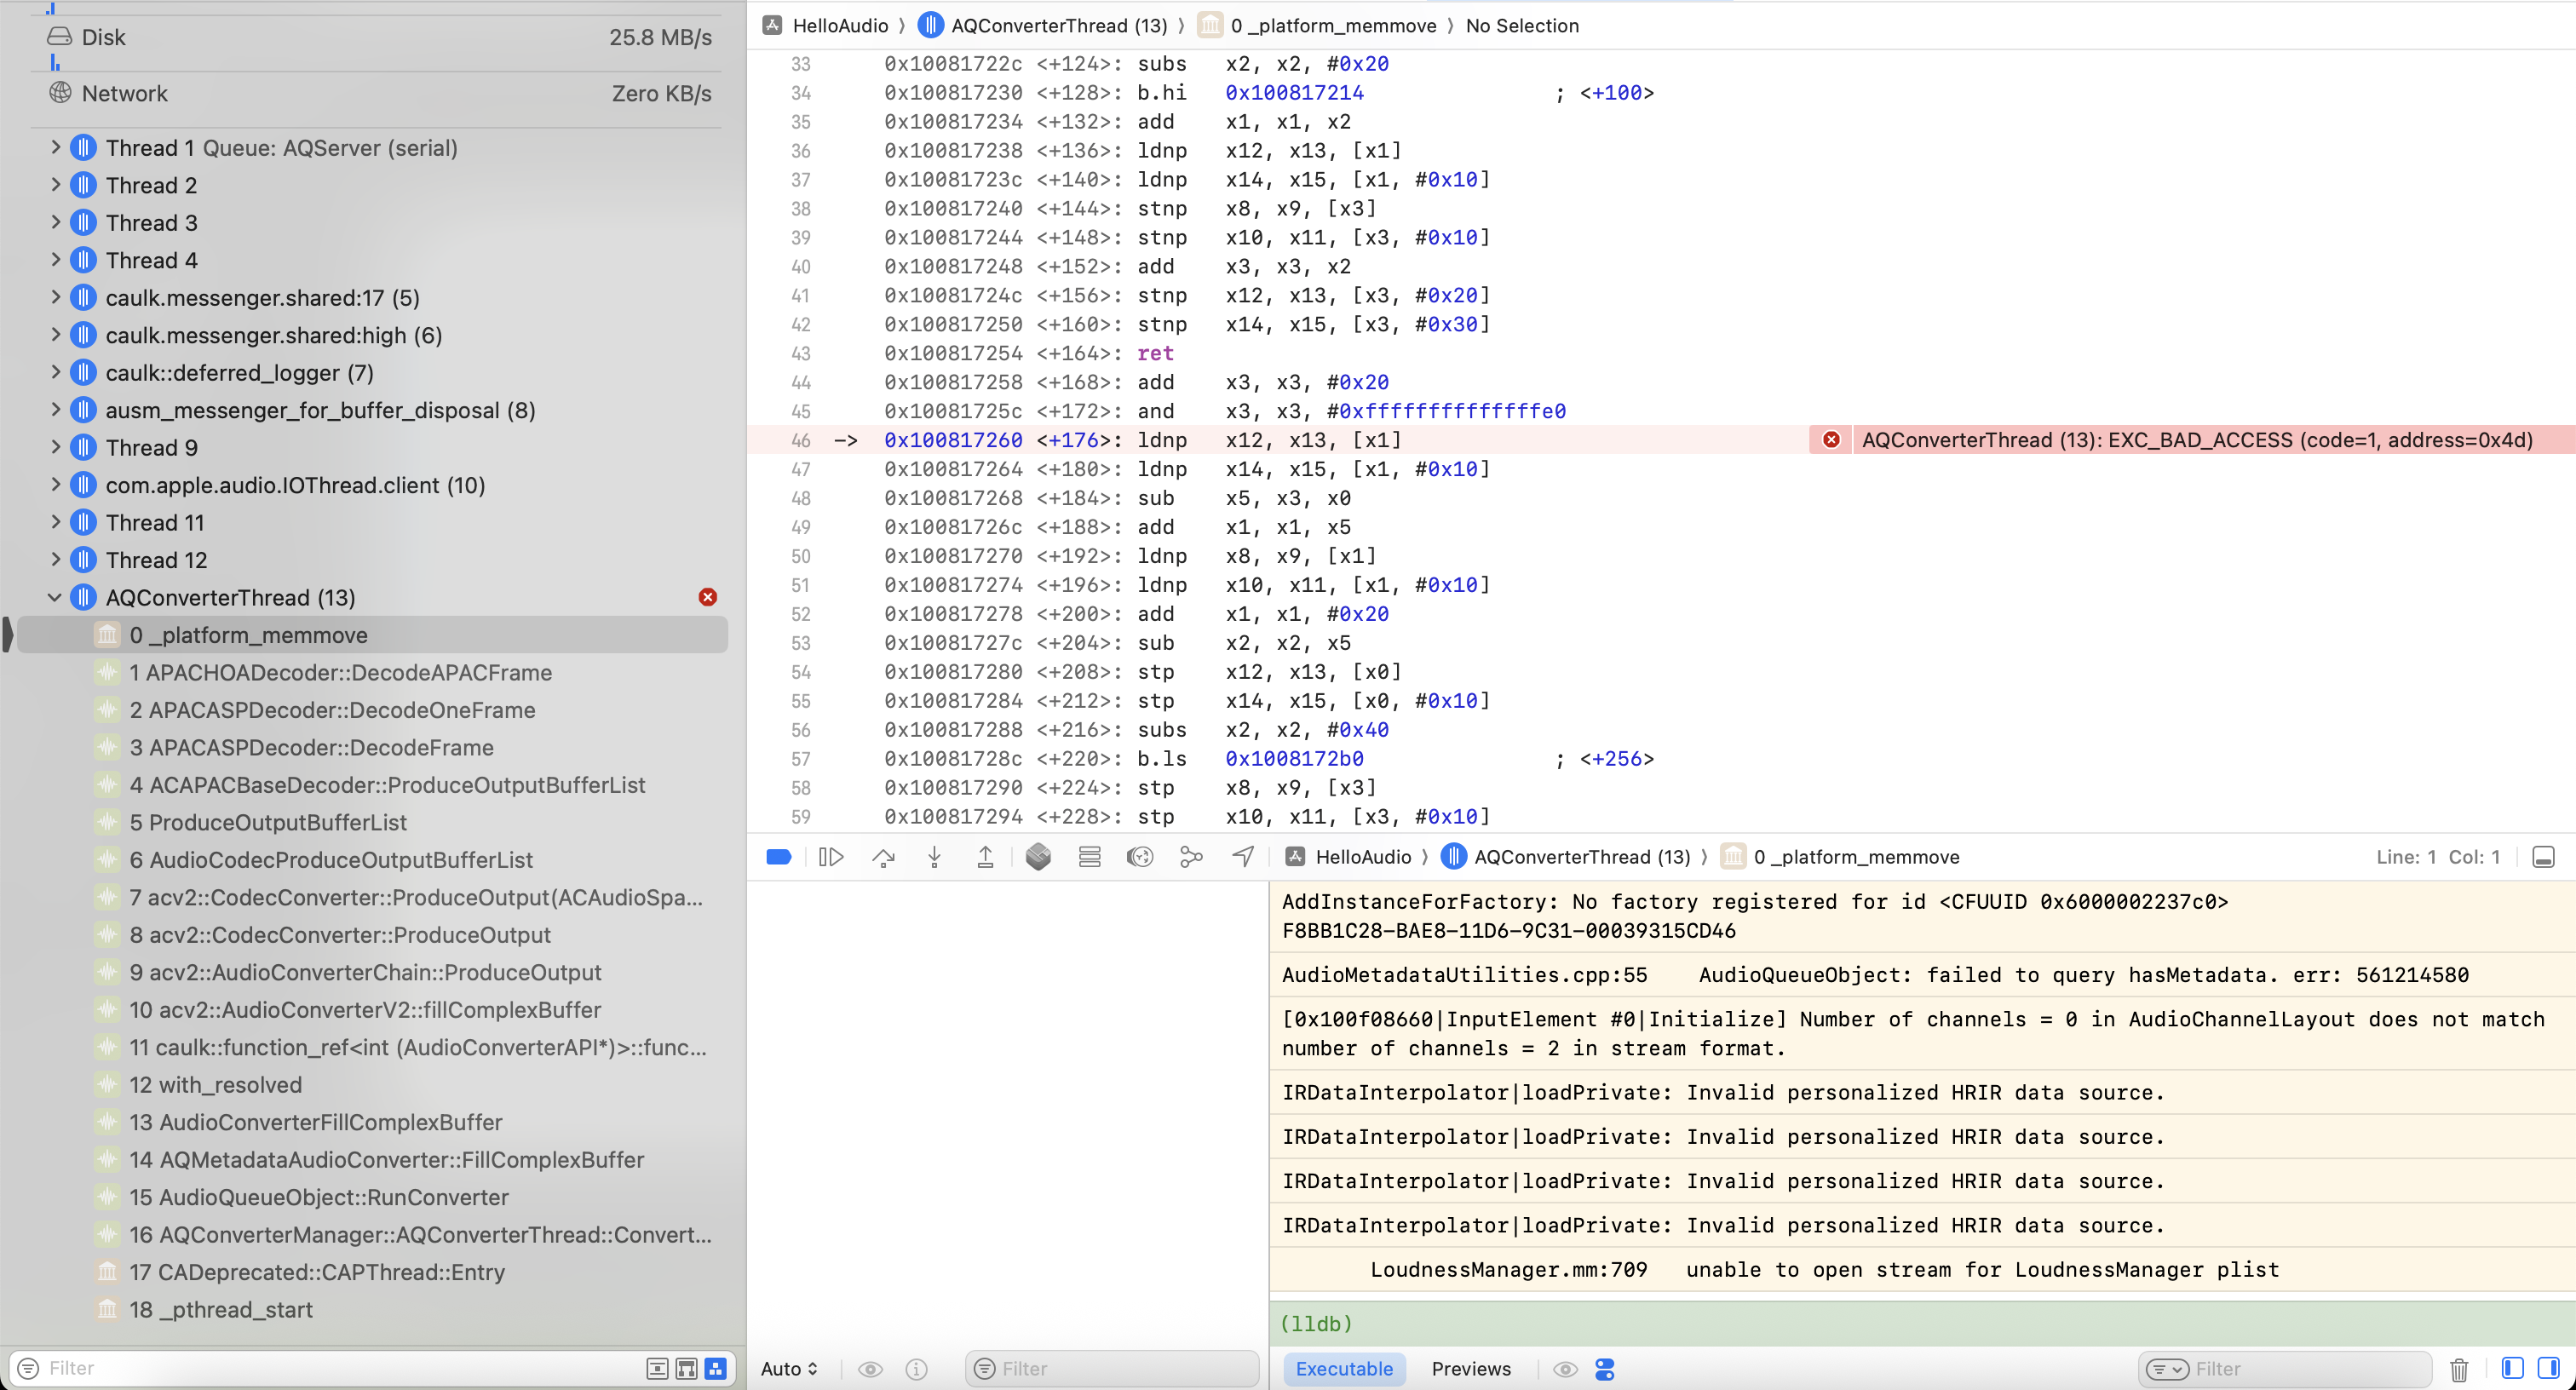 zhuowei/apple-positional-audio-codec-invalid-header
CVE-2025-31200 - @Noahhw46 figured it out
 dbrumley/extract75-cve-2020-13995
Control flow hijack exploit for CVE-2020-13995 with Docker-based deployment and Mayhem fuzzing integration for automated vulnerability testing.
 jaeles-project/jaeles-signatures
Default signature for Jaeles Scanner
 sn1r/forbidden-buster
A tool designed to automate various techniques in order to bypass HTTP 401 and 403 response codes and gain access to unauthorized areas in the…
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!
 khalidhusain786/scannerweb
Python3 vulnerability scanner that fuzzes all URLs of a target website and scans them for web vulnerabilities, with optional GoBuster integration for…
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…