CVE-2023-0386
 chenaotian/cve-2023-0386
Local privilege escalation exploit for CVE-2023-0386 targeting Linux kernel overlayfs. Includes detailed vulnerability analysis, PoC code, and…
binary-exploitationeducationexploitation+3
123
chenaotian/cve-2023-0386Local privilege escalation exploit for CVE-2023-0386 targeting Linux kernel overlayfs. Includes detailed vulnerability analysis, PoC code, and…
 r3fr4kt/popcorn-tjnull-oscp-
Popcorn HTB write-up covering advanced directory fuzzing, file upload bypass via magic numbers/extension spoofing using Burp Suite, and privilege…
 r4mbb/cve-2024-21626-poc
Root cuase & Proof Of Code
 szymonh/inspector-gadget
CVE-2021-39685 Description and sample exploit for Linux USB Gadget overflow vulnerability
 ww9210/cve-2017-7374
Proof-of-concept exploit for CVE-2017-7374, triggering a vulnerability in ext4 filesystem encryption via crafted directory operations on Linux.
 chunzhennn/cve-2023-21987-poc
Proof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…
 xairy/linux-kernel-exploitation
A collection of links related to Linux kernel security and exploitation
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
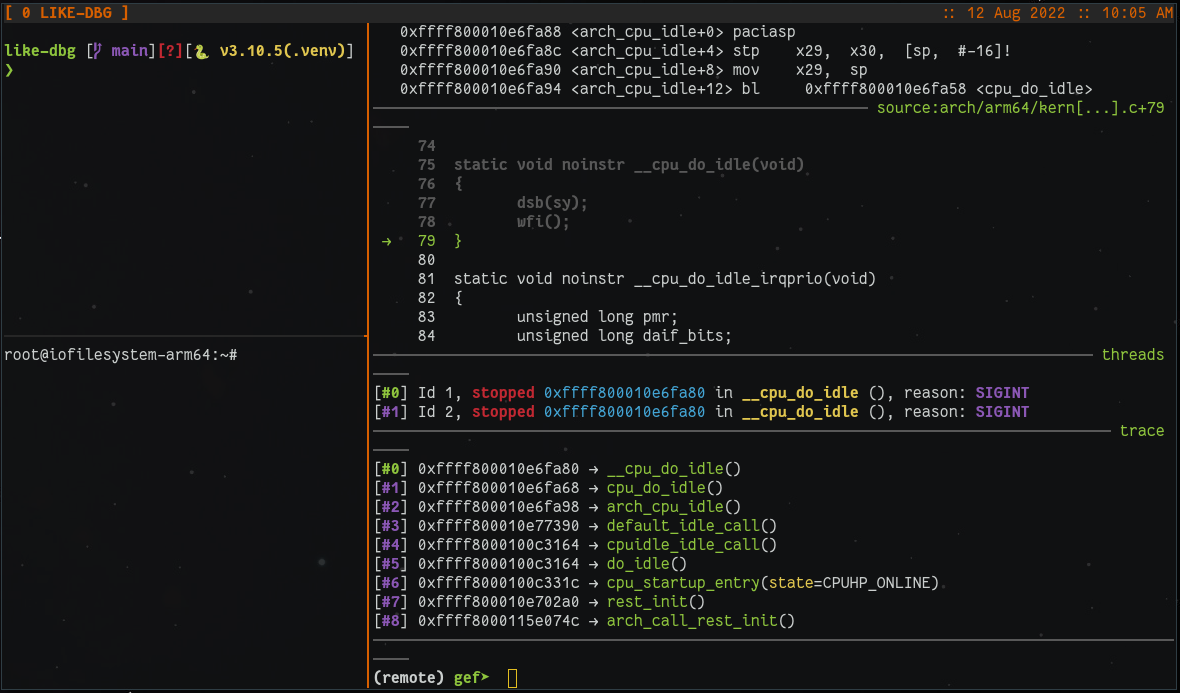 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
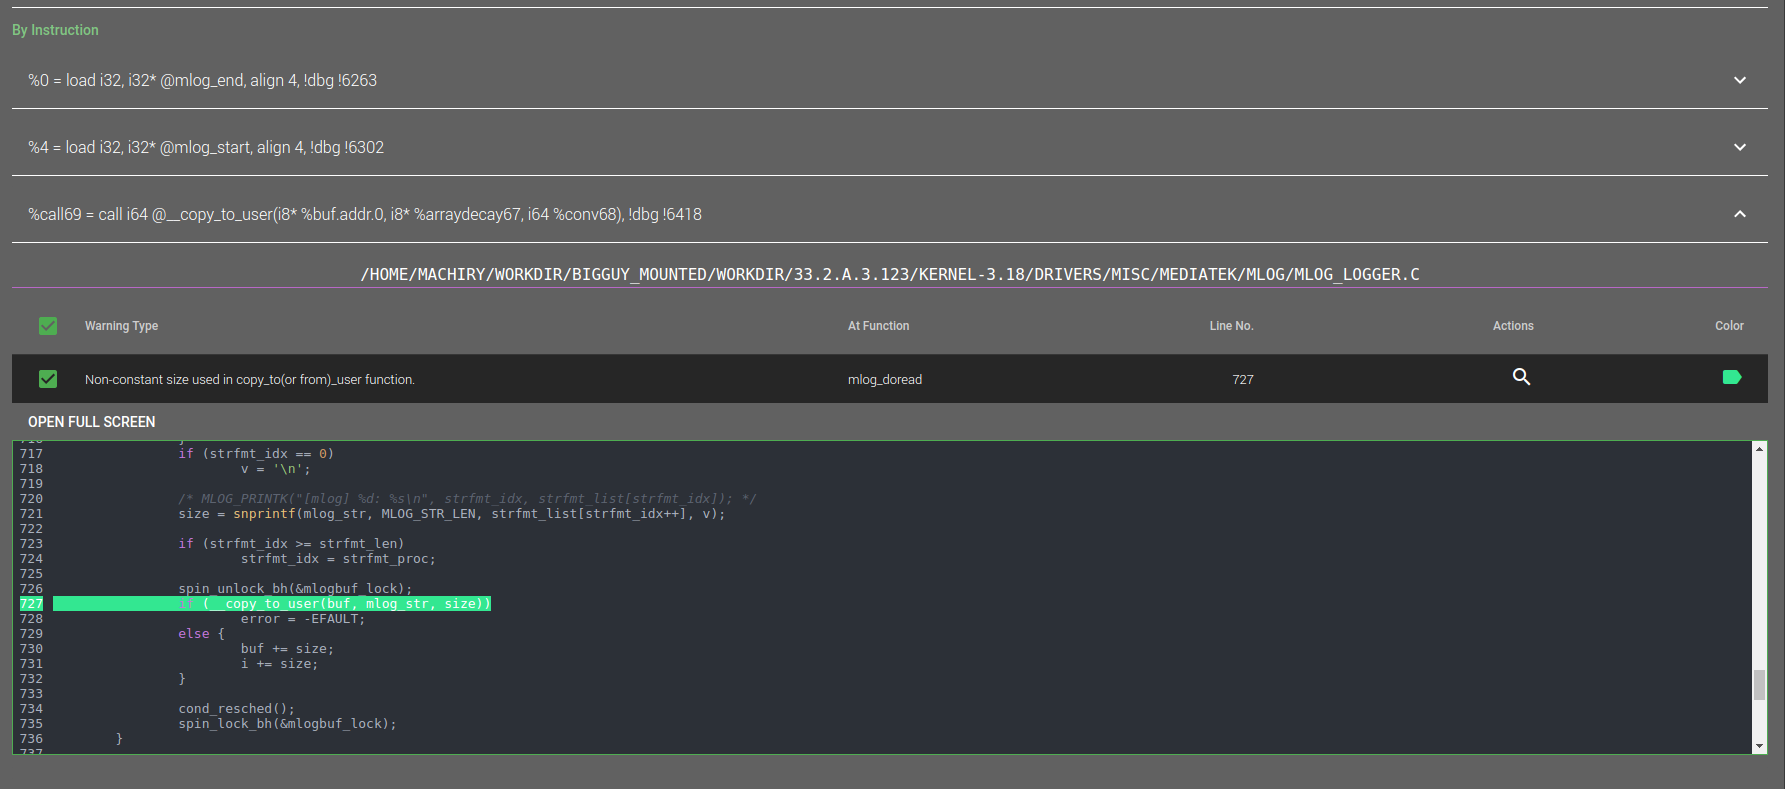 ucsb-seclab/dr_checker
DR.CHECKER : A Soundy Vulnerability Detection Tool for Linux Kernel Drivers
 mxmssh/drafl
AFL + DynamoRIO = fuzzing binaries with no source code on Linux
 emrekybs/draculaos
Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber Intelligence missions.
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…