

RESim
 mfthomps/resim
Reverse engineering software using a full system simulator
binary-analysisdebuggersdynamic-analysis-sandboxing+3
mfthomps/resimReverse engineering software using a full system simulator
 samsung/cotopaxi
Set of tools for security testing of Internet of Things devices using specific network IoT protocols
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 keensecuritylab/binabsinspector
Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…
 idoka/awesome-canbus
:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…
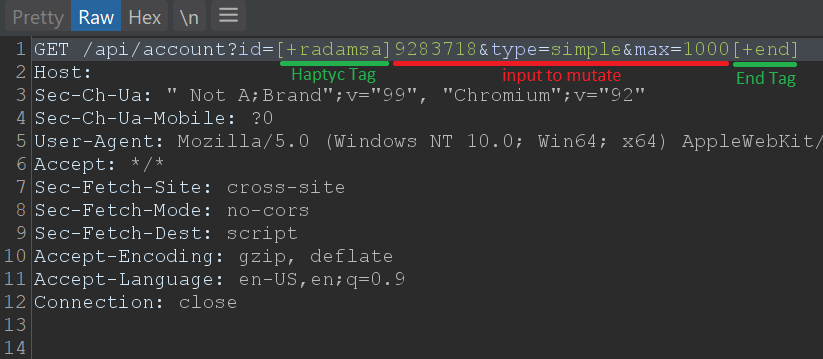 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 d0ge/websocketturbointruder
Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…
 jonathansalwan/vmprotect-devirtualization
Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
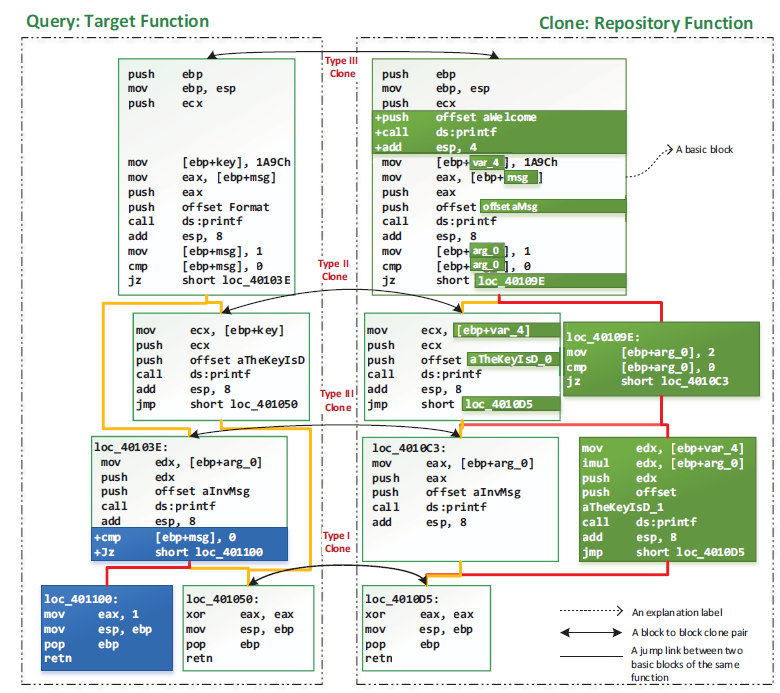 mcgill-dmas/kam1n0-community
Scalable assembly analysis platform for indexing, clone search, and executable classification using static, dynamic, and machine-learning techniques…
 airbus-cyber/ghidralligator
Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
 seal9055/sfuzz
High performance fuzzing using riscv to x86 binary translations and modern fuzzing techniques
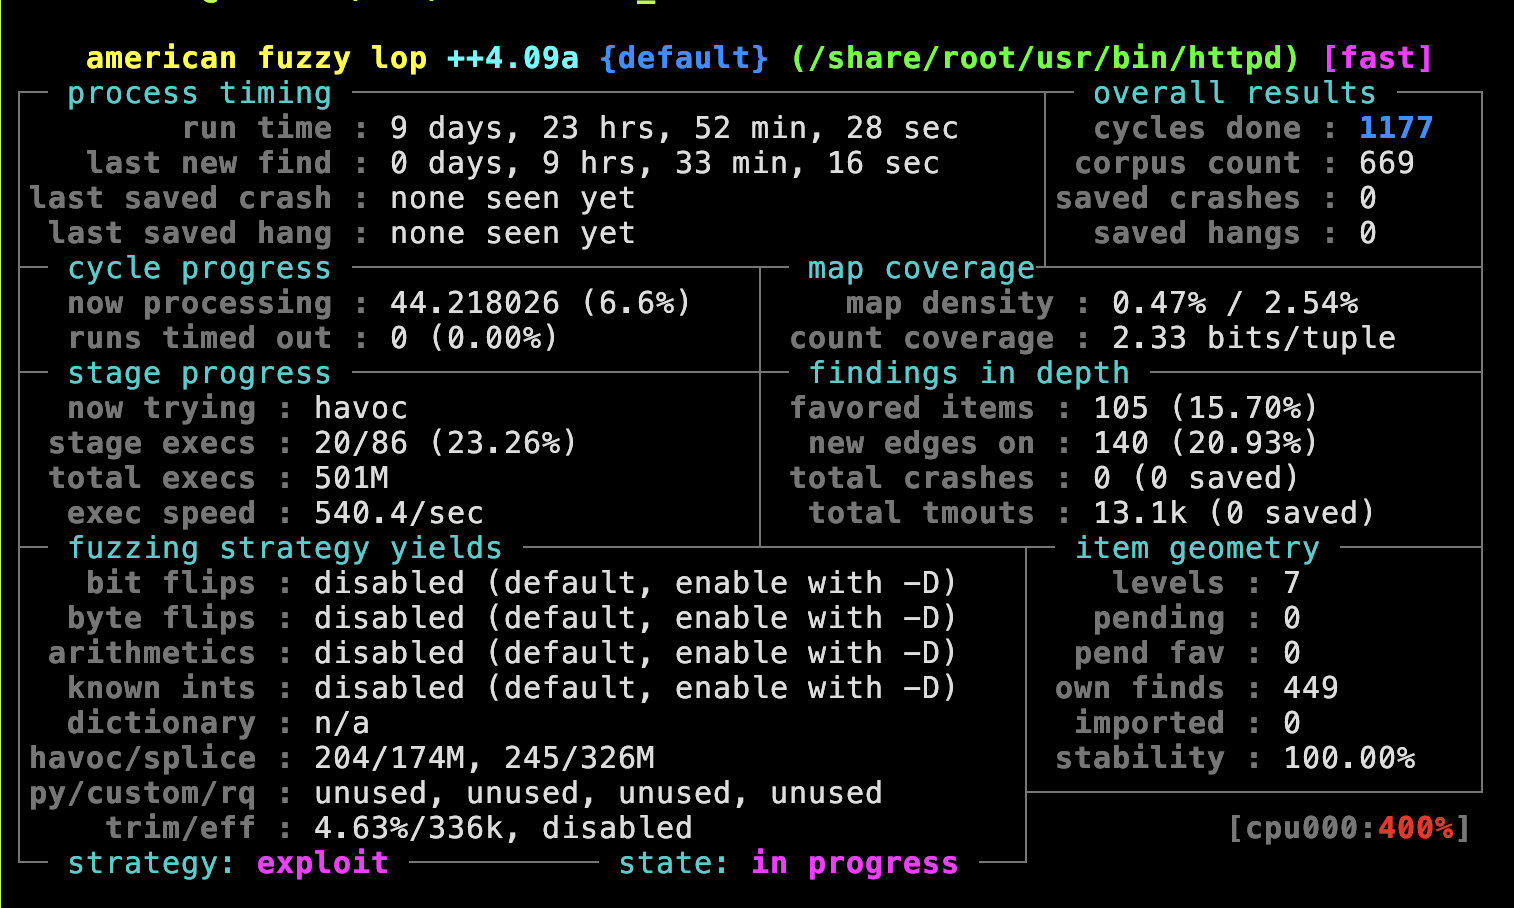 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
 liveoverflow/webp-cve-2023-4863
Educational repository demonstrating CVE-2023-4863 exploitation in libwebp using AFL++ fuzzing, with step-by-step video walkthroughs for…
 boredpentester/abl_rop
Experimenting with CVE-2022-20120 (Pixel Bootloader / ABL) using Unicorn, derived from eShard's emulator at…
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!