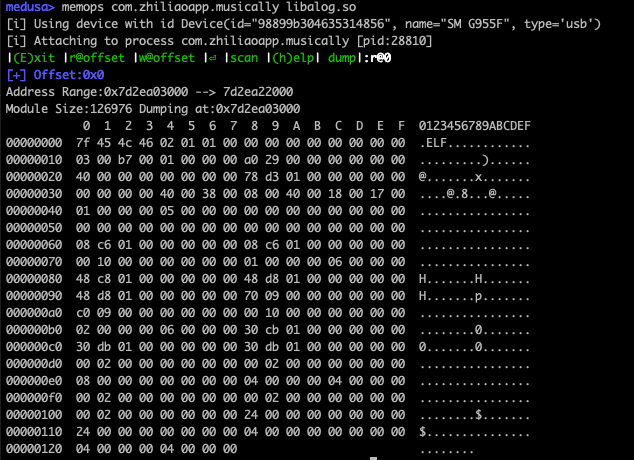
medusa
 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
android-securitydynamic-analysis-sandboxingexploitation+8
ch0pin/medusaMobile Edge-Dynamic Unified Security Analysis
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
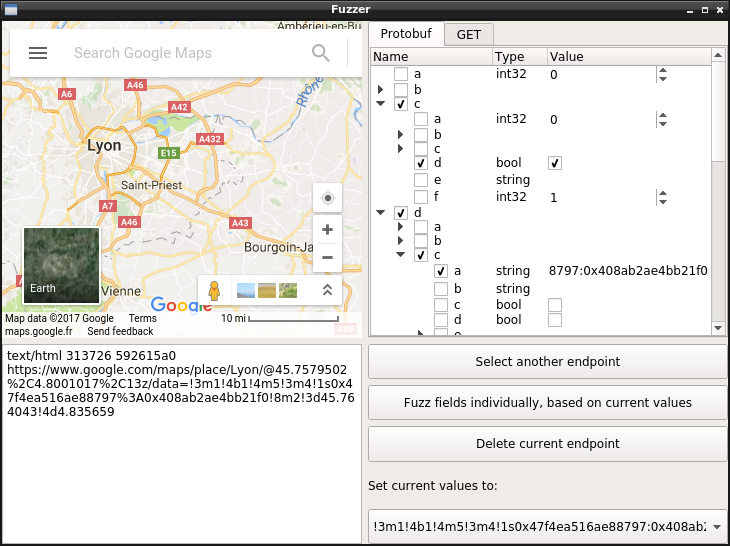 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 ucsb-seclab/bootstomp
BootStomp: a bootloader vulnerability finder
 flankerhqd/vendor-android-cves
Collections of my POCs for android vendor CVEs
 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
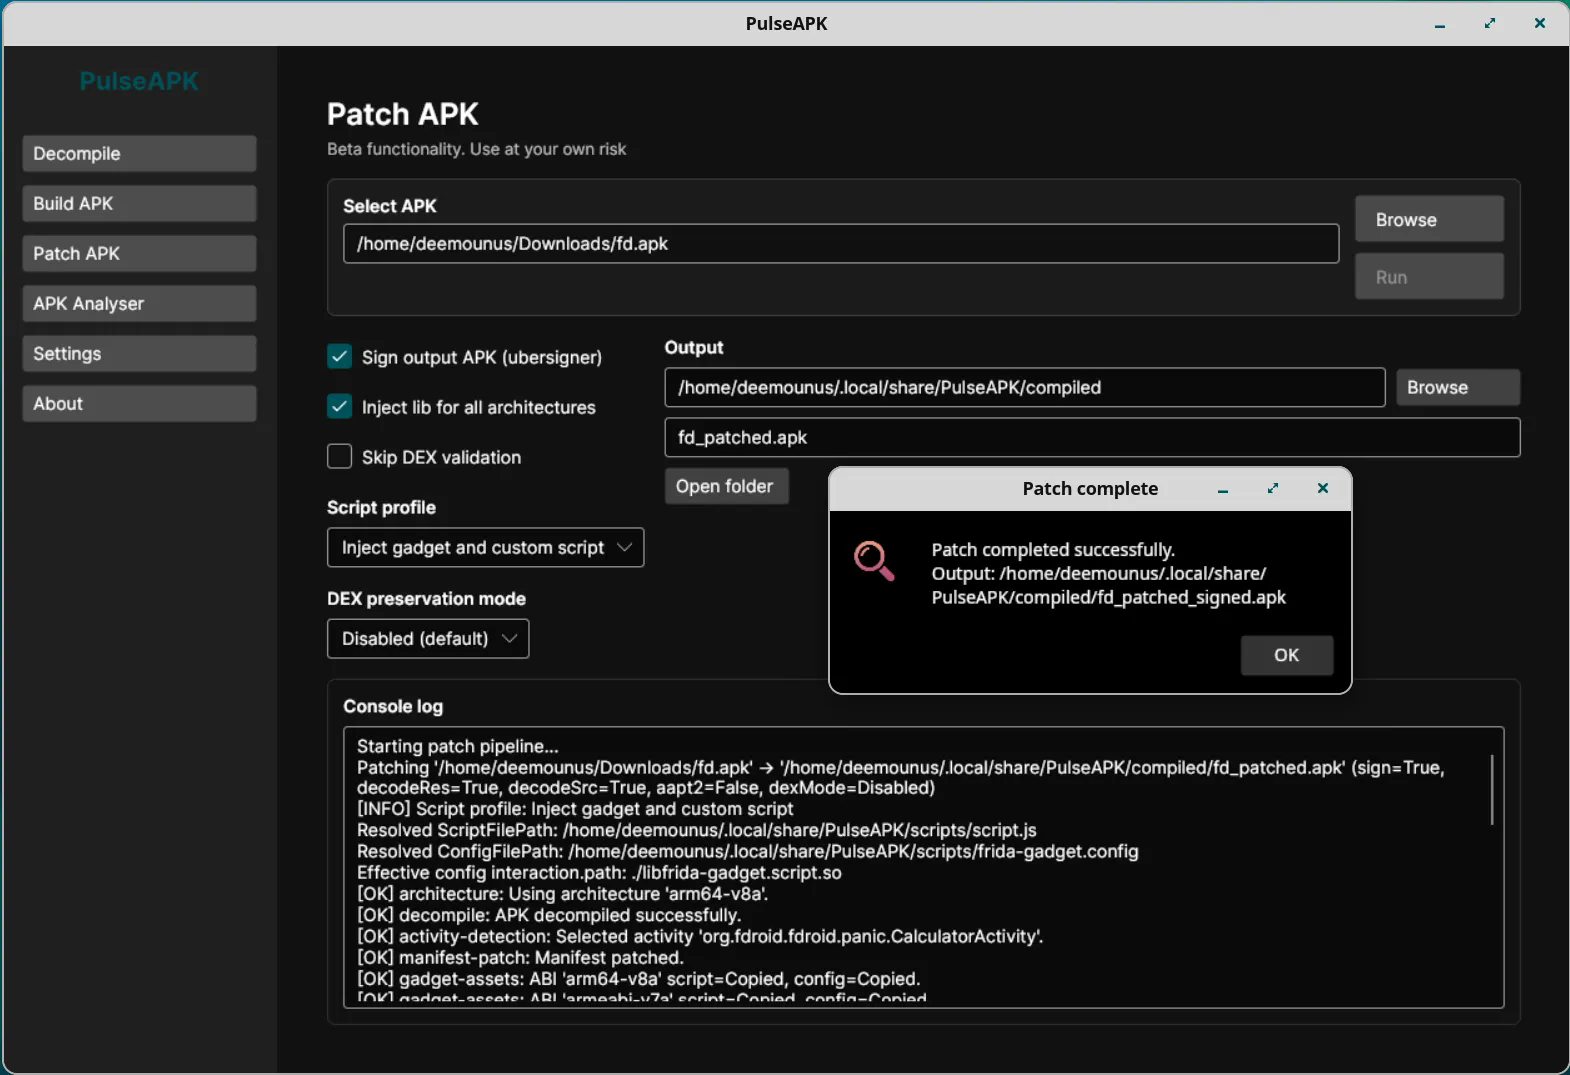 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 flankerhqd/cve-2015-6620-poc
POC for CVE-2015-6620, AMessage unmarshal arbitrary write
 0xbinder/android-kernel-exploitation-lab
This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.
 parallelbeings/cve-2019-14079
USB device fuzzing on Android Phone